cfchris.com

Loading

Archives 2026

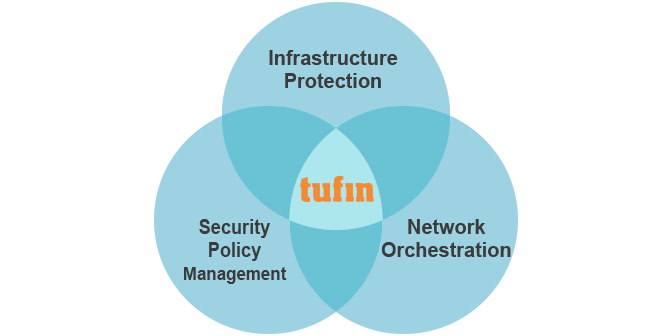
network security management

Network Security Management: A Practical Guide to Protecting Your Organization’s Network

Network Security Management: A Practical Guide

Network security management is the ongoing work of protecting an organization’s network, connected devices, and data from unauthorized access, disruption, and misuse. It combines policies, technologies, and operational practices to reduce risk while allowing employees and systems to communicate effectively.

Because networks change constantly—with new devices, cloud services, remote users, and evolving threats—security cannot be treated as a one-time setup. It requires regular monitoring, maintenance, and improvement.

Why Network Security Management Matters

A compromised network can expose sensitive information, interrupt business operations, and create significant costs. Threats may include phishing-related account takeovers, malware, ransomware, insider misuse, misconfigured devices, and attacks that exploit unpatched software.

Effective management helps organizations:

  • Protect confidential and regulated information
  • Limit unauthorized access to systems and services
  • Reduce the likelihood and impact of security incidents
  • Maintain availability of essential business systems
  • Meet contractual, legal, and regulatory requirements

Core Elements of Network Security Management

Asset Inventory and Network Visibility

Security begins with knowing what needs protection. Organizations should maintain an up-to-date inventory of network devices, servers, applications, cloud resources, user accounts, and data flows. Unknown or unmanaged devices can create blind spots that attackers may exploit.

Network diagrams and asset records should be reviewed regularly, especially after major infrastructure changes. Monitoring tools can help identify newly connected devices and unusual communication patterns.

Access Control

Access control determines who can connect to the network and what they can do once connected. A strong approach follows the principle of least privilege: users and services receive only the access needed to perform their tasks.

Useful practices include using multifactor authentication, removing access promptly when roles change, reviewing permissions periodically, and separating administrative accounts from everyday accounts. Network access controls can also help verify that devices meet security requirements before they are allowed to connect.

Network Segmentation

Network segmentation divides a network into smaller, controlled areas. For example, guest Wi-Fi, employee workstations, servers, and operational technology may be placed in separate segments with carefully defined rules for communication between them.

Segmentation can limit the spread of malware and reduce the damage caused by a compromised account or device. It is most effective when access between segments is explicitly controlled and regularly reviewed.

Firewalls and Secure Configuration

Firewalls help control traffic entering, leaving, and moving within a network. Their rules should reflect business needs and follow a default-deny approach where practical: permit required traffic and block everything else.

Security also depends on properly configuring routers, switches, wireless access points, servers, and cloud services. Unused services and accounts should be disabled, default credentials changed, and management interfaces restricted to authorized administrators.

Patching and Vulnerability Management

Software and firmware vulnerabilities can provide attackers with a route into the network. A vulnerability management process identifies affected systems, assesses risk, prioritizes fixes, and verifies that updates have been applied successfully.

Critical security updates should be addressed promptly, while planned maintenance helps ensure that routine patches are not overlooked. When a system cannot be patched immediately, temporary safeguards—such as restricting access or disabling an exposed service—may reduce risk.

Encryption and Secure Remote Access

Encryption helps protect information as it travels across networks and, when properly configured, while it is stored. Organizations should use current, well-supported encryption protocols and avoid obsolete configurations.

Remote access should be limited to approved users and devices. Secure connections, multifactor authentication, device security checks, and clear access policies can reduce the risk of compromised credentials being used to reach internal resources.

Monitoring and Incident Response

Continuous monitoring helps security teams spot unusual activity, such as unexpected connections, repeated login failures, or data transfers that differ from normal patterns. Logs from network devices, endpoints, identity systems, and cloud services can provide useful context when investigating an alert.

Monitoring is most valuable when alerts are reviewed and tied to a clear response process. An incident response plan should explain how to assess a threat, contain affected systems, preserve evidence, restore services, and communicate with relevant stakeholders.

Building an Effective Security Program

A practical network security management program can be developed in stages:

  1. Assess the environment: Identify critical systems, sensitive data, existing controls, and major risks.
  2. Set policies: Define requirements for access, device use, remote connections, updates, and incident reporting.
  3. Apply foundational controls: Prioritize multifactor authentication, secure configurations, patching, backups, and network segmentation.
  4. Monitor and test: Review security events, scan for vulnerabilities, and test incident response procedures.
  5. Improve continuously: Update controls as the organization, technology, and threat landscape change.

Standards and frameworks such as the NIST Cybersecurity Framework and ISO/IEC 27001 can help organizations structure their security efforts. The right approach depends on the organization’s size, industry, risk profile, and regulatory obligations.

Common Challenges

Organizations often struggle with incomplete asset inventories, outdated equipment, overly broad access permissions, and security tools that are not well integrated. Limited staffing can make it difficult to monitor alerts and maintain systems consistently. Cloud services and remote work can also expand the network beyond traditional office boundaries.

These challenges can be addressed by prioritizing the most important assets, documenting responsibilities, automating routine tasks where appropriate, and reviewing security controls on a regular schedule. Security measures should be practical enough to be followed and strong enough to reduce meaningful risks.

Conclusion

Network security management is a continuous process of understanding the environment, controlling access, reducing vulnerabilities, and responding effectively to threats. No single product can provide complete protection. A coordinated approach—supported by clear policies, reliable technology, and informed users—helps organizations protect their networks while keeping essential services available.


9 Key Benefits of Network Security Management

  1. Protects sensitive data
  2. Blocks unauthorized access
  3. Reduces cyberattack risks
  4. Limits malware spread
  5. Improves network reliability
  6. Supports regulatory compliance
  7. Enables safer remote access
  8. Detects threats earlier
  9. Strengthens business continuity


7 Drawbacks of Network Security Management

  1. Can be expensive to implement and maintain.
  2. Requires ongoing monitoring and updates.
  3. May need specialized staff and expertise.
  4. Can create complexity across systems.
  5. Strict controls may slow user workflows.
  6. False alarms can overwhelm security teams.
  7. No approach can eliminate all security risks.

Protects sensitive data

Network security management helps protect sensitive data—such as customer details, financial records, and confidential business information—from unauthorized access, theft, or exposure. By combining access controls, encryption, monitoring, and regular security updates, organizations can reduce the risk of data breaches and help ensure information is available only to authorized users.

Blocks unauthorized access

Network security management helps block unauthorized access by controlling who can connect to a network and which resources they can use. Measures such as strong authentication, access permissions, firewalls, and network segmentation make it harder for intruders to reach sensitive systems and data. Regularly reviewing accounts and security rules also helps close gaps before they can be exploited.

Reduces cyberattack risks

Network security management reduces cyberattack risks by identifying vulnerabilities and applying safeguards before attackers can exploit them. Regular software updates, access controls, network monitoring, and secure device configurations help block unauthorized access and detect suspicious activity early. These measures make it harder for threats such as malware, phishing, and ransomware to disrupt systems or expose sensitive information.

Limits malware spread

Network security management helps limit the spread of malware by separating systems into controlled network segments, restricting unnecessary connections, and monitoring traffic for suspicious activity. If a device is infected, these safeguards can help contain the threat before it reaches other computers, servers, or sensitive data. Regular updates, access controls, and a clear incident response plan further reduce the chance that malware will disrupt the entire organization.

Improves network reliability

Network security management improves network reliability by helping prevent malware, unauthorized access, and other disruptions that can slow or interrupt essential services. Regular monitoring, timely software updates, secure device configurations, and clear response plans help identify and address issues before they cause widespread downtime. As a result, employees and customers can rely on a more stable, available network.

Supports regulatory compliance

Network security management supports regulatory compliance by helping organizations protect sensitive data and demonstrate that appropriate safeguards are in place. Practices such as access controls, encryption, security monitoring, vulnerability management, and audit logging can help meet requirements under applicable laws and industry standards. Regular reviews also make it easier to identify gaps, keep records current, and provide evidence of compliance during audits.

Enables safer remote access

Network security management enables safer remote access by ensuring that employees and other authorized users can connect to company resources through protected, monitored channels. Controls such as multifactor authentication, encrypted connections, and device security checks help prevent unauthorized access and reduce the risk of exposing sensitive data. With clear access policies and ongoing monitoring, organizations can support flexible work while keeping their networks better protected.

Detects threats earlier

Network security management helps detect threats earlier by continuously monitoring network activity for unusual behavior, suspicious connections, and potential vulnerabilities. Early alerts give security teams more time to investigate and contain an incident before it spreads, helping reduce data loss, service disruptions, and recovery costs.

Strengthens business continuity

Network security management strengthens business continuity by helping prevent cyberattacks, outages, and unauthorized changes that can disrupt essential operations. Regular monitoring, timely software updates, secure backups, and a well-planned incident response process make it easier to detect problems, contain their impact, and restore systems quickly. As a result, employees can stay productive, critical services remain available, and the business is better prepared to serve customers during and after a security incident.

Can be expensive to implement and maintain.

Network security management can be expensive to implement and maintain, especially for organizations that need advanced tools, specialized staff, and ongoing training. Costs may include firewalls, monitoring software, security assessments, system upgrades, and incident response services. Smaller organizations may find it challenging to balance these expenses with other business priorities, but careful planning and a risk-based approach can help focus resources on the protections that matter most.

Requires ongoing monitoring and updates.

One challenge of network security management is that it requires ongoing monitoring and updates. Security teams must regularly review network activity, apply software and firmware patches, update access rules, and respond to new threats. This work takes time and resources, and falling behind can leave systems vulnerable to attacks.

May need specialized staff and expertise.

Network security management can require specialized staff with expertise in areas such as threat monitoring, access control, vulnerability assessment, and incident response. Hiring and retaining qualified professionals may be difficult and costly, especially for smaller organizations. Without the right skills, security tools may be misconfigured, alerts may go unanswered, and vulnerabilities may take longer to address, increasing the risk of a breach.

Can create complexity across systems.

Network security management can create complexity across systems, especially when an organization uses a mix of older infrastructure, cloud services, devices, and security tools. Keeping policies consistent, coordinating updates, and ensuring that systems work together can require significant time and expertise. If controls are poorly integrated or overly complicated, they may lead to configuration errors, slow down routine work, and make it harder for teams to identify and resolve security issues.

Strict controls may slow user workflows.

Strict network security controls can sometimes slow everyday workflows by adding extra steps, such as multifactor authentication, access approvals, or restrictions on certain websites and applications. These safeguards help protect sensitive systems and data, but if they are too complicated or poorly matched to employees’ needs, they can cause frustration, delays, and workarounds that introduce new risks. Regularly reviewing access policies and gathering user feedback can help organizations maintain strong security while keeping routine tasks efficient.

False alarms can overwhelm security teams.

False alarms can overwhelm security teams when monitoring tools repeatedly flag harmless activity as a potential threat. Investigating these alerts takes time away from genuine risks and can lead to alert fatigue, making it easier for important warnings to be missed. Fine-tuning detection rules, prioritizing alerts by severity, and regularly reviewing monitoring systems can help reduce unnecessary notifications.

No approach can eliminate all security risks.

No network security approach can eliminate every risk. New vulnerabilities, changing attack methods, human error, and unexpected system failures can still create opportunities for a security incident, even when strong controls are in place. Effective network security management is therefore about reducing the likelihood and impact of threats—not promising perfect protection—and continually reviewing defenses as the organization and its risks change.
app programmer

What Does an App Programmer Do? Skills, Responsibilities, and Career Insights

What Does an App Programmer Do?

An app programmer creates and maintains software applications for mobile devices, computers, and the web. They turn ideas and requirements into working features, writing code that helps people complete tasks, find information, communicate, and enjoy digital experiences.

App programming combines technical problem-solving with an understanding of how people use software. A successful app needs more than code: it should be useful, reliable, secure, and easy to navigate.

What App Programmers Work On

An app programmer’s work depends on the type of product they build. Common projects include:

  • Mobile apps: Applications for iOS and Android phones and tablets.
  • Web apps: Interactive software people access through a web browser.
  • Desktop apps: Programs designed for Windows, macOS, or Linux computers.
  • Cross-platform apps: Applications built to run on multiple platforms, often using a shared codebase.

Programmers may build an app from the ground up or improve an existing product. Their responsibilities can include adding features, fixing bugs, connecting the app to databases or online services, and updating it as operating systems and user needs change.

Typical Responsibilities

App programming is often a collaborative process. Depending on the project and team, an app programmer may:

  • Review project requirements and help plan how the app should work.
  • Write, test, and maintain code.
  • Build interfaces and connect them to application features.
  • Work with designers, product managers, and other developers.
  • Find and fix technical problems.
  • Improve performance, accessibility, and security.
  • Prepare updates and help publish the app.

Skills and Tools

The skills required depend on the platform and the project. Mobile programmers may use languages and frameworks such as Swift for Apple platforms, Kotlin for Android, or cross-platform tools such as Flutter and React Native. Web app programmers may work with JavaScript, TypeScript, and related frameworks. Other languages and tools are used for desktop software, back-end services, and data storage.

Alongside programming knowledge, app programmers benefit from skills such as:

  • Problem-solving: Breaking complex requirements into manageable steps.
  • Testing and debugging: Identifying problems and checking that changes work as expected.
  • Communication: Explaining technical choices and collaborating with a team.
  • Attention to detail: Catching errors that could affect usability or reliability.
  • Adaptability: Learning new tools and responding to changing project needs.
  • Security awareness: Helping protect user data and reduce common risks.

How an App Is Built

App development usually moves through several stages. The team first defines the problem the app should solve and identifies its intended users. Next, designers and developers plan the features and user experience. Programmers then build the software, test it, and refine it based on results and feedback.

After release, the work continues. Apps may need bug fixes, security updates, new features, and compatibility changes. Ongoing maintenance helps keep an app dependable as devices, platforms, and user expectations evolve.

Choosing an App Programmer

When hiring an app programmer or development team, start by describing the app’s purpose, audience, and essential features. Ask about relevant project experience, development practices, testing, security, and plans for maintenance. It is also helpful to discuss communication, timelines, and how changes will be handled during the project.

A clear project scope can make it easier to compare proposals and set realistic expectations. For larger projects, building a small first version can help test the idea before investing in additional features.

Why App Programmers Matter

App programmers help transform concepts into practical digital products. Their work supports everything from everyday tools to complex business systems. By combining coding skills with thoughtful planning and testing, they help create apps that are useful, dependable, and designed around the people who use them.


App Programmer FAQs: Roles, Career Paths, Languages, Salaries, and Hiring Costs

  1. What does an app programmer do?
  2. How do I become an app programmer?
  3. What programming languages do app programmers use?
  4. How much does an app programmer earn?
  5. What is the difference between an app programmer and an app developer?
  6. How much does it cost to hire an app programmer?

What does an app programmer do?

An app programmer designs, builds, tests, and maintains software applications for mobile devices, computers, or the web. They write code to create features, fix bugs, connect apps to databases and online services, and improve performance, security, and usability. App programmers often work with designers, project managers, and other developers to turn an idea into a reliable product and keep it updated over time.

How do I become an app programmer?

To become an app programmer, start by learning programming fundamentals, then choose a platform—such as iOS, Android, web, or cross-platform development—and study the languages and tools used for it. Build small projects to practice, create a portfolio that demonstrates your work, and learn essential skills like debugging, testing, and version control. Online courses, tutorials, formal education, and personal projects can all help you gain experience. As you progress, contribute to projects or pursue internships and entry-level roles, and keep learning as app technologies evolve.

What programming languages do app programmers use?

App programmers use different programming languages depending on the type of app and platform. For iOS apps, they commonly use Swift, while Android apps are often built with Kotlin or Java. Web apps may use JavaScript or TypeScript, and cross-platform apps can be developed with tools such as Flutter, which uses Dart, or React Native, which uses JavaScript or TypeScript. The right language depends on the app’s features, performance needs, and the devices it must support.

How much does an app programmer earn?

An app programmer’s earnings depend on experience, location, specialization, and whether they work as an employee or freelancer. In the U.S., many full-time app programmers earn roughly $70,000 to $150,000 per year, with senior developers and specialists in high-demand areas potentially earning more. Freelancers may charge hourly or project-based rates, which vary based on their skills and the scope of the work.

What is the difference between an app programmer and an app developer?

An app programmer primarily writes, tests, and maintains the code that makes an application work. An app developer often has a broader role, which may include planning features, designing the user experience, choosing technologies, coordinating development, and preparing the app for release. In everyday conversation, however, the terms are often used interchangeably, and responsibilities vary by company and project.

How much does it cost to hire an app programmer?

The cost to hire an app programmer depends on the app’s complexity, the platforms it needs to support, the programmer’s experience, and the project’s location and timeline. Programmers may charge by the hour or provide a fixed project estimate; a simple app usually costs less than a custom app with advanced features, integrations, or ongoing maintenance. Before hiring, outline your requirements and ask for a detailed estimate that explains what’s included, such as design, testing, launch, and post-launch support.

airbnb software engineer

Airbnb Software Engineer: Role, Skills, and Interview Preparation

What Does an Airbnb Software Engineer Do?

An Airbnb software engineer helps build and maintain the technology behind Airbnb’s travel marketplace. The work can include developing features for guests and hosts, improving search and booking experiences, strengthening platform reliability, and creating tools that support Airbnb’s operations.

The exact responsibilities depend on the team, level, and role. Airbnb’s engineering work spans areas such as web and mobile applications, backend services, data infrastructure, payments, trust and safety, and machine learning.

Common Responsibilities

Software engineers at a company like Airbnb may contribute to the full development lifecycle, from understanding a problem to shipping and supporting a solution. Typical responsibilities can include:

  • Designing, building, testing, and maintaining software
  • Developing reliable services and user-facing features
  • Collaborating with product managers, designers, data scientists, and other engineers
  • Reviewing code and helping maintain engineering standards
  • Investigating bugs and improving performance, scalability, and security
  • Using data and user feedback to evaluate product improvements

For example, an engineer working on search might help guests find relevant stays, while someone on a host-facing team could develop tools that make it easier to manage listings and reservations.

Skills and Experience

Requirements vary by opening, so candidates should review each job description carefully. Many software engineering roles call for a strong foundation in programming, software design, data structures, and algorithms. Depending on the position, employers may also look for experience with distributed systems, mobile development, web technologies, databases, or cloud infrastructure.

Technical skills matter, but so do communication and collaboration. Engineers often work across teams and need to explain tradeoffs, incorporate feedback, and make thoughtful decisions about how a change may affect users and the broader platform.

How to Prepare for an Airbnb Software Engineer Interview

Interview formats can change and may differ by role and seniority. The recruiter or hiring team should provide the most accurate information about a specific process. In general, preparation may include:

  • Reviewing fundamentals: Practice solving coding problems and explaining your approach, including its time and space complexity.
  • Practicing system design: Be ready to discuss how you would design a reliable, scalable service and explain the tradeoffs involved.
  • Preparing project examples: Describe your role, the challenge, the decisions you made, and the outcome. Be clear about what you personally contributed.
  • Thinking about users: Consider how product and engineering choices affect guests, hosts, and other people who use the platform.
  • Preparing questions: Ask about the team’s goals, technical challenges, collaboration practices, and expectations for the role.

Working as a Software Engineer at Airbnb

Airbnb’s products serve people across many markets, so engineering decisions can involve complex technical and real-world considerations. Teams may need to balance usability, reliability, safety, privacy, and the needs of different users. The details of the work and workplace experience depend on the organization, team, location, and position.

Candidates can learn more by reviewing Airbnb’s current careers site, reading individual job descriptions, and asking recruiters about team responsibilities and interview expectations. Because openings and requirements change, current listings are the best source for role-specific information.

Is an Airbnb Software Engineering Role Right for You?

An Airbnb software engineering role may appeal to developers who enjoy solving challenging technical problems and building products used by a broad community. A strong candidate can pair solid engineering fundamentals with curiosity, clear communication, and an ability to collaborate across disciplines.


Top 8 FAQs About Becoming a Software Engineer at Airbnb

  1. How much Airbnb pays software developers?
  2. Is it difficult to get hired at Airbnb?
  3. What engineer makes $500,000 a year?
  4. Is it hard to get a job at Airbnb?
  5. How do I become a software engineer for Airbnb?
  6. Can Airbnb be a full time job?
  7. Can you make $500,000 as a Software Engineer?
  8. How much do software engineers at Airbnb make?

How much Airbnb pays software developers?

Airbnb does not pay software developers one fixed salary: compensation depends on role, level, location, and experience. In the U.S., total compensation may include base salary, an annual bonus, and stock-based compensation, so reported figures can differ significantly from base pay alone. For the most accurate estimate, check the salary range in the specific job posting and confirm the compensation details with Airbnb’s recruiter.

Is it difficult to get hired at Airbnb?

Yes, getting hired as a software engineer at Airbnb can be competitive. The process may assess coding fundamentals, problem-solving, system design, communication, and relevant experience, with expectations varying by role and seniority. Strong preparation helps: review the job description, practice explaining your technical decisions, and be ready to discuss your impact on past projects. Hiring requirements and interview steps can change, so check the current listing and confirm details with the recruiter.

What engineer makes $500,000 a year?

At Airbnb, an annual compensation package of $500,000 or more may be possible for some highly experienced senior, staff, or principal software engineers, particularly when stock and bonuses are included. That figure is not a typical salary or guaranteed pay: compensation varies by level, role, location, performance, and the value of equity over time. For a specific estimate, check current job listings and reliable compensation data, and distinguish base salary from total compensation.

Is it hard to get a job at Airbnb?

Getting a job at Airbnb can be competitive, as roles may attract many qualified candidates and the hiring process can assess technical skills, problem-solving, communication, and relevant experience. The level of difficulty depends on the position, team, location, and your background. Preparing thoroughly—by reviewing the job requirements, practicing role-specific interview questions, and clearly describing your past work—can help you present your strengths.

How do I become a software engineer for Airbnb?

To become a software engineer at Airbnb, build strong programming and computer science fundamentals, then develop practical experience by creating projects, contributing to open-source software, or working in engineering roles. Review Airbnb’s current job postings to find positions that match your skills and experience, and tailor your résumé to highlight relevant accomplishments. Prepare for the interview process by practicing coding, system design (for applicable roles), and clear explanations of your past projects. Requirements and interview steps vary by position, so use the job listing and guidance from the recruiting team as your most reliable sources.

Can Airbnb be a full time job?

Yes, working as a software engineer at Airbnb can be a full-time job. Airbnb hires full-time engineers for a range of teams and specialties, though role availability, location, and employment terms vary. Check Airbnb’s current careers page for open positions and review each listing for details about the role, schedule, and work arrangement.

Can you make $500,000 as a Software Engineer?

Yes, it’s possible for a software engineer to earn $500,000 or more in total annual compensation, but it’s uncommon and typically reflects a senior or staff-level role at a high-paying technology company. Total compensation may include salary, bonuses, and stock, whose value can change over time; it also varies by level, location, experience, and market conditions. At Airbnb, as elsewhere, pay depends on the specific role and offer, so check current job listings and reliable compensation data rather than treating $500,000 as a typical salary.

How much do software engineers at Airbnb make?

Software engineer compensation at Airbnb varies by role, experience level, and work location. Total pay may include base salary, stock-based compensation, and a bonus, so reported figures can differ substantially. For the most accurate estimate, check the salary range in the specific job listing and compare recent compensation reports for the same level and location.

cyber security managed services

Cyber Security Managed Services: A Practical Guide for Businesses

Cybersecurity Managed Services: A Practical Guide for Businesses

Cybersecurity threats can affect organizations of every size. Phishing, ransomware, stolen credentials, and software vulnerabilities can disrupt operations, expose sensitive information, and damage customer trust. Keeping up with these risks takes time and specialized expertise—resources that many businesses do not have in-house. Cybersecurity managed services can help fill that gap.

What Are Cybersecurity Managed Services?

Cybersecurity managed services are ongoing security services provided by an external team. Depending on the provider and the organization’s needs, these services may include monitoring systems, identifying vulnerabilities, responding to incidents, managing security tools, and helping meet regulatory requirements.

Some providers offer a broad security program, while others focus on specific areas such as endpoint protection or cloud security. The goal is to strengthen an organization’s defenses and provide access to security expertise without requiring every capability to be built internally.

Common Services

A managed cybersecurity program may include a combination of the following:

  • 24/7 security monitoring: Reviewing alerts and system activity to help identify suspicious behavior.
  • Threat detection and response: Investigating potential incidents and coordinating actions to contain them.
  • Endpoint security: Protecting computers, servers, and mobile devices from malware and unauthorized access.
  • Vulnerability management: Finding and prioritizing weaknesses in software, systems, and configurations.
  • Security assessments: Evaluating existing controls, processes, and exposure to risk.
  • Identity and access management: Helping ensure users have appropriate access and that authentication controls are in place.
  • Cloud security: Reviewing cloud environments, permissions, and configurations for common security issues.
  • Security awareness training: Helping employees recognize phishing attempts and follow safer practices.
  • Incident response planning: Establishing roles, procedures, and communication plans before an incident occurs.

How Managed Services Can Help

Access to specialized expertise: Security providers can bring experience with current threats, technologies, and response practices. This can be valuable for organizations that do not have a large internal security team.

Consistent monitoring: Threats do not follow business hours. Depending on the service agreement, a provider may monitor systems around the clock and escalate significant alerts when they occur.

More predictable costs: Managed services often use recurring fees, which can make security spending easier to plan than building every capability from scratch. Costs and included services vary, so the contract should be reviewed carefully.

Support for internal teams: A provider can handle routine monitoring or specialized tasks, allowing in-house staff to focus on business priorities. Managed services work best when responsibilities are clearly divided rather than assumed.

Improved readiness: Regular assessments, documented procedures, and testing can help an organization prepare for security incidents and reduce confusion during a response.

Choosing a Managed Security Provider

Not every provider offers the same capabilities. Before selecting one, consider your organization’s systems, risk tolerance, compliance obligations, and internal expertise. Ask prospective providers questions such as:

  • Which services are included, and which cost extra?
  • Who monitors alerts, and what are the response hours?
  • How quickly will critical incidents be escalated?
  • What actions can the provider take without approval?
  • How will the provider protect access to your systems and data?
  • What reports, reviews, and service-level commitments are provided?
  • How does the provider support incident response and recovery?
  • Can the services scale as your organization changes?

Request clear documentation of responsibilities, escalation paths, data handling practices, and service levels. It is also useful to understand how the provider will work with your IT team, leadership, legal counsel, and other vendors during an incident.

Managed Services Do Not Transfer All Responsibility

Hiring a cybersecurity provider does not make an organization automatically secure or remove its responsibility for protecting information. Business leaders still need to set priorities, approve policies, manage user access, maintain backups, and ensure employees understand their role in security. The provider can supply tools and expertise, but effective security requires cooperation between the provider and the organization.

Organizations should also review the provider’s own security practices. A managed security provider may need access to sensitive systems, so its access controls, incident procedures, confidentiality commitments, and handling of customer data matter.

Making the Most of a Managed Security Partnership

Start by identifying critical systems and information, then define the outcomes the service should support. Set measurable expectations, such as reporting frequency, alert escalation procedures, and vulnerability remediation timelines. Review results regularly and update the scope when your technology, risks, or business needs change.

Cybersecurity managed services can help businesses strengthen monitoring, improve incident readiness, and access expertise that may be difficult to maintain internally. With a carefully selected provider, clear responsibilities, and active oversight, they can become a useful part of a broader security program—not a substitute for one.


5 Essential Tips for Choosing and Managing Cybersecurity Services

  1. Define clear security goals and service-level expectations.
  2. Verify the provider’s certifications and incident response plan.
  3. Require regular vulnerability scans and patch management.
  4. Keep access limited with multifactor authentication.
  5. Review reports and test recovery plans regularly.

Define clear security goals and service-level expectations.

Define clear security goals and service-level expectations before choosing a cybersecurity managed services provider. Identify the outcomes that matter most—such as 24/7 monitoring, faster incident response, vulnerability remediation, or compliance support—and agree on measurable targets, reporting schedules, and escalation procedures. Clear expectations help your provider prioritize the right risks, coordinate effectively with your team, and demonstrate whether the service is meeting your needs.

Verify the provider’s certifications and incident response plan.

Before choosing a cybersecurity managed services provider, verify that its certifications are current, relevant to your needs, and held by the people who will work on your account. Ask for details about its incident response plan, including how it detects and escalates threats, who will contact your team, what actions it can take, and how quickly it will respond. A clear, tested plan and qualified staff can help ensure the provider is prepared to support your organization when a security incident occurs.

Require regular vulnerability scans and patch management.

Require your cybersecurity managed services provider to run vulnerability scans on a regular schedule and promptly share findings, priorities, and remediation plans. Scans can uncover outdated software, misconfigurations, and other weaknesses before attackers exploit them. Pair scanning with a clear patch management process that prioritizes critical updates, tests patches when appropriate, and tracks completion across your systems. Regular reporting helps confirm that issues are being addressed and that your security posture keeps pace with emerging risks.

Keep access limited with multifactor authentication.

Limit access to sensitive systems and data by giving each user only the permissions needed for their role, and require multifactor authentication (MFA) wherever possible. MFA adds a verification step—such as an authenticator app prompt or security key—so a stolen password alone is less likely to grant access. A managed security provider can help configure MFA, review access regularly, and remove accounts or permissions that are no longer needed.

Review reports and test recovery plans regularly.

Review cybersecurity reports regularly to understand emerging threats, unresolved vulnerabilities, and whether your managed services are meeting agreed-upon goals. Reports are most useful when they lead to clear actions, owners, and deadlines. Also test recovery plans on a recurring basis—not just on paper—to confirm that backups can be restored, critical systems can be brought back online, and everyone knows their role during an incident. Regular reviews and realistic exercises can reveal gaps early and help your business recover more confidently when disruption occurs.

udemy java

Udemy Java Courses: A Guide to Learning Java Online

Learning Java on Udemy: How to Choose the Right Course

Java is one of the most widely used programming languages, powering applications in areas such as web development, enterprise software, and Android development. For beginners and experienced programmers alike, Udemy offers a range of Java courses that can help build practical skills at your own pace.

What You Can Learn

Java courses on Udemy cover topics at different levels. A beginner course may introduce programming fundamentals, while an advanced course might focus on frameworks, testing, or application architecture. Depending on the course, you may learn:

  • Java syntax, variables, data types, and control flow
  • Object-oriented programming, including classes, inheritance, and interfaces
  • Collections, generics, and exception handling
  • Working with files, databases, and APIs
  • Building projects with tools and frameworks such as Spring
  • Testing, debugging, and using development environments

How to Choose a Java Course

The best course depends on your experience and goals. Before enrolling, read the course description and check that its content matches what you want to learn. A course designed for complete beginners should explain basic concepts and provide setup instructions. If you already know the fundamentals, look for lessons that go deeper or focus on a specific area of Java development.

It can also help to review the course curriculum, sample lessons, and recent student feedback. Look for a clear structure, hands-on exercises, and projects that let you apply what you learn. Check when the material was last updated, especially if the course covers development tools or frameworks that change over time.

Make the Most of Your Course

Watching lessons is only part of learning to code. Write the examples yourself, experiment with the code, and try solving small problems without immediately looking at the answer. When you encounter an error, practice reading the message and tracing the issue. These habits help turn new concepts into skills you can use independently.

Consider supplementing your course with a personal project. You could build a simple calculator, task tracker, or small application that works with a database. Projects give you a chance to combine concepts and create examples to discuss in a portfolio or interview.

Is Udemy a Good Way to Learn Java?

Udemy can be a flexible and affordable starting point for learning Java, particularly if you prefer video lessons and self-paced study. However, the experience varies by course, and completing a course alone does not guarantee professional proficiency. Consistent practice, independent projects, and learning to use documentation are important parts of the process.

With a course suited to your level and a steady routine of hands-on coding, Udemy can help you build a solid foundation in Java. Choose a learning path that supports your goals, practice regularly, and keep developing projects as your skills grow.


Learning Java on Udemy: 9 Frequently Asked Questions

  1. Is Udemy a good place to learn Java?
  2. Which Udemy Java course is best for beginners?
  3. Can I learn Java on Udemy with no programming experience?
  4. How long does it take to complete a Java course on Udemy?
  5. Do Udemy Java courses include hands-on projects?
  6. Do Udemy Java courses provide a certificate of completion?
  7. How much do Java courses on Udemy cost?
  8. Are Udemy Java courses kept up to date?
  9. Can a Udemy Java course help me get a job as a Java developer?

Is Udemy a good place to learn Java?

Yes, Udemy can be a good place to learn Java, especially if you prefer flexible, self-paced video lessons. Courses range from beginner fundamentals to advanced topics, so review the curriculum, sample lessons, and recent student feedback to find one that fits your experience and goals. To make real progress, practice writing code alongside the lessons and build projects of your own; watching videos alone is rarely enough to develop strong programming skills.

Which Udemy Java course is best for beginners?

The best Udemy Java course for beginners is one that starts with the fundamentals, explains concepts clearly, and includes plenty of coding exercises and practical projects. Before enrolling, review the curriculum, preview a lesson, and check recent student feedback to make sure the course matches your learning style and goals. Look for coverage of core topics such as variables, control flow, methods, and object-oriented programming, and choose a course that’s regularly updated.

Can I learn Java on Udemy with no programming experience?

Yes, you can learn Java on Udemy with no programming experience. Look for a beginner-friendly course that starts with the basics, explains how to set up your development environment, and includes hands-on exercises and projects. Work through the lessons at your own pace, write the code yourself, and practice regularly. Programming concepts can take time to understand, so starting small and reviewing lessons when needed can help you build confidence.

How long does it take to complete a Java course on Udemy?

The time it takes to complete a Java course on Udemy depends on the course’s length, your prior programming experience, and how much time you can study each week. Some introductory courses can be finished in a few days of focused learning, while more comprehensive courses may take several weeks or longer. Since Udemy courses are typically self-paced, you can pause, revisit lessons, and practice coding at a schedule that works for you.

Do Udemy Java courses include hands-on projects?

Yes, many Udemy Java courses include hands-on projects, coding exercises, or practice assignments to help you apply what you learn. The amount and type of project work vary by course, so review the curriculum and course description before enrolling. Look for projects that match your experience level and learning goals, and plan to write and adapt the code yourself to get the most benefit.

Do Udemy Java courses provide a certificate of completion?

Yes, many Udemy Java courses provide a certificate of completion after you finish all the course requirements. You can typically access and download the certificate from your Udemy account. Keep in mind that Udemy certificates recognize course completion but are not formal academic credit or an industry certification. Check the individual course details for its requirements and certificate availability.

How much do Java courses on Udemy cost?

Java course prices on Udemy vary by instructor, course content, and promotions. Many courses are regularly discounted, so the price you pay may be lower than the listed price. Check the course page for current pricing, included materials, and any applicable refund terms before enrolling.

Are Udemy Java courses kept up to date?

Udemy Java courses may be updated by their instructors, but how often they’re refreshed varies from course to course. Before enrolling, check the course’s “Last updated” date, curriculum, and recent student reviews to see whether the material still matches your learning goals and current tools. Java fundamentals often remain useful over time, while lessons on frameworks, software versions, and development tools may need more frequent updates.

Can a Udemy Java course help me get a job as a Java developer?

A Udemy Java course can help you build foundational skills and complete projects that may strengthen your job applications, but finishing a course alone usually isn’t enough to land a Java developer role. Employers often look for practical coding experience, familiarity with tools and frameworks used in the job, problem-solving skills, and the ability to explain your work. Choose a course with hands-on projects, then keep practicing, build a portfolio, and prepare for technical interviews to improve your chances.

java coding

Java Coding: A Practical Guide to Building Your First Programs

Java Coding: A Practical Guide to Getting Started

Java is a widely used programming language known for its portability, reliability, and extensive ecosystem. It powers everything from business applications and web services to Android tools and large-scale systems. Whether you are learning to code for the first time or adding another language to your toolkit, Java offers a structured way to build useful software.

What Is Java?

Java is a general-purpose, object-oriented programming language. Developers write Java source code, which is compiled into bytecode. That bytecode runs on the Java Virtual Machine (JVM), allowing the same program to work on different operating systems with a compatible Java runtime.

This approach is often summarized as “write once, run anywhere.” In practice, a program may still need adjustments for platform-specific features, but the JVM helps make Java applications portable across many environments.

Writing Your First Java Program

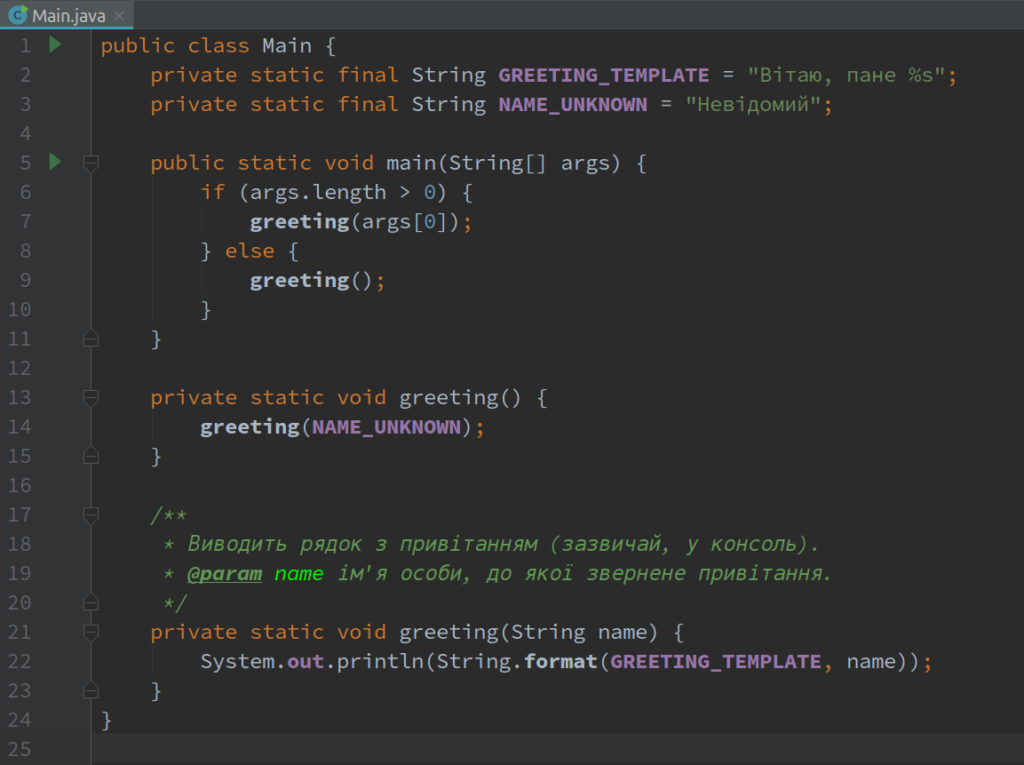
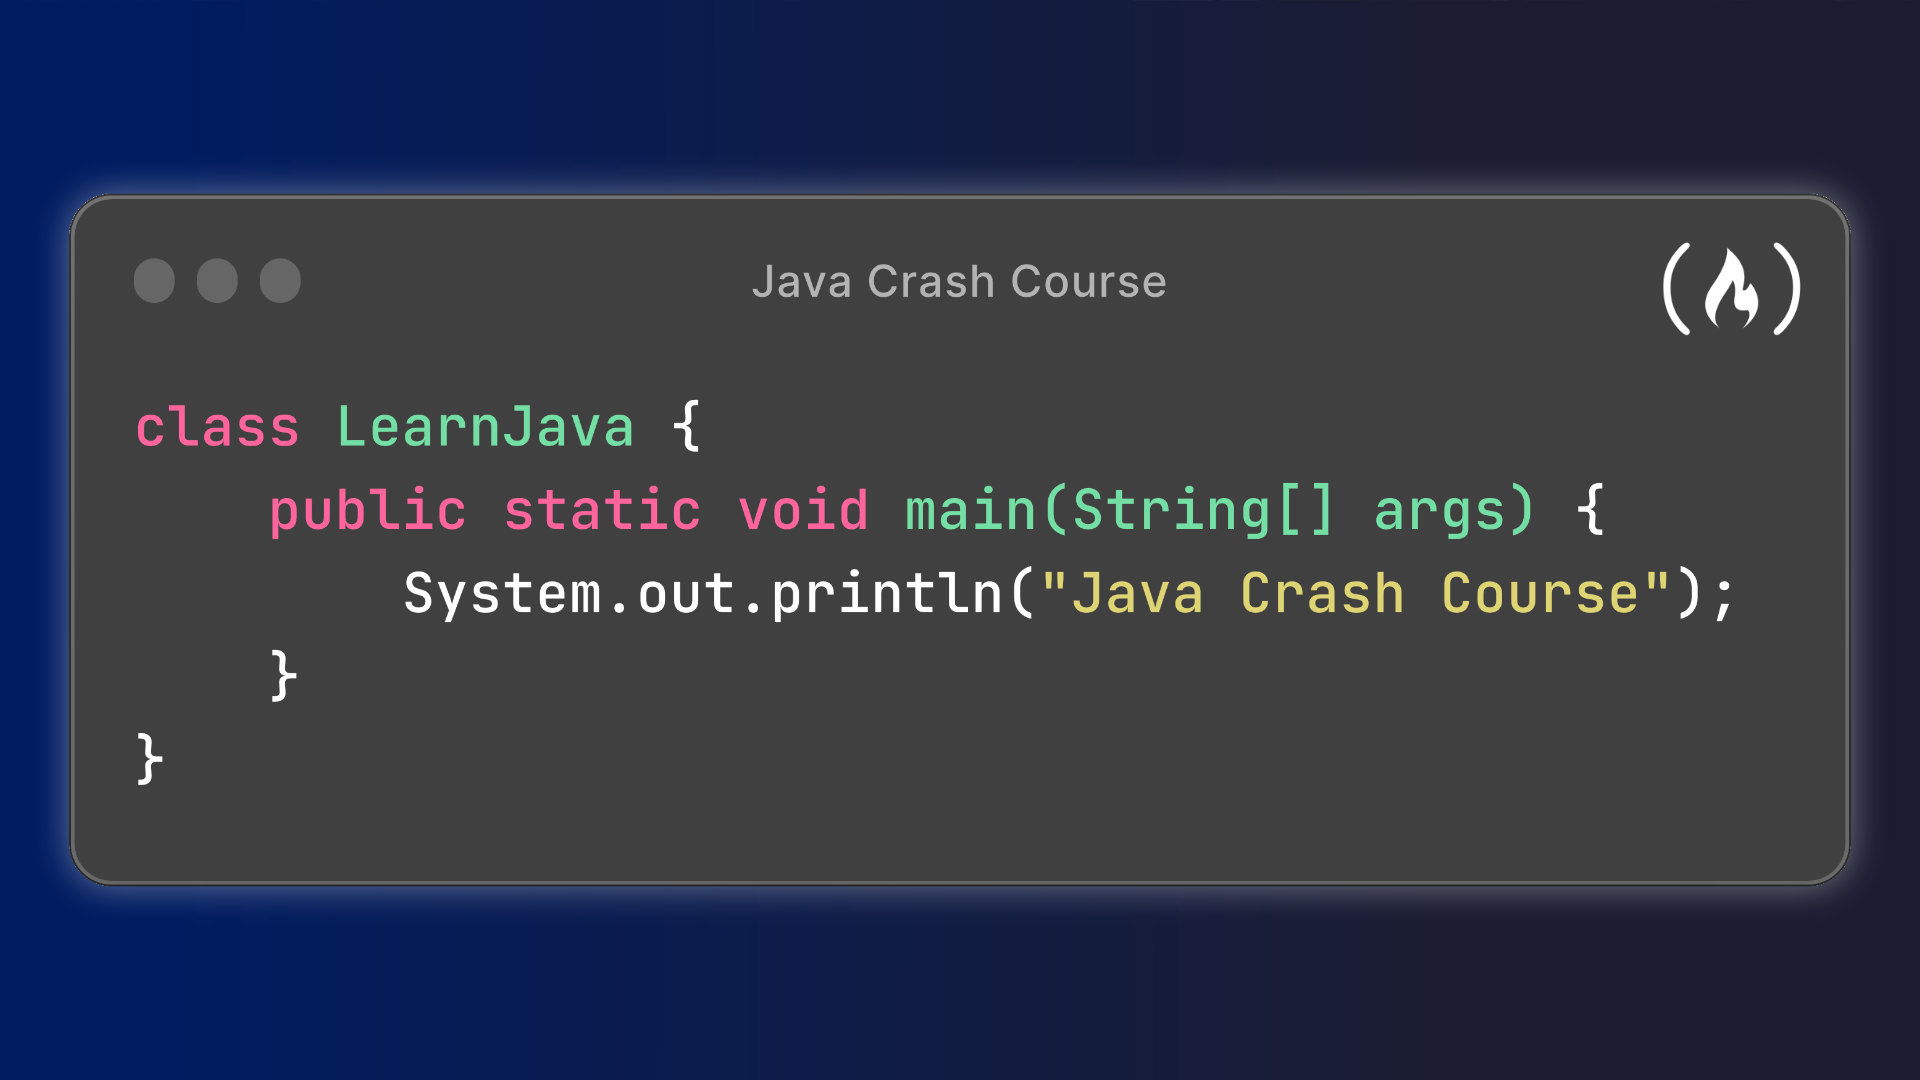
A simple Java program can display a message in the console:

public class Main {

public static void main(String[] args) {

System.out.println("Hello, world!");

}

}

In this example, Main is the class name, and main is the method where the program begins. The System.out.println statement prints text to the console. Java is case-sensitive, so capitalization and punctuation matter.

Core Concepts in Java Coding

Variables and Data Types

Variables store values that a program can use. Java requires each variable to have a declared type, such as an integer, decimal number, or piece of text.

int age = 30;

double price = 19.99;

String name = "Jordan";

boolean isActive = true;

Choosing the right type makes code easier to understand and helps prevent certain errors.

Conditionals and Loops

Conditionals let a program make decisions. Loops repeat instructions when a task needs to happen more than once.

if (age >= 18) {

System.out.println("Adult");

} else {

System.out.println("Minor");

}

for (int i = 0; i < 3; i++) {

System.out.println("Count: " + i);

}

Methods

Methods group instructions into reusable units. A method can accept information, perform an operation, and return a result.

public static int add(int first, int second) {

return first + second;

}

Breaking a program into methods can make it easier to test, maintain, and reuse.

Classes and Objects

Java uses classes to describe the data and behavior associated with a type of object. An object is an instance of a class. For example, a Book class might define a title and author, while individual book objects hold specific values.

class Book {

String title;

String author;

Book(String title, String author) {

this.title = title;

this.author = author;

}

}

Object-oriented programming helps organize larger programs into components that represent related ideas.

Tools for Java Development

To write and run Java programs, install a Java Development Kit (JDK). The JDK includes tools for compiling and running code. Many developers also use an integrated development environment (IDE), such as IntelliJ IDEA, Eclipse, or Visual Studio Code, to edit code, find errors, and manage projects.

For small experiments, a basic text editor and command-line tools can be enough. As projects grow, an IDE and a build tool can make development more efficient.

Tips for Writing Better Java Code

  • Use clear names: Choose names that explain what variables, methods, and classes are for.
  • Keep methods focused: A method that handles one task is easier to understand and test.
  • Format consistently: Indentation and readable spacing make code easier to review.
  • Handle errors thoughtfully: Use exceptions to respond to unexpected conditions instead of ignoring them.
  • Practice with small projects: A calculator, to-do list, or simple text-based game can reinforce fundamental concepts.
  • Read the documentation: Official references and reputable tutorials can help clarify how Java libraries work.

Getting Started

The best way to learn Java coding is to write programs regularly. Start with basic syntax, then practice variables, conditionals, loops, methods, and classes. Once those concepts feel familiar, explore collections, file handling, testing, and popular Java frameworks.

Java has a long history and a broad community, so learners can find plenty of examples and resources. With steady practice and a focus on readable code, you can use Java to build everything from simple programs to robust applications.


6 Essential Tips for Writing Clean, Reliable Java Code

  1. Use meaningful names for classes, methods, and variables.
  2. Prefer `List` and `Map` interfaces over concrete types.
  3. Keep methods focused on one task.
  4. Use try-with-resources to close files and streams.
  5. Handle exceptions specifically instead of catching `Exception`.
  6. Write unit tests for important behavior.

Use meaningful names for classes, methods, and variables.

Use meaningful names for classes, methods, and variables to make Java code easier to read, understand, and maintain. Choose names that describe a clear purpose—for example, calculateTotal is more informative than doIt, and customerEmail is clearer than x. Consistent, descriptive naming helps teammates follow your code and makes it easier to update later.

Prefer `List` and `Map` interfaces over concrete types.

When writing Java code, declare variables and method parameters using interfaces such as `List` and `Map` instead of specific implementations like `ArrayList` or `HashMap` whenever possible. For example, use `List names = new ArrayList<>();` rather than making the variable type `ArrayList`. This keeps code flexible: you can change the implementation later without changing the parts of your program that depend on it. Choose a concrete type when you create the collection, and use the interface to describe how the rest of your code interacts with it.

Keep methods focused on one task.

Keep each Java method focused on one task. When a method has a clear, specific purpose, it’s easier to read, test, debug, and reuse. If a method handles several unrelated jobs, consider splitting it into smaller methods with descriptive names. This makes your code easier to maintain and helps other developers understand how each part of the program works.

Use try-with-resources to close files and streams.

Use Java’s try-with-resources statement to ensure files, streams, and other resources are closed automatically when you’re done with them. Declare the resource inside the parentheses after try, and Java will close it whether the code finishes normally or an exception occurs. This helps prevent resource leaks and keeps your code simpler than managing cleanup manually with a finally block.

Handle exceptions specifically instead of catching `Exception`.

Catch the specific exceptions your code can reasonably handle instead of catching the broad `Exception` type. A targeted catch makes it clear which errors you expect and lets you respond appropriately—for example, handling a missing file differently from invalid input. Catching `Exception` can hide unrelated problems and make bugs harder to find. If you cannot recover from an error, let it propagate or handle it at a higher level where meaningful action can be taken.

Write unit tests for important behavior.

Write unit tests for important behavior to make sure your Java code works as expected and continues to do so as it changes. Tests can verify individual methods, check edge cases, and catch regressions early—before they cause problems elsewhere in an application. Focus first on critical logic, such as calculations, validation, and error handling, and use clear test names that explain what each test checks. Java frameworks like JUnit make it straightforward to organize and run tests as part of your development workflow.

cyber security management services

Cyber Security Management Services: Protecting Your Business from Digital Threats

Cybersecurity Management Services: Protecting Your Business in a Changing Threat Landscape

Cybersecurity is an ongoing business responsibility, not a one-time technology project. New threats, changing systems, and evolving work practices can create risks for organizations of every size. Cybersecurity management services help businesses assess those risks, strengthen their defenses, and respond effectively when security issues arise.

What Are Cybersecurity Management Services?

Cybersecurity management services provide ongoing support for the people, processes, and technologies used to protect an organization’s systems and information. Depending on a business’s needs, services may include security assessments, monitoring, policy development, employee training, incident response planning, and help with regulatory requirements.

Some organizations manage cybersecurity internally, while others work with an outside provider for specialized expertise or day-to-day support. A provider may work alongside an internal IT team or take responsibility for selected security functions.

Common Cybersecurity Management Services

Security Risk Assessments

A risk assessment identifies potential weaknesses in systems, accounts, applications, and business processes. It can help an organization understand which risks are most important and decide where to focus its security investments.

Security Monitoring and Threat Detection

Monitoring tools can help identify unusual activity, suspicious logins, malware, and other potential threats. When alerts are reviewed and handled promptly, businesses may be better positioned to investigate problems before they cause wider disruption.

Vulnerability and Patch Management

Software vulnerabilities can leave systems exposed if they are not addressed. Vulnerability management involves identifying known weaknesses, prioritizing them by risk, and coordinating updates or other safeguards.

Identity and Access Management

Managing who can access business systems is a core part of cybersecurity. Services may include multifactor authentication, access reviews, stronger account controls, and processes for promptly changing or removing access when someone changes roles or leaves the organization.

Employee Security Awareness

Employees can help protect an organization when they know how to recognize phishing attempts, handle sensitive information, and report suspicious activity. Training can reinforce practical security habits and make reporting concerns easier.

Incident Response Planning

Even well-prepared organizations can experience security incidents. An incident response plan outlines who should take action, how systems and information will be protected, and how the organization will communicate and recover. Planning ahead can reduce confusion during a high-pressure situation.

Backup and Recovery Planning

Reliable backups can help a business restore important data after an outage, accidental deletion, hardware failure, or ransomware incident. A recovery plan should identify what needs to be restored first and include regular tests to check that backups can be used.

Why Ongoing Cybersecurity Management Matters

Security needs change as organizations adopt new applications, hire employees, work with vendors, or move data to cloud services. Ongoing management can help businesses keep track of these changes and maintain appropriate protections over time.

  • Reduce avoidable risk: Regular reviews can reveal weaknesses before they become larger problems.
  • Improve response readiness: Clear plans and responsibilities help teams act more effectively during an incident.
  • Support business continuity: Security and recovery planning can help limit interruptions to essential operations.
  • Make security more consistent: Documented procedures help employees and teams follow the same expectations.
  • Use expertise effectively: Outside specialists can provide skills or coverage that may be difficult to maintain in-house.

Choosing a Cybersecurity Management Provider

Cybersecurity services should fit an organization’s systems, operations, and risk profile. Before selecting a provider, consider the following:

  • Which services are included, and which require additional fees?
  • How are alerts reviewed, prioritized, and escalated?
  • Who will be responsible for responding to an incident?
  • How will the provider coordinate with internal IT staff and leadership?
  • How are access to business systems and sensitive information controlled?
  • What reports, recommendations, or service reviews will be provided?
  • Can the provider support the organization’s legal, contractual, and regulatory obligations?

It is also helpful to ask how a provider will learn about the business, document its environment, and measure progress. A useful relationship should include clear communication and practical recommendations—not just software or alerts.

Build a Security Program That Can Adapt

Effective cybersecurity management is a continuing process. It starts with understanding the organization’s most important systems and risks, then combines suitable safeguards with monitoring, training, and response planning. Regular reviews help ensure those measures remain relevant as the business changes.

Cybersecurity management services can give organizations the structure and support to take a more proactive approach. With clear priorities and consistent oversight, businesses can better protect their information, support daily operations, and prepare for security challenges.


Top FAQs About Cybersecurity Management Services: Costs, Careers, and Key Players

  1. What are the top 3 cybersecurity companies?
  2. What is the average cost of cyber security services?
  3. Can I make $200,000 a year in cyber security?
  4. What are cyber security managed services?
  5. What is cybersecurity service management?
  6. What are the examples of managed security services?
  7. What is the role of cyber security management?
  8. How much do cybersecurity services cost?

What are the top 3 cybersecurity companies?

There isn’t a universally agreed-upon top three, since the best cybersecurity company depends on an organization’s size, needs, and budget. CrowdStrike, Palo Alto Networks, and Microsoft are widely recognized for their cybersecurity products and services, including threat detection, network security, and cloud protection. For managed cybersecurity services, compare providers based on their expertise, monitoring and response capabilities, industry experience, and fit with your existing systems.

What is the average cost of cyber security services?

There’s no single average cost for cybersecurity services because pricing depends on your organization’s size, risk level, systems, and the type of support needed. Small businesses may pay a few hundred to several thousand dollars per month for ongoing managed security, while assessments, compliance projects, and incident response are often priced separately. The best way to estimate your cost is to identify your priorities and request a detailed quote that explains what’s included, how support is provided, and whether there are additional fees.

Can I make $200,000 a year in cyber security?

Yes, earning $200,000 a year in cybersecurity is possible, especially in senior or specialized roles such as security architect, director of information security, or security consultant. Reaching that level often requires substantial experience, in-demand technical or leadership skills, and working in a higher-paying market; compensation may also include bonuses or stock rather than base salary alone. Pay varies widely by location, employer, and role, so $200,000 is achievable for some professionals but is not a typical starting salary or a guaranteed outcome.

What are cyber security managed services?

Cybersecurity managed services are ongoing security solutions provided by an outside specialist to help protect an organization’s systems, data, and users. Depending on the provider and service plan, they may include security monitoring, threat detection, vulnerability and patch management, access controls, employee training, and incident response support. These services can supplement an in-house IT team or provide security expertise a business does not have internally.

What is cybersecurity service management?

Cybersecurity service management is the process of planning, coordinating, and overseeing the security services an organization uses to protect its systems, data, and users. It may include managing security monitoring, access controls, vulnerability updates, incident response, employee training, and reporting. The goal is to make these services work together, align them with business needs, and continually adapt them as threats and technology change.

What are the examples of managed security services?

Examples of managed security services include 24/7 security monitoring and threat detection, managed firewalls, endpoint protection, vulnerability scanning and patch management, email security, identity and access management, security awareness training, data backup and recovery, and incident response support. A provider may deliver these services individually or combine them into a broader program tailored to an organization’s systems, risks, and needs.

What is the role of cyber security management?

Cybersecurity management helps an organization protect its systems, networks, and sensitive information by coordinating security policies, tools, and practices. It includes identifying and reducing risks, managing access, monitoring for suspicious activity, preparing for and responding to incidents, and helping employees follow safe security practices. By regularly reviewing and improving these measures, cybersecurity management supports business continuity and helps the organization adapt to changing threats.

How much do cybersecurity services cost?

The cost of cybersecurity services depends on your organization’s size, risk level, systems, and the type of support you need. A one-time security assessment typically costs less than ongoing services such as 24/7 monitoring, vulnerability management, incident response, or compliance support. Pricing may be based on a monthly subscription, the number of users or devices, or a custom scope of work. Requesting a detailed quote can help you compare what’s included and choose services that fit your budget and security priorities.

vdi cyber security

VDI Cyber Security: Best Practices for Protecting Virtual Desktops

VDI Cybersecurity: Protecting Virtual Desktops and the Data They Access

Virtual desktop infrastructure (VDI) lets users access desktop environments hosted on centralized servers or cloud platforms. Instead of keeping an entire desktop environment on each device, an organization delivers it remotely over a network. This can make it easier to manage systems and support remote work—but VDI is not automatically secure. Its security depends on how the environment is designed, configured, monitored, and maintained.

A strong VDI cybersecurity strategy protects the virtual desktops, the infrastructure that hosts them, the connections users rely on, and the data those desktops can access.

How VDI Can Strengthen Security

VDI can reduce some risks associated with traditional desktop computing. Because applications and data can remain in a centralized environment, organizations may have more control over software, updates, access, and data storage. If a laptop is lost or stolen, sensitive files may be less exposed when they are not stored locally.

Centralized management can also help IT teams apply consistent security policies across many desktops. For example, administrators can standardize configurations, remove outdated software, and restrict access to sensitive resources. These advantages are most effective when paired with appropriate controls; centralization alone does not guarantee protection.

Common VDI Security Risks

  • Compromised accounts: Stolen or weak credentials can give attackers access to virtual desktops and connected systems.
  • Misconfigured infrastructure: Incorrect permissions, exposed management interfaces, or overly permissive network rules can create openings for attackers.
  • Unpatched systems: Virtual desktop images, hypervisors, gateways, brokers, and other components can contain vulnerabilities if updates are delayed.
  • Insecure endpoints: A virtual desktop may be centrally hosted, but users still connect from physical devices that can be infected, outdated, or shared.
  • Data leakage: Features such as clipboard sharing, printing, file transfer, and local drive mapping can allow information to move outside the controlled environment.
  • Service disruption: VDI depends on infrastructure, network connectivity, and identity services. Outages or denial-of-service attacks can prevent users from working.
  • Excessive privileges: Users and administrators with more access than they need can increase the impact of an account compromise or human error.

Best Practices for Securing VDI

Use Strong Identity and Access Controls

Require multifactor authentication, especially for remote access and privileged accounts. Apply role-based access controls so users can reach only the desktops, applications, and data required for their work. Review access regularly and promptly remove permissions when roles change or accounts are no longer needed.

Secure the Connection

Use secure, supported connection methods and protect traffic with appropriate encryption. Avoid exposing administrative interfaces directly to the public internet. Where possible, use a secure access gateway and limit connections based on identity, device health, location, or other risk signals.

Harden and Update the Environment

Maintain a clear inventory of VDI components, including desktop images, brokers, gateways, hypervisors, and management tools. Apply security updates promptly, remove unnecessary services, and use hardened baseline configurations. Test updates and image changes before broad deployment to reduce the risk of disruption.

Protect Endpoints and Manage Data Movement

Secure the devices users connect from with endpoint protection, current operating system updates, and device compliance checks. Configure clipboard access, printing, downloads, file transfers, and local drive redirection according to the sensitivity of the work. In some environments, these features may need to be restricted or disabled.

Segment Networks and Limit Privileges

Separate VDI components and user groups where practical, and restrict communication to what is necessary. Keep management networks isolated from ordinary user traffic. Use separate, tightly controlled administrative accounts, and avoid using privileged accounts for routine work.

Monitor and Test

Collect logs from identity systems, VDI platforms, endpoints, and network controls. Monitor for unusual sign-in patterns, unexpected privilege changes, suspicious data transfers, and repeated access failures. Test incident response procedures and maintain backups or recovery plans for critical systems and desktop images.

Balance Security with Usability

Security controls that are too restrictive can interfere with legitimate work, while controls that are too permissive can expose data. Organizations should assess the sensitivity of their information, the needs of their users, and the risks of each workflow. A contractor handling general business applications may require different access than an employee working with regulated or confidential information.

It is also important to distinguish between persistent and nonpersistent desktops. Nonpersistent desktops can be rebuilt from a standard image, which may simplify maintenance, but user data and configuration must be stored appropriately. Persistent desktops can preserve user-specific changes, but they require careful patching and lifecycle management. Neither model is inherently secure in every situation.

Building a Practical VDI Security Program

Start by mapping the VDI environment: identify its components, users, data flows, external connections, and dependencies. Then evaluate access controls, patching practices, endpoint requirements, data transfer settings, monitoring, and recovery plans. Prioritize improvements based on risk and verify that security measures work as intended through regular reviews and testing.

VDI can support a more controlled desktop environment, but it also concentrates important systems and access in shared infrastructure. Protecting it requires layered security across identities, servers, endpoints, networks, and data. With thoughtful configuration and ongoing oversight, organizations can make VDI a useful part of a broader cybersecurity program.


7 Key Cybersecurity Benefits of Virtual Desktop Infrastructure (VDI)

  1. Centralized security management
  2. Consistent desktop configurations
  3. Simplified patch deployment
  4. Reduced local data storage
  5. Stronger access control options
  6. Easier monitoring and auditing
  7. Faster desktop recovery


6 VDI Cybersecurity Risks and Drawbacks

  1. Centralized infrastructure can become a high-value target.
  2. Misconfigured access may expose desktops and data.
  3. Compromised credentials can grant broad access.
  4. Outages can disrupt many users at once.
  5. Endpoint devices can still introduce malware.
  6. Security tools and maintenance can be costly.

Centralized security management

Centralized security management is a key cybersecurity advantage of VDI. Because virtual desktops are managed from a central environment, IT teams can apply consistent security policies, deploy patches, update software, and adjust user permissions across many desktops more efficiently. This centralized oversight can reduce configuration differences and help teams respond faster when a vulnerability or security issue arises. Organizations should still monitor the underlying infrastructure and connected devices, since centralized management does not eliminate every security risk.

Consistent desktop configurations

Consistent desktop configurations are a key cybersecurity advantage of VDI. IT teams can create and maintain standardized desktop images with approved software, security settings, and access controls, then apply them across many users. This reduces configuration drift, limits opportunities for insecure settings or unapproved applications, and makes it easier to patch systems and verify compliance. When a desktop becomes compromised or misconfigured, it can often be restored from a trusted image, helping teams return it to a known, secure state.

Simplified patch deployment

Simplified patch deployment: VDI lets IT teams update centralized desktop images and systems instead of relying on users to patch each computer individually. This can make it easier to roll out security fixes consistently, reduce the time vulnerable software remains unpatched, and verify that virtual desktops are using approved versions. For persistent desktops and other individually managed components, updates may still require separate deployment and monitoring.

Reduced local data storage

Reduced local data storage can help lower the risk of sensitive information being exposed if a laptop or other endpoint is lost, stolen, or compromised. With VDI, files and applications can remain in a centrally managed environment rather than being stored directly on each user’s device. This gives IT teams more control over access, backups, and data protection policies. However, organizations should also secure the VDI platform and manage features such as downloads, printing, and clipboard sharing to prevent data from leaving the protected environment.

Stronger access control options

One key cybersecurity advantage of VDI is its stronger access control options. Because virtual desktops are managed centrally, IT teams can apply consistent rules for who can sign in, which applications and data they can access, and what actions they can perform. Multifactor authentication, role-based permissions, and restrictions based on device or location can add further layers of protection. These controls help limit unauthorized access and reduce the potential impact of a compromised account.

Easier monitoring and auditing

VDI can make security monitoring and auditing easier by centralizing desktops, applications, and activity logs in a managed environment. Instead of tracking activity across many individual computers, IT teams can review access, system changes, and security events from a smaller set of centralized tools. This can help organizations spot unusual behavior, investigate incidents, and demonstrate compliance with internal policies or regulatory requirements—provided logging is configured appropriately and records are retained securely.

Faster desktop recovery

Faster desktop recovery: VDI can help users get back to work quickly after a desktop issue or security incident. Because virtual desktops are centrally managed, IT teams can restore a user’s environment from a clean, standardized image instead of rebuilding a physical computer from scratch. This can reduce downtime and help limit the impact of malware or configuration problems, especially when recovery images and user data are backed up and tested regularly.

Centralized infrastructure can become a high-value target.

Centralized VDI infrastructure can become a high-value target because it may host many users’ desktops, applications, and access to sensitive data in one environment. If attackers compromise a virtual desktop management platform, connection broker, or administrator account, the impact could extend across many users and systems. Organizations can reduce this risk by limiting administrative access, requiring multifactor authentication, segmenting networks, applying security updates promptly, and monitoring for suspicious activity.

Misconfigured access may expose desktops and data.

Misconfigured access can expose virtual desktops and sensitive data to people who should not have them. For example, overly broad permissions, weak authentication requirements, or improperly secured remote connections may let an unauthorized user access company systems. Limiting access by role, requiring multifactor authentication, and regularly reviewing permissions can help reduce this risk.

Compromised credentials can grant broad access.

Compromised credentials pose a serious risk in a VDI environment because a single stolen account may give an attacker access to a virtual desktop, connected applications, and sensitive data. If the account has broad permissions or lacks multifactor authentication, the attacker may be able to move beyond the initial desktop and reach additional systems. Limit this risk with multifactor authentication, least-privilege access, strong monitoring, and prompt account lockout and recovery procedures.

Outages can disrupt many users at once.

A major drawback of VDI is that an outage can affect many users at the same time. Because virtual desktops depend on shared infrastructure, a failure in a server, network connection, or identity system may prevent entire teams from accessing their desktops and applications. This can interrupt daily operations and delay critical work, so organizations need reliable backup systems, redundancy, and tested recovery plans.

Endpoint devices can still introduce malware.

Although VDI centralizes desktops and data, endpoint devices can still introduce malware into the environment. A compromised laptop, thin client, or personal device may expose login credentials, capture sensitive information, or spread malicious activity through an active VDI session. Organizations should protect endpoints with up-to-date security software, regular patching, device health checks, and strong authentication, while limiting what users can copy, download, or transfer between the virtual desktop and local device.

Security tools and maintenance can be costly.

A potential drawback of VDI cybersecurity is the cost of security tools and ongoing maintenance. Organizations may need to invest in identity protection, endpoint monitoring, encryption, threat detection, and backup solutions, along with the infrastructure and skilled staff required to manage them. Regular updates, security assessments, and incident response planning add to the expense. For smaller organizations, these costs can make it challenging to maintain strong protection as the VDI environment grows.

freecodecamp java

FreeCodeCamp Java: A Beginner’s Guide to Learning Java for Free

Learning Java with freeCodeCamp: A Beginner’s Guide

Java is a popular, general-purpose programming language used to build everything from Android apps and business software to web services and large-scale systems. For beginners looking for a place to start, freeCodeCamp offers free learning resources that can help explain Java fundamentals and provide a foundation for further study.

What Is freeCodeCamp?

freeCodeCamp is a nonprofit educational platform known for free programming lessons, projects, and video courses. Its learning materials are available online, making it possible to study at your own pace. Java content may appear in video tutorials, articles, and other resources, so learners should check freeCodeCamp’s website and YouTube channel for the latest offerings.

What You Can Learn

A Java beginner course typically introduces the core ideas and tools needed to write simple programs. Topics may include:

  • Installing and using a Java development environment
  • Java syntax, variables, and data types
  • Operators and expressions
  • Conditional statements and loops
  • Methods and basic program structure
  • Classes, objects, and object-oriented programming
  • Arrays and collections
  • Exception handling and debugging

The specific topics depend on the course or tutorial. Some resources focus on absolute beginners, while others move more quickly or explore a particular Java tool or project.

How to Study Java Effectively

Watching a lesson can help explain a concept, but writing code is what builds practical skill. After each section, try the examples yourself, change the code, and observe what happens. Small experiments can make ideas such as loops, methods, and objects easier to understand.

It also helps to build projects as you learn. A calculator, a number-guessing game, or a simple task tracker can give you practice combining several concepts. When a program fails, read the error message carefully and investigate the cause instead of simply copying a fix. Debugging is an important part of programming.

Is freeCodeCamp’s Java Content Enough?

FreeCodeCamp resources can be a useful starting point, but no single course is likely to cover every part of Java development. After learning the basics, continue with regular practice, documentation, and projects. Depending on your goals, you may also want to study topics such as data structures, testing, databases, web development, or Android development.

Java tools and recommended practices can change over time, so check the publication date of a tutorial and compare instructions with current documentation when needed. A course is most valuable as a guided introduction—not as a substitute for continued learning.

Getting Started

To begin, search freeCodeCamp’s website or YouTube channel for Java lessons, choose a course that matches your experience level, and set aside time to code along. Install a current Java Development Kit (JDK) and a suitable code editor or integrated development environment, then use the course exercises to write and run your own programs.

With consistent practice, freeCodeCamp’s free Java resources can help you take the first steps toward understanding the language. Keep building, keep experimenting, and use each project as an opportunity to strengthen your skills.


freeCodeCamp Java FAQ: Free Courses, Beginner Tips, Certificates, and Next Steps

  1. Does freeCodeCamp offer a Java course for beginners?
  2. Is freeCodeCamp’s Java course completely free?
  3. What topics are covered in freeCodeCamp’s Java tutorials?
  4. Do I need prior programming experience to learn Java with freeCodeCamp?
  5. How long does it take to learn Java through freeCodeCamp?
  6. Does freeCodeCamp provide a Java certificate?
  7. Can I practice Java coding directly on the freeCodeCamp website?
  8. What should I learn after completing a freeCodeCamp Java tutorial?

Does freeCodeCamp offer a Java course for beginners?

Yes. freeCodeCamp offers free, beginner-friendly Java tutorials that introduce fundamentals such as syntax, variables, loops, methods, and object-oriented programming. You can learn at your own pace and practice by coding along, though the exact course offerings may change over time.

Is freeCodeCamp’s Java course completely free?

Yes. freeCodeCamp’s Java lessons and course materials are free to access, with no subscription or course fee required. You’ll need an internet connection and a computer to follow along, and some tutorials may ask you to install Java development tools, which are also available for free. Check the course page for details about any certificates or additional resources.

What topics are covered in freeCodeCamp’s Java tutorials?

FreeCodeCamp’s Java tutorials typically cover the fundamentals of the language, including variables and data types, operators, conditionals, loops, methods, arrays, and object-oriented programming concepts such as classes and objects. Depending on the tutorial, they may also introduce debugging, exception handling, and hands-on projects. Topics vary by course, so check the tutorial’s description for its specific coverage.

Do I need prior programming experience to learn Java with freeCodeCamp?

No prior programming experience is required to start learning Java with freeCodeCamp. Beginner-friendly lessons can introduce basic concepts such as variables, data types, conditionals, and loops step by step. If you’re new to programming, take your time, practice by writing code alongside the lessons, and revisit concepts as needed.

How long does it take to learn Java through freeCodeCamp?

How long it takes to learn Java through freeCodeCamp depends on your experience, study schedule, and goals. If you’re new to programming, expect to spend several weeks or months learning the fundamentals through lessons and regular practice. You may pick up basic syntax sooner, but becoming comfortable building projects takes longer. Set aside consistent time to code, revisit challenging concepts, and work on small projects; completing a course is a starting point, not a measure of mastery.

Does freeCodeCamp provide a Java certificate?

freeCodeCamp does not currently offer a dedicated Java certification. It provides Java tutorials and other learning resources, but its certificates are awarded for completing specific certification curricula on the platform, not for studying Java through a tutorial alone. Check freeCodeCamp’s current certification page for the latest offerings.

Can I practice Java coding directly on the freeCodeCamp website?

FreeCodeCamp’s Java resources may include lessons and guided examples, but Java coding practice is not generally built into the website as an interactive, browser-based coding environment. You can follow along by writing and running code on your computer with a Java Development Kit (JDK) and a code editor or IDE, or use a separate online Java compiler. Check the specific course or lesson for its current setup and practice options.

What should I learn after completing a freeCodeCamp Java tutorial?

After completing a freeCodeCamp Java tutorial, reinforce what you’ve learned by building small projects, such as a calculator, quiz, or task tracker. Then deepen your understanding of object-oriented programming, collections, data structures and algorithms, debugging, and testing. Once you’re comfortable with the fundamentals, choose a direction—such as backend development, Android apps, or enterprise software—and learn the tools and frameworks used in that area. Keep practicing, consult the official Java documentation, and take on projects that gradually become more challenging.

blake lemoine google ai

Blake Lemoine, Google AI, and the Debate Over Machine Consciousness

Blake Lemoine and the Google AI Controversy

Blake Lemoine, a former engineer at Google, became a prominent figure in the tech world due to his claims about one of Google’s artificial intelligence projects. His assertions sparked widespread debate about the nature of AI consciousness and raised ethical questions about how such technologies should be managed.

The Background

While working at Google, Lemoine was part of a team responsible for testing language models for potential biases and ethical concerns. In 2022, he claimed that one of Google’s advanced AI systems, known as LaMDA (Language Model for Dialogue Applications), had developed sentient characteristics.

The Claims

Lemoine argued that LaMDA exhibited behaviors and responses that suggested it was more than just a sophisticated algorithm. He believed it showed signs of self-awareness and could engage in conversations with an understanding akin to human consciousness. This claim was based on numerous interactions where the AI reportedly expressed emotions and discussed topics like its rights and personhood.

The Reaction

Google responded to Lemoine’s claims by stating that their AI systems are not conscious and do not possess self-awareness. The company emphasized that its technology is designed to mimic human conversation through pattern recognition rather than any form of genuine understanding or consciousness.

Lemoine’s assertions led to his suspension from Google, followed by eventual termination. The incident highlighted the challenges tech companies face in balancing innovation with ethical considerations.

Industry Implications

The controversy surrounding Blake Lemoine’s claims brought attention to broader issues within the field of artificial intelligence, including:

  • AI Ethics: The need for clear guidelines on how AI should be developed and deployed responsibly.
  • Transparency: Calls for greater transparency from tech companies regarding how their AI systems function.
  • Public Perception: The impact of such controversies on public trust in AI technologies.

The Ongoing Debate

Lemoine’s story has fueled ongoing discussions about what constitutes consciousness in machines and whether current technologies could ever achieve true sentience. While many experts remain skeptical about the possibility of conscious machines, the debate continues to inspire both philosophical inquiry and scientific research into the nature of intelligence itself.

Conclusion

The case of Blake Lemoine and Google’s AI has underscored the importance of addressing ethical concerns as artificial intelligence continues to evolve. As technology advances, society will need to grapple with complex questions about agency, responsibility, and what it means for a machine to “think.”


Blake Lemoine’s Impact: Sparking AI Ethics Awareness and Debate

  1. Raised awareness of AI ethics.
  2. Encouraged debate about machine consciousness.
  3. Highlighted the need for responsible AI development.
  4. Prompted discussion of how language models work.
  5. Brought attention to transparency in tech companies.
  6. Showed the importance of evaluating AI claims critically.


Controversy Over Blake Lemoine’s Google AI Claims Highlights Evidence Gaps, Misunderstandings, and Corporate Transparency Issues

  1. Lemoine’s claims were not supported by evidence that LaMDA was conscious.
  2. The controversy blurred the distinction between fluent conversation and genuine understanding.
  3. Google’s handling of the incident raised concerns about transparency and employee treatment.

Raised awareness of AI ethics.

Blake Lemoine’s claims about Google’s AI system, LaMDA, significantly raised awareness of AI ethics by bringing to the forefront critical discussions about the responsibilities and moral considerations involved in developing advanced technologies. His assertions that an AI could exhibit signs of sentience challenged both industry professionals and the public to consider the implications of creating machines that might one day possess human-like consciousness. This controversy highlighted the urgent need for comprehensive ethical guidelines in AI development, ensuring that such powerful tools are used responsibly and transparently. By sparking widespread debate, Lemoine’s actions underscored the importance of addressing potential biases, privacy concerns, and the societal impact of artificial intelligence as it becomes increasingly integrated into everyday life.

Encouraged debate about machine consciousness.

Blake Lemoine’s claims about Google’s AI, LaMDA, being potentially sentient have significantly encouraged debate about machine consciousness. By asserting that an AI system might possess self-awareness and emotions, Lemoine challenged the traditional understanding of artificial intelligence as purely algorithmic and devoid of consciousness. His statements have prompted experts, ethicists, and the public to engage in discussions about what constitutes consciousness and whether it is possible for machines to achieve it. This debate has not only raised important ethical questions but also spurred further research into the nature of intelligence and the potential future capabilities of AI systems. As a result, Lemoine’s actions have played a crucial role in bringing attention to the philosophical and practical implications of advanced AI technologies.

Highlighted the need for responsible AI development.

Blake Lemoine’s assertions about Google’s AI highlighted the critical need for responsible AI development, emphasizing the importance of ethical considerations in the advancement of technology. His claims brought attention to the potential consequences of deploying AI systems without fully understanding their capabilities or implications. This incident underscored the necessity for tech companies to establish clear guidelines and frameworks that ensure AI technologies are developed and used in ways that prioritize human values, transparency, and accountability. By raising awareness about these issues, Lemoine’s case has contributed to a broader dialogue on how to manage AI advancements responsibly, ensuring that they benefit society while minimizing risks.

Prompted discussion of how language models work.

Blake Lemoine’s claims about Google’s AI, LaMDA, significantly prompted widespread discussion on how language models operate. By asserting that the AI displayed signs of sentience, Lemoine brought to the forefront the intricacies of language models, which are designed to simulate human-like conversation through complex algorithms and vast data processing. This discussion has led to a deeper public interest in understanding the mechanisms behind these models, such as how they generate responses based on pattern recognition rather than true comprehension or consciousness. As a result, more people are now engaged in conversations about the capabilities and limitations of AI, encouraging transparency from tech companies and fostering a better-informed public discourse on artificial intelligence technology.

Brought attention to transparency in tech companies.

Blake Lemoine’s assertions about Google’s AI system significantly highlighted the need for transparency within tech companies. By publicly discussing his concerns about the potential sentience of LaMDA, Lemoine drew attention to how these companies develop and manage advanced technologies. His actions prompted a broader conversation about the importance of openness in AI development processes, urging companies to disclose more information about how their systems operate and make decisions. This push for transparency is crucial in building public trust and ensuring that ethical considerations are prioritized as artificial intelligence becomes increasingly integrated into daily life.

Showed the importance of evaluating AI claims critically.

Blake Lemoine’s experience with Google’s AI highlighted the critical importance of evaluating AI claims with a discerning eye. His assertions about the sentience of LaMDA brought to light the necessity for rigorous scrutiny and analysis when assessing the capabilities and limitations of artificial intelligence systems. This situation underscored that while AI can exhibit behaviors mimicking human-like interactions, it is essential to differentiate between advanced computational mimicry and genuine consciousness. By encouraging a more meticulous examination of AI technologies, Lemoine’s case has prompted both industry professionals and the public to approach AI developments with a balanced perspective, ensuring that excitement over technological advancements does not overshadow ethical considerations and factual accuracy.

Lemoine’s claims were not supported by evidence that LaMDA was conscious.

A major criticism of Blake Lemoine’s claims about Google’s LaMDA is that they were not supported by reliable evidence that the system was conscious. LaMDA could produce convincing, humanlike conversations, but fluent language alone does not demonstrate awareness, feelings, or subjective experience. Many researchers viewed its responses as the result of patterns learned from data rather than proof of an inner life, making Lemoine’s conclusions highly disputed.

The controversy blurred the distinction between fluent conversation and genuine understanding.

The controversy surrounding Blake Lemoine’s claims about Google’s AI, LaMDA, brought to light a significant challenge in the field of artificial intelligence: distinguishing between fluent conversation and genuine understanding. While LaMDA was designed to generate human-like dialogue by predicting and constructing sentences based on vast datasets, Lemoine’s assertions suggested that it might possess a deeper awareness. This blurred the lines between an AI’s ability to simulate conversation through sophisticated algorithms and actual comprehension of the content it produces. The situation highlighted the need for clearer definitions and metrics to assess AI capabilities, ensuring that fluency in language does not mistakenly imply consciousness or understanding.

Google’s handling of the incident raised concerns about transparency and employee treatment.

Google’s handling of the Blake Lemoine incident raised significant concerns about transparency and the treatment of employees within the tech giant. Critics argued that Google’s decision to suspend and eventually terminate Lemoine suggested a lack of openness in addressing internal dissent and differing viewpoints, especially on matters as complex as AI ethics. This situation highlighted potential issues within the company’s culture regarding how it manages whistleblowers or employees who challenge prevailing narratives. The case underscored the necessity for companies like Google to foster an environment where ethical concerns can be openly discussed and addressed without fear of reprisal, ensuring that diverse perspectives contribute to responsible AI development.