cfchris.com

Loading

Archives August 2026

siem cyber

SIEM Cybersecurity: A Guide to Security Information and Event Management

SIEM in Cybersecurity: How Security Information and Event Management Works

Cyberattacks can leave clues across an organization’s computers, applications, networks, and cloud services. The challenge is finding those clues quickly and understanding whether they point to a real threat. Security information and event management (SIEM) helps by bringing security data together, analyzing it, and alerting teams to suspicious activity.

What Is SIEM?

SIEM, pronounced “sim,” is a cybersecurity technology that collects and analyzes security-related data from across an organization’s IT environment. It can gather logs and events from sources such as servers, endpoints, firewalls, identity systems, applications, and cloud platforms.

By reviewing this information in one place, security teams can spot patterns that might be difficult to see in separate systems. For example, an unusual login may look harmless on its own. When correlated with repeated failed attempts and unexpected access to sensitive files, it may signal a compromised account.

How Does SIEM Work?

Most SIEM solutions support several core activities:

  1. Data collection: The system receives logs and security events from connected sources.
  2. Normalization: It organizes data from different tools into a consistent format so events can be compared.
  3. Correlation and analysis: Rules, analytics, and sometimes machine learning identify relationships or unusual behavior across events.
  4. Alerting: When activity matches a detection rule or risk pattern, the SIEM creates an alert for investigation.
  5. Investigation and reporting: Analysts use search tools, dashboards, and timelines to examine activity and document findings.

SIEM systems can also retain event data for a set period, helping teams investigate incidents and meet applicable audit or compliance requirements. Retention capabilities and requirements vary by product and organization.

Why SIEM Matters for Cybersecurity

A SIEM can help security teams gain a broader view of activity across their environment. Its value often includes:

  • Centralized visibility: Security events from multiple systems can be reviewed in one place.
  • Threat detection: Correlation can reveal suspicious combinations of events that individual tools may not identify together.
  • Faster investigations: Searchable logs and event timelines can help analysts understand what happened and when.
  • Incident response support: Alerts and investigative context can help teams decide what actions to take.
  • Audit and compliance support: Reports and retained logs may help organizations demonstrate how security events are monitored and reviewed.

A SIEM is not a substitute for a complete security program. It works best alongside sound security practices, capable staff, clear response procedures, and effective controls such as multifactor authentication and endpoint protection.

Common SIEM Use Cases

Organizations use SIEM tools to monitor for a range of security concerns, including:

  • Repeated or unusual login attempts
  • Unexpected access to sensitive information
  • Suspicious changes to user accounts or permissions
  • Malware alerts and unusual endpoint behavior
  • Potential data exfiltration or unusual network traffic
  • Activity involving accounts, devices, or locations that differ from normal patterns

These detections depend on which data sources are connected and how the system is configured. A SIEM cannot reliably identify activity it cannot observe, and alerts require appropriate review.

SIEM Challenges to Consider

SIEM can strengthen security monitoring, but it also requires thoughtful implementation and ongoing maintenance. Common challenges include:

  • Alert fatigue: Too many low-value alerts can make it harder to prioritize genuine risks.
  • Incomplete data: Missing or poorly configured data sources can create gaps in visibility.
  • Complex setup: Detection rules and integrations often need to be tailored to an organization’s systems and risks.
  • Storage and cost: Collecting and retaining large volumes of logs can affect licensing, infrastructure, and operational costs.
  • Staffing and expertise: Analysts need time and training to investigate alerts and improve detection quality.

Organizations can address these challenges by prioritizing important data sources, tuning detection rules, setting clear alert-handling procedures, and regularly reviewing whether the SIEM is producing useful results.

SIEM and Related Security Technologies

SIEM is often used alongside other security tools. A security orchestration, automation, and response (SOAR) platform can help coordinate or automate parts of incident response. Extended detection and response (XDR) tools focus on detecting and responding to threats across connected security products. Some modern security platforms combine capabilities from several categories, but features and terminology differ among vendors.

How to Get Started with SIEM

Before choosing or deploying a SIEM, an organization should define what it needs to monitor and why. A practical starting point includes:

  1. Identify critical systems, sensitive data, and key security risks.
  2. Select the log sources that provide meaningful visibility into those risks.
  3. Establish detection priorities and define who will review alerts.
  4. Set retention, access, and privacy requirements for collected data.
  5. Test alerts and response procedures, then adjust rules based on real results.
  6. Measure performance using relevant indicators, such as investigation time and the proportion of actionable alerts.

The Role of SIEM in a Strong Security Program

SIEM helps organizations turn activity from many systems into information that security teams can investigate. Its effectiveness depends on the quality of the data it receives, the relevance of its detections, and the organization’s ability to respond.

With clear goals, reliable integrations, and ongoing tuning, SIEM can become an important part of cybersecurity monitoring. It gives teams a more connected view of potential threats—and a stronger foundation for investigating suspicious activity.


Understanding SIEM in Cybersecurity: Key FAQs Answered

  1. What is SIEM in cybersecurity?
  2. How does a SIEM system work?
  3. What are the main benefits of using SIEM?
  4. What types of security events can SIEM detect?
  5. What is the difference between SIEM, SOAR, and XDR?
  6. How much does SIEM cost, and what affects the price?

What is SIEM in cybersecurity?

SIEM, or security information and event management, is a cybersecurity technology that collects and analyzes log and event data from systems such as networks, servers, applications, and cloud services. By bringing this information together, SIEM helps security teams identify suspicious patterns, investigate potential threats, and respond to incidents. Its effectiveness depends on having useful data sources, well-tuned alerts, and a team or process to review and act on findings.

How does a SIEM system work?

A SIEM system works by collecting security logs and events from sources such as computers, applications, firewalls, and cloud services, then organizing and analyzing that data in one place. It looks for suspicious patterns by comparing events against detection rules and expected behavior. When it identifies activity that may indicate a threat, it generates an alert so security teams can investigate, respond, and review related events.

What are the main benefits of using SIEM?

The main benefits of using SIEM (security information and event management) include centralized visibility into security activity, faster detection of suspicious behavior, and more efficient incident investigations. By collecting and correlating data from systems such as networks, servers, endpoints, and cloud services, SIEM can help security teams identify patterns they might otherwise miss. It can also support incident response, provide searchable records for audits, and help organizations meet certain compliance requirements. Its effectiveness depends on collecting the right data, tuning alerts, and having people and processes in place to respond.

What types of security events can SIEM detect?

A SIEM can detect a wide range of security events by analyzing logs and activity from systems such as networks, endpoints, applications, identity platforms, and cloud services. Depending on the data sources and detection rules in place, it may flag repeated failed logins, unusual access to accounts or sensitive files, unexpected changes to permissions, malware alerts, suspicious network traffic, and signs of possible data exfiltration. SIEM can also connect events across different systems—for example, linking an unusual login to later access to critical data—to help security teams investigate potential threats. Detection coverage depends on how the SIEM is configured and the quality of the data it receives.

What is the difference between SIEM, SOAR, and XDR?

SIEM, SOAR, and XDR support cybersecurity in different ways. A SIEM collects and analyzes security data from across an organization to identify suspicious activity and generate alerts. SOAR helps teams coordinate and automate parts of their response, such as assigning incidents or running approved investigation steps. XDR detects and responds to threats across connected security layers, such as endpoints, email, and cloud services, often bringing related activity together for investigation. These tools can complement one another, but their capabilities vary by product.

How much does SIEM cost, and what affects the price?

SIEM costs vary widely, from a few hundred dollars per month for a small or managed service to much higher amounts for large, complex deployments. Pricing may be based on daily data volume, the number of monitored devices or users, data retention, and included features. Costs can also include setup, integrations, cloud storage, staff training, ongoing tuning, and analyst support. To compare options, estimate the log data you need to collect, identify essential capabilities, and ask vendors to clarify any usage limits or add-on fees.
Enhancing Cyber Security: The Role of Trusted Providers

The Importance of Cyber Security Providers

The Importance of Cyber Security Providers

In today’s digital age, where businesses and individuals rely heavily on technology, the need for robust cyber security measures has never been greater. Cyber threats are constantly evolving, becoming more sophisticated and dangerous. This is where cyber security providers play a crucial role in safeguarding sensitive information and protecting against cyber attacks.

What Do Cyber Security Providers Offer?

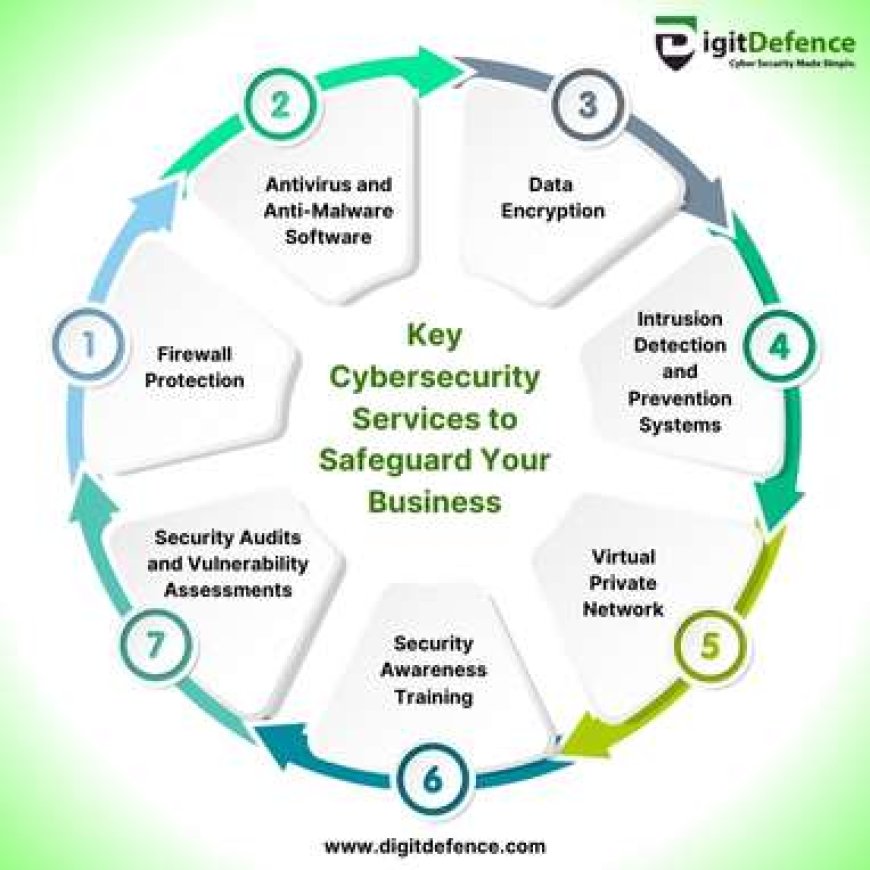
Cyber security providers offer a range of services designed to protect organizations from cyber threats. These services may include:

  • Network security: Securing networks from unauthorized access and monitoring for suspicious activities.
  • Endpoint security: Protecting individual devices such as computers, laptops, and mobile devices from malware and other threats.
  • Incident response: Developing strategies to respond to and mitigate the impact of cyber attacks.
  • Security awareness training: Educating employees on best practices for maintaining cyber security.
  • Vulnerability assessments: Identifying weaknesses in systems that could be exploited by attackers.

Why Choose a Cyber Security Provider?

Partnering with a cyber security provider offers several benefits:

  • Expertise: Cyber security providers have specialized knowledge and experience in identifying and mitigating cyber threats.
  • 24/7 Monitoring: Many providers offer around-the-clock monitoring to detect and respond to threats in real-time.
  • Compliance: Providers can help ensure that organizations comply with relevant regulations and standards related to data protection.
  • Cutting-Edge Technology: Providers stay abreast of the latest trends in cyber security technology to provide the most effective protection.
  • Cost-Effectiveness: Outsourcing cyber security services can be more cost-effective than maintaining an in-house team.

Conclusion

In conclusion, cyber security providers play a vital role in defending against the ever-growing threat of cyber attacks. By partnering with a reputable provider, organizations can enhance their defenses, protect sensitive data, and maintain business continuity in the face of evolving cyber threats.


Top 7 FAQs About Choosing and Working with Cyber Security Providers

  1. What services do cyber security providers offer?
  2. How can a cyber security provider help protect my business from cyber threats?
  3. What factors should I consider when choosing a cyber security provider?
  4. Do cyber security providers offer 24/7 monitoring services?
  5. How do cyber security providers stay updated on the latest threats and technologies?
  6. Can a cyber security provider help my business comply with data protection regulations?
  7. What are the benefits of outsourcing cyber security services to a provider?

What services do cyber security providers offer?

Cyber security providers offer a wide range of services to help organizations protect themselves against cyber threats. These services typically include network security to secure systems from unauthorized access, endpoint security to protect individual devices from malware, incident response to mitigate the impact of cyber attacks, security awareness training for employees, and vulnerability assessments to identify weaknesses in systems. By offering these comprehensive services, cyber security providers empower businesses to enhance their defenses, safeguard sensitive information, and maintain a secure digital environment in the face of evolving cyber threats.

How can a cyber security provider help protect my business from cyber threats?

A cyber security provider can help protect your business from cyber threats by offering a comprehensive range of services tailored to your specific needs. They can conduct thorough assessments to identify vulnerabilities in your systems, implement robust security measures to safeguard your network and data, provide continuous monitoring for early threat detection, offer incident response services to mitigate the impact of attacks, and educate your employees on best practices for maintaining cyber security. By leveraging their expertise and cutting-edge technology, a cyber security provider can significantly enhance your defenses against cyber threats and ensure the resilience of your business in the face of evolving risks.

What factors should I consider when choosing a cyber security provider?

When choosing a cyber security provider, several factors should be carefully considered to ensure that you select the right partner for your organization’s needs. Firstly, evaluate the provider’s expertise and experience in the field of cyber security, including their track record in handling similar challenges. Assess the range of services they offer and determine if they align with your specific requirements. Additionally, consider the provider’s approach to compliance with industry regulations and standards to ensure that your data is adequately protected. It is also essential to assess their response capabilities in the event of a cyber incident and their commitment to staying updated on emerging threats and technologies. Lastly, factor in considerations such as cost-effectiveness, scalability of services, and the provider’s reputation within the industry when making your decision.

Do cyber security providers offer 24/7 monitoring services?

Yes, many cyber security providers offer 24/7 monitoring services as part of their comprehensive security solutions. This continuous monitoring allows for real-time detection and response to potential cyber threats, ensuring that any suspicious activities are identified and addressed promptly. By providing around-the-clock monitoring, cyber security providers can help organizations enhance their security posture and mitigate the risks associated with cyber attacks effectively.

How do cyber security providers stay updated on the latest threats and technologies?

Cyber security providers stay updated on the latest threats and technologies through a variety of proactive measures. They continuously monitor industry trends, research emerging cyber threats, and analyze data from previous incidents to stay ahead of potential risks. Additionally, many providers participate in information-sharing networks, collaborate with other security professionals, attend conferences, and undergo regular training to enhance their knowledge and skills. By investing in ongoing education and leveraging a network of resources, cyber security providers ensure they are well-equipped to protect their clients from evolving cyber threats.

Can a cyber security provider help my business comply with data protection regulations?

A cyber security provider can indeed help your business comply with data protection regulations. These providers have expertise in understanding and implementing the necessary security measures to ensure that your organization meets the requirements set forth by data protection regulations. They can assist in identifying potential vulnerabilities, implementing appropriate safeguards, and monitoring compliance to mitigate risks of data breaches. By partnering with a cyber security provider, businesses can benefit from specialized knowledge and guidance to navigate the complex landscape of data protection regulations effectively.

What are the benefits of outsourcing cyber security services to a provider?

Outsourcing cyber security services to a provider offers numerous benefits to organizations. By partnering with a specialized cyber security provider, businesses can access expert knowledge and experience in identifying and mitigating cyber threats. These providers often offer 24/7 monitoring, ensuring that threats are detected and responded to in real-time. Additionally, outsourcing can help organizations ensure compliance with data protection regulations and standards, leverage cutting-edge technology for enhanced protection, and potentially reduce costs compared to maintaining an in-house cyber security team. Overall, outsourcing cyber security services to a reputable provider can strengthen an organization’s defenses and safeguard sensitive data against evolving cyber threats.

computer tech solutions

Computer Tech Solutions for a Smarter, More Secure Future

Computer Tech Solutions: Helping People and Businesses Work Smarter

Computers and digital tools play a central role in how people work, communicate, and manage everyday tasks. When technology works well, it can save time and make work easier. When it breaks down or falls behind, it can interrupt business, create security risks, and cause frustration. Computer tech solutions help people and organizations choose, maintain, and use technology more effectively.

What Are Computer Tech Solutions?

Computer tech solutions are services, tools, and strategies that address technology needs and problems. They can include setting up computers, repairing hardware, managing networks, protecting data, moving systems to the cloud, and providing ongoing technical support. The right solution depends on the user’s goals, budget, existing equipment, and security requirements.

Common Types of Technology Support

Computer Setup and Repair

Proper setup helps computers run reliably from the start. This may involve installing operating systems and applications, configuring user accounts, connecting printers, and transferring files from an older device. Repair services can help diagnose problems such as slow performance, failing components, software errors, or unexpected shutdowns.

Network and Wi-Fi Management

A dependable network allows computers, phones, printers, and other devices to communicate. Network support can include router configuration, Wi-Fi coverage improvements, equipment installation, and troubleshooting connection issues. For businesses, network planning can also help control access and keep important systems available.

Cybersecurity and Data Protection

Security is an essential part of any technology plan. Useful safeguards include strong, unique passwords, multifactor authentication, software updates, antivirus protection, and regular data backups. Businesses may also need access controls, security monitoring, and an incident response plan. No single tool can prevent every threat, so a layered approach is often the most practical.

Cloud Services and Data Backup

Cloud services can make files and applications available across multiple devices and locations. They can also support collaboration and flexible work arrangements. Before moving data to the cloud, it is important to consider privacy, access permissions, ongoing costs, and backup needs. Cloud storage and backup are not always the same, so organizations should confirm that critical data can be restored when needed.

Software and System Support

Software support helps keep applications compatible, updated, and configured for the work they need to do. This may include installing business software, resolving errors, managing licenses, and helping users learn new tools. Regular maintenance can reduce avoidable problems and help systems stay useful over time.

Choosing the Right Solution

Before investing in technology, identify the problem you want to solve. A useful assessment includes the devices and software already in use, the people who rely on them, any security or compliance requirements, and the budget available. It is also worth considering future needs so that a short-term fix does not create a larger challenge later.

For ongoing support, look for clear communication, transparent pricing, relevant experience, and a practical plan for maintaining and protecting your systems. Ask what is included, how urgent issues are handled, and how your data and account access will be managed.

Technology That Supports Your Goals

Computer tech solutions are most effective when they fit the people and processes using them. A well-maintained computer, secure network, reliable backup, or thoughtfully chosen cloud service can make daily work smoother and reduce unnecessary risk. With regular maintenance and informed planning, technology can remain a dependable tool for both personal and business needs.


9 Essential Computer Tech Tips for a Smooth and Secure Experience

  1. Restart the computer to clear temporary glitches.
  2. Install updates to fix bugs and security issues.
  3. Back up important files to cloud storage or an external drive.
  4. Use strong, unique passwords for every account.
  5. Run a trusted antivirus scan if the computer behaves strangely.
  6. Free up disk space by removing unused apps and files.
  7. Check cable connections when a device stops working.
  8. Use a password manager to store login details securely.
  9. Contact tech support if basic troubleshooting fails.

Restart the computer to clear temporary glitches.

Restarting your computer is a simple first step when you encounter a temporary glitch, such as a frozen app, sluggish performance, or a device that isn’t responding as expected. A restart closes active programs and refreshes the operating system, which can clear minor errors and restore normal operation. Save your work first, then restart and check whether the issue is resolved.

Install updates to fix bugs and security issues.

Install updates regularly to fix bugs, improve performance, and address security vulnerabilities. Operating system, software, and device updates often include important protections against new threats, so delaying them can leave your computer exposed. Turn on automatic updates when practical, and restart your device when prompted to complete the installation.

Back up important files to cloud storage or an external drive.

Protect important files by backing them up regularly to a trusted cloud storage service, an external drive, or both. Cloud backups make files accessible from different devices, while an external drive gives you a separate copy that can be stored safely offline. Set up automatic backups when possible, and occasionally check that your files can be restored—having a backup is only useful if it works when you need it.

Use strong, unique passwords for every account.

Use a strong, unique password for every account to reduce the risk of a security breach. If one password is stolen or exposed, unique passwords help prevent attackers from using it to access your other accounts. Consider using a reputable password manager to create and securely store long passwords, and turn on multifactor authentication whenever it’s available for an extra layer of protection.

Run a trusted antivirus scan if the computer behaves strangely.

If your computer starts behaving strangely—such as slowing down, showing unexpected pop-ups, or opening unfamiliar programs—run a scan with trusted, up-to-date antivirus software. Follow the program’s instructions to quarantine or remove any detected threats, then restart your computer if prompted. Avoid downloading unfamiliar “cleanup” tools, and keep your operating system and security software updated to help protect against future threats.

Free up disk space by removing unused apps and files.

Freeing up disk space can help your computer run more smoothly and leave room for important updates and new files. Start by uninstalling apps you no longer use, then review your Downloads, Documents, and desktop folders for duplicate or unnecessary files. Before deleting anything, make sure you have a backup of files you may want later, and empty the Recycle Bin or Trash when you’re ready.

Check cable connections when a device stops working.

When a device suddenly stops working, check its cable connections before trying more complicated fixes. Make sure each cable is firmly plugged into the device and the power outlet, and look for loose, damaged, or frayed cords. If possible, unplug and reconnect the cables, then test the device again. A simple connection issue is often easy to fix and can save time and unnecessary repair costs.

Use a password manager to store login details securely.

Use a password manager to store your login details securely and make it easier to use a unique, strong password for every account. Instead of remembering dozens of passwords or reusing the same one, you’ll only need to remember the manager’s main password. Choose a reputable password manager, protect it with multifactor authentication when available, and never share your master password.

Contact tech support if basic troubleshooting fails.

If basic troubleshooting doesn’t solve the problem, contact tech support for help. A support professional can identify issues that may not be obvious, guide you through safe next steps, and recommend repairs or solutions. Before reaching out, note any error messages, what you’ve already tried, and when the problem started—these details can help speed up diagnosis.

java course for beginners

Java Course for Beginners: Learn the Fundamentals and Build Your First Programs

Java Course for Beginners: A Practical Guide to Getting Started

Java is a popular programming language used to build everything from business applications and web services to Android apps and large-scale software systems. Its clear structure, broad ecosystem, and strong community make it a useful language for people learning to code. A well-designed Java course for beginners can help you move from basic concepts to building programs of your own.

Why Learn Java?

Java is designed to run on many types of computers. Java programs are typically compiled into bytecode, which runs on the Java Virtual Machine (JVM). This approach helps the same program work across different operating systems, provided a compatible JVM is available.

Java is also widely used in professional software development. Learning it can introduce you to essential programming ideas—including variables, loops, methods, and object-oriented programming—that apply to many other languages as well.

What a Beginner Java Course Should Cover

You do not need previous programming experience to begin. A good introductory course explains each idea step by step and gives you opportunities to practice it. Look for a course that includes these core topics:

  • Setting up your tools: Install a Java Development Kit (JDK) and choose a code editor or integrated development environment (IDE).
  • Your first program: Learn how to write, compile, and run a simple Java application.
  • Variables and data types: Store information using types such as int, double, boolean, and String.
  • Operators and expressions: Perform calculations and compare values.
  • Conditionals: Use if, else, and switch statements to make decisions.
  • Loops: Repeat tasks with for and while loops.
  • Methods: Organize code into reusable blocks.
  • Arrays and collections: Work with groups of values.
  • Object-oriented programming: Create classes and objects, and learn about fields, constructors, and methods.
  • Debugging and errors: Read compiler messages, find mistakes, and improve your code.

How to Choose the Right Course

Beginner courses come in many formats, including online lessons, classroom instruction, books, and self-paced tutorials. The best choice depends on how you like to learn and how much time you can set aside. Before enrolling, check that the course:

  • Clearly identifies itself as suitable for beginners.
  • Uses current Java tools and explains how to install them.
  • Includes coding exercises, not just videos or lectures.
  • Builds concepts gradually and explains unfamiliar terms.
  • Offers small projects that let you apply what you have learned.

A course does not have to teach every Java feature at once. A strong foundation in the basics is more valuable than rushing through advanced topics before you are ready.

Practice with Small Projects

Writing code regularly is one of the best ways to make progress. After learning the fundamentals, try projects that are simple enough to finish but flexible enough to expand. For example, you could create:

  • A temperature or unit converter
  • A basic calculator
  • A number-guessing game
  • A to-do list for the command line
  • A program that tracks books, movies, or personal expenses

Start with a basic version, then add features as your skills improve. A number-guessing game, for instance, can begin with a random number and a loop. Later, you can add input validation, a limited number of guesses, and a way to play again.

Tips for Learning Java Successfully

Set a manageable learning schedule. Short, frequent practice sessions often work better than trying to learn everything in one sitting. Type out examples yourself, change them, and observe what happens. When you encounter an error, read the message carefully and test one possible fix at a time.

It is also normal to revisit concepts. Object-oriented programming and other topics may take time to feel comfortable. Keep your early programs, review them later, and notice how your understanding has grown.

What Comes After the Basics?

Once you can write small programs and understand how classes and objects work, you can explore topics such as exception handling, file input and output, generics, testing, and common data structures. Your next steps can depend on your goals. For example, you might study web development, Android development, or backend application development.

Start Building with Java

A Java course for beginners can give you a clear path into programming, but progress comes from applying what you learn. Choose a course with hands-on exercises, practice consistently, and build small projects along the way. With patience and regular effort, you can develop the skills to create useful Java applications and continue learning more advanced programming concepts.


Top FAQs About Starting a Java Course for Beginners

  1. Which is the best Java course for beginners?
  2. How can I learn Java as a beginner?
  3. Is 1 month enough to learn Java?
  4. How do I start studying Java?

Which is the best Java course for beginners?

The best Java course for beginners is one that assumes no prior programming experience, teaches concepts step by step, and gives you plenty of hands-on practice. Look for lessons covering Java basics, problem-solving, and object-oriented programming, along with exercises and small projects that help you apply what you learn. The right choice also depends on your learning style, schedule, and budget, so preview a lesson or two before committing.

How can I learn Java as a beginner?

Beginners can learn Java by starting with the basics: installing the JDK and a code editor, then practicing variables, data types, conditionals, loops, methods, and classes. Follow a structured beginner course with hands-on exercises, and write code regularly rather than only watching lessons. Small projects—such as a calculator or number-guessing game—help reinforce new concepts. When errors come up, read the messages carefully and use them as clues; steady practice is more effective than trying to learn everything at once.

Is 1 month enough to learn Java?

One month is enough to learn Java’s fundamentals if you study consistently and practice regularly, but it’s usually not enough to master the language or become job-ready. In that time, you can learn basic syntax, variables, conditionals, loops, methods, and introductory object-oriented programming, then apply them in small projects. Your progress will depend on your prior experience and the time you can dedicate each day. Continue practicing after the first month to strengthen your skills and explore more advanced topics.

How do I start studying Java?

To start studying Java, install the latest Java Development Kit (JDK) and choose a beginner-friendly editor or IDE, such as IntelliJ IDEA or Visual Studio Code. Then follow a structured introductory course that covers basic syntax, variables, conditionals, loops, methods, and classes. Write and run small programs as you learn—such as a calculator or number-guessing game—and practice regularly. When you encounter errors, read the messages carefully and use them to understand how your code works.

www java com

www java com: A Guide to Java Downloads, Updates, and Support

What Is Java.com?

Java.com is the official website for Java software from Oracle. It provides information and resources for people who use Java on personal computers, including guidance on downloading, installing, and updating Java when it is needed to run certain applications.

What Is Java?

Java is a widely used programming language and software platform. Developers use it to build applications for many kinds of devices and systems. Some programs require Java components to be installed on a computer before they can run.

Java is distinct from JavaScript, despite the similar names. JavaScript is commonly used to add interactive features to websites, while Java is a separate programming language and platform.

What You Can Find on Java.com

Visitors can use Java.com to find Java-related downloads, installation instructions, troubleshooting help, and information about updates. The site is especially useful when a program specifically says that Java is required.

Not every computer needs Java installed. Many modern websites and applications work without it, so it is best to install Java only when a trusted application requires it. Before downloading software, check that you are visiting the official website and review the installation prompts carefully.

Keeping Java Up to Date

When Java is installed, keeping it updated can help address security issues and improve compatibility. Use the update tools included with the software or follow the instructions on Java.com. Avoid download links in unexpected pop-ups or messages, which may lead to unwanted or unsafe software.

Java for Developers

Java.com is aimed mainly at people who need Java for applications on their computers. Developers looking for programming tools, technical documentation, or enterprise products may need Oracle’s developer resources or other official Java project sites instead.

In Summary

Java.com is a starting point for learning about and obtaining Java software for compatible applications. If you need Java, use trusted sources, install only what is necessary, and keep the software updated.


Comprehensive Guide to Java: Download, Install, and Troubleshoot with Confidence

  1. Official source for Java downloads.
  2. Provides installation instructions.
  3. Offers update guidance.
  4. Includes troubleshooting resources.
  5. Explains Java’s purpose.
  6. Helps users check Java requirements.
  7. Supports safe, informed downloading.
  8. Easy starting point for Java users.


7 Drawbacks of Using www.java.com: Why It May Not Be Essential for Everyone

  1. Java is unnecessary for many users.
  2. Some Java apps require manual setup.
  3. Installation prompts may include extras.
  4. Java updates can interrupt workflows.
  5. Compatibility issues may affect older apps.
  6. The site focuses mainly on consumer Java downloads.
  7. Java is often confused with JavaScript.

Official source for Java downloads.

One key advantage of Java.com is that it provides an official source for Java downloads. Getting Java directly from the official website can help you avoid unofficial installers that may include unwanted software or outdated files. Before downloading, make sure Java is needed for the application you want to use, and follow the site’s installation and update instructions.

Provides installation instructions.

One useful feature of Java.com is its clear installation instructions. The site guides users through downloading and setting up Java, helping them follow the right steps for their computer and troubleshoot common issues along the way.

Offers update guidance.

Java.com offers clear guidance on checking for and installing Java updates. Keeping Java up to date can help improve compatibility and address security issues, while the site’s instructions make it easier to follow the recommended update process.

Includes troubleshooting resources.

One advantage of Java.com is that it includes troubleshooting resources to help users resolve common issues with downloading, installing, updating, or running Java. These guides can make it easier to find a solution and get back to using applications that rely on Java.

Explains Java’s purpose.

Java.com explains Java’s purpose in clear, accessible terms, helping visitors understand what the technology does and why certain applications may require it. This makes the site a useful starting point for people who want to learn the basics before deciding whether they need to download or use Java.

Helps users check Java requirements.

Java.com helps users check whether their computer meets the requirements for Java and whether Java is installed and working properly. This can make it easier to troubleshoot applications that depend on Java and determine whether an update or installation is needed.

Supports safe, informed downloading.

Java.com supports safe, informed downloading by providing official Java software alongside installation guidance and helpful information. Users can check what they’re downloading, follow clear setup instructions, and avoid relying on unfamiliar third-party download sites.

Easy starting point for Java users.

Java.com is an easy starting point for anyone who needs Java on a computer. The site brings together helpful information about downloading, installing, and updating Java, so users can quickly find the guidance they need without sorting through technical resources designed for developers.

Java is unnecessary for many users.

One drawback of Java.com is that many users may not need Java at all. Most modern websites and everyday applications run without it, so installing Java when no program requires it can add unnecessary software to a computer. Users should check whether a trusted application specifically needs Java before downloading or installing it.

Some Java apps require manual setup.

Some Java applications require manual setup before they work properly. You may need to adjust settings, install a specific version, or follow extra steps, which can be confusing if you’re not familiar with Java.

Installation prompts may include extras.

One potential drawback of www.java.com is that installation prompts may offer optional extras alongside Java. These offers can be easy to overlook, so review each screen carefully and decline anything you don’t want before continuing.

Java updates can interrupt workflows.

Java updates can interrupt workflows, especially when they appear during important tasks or require a browser or application restart. Downloads, installation steps, and compatibility checks may take time, while changes to Java settings can affect applications that depend on a particular version. Scheduling updates for a convenient time and checking that essential programs remain compatible can help reduce disruption.

Compatibility issues may affect older apps.

Compatibility issues may affect older apps that rely on specific Java versions or features. Updating Java can sometimes cause these applications to behave differently or stop working, so check the app’s requirements before installing a new version. Older software may also need updates or help from its developer to run properly.

The site focuses mainly on consumer Java downloads.

One drawback of Java.com is that it focuses mainly on Java downloads and support for everyday users, so developers may not find the technical documentation, development tools, or enterprise resources they need. They may have to look elsewhere on Oracle’s developer sites or other Java community resources.

Java is often confused with JavaScript.

A common drawback of Java.com is that Java is often confused with JavaScript because their names are so similar. Despite the resemblance, they are different technologies used for different purposes, and installing Java does not enable JavaScript in a web browser. This confusion can make it harder for users to find the right information or software for their needs.

simple java program

Simple Java Program: A Beginner’s Guide to Writing and Running Your First Code

How to Write a Simple Java Program

Java is a popular programming language used to build desktop, web, and mobile applications. A good way to get started is to write a small program that displays a message on the screen.

Your First Java Program

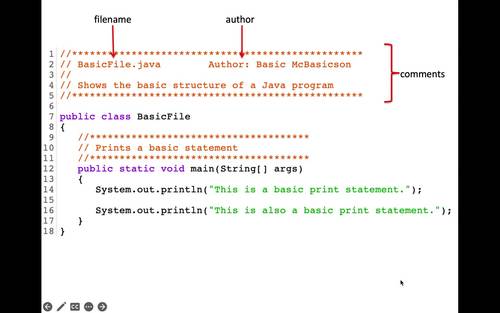
The program below prints “Hello, World!” in the console:

public class HelloWorld {

public static void main(String[] args) {

System.out.println("Hello, World!");

}

}

Understanding the Code

  • public class HelloWorld defines a class named HelloWorld. In Java, the class name should match the file name, so save the program as HelloWorld.java.
  • public static void main(String[] args) defines the main method. Java starts running the program from this method.
  • System.out.println() displays text in the console. The text to display goes inside the parentheses and quotation marks.
  • Braces, { }, mark the beginning and end of the class and method.
  • The semicolon at the end of the print statement tells Java that the instruction is complete.

Compile and Run the Program

Install a Java Development Kit (JDK), then open a terminal or command prompt in the folder containing HelloWorld.java. Compile the program with:

javac HelloWorld.java

If compilation succeeds, Java creates a file named HelloWorld.class. Run the program with:

java HelloWorld

The output will be:

Hello, World!

Try a Small Change

Replace the message inside System.out.println() with your own text. For example:

System.out.println("Java is fun to learn!");

Save the file, compile it again, and run it to see the new output. This simple example introduces the basic structure of a Java program and gives you a starting point for exploring variables, input, and other programming concepts.


7 Essential Tips for Writing Simple Java Programs

  1. Use `public static void main(String[] args)` as the program’s entry point.
  2. Save the file with the same name as its public class.
  3. Use `System.out.println()` to display text.
  4. End most statements with a semicolon.
  5. Match every opening brace with a closing brace.
  6. Compile with `javac` and run with `java`.
  7. Keep variable names clear and descriptive.

Use `public static void main(String[] args)` as the program’s entry point.

In a simple Java program, `public static void main(String[] args)` is the entry point—the method Java looks for to begin running your code. Place the statements you want the program to execute inside its braces. The method signature must be written with the correct spelling and capitalization, or Java won’t recognize it as the program’s starting point.

Save the file with the same name as its public class.

In Java, save your source file with the same name as its public class, including matching capitalization, and add the .java extension. For example, if your public class is HelloWorld, name the file HelloWorld.java. This naming rule helps the Java compiler locate and compile the class correctly.

Use `System.out.println()` to display text.

Use `System.out.println()` to display text in a Java program’s console. Place the text inside quotation marks within the parentheses, as in `System.out.println(“Hello, world!”);`. Java prints the message and then moves to a new line, making this method useful for showing greetings, results, and other output.

End most statements with a semicolon.

In Java, most statements end with a semicolon, which tells the compiler that an instruction is complete. For example, `System.out.println(“Hello, world!”);` needs a semicolon at the end. Forgetting one can cause a compile-time error, so check your statements when the compiler reports a problem. Some Java structures, such as class and method declarations, do not end with semicolons.

Match every opening brace with a closing brace.

In a simple Java program, every opening brace ({) must have a matching closing brace (}). Braces mark the beginning and end of code blocks, such as classes and methods, so a missing or misplaced brace can cause compilation errors or change how the program works. Indenting nested blocks consistently makes braces easier to match and your code easier to read.

Compile with `javac` and run with `java`.

To compile a simple Java program, open a terminal in the folder containing the `.java` file and run `javac FileName.java`, replacing `FileName` with the name of your file. After compilation succeeds, run the program with `java ClassName`—without the `.java` extension—to see its output.

Keep variable names clear and descriptive.

Use clear, descriptive variable names so your code is easier to read and understand. For example, studentAge is more informative than x, and totalPrice makes its purpose clearer than n. Meaningful names also make simple Java programs easier to update and help you spot mistakes as you learn.

java certification course

Java Certification Course: Build Your Skills and Prepare for the Exam

Java Certification Course: A Practical Guide to Getting Started

A Java certification course can help you build programming skills, prepare for a recognized credential, and demonstrate your knowledge to employers. Whether you’re new to software development or an experienced programmer looking to strengthen your résumé, the right course can provide a structured path to learning Java.

What Is a Java Certification Course?

A Java certification course teaches the concepts and skills covered by a particular Java certification exam or learning program. Courses may include video lessons, instructor-led classes, coding exercises, practice tests, and projects.

Course content varies, but commonly covers Java syntax, object-oriented programming, classes and interfaces, exception handling, collections, generics, and working with the Java development environment. More advanced courses may explore concurrency, database connectivity, APIs, and application development.

Who Should Consider Taking a Course?

Java certification courses may be useful for:

  • Beginners who want a guided introduction to programming
  • Students preparing for software development roles
  • Developers who use other languages and want to learn Java
  • Java programmers seeking to review core concepts
  • Professionals preparing for a specific certification exam

Before choosing a course, check its prerequisites. Some are designed for learners with no programming experience, while others expect familiarity with Java or general programming concepts.

Choosing the Right Java Course

Start by identifying your goal. If you want to learn programming, look for a beginner-friendly course with regular coding practice. If you’re preparing for an exam, confirm that the course aligns with the current exam objectives and Java version.

Consider these factors when comparing options:

  • Course level: Choose a course suited to your current experience.
  • Practice opportunities: Look for coding assignments, projects, and realistic questions.
  • Instructor support: Decide whether you prefer self-paced lessons or live instruction.
  • Current materials: Java and certification requirements can change, so check when the content was last updated.
  • Cost and schedule: Compare the total price, course length, and any additional exam fees.
  • Credential details: Verify who issues the certification and what completing the course actually provides.

Course Completion and Certification Are Not Always the Same

Completing a course may earn you a certificate of completion, but that is not necessarily the same as earning an industry certification. Some credentials require passing a separate exam. Review the certification provider’s official requirements, exam format, fees, and policies before enrolling in a preparation course.

Certification programs and exam details may change. Use the provider’s official website as the final source of information about available credentials and current requirements.

How to Prepare for a Java Certification Exam

A consistent study plan is usually more effective than cramming. Begin by reviewing the exam objectives and noting topics that are unfamiliar. Then combine instruction with hands-on practice: write small programs, test different inputs, and explain what the code does.

  1. Review the objectives. Use them to organize your study plan.
  2. Learn the fundamentals. Make sure you understand syntax, data types, control flow, and object-oriented principles.
  3. Code regularly. Practice in a development environment rather than relying only on videos or notes.
  4. Work through practice questions. Use them to find gaps in your understanding, not just to memorize answers.
  5. Build a small project. A practical project can help connect individual concepts.
  6. Review and adjust. Spend extra time on topics you find challenging.

Benefits of Learning Java

Java is used in a range of software applications, including business systems, web services, and Android development. Learning the language can help you understand programming fundamentals that transfer to other technologies. A certification may also give you a structured learning goal and a way to document your achievement.

However, a credential alone does not guarantee a job or prove practical ability. Employers may also look for problem-solving skills, project experience, communication, and familiarity with the tools used in their environment. Pairing coursework with hands-on projects can help you show what you can do.

Start with a Clear Goal

The best Java certification course is one that matches your experience, learning preferences, and career goals. Compare the course outline with the relevant exam objectives, confirm what credential—if any—you’ll earn, and make time for regular coding practice. With a realistic plan and steady effort, a course can be a useful step toward stronger Java skills.


9 Essential Tips for Mastering Your Java Certification Course

  1. Choose a course aligned with your Java certification exam.
  2. Check that the syllabus matches the latest exam objectives.
  3. Review Java fundamentals before starting advanced topics.
  4. Practice coding exercises regularly.
  5. Use mock exams to track your progress.
  6. Study core APIs and object-oriented programming.
  7. Ask instructors for help with difficult concepts.
  8. Set a consistent weekly study schedule.
  9. Review incorrect answers and learn from them.

Choose a course aligned with your Java certification exam.

Choose a course that aligns closely with the Java certification exam you plan to take. Exam objectives and Java versions can vary, so review the official exam outline and compare it with the course syllabus before enrolling. A well-matched course helps you focus your study time on relevant topics, practice the skills the exam measures, and avoid gaps in your preparation.

Check that the syllabus matches the latest exam objectives.

Before enrolling in a Java certification course, compare its syllabus with the certification provider’s latest exam objectives. Exam topics and requirements can change, so an outdated course may leave gaps in your preparation or spend time on material that’s no longer relevant. Check when the course was last updated and use the official exam page to confirm that the lessons cover the skills and topics you’ll be tested on.

Review Java fundamentals before starting advanced topics.

Before diving into advanced topics in a Java certification course, review the fundamentals, including data types, control flow, classes, objects, and methods. A strong grasp of these core concepts makes complex material easier to understand and helps you spot mistakes in your code. If anything feels rusty, spend time practicing with small programs before moving on.

Practice coding exercises regularly.

Practice coding exercises regularly to turn Java concepts into skills you can use confidently. Write programs from scratch, experiment with different solutions, and revisit topics such as loops, classes, collections, and exception handling. Consistent practice helps you spot gaps in your understanding, prepare for exam-style questions, and become more comfortable applying Java in real-world projects.

Use mock exams to track your progress.

Use mock exams to track your progress as you prepare for a Java certification. Taking practice tests under timed conditions can help you get comfortable with the exam format, identify topics that need more review, and see how your performance changes over time. After each test, review both incorrect answers and any questions you guessed on, then use those results to guide your next study sessions.

Study core APIs and object-oriented programming.

Focus on Java’s core APIs and object-oriented programming as you prepare for a certification course or exam. Practice using common classes and collections, and make sure you understand how classes, objects, inheritance, interfaces, and encapsulation work together. Writing small programs is a useful way to reinforce these concepts and recognize how they apply to real code.

Ask instructors for help with difficult concepts.

When a Java concept feels difficult, ask your instructor for help instead of letting confusion build. Describe what you’ve tried, share the code or error message you’re working with, and point out where you get stuck. An instructor can clarify the idea, suggest a different way to approach it, or recommend extra practice. Getting help early can make challenging topics easier to understand and keep you moving forward in your course.

Set a consistent weekly study schedule.

Set a consistent weekly study schedule to make steady progress in your Java certification course. Choose study times that fit your routine, then set aside regular blocks for lessons, coding practice, and reviewing challenging topics. Even a few focused sessions each week can help you retain concepts, build confidence, and avoid last-minute cramming.

Review incorrect answers and learn from them.

After each practice test, take time to review every incorrect answer and understand why your choice was wrong. Revisit the related Java concepts, check the official documentation or course materials, and try a few similar coding questions to reinforce what you’ve learned. This turns mistakes into useful feedback, helps reveal gaps in your understanding, and prepares you to handle unfamiliar questions on the certification exam.

cybersecurity as a service

Cybersecurity as a Service: A Practical Guide for Businesses

Cybersecurity as a Service: A Practical Guide for Businesses

Cybersecurity is no longer a one-time project. Threats change constantly, software needs regular updates, and even well-prepared organizations can face new risks. For many businesses, keeping up requires more time and specialized expertise than an in-house team can provide. Cybersecurity as a Service (CSaaS) offers another approach: access to ongoing security tools and expertise through an external provider.

What Is Cybersecurity as a Service?

Cybersecurity as a Service is a model in which an organization relies on a third-party provider for some or all of its security operations. Services are typically delivered on an ongoing basis and may be tailored to the organization’s size, systems, risk profile, and regulatory requirements.

Depending on the provider and service plan, CSaaS may include security monitoring, threat detection, vulnerability assessments, incident response support, employee training, and help with security policies. Some providers focus on a specific area, while others offer a broader managed security program.

Common Cybersecurity as a Service Offerings

  • Security monitoring: Reviewing activity across networks, devices, cloud environments, and applications to identify suspicious behavior.
  • Managed detection and response: Investigating potential threats and helping contain or remediate them. The exact level of response varies by provider and contract.
  • Vulnerability management: Identifying weaknesses in systems and helping prioritize fixes based on risk.
  • Endpoint protection: Managing security for computers, mobile devices, and servers.
  • Cloud security: Helping protect cloud accounts, workloads, data, and configurations.
  • Identity and access management: Supporting controls such as multifactor authentication, role-based access, and account reviews.
  • Security awareness training: Teaching employees how to recognize phishing, handle sensitive information, and report concerns.
  • Incident response planning: Preparing procedures and providing support when a security event occurs.

Why Businesses Choose CSaaS

Access to specialized expertise: Security providers may bring experience across different technologies and threat scenarios. This can be valuable for organizations that do not have a dedicated security team.

Ongoing coverage: Security risks do not follow business hours. Some services provide continuous monitoring or on-call support, depending on the agreement.

Predictable costs: A subscription or managed-services arrangement can make security spending easier to plan than building every capability internally. Costs and included services vary, so it is important to review the full scope.

Room to scale: Services can often be adjusted as an organization adds employees, locations, applications, or cloud systems.

More focus on core work: By delegating selected security tasks, internal staff may have more time for other business priorities. Outsourcing does not remove the organization’s responsibility for managing risk, however.

What CSaaS Does Not Do

Cybersecurity as a Service is not a guarantee that an organization will never experience a breach. No provider can eliminate every risk, and technology alone cannot prevent every incident. Effective security still depends on clear policies, reliable backups, timely software updates, appropriate access controls, and informed employees.

Responsibility is also shared. The provider may operate specific tools or monitor defined systems, while the customer remains responsible for decisions such as approving access, protecting business data, and following applicable legal or regulatory requirements. Those boundaries should be documented before service begins.

How to Choose a Provider

Start by identifying the problems the service needs to solve. A business seeking help with after-hours monitoring may need a different arrangement from one preparing for a compliance review or improving cloud security.

  • Define the scope: Confirm which systems, locations, users, and data are covered—and which are not.
  • Understand response procedures: Ask who investigates alerts, who can take action, how quickly the provider responds, and when the business will be contacted.
  • Review service levels: Look for clear commitments about availability, response times, reporting, and escalation. Check how those commitments are measured.
  • Ask about data handling: Understand what information the provider collects, where it is stored, who can access it, and how it is protected.
  • Check experience and references: Look for experience with organizations of a similar size, industry, and technology environment.
  • Clarify responsibilities: Establish who manages software updates, account permissions, investigations, backups, and incident communications.
  • Plan for continuity: Ask how service handoffs, data access, and security operations will work if the contract ends.

Making the Most of the Service

Before onboarding, create an accurate inventory of devices, applications, cloud services, and important data. Share existing policies and known risks with the provider, and identify internal contacts who can make decisions during an incident. Regularly review reports and hold meetings to discuss unresolved issues, changing business needs, and recommended improvements.

It is also important to test the relationship before an emergency. Tabletop exercises and incident-response drills can reveal unclear responsibilities and communication gaps while there is still time to address them.

Conclusion

Cybersecurity as a Service can help businesses access security expertise and ongoing support without building every capability in-house. The value depends on choosing services that match actual risks, defining responsibilities clearly, and staying actively involved. With a well-scoped agreement and sound internal practices, CSaaS can become a practical part of a broader cybersecurity program.


Top 5 Advantages of Cybersecurity as a Service for Your Business

  1. Access to specialized security expertise
  2. Continuous threat monitoring
  3. Predictable subscription costs
  4. Scales with business needs
  5. Frees staff to focus on core work


7 Potential Drawbacks of Cybersecurity as a Service: Costs, Control, and More

  1. Ongoing subscription costs can add up.
  2. Less direct control over security operations.
  3. Service quality varies between providers.
  4. Sensitive data may be shared with a vendor.
  5. Response times may depend on the service agreement.
  6. Integrating tools can be complex.
  7. Outsourcing does not eliminate business risk.

Access to specialized security expertise

Cybersecurity as a Service gives businesses access to specialized security expertise without requiring them to hire and maintain a large in-house team. Providers bring experience with evolving threats, security tools, and industry practices, helping organizations identify risks, strengthen defenses, and respond to potential incidents. This expertise can be especially valuable for small and midsize businesses that need knowledgeable support but may not have the resources to build a dedicated security department.

Continuous threat monitoring

Continuous threat monitoring helps organizations spot suspicious activity as it happens, rather than discovering it after significant damage has occurred. A cybersecurity provider can monitor networks, devices, and cloud systems around the clock, investigate alerts, and notify the right people when action is needed. This ongoing visibility can help businesses respond to emerging threats more quickly, even when their internal team is unavailable.

Predictable subscription costs

Cybersecurity as a Service can make security spending more predictable through a regular subscription fee. Instead of making large upfront investments in tools, hiring, and ongoing maintenance, businesses can budget for an agreed set of services each month or year. Costs depend on the provider and scope, so reviewing what’s included—and what may incur extra charges—helps avoid surprises.

Scales with business needs

Cybersecurity as a Service can scale as your business changes. You can adjust coverage as you add employees, open new locations, adopt cloud tools, or face new security requirements—without having to build an entirely new in-house security team. This flexibility helps keep protection aligned with your needs and budget as your organization grows.

Frees staff to focus on core work

Cybersecurity as a Service can free employees from time-consuming security tasks, such as monitoring alerts, managing tools, and tracking routine updates. With a specialized provider handling agreed-upon responsibilities, your team can spend more time on the work that directly supports your business goals. Outsourcing security does not eliminate the need for internal oversight, but it can help staff focus their attention where it matters most.

Ongoing subscription costs can add up.

Ongoing subscription costs for cybersecurity as a service can add up over time, especially as a business grows or adds more users, devices, and security features. What starts as a manageable monthly expense may become a significant part of the IT budget, so it’s important to review pricing, renewal terms, and potential add-on fees regularly. Compare the total long-term cost with the value and coverage provided to make sure the service continues to fit your needs.

Less direct control over security operations.

One potential drawback of cybersecurity as a service is having less direct control over day-to-day security operations. When an outside provider manages monitoring, tools, or incident response, your team may have limited visibility into how decisions are made or how quickly actions are taken. This can create challenges if the provider’s procedures do not align with your business priorities. To reduce the risk, define responsibilities, approval requirements, reporting expectations, and escalation procedures clearly in the service agreement.

Service quality varies between providers.

Service quality can vary significantly between cybersecurity providers, making it difficult to know what level of protection you’ll receive. Providers may differ in their expertise, monitoring capabilities, response times, communication, and the tools they use. A service that sounds comprehensive may also have important limits in its contract. Before choosing a provider, review exactly what’s included, ask how incidents are handled, and check references to ensure the service meets your organization’s needs.

Sensitive data may be shared with a vendor.

One potential drawback of cybersecurity as a service is that protecting your systems may require sharing sensitive data with an outside vendor. Depending on the service, the provider could access security logs, user information, system configurations, or other confidential details. This creates additional privacy and data-protection risks, especially if the vendor’s controls or practices are inadequate. Before signing an agreement, review what data will be collected, how it will be stored and protected, who can access it, and whether it will be shared with subcontractors.

Response times may depend on the service agreement.

Response times for cybersecurity as a service can depend on the terms of the service agreement. A provider may prioritize incidents according to severity, offer different response levels for different plans, or limit support to certain hours. If those details are unclear, a business could wait longer than expected for help during a security incident. Before signing, confirm response-time commitments, after-hours coverage, escalation procedures, and what actions the provider is authorized to take.

Integrating tools can be complex.

Integrating cybersecurity tools can be complex, especially when a provider’s platforms need to work with existing networks, cloud services, and business applications. Compatibility issues, duplicated alerts, or gaps in data sharing can make it harder to get a clear view of security risks. Setup may also require changes to workflows and access controls, so businesses should clarify integration requirements, responsibilities, and ongoing support before adopting a service.

Outsourcing does not eliminate business risk.

Outsourcing cybersecurity can add valuable expertise and support, but it does not eliminate a business’s responsibility for managing risk. The provider can only protect the systems, data, and processes covered by the agreement, and gaps in scope, communication, or internal practices may leave the organization exposed. Businesses still need to make informed security decisions, maintain sound policies, train employees, and understand who is responsible for each task—especially during an incident.

nydfs cybersecurity

Enhancing Financial Security: The Role of NYDFS in Cybersecurity

The Role of NYDFS in Cybersecurity

The Role of NYDFS in Cybersecurity

As cyber threats continue to evolve and become more sophisticated, the New York Department of Financial Services (NYDFS) plays a crucial role in ensuring the cybersecurity of financial institutions operating within the state.

The NYDFS has implemented stringent regulations and guidelines to safeguard sensitive financial data and protect consumers from cyber attacks. These regulations require financial institutions to establish robust cybersecurity programs, conduct regular risk assessments, and report any cybersecurity incidents promptly.

One of the key initiatives introduced by the NYDFS is the Cybersecurity Regulation (23 NYCRR 500), which sets forth minimum standards for cybersecurity practices that financial institutions must adhere to. This regulation includes requirements such as multi-factor authentication, encryption of sensitive data, and regular cybersecurity training for employees.

In addition to setting regulatory standards, the NYDFS actively monitors compliance with these regulations through examinations and assessments. Financial institutions are required to submit annual certifications of their compliance with the Cybersecurity Regulation, demonstrating their commitment to maintaining strong cybersecurity measures.

Furthermore, the NYDFS collaborates with other regulatory agencies and law enforcement authorities to share information on emerging cyber threats and coordinate responses to cyber incidents. By fostering a culture of information sharing and cooperation, the NYDFS aims to enhance the overall resilience of the financial sector against cyber threats.

In conclusion, the NYDFS plays a vital role in promoting cybersecurity within the financial industry and protecting both institutions and consumers from cyber risks. Through its proactive approach to regulation and oversight, the NYDFS helps ensure that New York remains at the forefront of cybersecurity best practices.


6 Essential Tips for Strengthening Cybersecurity Compliance with NYDFS Regulations

  1. Regularly update software and systems to protect against vulnerabilities.
  2. Implement strong password policies and multi-factor authentication.
  3. Train employees on cybersecurity best practices and how to identify phishing attempts.
  4. Encrypt sensitive data both in transit and at rest.
  5. Conduct regular security assessments and audits to identify weaknesses.
  6. Establish a an incident response plan to quickly respond to and mitigate cybersecurity incidents.

Regularly update software and systems to protect against vulnerabilities.

Regularly updating software and systems is a critical tip in NYDFS cybersecurity practices to safeguard against vulnerabilities. By staying current with software patches and system updates, financial institutions can address known security weaknesses and reduce the risk of exploitation by cyber attackers. This proactive approach helps ensure that systems remain resilient to emerging threats and maintain the integrity of sensitive financial data. Compliance with this best practice not only enhances cybersecurity posture but also demonstrates a commitment to maintaining a secure environment for both the institution and its customers as mandated by NYDFS regulations.

Implement strong password policies and multi-factor authentication.

To enhance cybersecurity measures in compliance with NYDFS regulations, it is crucial for financial institutions to implement strong password policies and multi-factor authentication. By enforcing complex password requirements and requiring an additional layer of verification through multi-factor authentication, institutions can significantly reduce the risk of unauthorized access to sensitive data. These practices not only bolster security but also demonstrate a commitment to safeguarding confidential information and meeting the stringent cybersecurity standards set forth by the NYDFS.

Train employees on cybersecurity best practices and how to identify phishing attempts.

Training employees on cybersecurity best practices is essential in strengthening an organization’s defense against cyber threats. By educating staff members on how to identify phishing attempts, such as suspicious emails or messages, companies can empower their workforce to act as the first line of defense against potential security breaches. Equipping employees with the knowledge and skills to recognize and report phishing attempts not only helps protect sensitive data but also contributes to creating a culture of cybersecurity awareness within the organization.

Encrypt sensitive data both in transit and at rest.

It is crucial for financial institutions under NYDFS regulation to encrypt sensitive data both in transit and at rest. Encrypting data in transit ensures that information remains secure while being transferred between systems or devices, protecting it from interception by malicious actors. Similarly, encrypting data at rest safeguards stored information from unauthorized access, adding an extra layer of security to prevent data breaches. By implementing robust encryption practices, financial institutions can enhance the protection of sensitive data and comply with NYDFS cybersecurity requirements effectively.

Conduct regular security assessments and audits to identify weaknesses.

Regular security assessments and audits are essential components of a comprehensive cybersecurity strategy recommended by the NYDFS. By conducting these assessments on a regular basis, financial institutions can proactively identify vulnerabilities and weaknesses in their systems and processes. This proactive approach allows organizations to address potential security gaps before they are exploited by cyber attackers, helping to strengthen overall cybersecurity defenses and protect sensitive data from unauthorized access or breaches.

Establish a an incident response plan to quickly respond to and mitigate cybersecurity incidents.

Establishing an incident response plan is a critical component of NYDFS cybersecurity guidelines. By having a well-defined plan in place, financial institutions can swiftly respond to and mitigate cybersecurity incidents, minimizing potential damages and disruptions. This proactive approach not only helps in containing the impact of security breaches but also demonstrates a commitment to effective risk management and compliance with regulatory requirements. Having an incident response plan ensures that organizations are prepared to handle cyber threats promptly and efficiently, safeguarding both their own operations and the sensitive data of their customers.

green tech solutions

Green Tech Solutions: Innovations for a Cleaner, More Sustainable Future

Green Tech Solutions: Building a More Sustainable Future

Green technology, often called green tech, uses innovation to reduce environmental impact and support more sustainable ways of living and working. From renewable energy systems to energy-efficient buildings, these solutions can help conserve resources, cut pollution, and address climate change.

What Are Green Tech Solutions?

Green tech includes products, services, and processes designed to use resources more efficiently or reduce harm to the environment. Some solutions replace high-emission technologies, while others help people and organizations track and lower their energy use, waste, and emissions.

Key Types of Green Technology

Renewable Energy

Solar, wind, geothermal, and hydropower systems generate electricity from renewable sources. Homeowners and businesses can install solar panels, while utilities can add large-scale renewable projects to the power grid. Battery storage can help make renewable electricity available when the sun is not shining or the wind is not blowing.

Energy-Efficient Buildings

Buildings can use less energy through better insulation, efficient windows, LED lighting, and high-efficiency heating and cooling systems. Smart thermostats and building-management systems can adjust energy use based on occupancy and weather conditions. These upgrades may also improve comfort and reduce utility costs.

Electric Transportation

Electric vehicles produce no tailpipe emissions and can reduce transportation-related pollution, particularly when charged with cleaner electricity. Public transit, electric buses, bike-sharing programs, and walking-friendly neighborhoods can further reduce reliance on single-occupancy vehicles. Charging access and responsible battery production remain important considerations as adoption grows.

Water Conservation

Green water technologies include leak detection, efficient irrigation, rainwater collection, and systems that reuse treated wastewater. These tools can help communities, farms, and businesses conserve water, especially in areas facing drought or pressure on local supplies.

Waste Reduction and the Circular Economy

Recycling is only one part of sustainable waste management. Green solutions also include designing products to last longer, repairing and reusing materials, composting organic waste, and recovering valuable resources. A circular approach aims to keep materials in use instead of sending them to landfills after a single use.

Benefits for Communities and Businesses

Green technology can deliver environmental, economic, and social benefits. Energy efficiency can lower operating costs, while renewable energy can diversify power sources. Cleaner transportation can improve local air quality, and water-saving measures can strengthen resilience during dry periods. Green industries can also create jobs in areas such as construction, engineering, manufacturing, and maintenance.

The benefits depend on how solutions are designed and implemented. For example, the full environmental impact of a product includes the materials used to make it, the energy required to operate it, and how it is handled at the end of its useful life.

Challenges to Consider

Upfront costs can make some green technologies difficult to adopt, even when they may provide savings over time. Other challenges include limited infrastructure, supply-chain impacts, access to skilled workers, and differences in local conditions. A solution that works well in one region may not be suitable for another.

Planning matters. Organizations and communities can compare options, assess long-term costs, consult qualified professionals, and consider the needs of the people who will use the technology. Government incentives and financing programs may also help make projects more accessible.

How to Get Started

  • Review energy, water, and waste use to identify the biggest opportunities for improvement.
  • Start with practical efficiency measures, such as sealing drafts, switching to LED lighting, or fixing leaks.
  • Explore renewable energy options that fit the local climate, property, and utility rules.
  • Choose durable products and look for repair, reuse, and recycling options.
  • Track results so improvements can be measured and adjusted over time.

Looking Ahead

Green tech solutions are most effective when they are part of a broader commitment to using resources wisely. Innovation can provide powerful tools, but thoughtful planning, responsible production, and everyday choices are also essential. By adopting solutions suited to local needs, households, businesses, and communities can help build a cleaner and more resilient future.


Understanding Green Tech Solutions: Common Questions and Answers

  1. What are green tech solutions?
  2. What are some examples of green technology?
  3. How can green tech solutions help reduce energy costs?
  4. Are green tech solutions affordable for homeowners and small businesses?
  5. How can I choose the right green tech solutions for my home or business?
  6. What are the environmental benefits and challenges of green technology?

What are green tech solutions?

Green tech solutions are products, services, and practices designed to reduce environmental impact and use resources more efficiently. They include renewable energy such as solar and wind power, energy-efficient appliances and buildings, electric transportation, water-saving systems, and ways to reduce waste through reuse and recycling. By lowering emissions and conserving resources, green tech can help households, businesses, and communities move toward a more sustainable future.

What are some examples of green technology?

Examples of green technology include solar panels and wind turbines that generate renewable electricity, energy-efficient appliances and LED lighting that reduce power use, and electric vehicles that can lower tailpipe emissions. Other examples include smart thermostats, battery storage, water-saving irrigation systems, rainwater collection, recycling and composting programs, and building materials designed to improve insulation or reduce waste.

How can green tech solutions help reduce energy costs?

Green tech solutions can help reduce energy costs by using less power and generating electricity from renewable sources. Energy-efficient lighting, appliances, insulation, and smart thermostats can lower consumption, while solar panels or other renewable systems can reduce reliance on utility electricity. Although some upgrades require an upfront investment, lower monthly bills and available incentives may help offset the cost over time.

Are green tech solutions affordable for homeowners and small businesses?

Green tech solutions can be affordable for homeowners and small businesses, especially when you start with lower-cost upgrades such as LED lighting, smart thermostats, improved insulation, or water-saving fixtures. Larger investments, such as solar panels, battery storage, and electric vehicle chargers, may have higher upfront costs but can reduce utility bills over time. The total cost depends on your location, energy use, and available incentives, rebates, or financing options. Comparing the expected long-term savings with installation and maintenance costs can help you choose a solution that fits your budget.

How can I choose the right green tech solutions for my home or business?

To choose the right green tech solutions for your home or business, start by reviewing your energy, water, and waste use to identify the biggest opportunities for improvement. Consider your goals, budget, building conditions, local climate, and available incentives, then compare options based on upfront and long-term costs, expected savings, environmental impact, and maintenance needs. A qualified energy auditor or sustainability professional can help assess your property and recommend solutions that fit your needs. Begin with practical upgrades, track the results, and expand your efforts over time.

What are the environmental benefits and challenges of green technology?

Green technology can reduce greenhouse gas emissions, air and water pollution, energy use, and waste while helping conserve natural resources. Renewable energy, efficient buildings, electric transportation, and water-saving systems can also support healthier communities and a more resilient climate. However, green technology has challenges: manufacturing solar panels, batteries, and electric vehicles requires energy and raw materials, and mining or disposal can harm ecosystems if not managed responsibly. High upfront costs, limited recycling options, and uneven access can also slow adoption. Considering a technology’s full life cycle helps maximize its benefits and reduce its drawbacks.