cfchris.com

Loading

microsoft cloud security

Microsoft Cloud Security: Essential Strategies for Protecting Your Data and Workloads

Microsoft Cloud Security: A Practical Guide

Microsoft cloud services—including Azure, Microsoft 365, and services built on the Microsoft cloud—offer organizations flexible ways to run applications, collaborate, and manage data. Protecting those environments takes more than turning on a security feature. It requires clear ownership, strong identity controls, thoughtful configuration, and ongoing monitoring.

Understand the Shared Responsibility Model

Cloud security is a shared responsibility between Microsoft and its customers. Microsoft secures the underlying cloud infrastructure, while customers remain responsible for areas such as user accounts, access permissions, data, and many service configurations. The exact division of responsibility depends on the service being used. For example, a managed software service generally requires less infrastructure management by the customer than a virtual machine running in Azure.

Before deploying a workload, identify what Microsoft manages and what your organization must secure. This helps prevent gaps in areas such as patching, backups, access control, and data protection.

Make Identity Your First Line of Defense

Compromised accounts are a common path into cloud environments, so identity protection should be a priority. Microsoft Entra ID provides identity and access management capabilities for Microsoft cloud services and other applications.

  • Require multifactor authentication, especially for administrators and remote access.
  • Use conditional access policies to evaluate factors such as user, device, location, and risk.
  • Apply least privilege: give users and applications only the access they need.
  • Use privileged identity management practices to limit standing administrator access.
  • Review inactive accounts, service principals, and access permissions regularly.

Strong identity controls can reduce the impact of stolen passwords and help limit an attacker’s ability to move through an environment.

Protect Azure Workloads and Configurations

Misconfigured cloud resources can expose systems or data even when the underlying platform is secure. In Azure, organizations should establish secure configuration standards for subscriptions, networks, storage, virtual machines, and databases. Azure Policy can help enforce organizational requirements, while Microsoft Defender for Cloud can provide security recommendations and threat protection capabilities for supported resources.

Important practices include restricting public access where it is not required, using network segmentation, securing administrative connections, encrypting sensitive data, and keeping workloads patched. Backups should be protected from accidental deletion and ransomware, and recovery plans should be tested rather than assumed to work.

Secure Microsoft 365 and Collaboration

Microsoft 365 brings together email, file storage, meetings, and collaboration tools. Security settings should reflect how people actually work while limiting unnecessary exposure. Review sharing defaults in services such as SharePoint and OneDrive, manage external collaboration, and establish retention and access policies appropriate to the organization.

Microsoft Defender for Office 365 can help protect against threats such as phishing and malicious attachments, depending on the plan and configuration. Security awareness training and clear procedures for reporting suspicious messages remain important because technical controls cannot prevent every social-engineering attempt.

Protect and Govern Data

Cloud security also depends on knowing what data an organization stores and who can access it. Microsoft Purview includes data governance, information protection, and compliance capabilities, with features varying by product and license. Organizations can use classification and sensitivity labels to help identify and protect important information, and apply data loss prevention policies to reduce inappropriate sharing.

Start by identifying sensitive data, defining who should be able to access it, and deciding how long it should be retained. Policies should be tested with users and business teams to avoid disrupting legitimate work.

Monitor, Detect, and Respond

Security controls are most effective when organizations can detect suspicious activity and respond quickly. Microsoft Defender products provide security capabilities across various environments, while Microsoft Sentinel is a cloud-based security information and event management (SIEM) and security orchestration, automation, and response (SOAR) platform. The tools an organization needs depend on its environment, risk profile, and licensing.

Establish a process for reviewing alerts, investigating incidents, and escalating serious findings. Keep audit logging enabled where appropriate, define incident-response roles, and practice response scenarios such as account compromise, data exposure, and ransomware. Monitoring without a clear response process can leave important alerts unattended.

Build a Sustainable Security Program

Microsoft cloud security is not a one-time setup. Services change, employees join and leave, and business requirements evolve. A sustainable program includes regular access reviews, configuration assessments, vulnerability management, backup testing, and updates to policies and incident-response plans.

Begin with the basics: secure administrator accounts, enable strong authentication, reduce excessive permissions, protect sensitive data, and establish reliable monitoring. Then use Microsoft’s security guidance and the controls available in your specific services to improve protection over time. Because features and licensing can change, verify current capabilities and requirements in Microsoft’s official documentation before designing or purchasing a solution.


Top 9 Benefits of Microsoft Cloud Security for Your Business

  1. Scales with your business needs
  2. Offers strong identity controls
  3. Supports multifactor authentication
  4. Helps protect data with encryption
  5. Provides built-in threat detection
  6. Integrates with Microsoft 365
  7. Enables centralized security management
  8. Supports compliance and governance
  9. Offers tools for monitoring and response


5 Challenges of Microsoft Cloud Security: Complexity, Costs, and Dependence

  1. Can be complex to configure and manage.
  2. Advanced security features may require costly licenses.
  3. Misconfigurations can expose data and services.
  4. Dependence on Microsoft can limit flexibility.
  5. Requires ongoing expertise and monitoring.

Scales with your business needs

Microsoft cloud security can scale alongside your business, helping you adjust protection as your team, data, and workloads grow or change. You can add security capabilities, expand coverage across cloud services, and adapt access controls and policies as new needs arise—without having to build and maintain all the supporting infrastructure yourself. This flexibility can help keep security aligned with your business while making it easier to manage changing requirements.

Offers strong identity controls

Microsoft cloud security offers strong identity controls that help organizations protect accounts, apps, and data. With tools such as Microsoft Entra ID, teams can require multifactor authentication, apply access policies based on user and device risk, and limit permissions to only what each person needs. These safeguards make it harder for unauthorized users to gain access and help reduce the impact of compromised credentials.

Supports multifactor authentication

Microsoft cloud security supports multifactor authentication (MFA), adding an extra layer of protection beyond a password. Users may be asked to confirm their identity with an authenticator app, a security key, or another approved method. This makes it harder for someone to access an account with a stolen or guessed password and helps organizations better protect email, files, and cloud resources.

Helps protect data with encryption

Microsoft cloud security helps protect data with encryption, making information harder to read if it is accessed without authorization. Encryption can safeguard data while it is stored and while it moves between services or devices. With appropriate configuration and key-management practices, organizations can add an important layer of protection for sensitive information across their cloud environments.

Provides built-in threat detection

Microsoft cloud security includes built-in threat detection capabilities that help identify suspicious activity across supported services, users, devices, and workloads. These tools can analyze signals and surface alerts about potential risks—such as unusual sign-ins or malicious behavior—so security teams can investigate and respond more quickly. When configured to fit an organization’s environment, built-in detection can strengthen visibility without requiring every monitoring capability to be assembled from scratch.

Integrates with Microsoft 365

Microsoft cloud security integrates seamlessly with Microsoft 365, helping organizations protect email, files, meetings, and user accounts within the tools employees already use. This integration can bring security policies, identity controls, and threat protection together across services such as Outlook, Teams, SharePoint, and OneDrive. As a result, administrators can manage access more consistently, respond to potential threats with greater visibility, and help safeguard sensitive information without disrupting everyday collaboration.

Enables centralized security management

Microsoft cloud security enables centralized security management by bringing key security settings, policies, alerts, and monitoring tools together across cloud services. This gives IT and security teams a clearer view of their environment and helps them apply consistent protections, manage access, and respond to potential threats more efficiently. Centralized oversight can also make it easier to identify gaps and coordinate security practices across users, devices, and workloads.

Supports compliance and governance

Microsoft cloud security supports compliance and governance by providing tools to help organizations protect sensitive information, manage access, apply data-retention policies, and monitor activity. Services such as Microsoft Purview can help classify and govern data, while built-in security and compliance features can support an organization’s efforts to meet applicable regulatory and internal requirements. The right controls depend on the Microsoft services in use, the organization’s configuration, and its specific compliance obligations.

Offers tools for monitoring and response

Microsoft cloud security offers tools that help organizations monitor activity, detect potential threats, and respond to incidents. Services such as Microsoft Defender and Microsoft Sentinel can bring security signals together, surface suspicious behavior, and support investigation and response workflows. With appropriate configuration and ongoing oversight, these tools can help teams identify problems sooner and coordinate a more effective response.

Can be complex to configure and manage.

One drawback of Microsoft cloud security is that it can be complex to configure and manage. Services such as Azure, Microsoft 365, and Microsoft Entra ID offer many security settings, policies, and tools, and the right setup depends on an organization’s needs and licensing. Misconfigured controls or unclear responsibilities can leave gaps in protection, so teams may need specialized expertise, ongoing training, and regular reviews to manage the environment effectively.

Advanced security features may require costly licenses.

Advanced security features in Microsoft cloud services can come at a significant additional cost. Capabilities such as enhanced threat detection, identity protection, compliance tools, and advanced data protection may require higher-tier subscriptions or separate licenses. For organizations with tight budgets, these costs can make it difficult to deploy the full set of recommended safeguards, so it’s important to compare licensing options and prioritize features based on risk and business needs.

Misconfigurations can expose data and services.

One potential drawback of Microsoft cloud security is that misconfigurations can expose sensitive data and services to unauthorized access. A storage account with overly permissive access, an exposed network endpoint, or an incorrectly assigned user role can create security gaps—even when the underlying Microsoft platform is operating securely. Preventing these issues requires careful setup, regular configuration reviews, and ongoing monitoring.

Dependence on Microsoft can limit flexibility.

Relying heavily on Microsoft’s cloud security tools can limit an organization’s flexibility. Teams may find it difficult or costly to switch providers, integrate competing products, or adapt workflows built around Microsoft-specific services. This dependence can also make it harder to respond to changing business needs or negotiate terms, so organizations should consider portability and interoperability when designing their cloud security strategy.

Requires ongoing expertise and monitoring.

Microsoft cloud security requires ongoing expertise and monitoring to remain effective. Services, threats, and security settings change over time, so organizations need knowledgeable staff to review configurations, manage access, investigate alerts, and respond to incidents. Without consistent oversight, misconfigurations or suspicious activity may go unnoticed, leaving sensitive data and systems at risk.
cyber security managed services

Cyber Security Managed Services: A Practical Guide for Businesses

Cybersecurity Managed Services: A Practical Guide for Businesses

Cybersecurity threats can affect organizations of every size. Phishing, ransomware, stolen credentials, and software vulnerabilities can disrupt operations, expose sensitive information, and damage customer trust. Keeping up with these risks takes time and specialized expertise—resources that many businesses do not have in-house. Cybersecurity managed services can help fill that gap.

What Are Cybersecurity Managed Services?

Cybersecurity managed services are ongoing security services provided by an external team. Depending on the provider and the organization’s needs, these services may include monitoring systems, identifying vulnerabilities, responding to incidents, managing security tools, and helping meet regulatory requirements.

Some providers offer a broad security program, while others focus on specific areas such as endpoint protection or cloud security. The goal is to strengthen an organization’s defenses and provide access to security expertise without requiring every capability to be built internally.

Common Services

A managed cybersecurity program may include a combination of the following:

  • 24/7 security monitoring: Reviewing alerts and system activity to help identify suspicious behavior.
  • Threat detection and response: Investigating potential incidents and coordinating actions to contain them.
  • Endpoint security: Protecting computers, servers, and mobile devices from malware and unauthorized access.
  • Vulnerability management: Finding and prioritizing weaknesses in software, systems, and configurations.
  • Security assessments: Evaluating existing controls, processes, and exposure to risk.
  • Identity and access management: Helping ensure users have appropriate access and that authentication controls are in place.
  • Cloud security: Reviewing cloud environments, permissions, and configurations for common security issues.
  • Security awareness training: Helping employees recognize phishing attempts and follow safer practices.
  • Incident response planning: Establishing roles, procedures, and communication plans before an incident occurs.

How Managed Services Can Help

Access to specialized expertise: Security providers can bring experience with current threats, technologies, and response practices. This can be valuable for organizations that do not have a large internal security team.

Consistent monitoring: Threats do not follow business hours. Depending on the service agreement, a provider may monitor systems around the clock and escalate significant alerts when they occur.

More predictable costs: Managed services often use recurring fees, which can make security spending easier to plan than building every capability from scratch. Costs and included services vary, so the contract should be reviewed carefully.

Support for internal teams: A provider can handle routine monitoring or specialized tasks, allowing in-house staff to focus on business priorities. Managed services work best when responsibilities are clearly divided rather than assumed.

Improved readiness: Regular assessments, documented procedures, and testing can help an organization prepare for security incidents and reduce confusion during a response.

Choosing a Managed Security Provider

Not every provider offers the same capabilities. Before selecting one, consider your organization’s systems, risk tolerance, compliance obligations, and internal expertise. Ask prospective providers questions such as:

  • Which services are included, and which cost extra?
  • Who monitors alerts, and what are the response hours?
  • How quickly will critical incidents be escalated?
  • What actions can the provider take without approval?
  • How will the provider protect access to your systems and data?
  • What reports, reviews, and service-level commitments are provided?
  • How does the provider support incident response and recovery?
  • Can the services scale as your organization changes?

Request clear documentation of responsibilities, escalation paths, data handling practices, and service levels. It is also useful to understand how the provider will work with your IT team, leadership, legal counsel, and other vendors during an incident.

Managed Services Do Not Transfer All Responsibility

Hiring a cybersecurity provider does not make an organization automatically secure or remove its responsibility for protecting information. Business leaders still need to set priorities, approve policies, manage user access, maintain backups, and ensure employees understand their role in security. The provider can supply tools and expertise, but effective security requires cooperation between the provider and the organization.

Organizations should also review the provider’s own security practices. A managed security provider may need access to sensitive systems, so its access controls, incident procedures, confidentiality commitments, and handling of customer data matter.

Making the Most of a Managed Security Partnership

Start by identifying critical systems and information, then define the outcomes the service should support. Set measurable expectations, such as reporting frequency, alert escalation procedures, and vulnerability remediation timelines. Review results regularly and update the scope when your technology, risks, or business needs change.

Cybersecurity managed services can help businesses strengthen monitoring, improve incident readiness, and access expertise that may be difficult to maintain internally. With a carefully selected provider, clear responsibilities, and active oversight, they can become a useful part of a broader security program—not a substitute for one.


5 Essential Tips for Choosing and Managing Cybersecurity Services

  1. Define clear security goals and service-level expectations.
  2. Verify the provider’s certifications and incident response plan.
  3. Require regular vulnerability scans and patch management.
  4. Keep access limited with multifactor authentication.
  5. Review reports and test recovery plans regularly.

Define clear security goals and service-level expectations.

Define clear security goals and service-level expectations before choosing a cybersecurity managed services provider. Identify the outcomes that matter most—such as 24/7 monitoring, faster incident response, vulnerability remediation, or compliance support—and agree on measurable targets, reporting schedules, and escalation procedures. Clear expectations help your provider prioritize the right risks, coordinate effectively with your team, and demonstrate whether the service is meeting your needs.

Verify the provider’s certifications and incident response plan.

Before choosing a cybersecurity managed services provider, verify that its certifications are current, relevant to your needs, and held by the people who will work on your account. Ask for details about its incident response plan, including how it detects and escalates threats, who will contact your team, what actions it can take, and how quickly it will respond. A clear, tested plan and qualified staff can help ensure the provider is prepared to support your organization when a security incident occurs.

Require regular vulnerability scans and patch management.

Require your cybersecurity managed services provider to run vulnerability scans on a regular schedule and promptly share findings, priorities, and remediation plans. Scans can uncover outdated software, misconfigurations, and other weaknesses before attackers exploit them. Pair scanning with a clear patch management process that prioritizes critical updates, tests patches when appropriate, and tracks completion across your systems. Regular reporting helps confirm that issues are being addressed and that your security posture keeps pace with emerging risks.

Keep access limited with multifactor authentication.

Limit access to sensitive systems and data by giving each user only the permissions needed for their role, and require multifactor authentication (MFA) wherever possible. MFA adds a verification step—such as an authenticator app prompt or security key—so a stolen password alone is less likely to grant access. A managed security provider can help configure MFA, review access regularly, and remove accounts or permissions that are no longer needed.

Review reports and test recovery plans regularly.

Review cybersecurity reports regularly to understand emerging threats, unresolved vulnerabilities, and whether your managed services are meeting agreed-upon goals. Reports are most useful when they lead to clear actions, owners, and deadlines. Also test recovery plans on a recurring basis—not just on paper—to confirm that backups can be restored, critical systems can be brought back online, and everyone knows their role during an incident. Regular reviews and realistic exercises can reveal gaps early and help your business recover more confidently when disruption occurs.

cyber security management services

Cyber Security Management Services: Protecting Your Business from Digital Threats

Cybersecurity Management Services: Protecting Your Business in a Changing Threat Landscape

Cybersecurity is an ongoing business responsibility, not a one-time technology project. New threats, changing systems, and evolving work practices can create risks for organizations of every size. Cybersecurity management services help businesses assess those risks, strengthen their defenses, and respond effectively when security issues arise.

What Are Cybersecurity Management Services?

Cybersecurity management services provide ongoing support for the people, processes, and technologies used to protect an organization’s systems and information. Depending on a business’s needs, services may include security assessments, monitoring, policy development, employee training, incident response planning, and help with regulatory requirements.

Some organizations manage cybersecurity internally, while others work with an outside provider for specialized expertise or day-to-day support. A provider may work alongside an internal IT team or take responsibility for selected security functions.

Common Cybersecurity Management Services

Security Risk Assessments

A risk assessment identifies potential weaknesses in systems, accounts, applications, and business processes. It can help an organization understand which risks are most important and decide where to focus its security investments.

Security Monitoring and Threat Detection

Monitoring tools can help identify unusual activity, suspicious logins, malware, and other potential threats. When alerts are reviewed and handled promptly, businesses may be better positioned to investigate problems before they cause wider disruption.

Vulnerability and Patch Management

Software vulnerabilities can leave systems exposed if they are not addressed. Vulnerability management involves identifying known weaknesses, prioritizing them by risk, and coordinating updates or other safeguards.

Identity and Access Management

Managing who can access business systems is a core part of cybersecurity. Services may include multifactor authentication, access reviews, stronger account controls, and processes for promptly changing or removing access when someone changes roles or leaves the organization.

Employee Security Awareness

Employees can help protect an organization when they know how to recognize phishing attempts, handle sensitive information, and report suspicious activity. Training can reinforce practical security habits and make reporting concerns easier.

Incident Response Planning

Even well-prepared organizations can experience security incidents. An incident response plan outlines who should take action, how systems and information will be protected, and how the organization will communicate and recover. Planning ahead can reduce confusion during a high-pressure situation.

Backup and Recovery Planning

Reliable backups can help a business restore important data after an outage, accidental deletion, hardware failure, or ransomware incident. A recovery plan should identify what needs to be restored first and include regular tests to check that backups can be used.

Why Ongoing Cybersecurity Management Matters

Security needs change as organizations adopt new applications, hire employees, work with vendors, or move data to cloud services. Ongoing management can help businesses keep track of these changes and maintain appropriate protections over time.

  • Reduce avoidable risk: Regular reviews can reveal weaknesses before they become larger problems.
  • Improve response readiness: Clear plans and responsibilities help teams act more effectively during an incident.
  • Support business continuity: Security and recovery planning can help limit interruptions to essential operations.
  • Make security more consistent: Documented procedures help employees and teams follow the same expectations.
  • Use expertise effectively: Outside specialists can provide skills or coverage that may be difficult to maintain in-house.

Choosing a Cybersecurity Management Provider

Cybersecurity services should fit an organization’s systems, operations, and risk profile. Before selecting a provider, consider the following:

  • Which services are included, and which require additional fees?
  • How are alerts reviewed, prioritized, and escalated?
  • Who will be responsible for responding to an incident?
  • How will the provider coordinate with internal IT staff and leadership?
  • How are access to business systems and sensitive information controlled?
  • What reports, recommendations, or service reviews will be provided?
  • Can the provider support the organization’s legal, contractual, and regulatory obligations?

It is also helpful to ask how a provider will learn about the business, document its environment, and measure progress. A useful relationship should include clear communication and practical recommendations—not just software or alerts.

Build a Security Program That Can Adapt

Effective cybersecurity management is a continuing process. It starts with understanding the organization’s most important systems and risks, then combines suitable safeguards with monitoring, training, and response planning. Regular reviews help ensure those measures remain relevant as the business changes.

Cybersecurity management services can give organizations the structure and support to take a more proactive approach. With clear priorities and consistent oversight, businesses can better protect their information, support daily operations, and prepare for security challenges.


Top FAQs About Cybersecurity Management Services: Costs, Careers, and Key Players

  1. What are the top 3 cybersecurity companies?
  2. What is the average cost of cyber security services?
  3. Can I make $200,000 a year in cyber security?
  4. What are cyber security managed services?
  5. What is cybersecurity service management?
  6. What are the examples of managed security services?
  7. What is the role of cyber security management?
  8. How much do cybersecurity services cost?

What are the top 3 cybersecurity companies?

There isn’t a universally agreed-upon top three, since the best cybersecurity company depends on an organization’s size, needs, and budget. CrowdStrike, Palo Alto Networks, and Microsoft are widely recognized for their cybersecurity products and services, including threat detection, network security, and cloud protection. For managed cybersecurity services, compare providers based on their expertise, monitoring and response capabilities, industry experience, and fit with your existing systems.

What is the average cost of cyber security services?

There’s no single average cost for cybersecurity services because pricing depends on your organization’s size, risk level, systems, and the type of support needed. Small businesses may pay a few hundred to several thousand dollars per month for ongoing managed security, while assessments, compliance projects, and incident response are often priced separately. The best way to estimate your cost is to identify your priorities and request a detailed quote that explains what’s included, how support is provided, and whether there are additional fees.

Can I make $200,000 a year in cyber security?

Yes, earning $200,000 a year in cybersecurity is possible, especially in senior or specialized roles such as security architect, director of information security, or security consultant. Reaching that level often requires substantial experience, in-demand technical or leadership skills, and working in a higher-paying market; compensation may also include bonuses or stock rather than base salary alone. Pay varies widely by location, employer, and role, so $200,000 is achievable for some professionals but is not a typical starting salary or a guaranteed outcome.

What are cyber security managed services?

Cybersecurity managed services are ongoing security solutions provided by an outside specialist to help protect an organization’s systems, data, and users. Depending on the provider and service plan, they may include security monitoring, threat detection, vulnerability and patch management, access controls, employee training, and incident response support. These services can supplement an in-house IT team or provide security expertise a business does not have internally.

What is cybersecurity service management?

Cybersecurity service management is the process of planning, coordinating, and overseeing the security services an organization uses to protect its systems, data, and users. It may include managing security monitoring, access controls, vulnerability updates, incident response, employee training, and reporting. The goal is to make these services work together, align them with business needs, and continually adapt them as threats and technology change.

What are the examples of managed security services?

Examples of managed security services include 24/7 security monitoring and threat detection, managed firewalls, endpoint protection, vulnerability scanning and patch management, email security, identity and access management, security awareness training, data backup and recovery, and incident response support. A provider may deliver these services individually or combine them into a broader program tailored to an organization’s systems, risks, and needs.

What is the role of cyber security management?

Cybersecurity management helps an organization protect its systems, networks, and sensitive information by coordinating security policies, tools, and practices. It includes identifying and reducing risks, managing access, monitoring for suspicious activity, preparing for and responding to incidents, and helping employees follow safe security practices. By regularly reviewing and improving these measures, cybersecurity management supports business continuity and helps the organization adapt to changing threats.

How much do cybersecurity services cost?

The cost of cybersecurity services depends on your organization’s size, risk level, systems, and the type of support you need. A one-time security assessment typically costs less than ongoing services such as 24/7 monitoring, vulnerability management, incident response, or compliance support. Pricing may be based on a monthly subscription, the number of users or devices, or a custom scope of work. Requesting a detailed quote can help you compare what’s included and choose services that fit your budget and security priorities.

vdi cyber security

VDI Cyber Security: Best Practices for Protecting Virtual Desktops

VDI Cybersecurity: Protecting Virtual Desktops and the Data They Access

Virtual desktop infrastructure (VDI) lets users access desktop environments hosted on centralized servers or cloud platforms. Instead of keeping an entire desktop environment on each device, an organization delivers it remotely over a network. This can make it easier to manage systems and support remote work—but VDI is not automatically secure. Its security depends on how the environment is designed, configured, monitored, and maintained.

A strong VDI cybersecurity strategy protects the virtual desktops, the infrastructure that hosts them, the connections users rely on, and the data those desktops can access.

How VDI Can Strengthen Security

VDI can reduce some risks associated with traditional desktop computing. Because applications and data can remain in a centralized environment, organizations may have more control over software, updates, access, and data storage. If a laptop is lost or stolen, sensitive files may be less exposed when they are not stored locally.

Centralized management can also help IT teams apply consistent security policies across many desktops. For example, administrators can standardize configurations, remove outdated software, and restrict access to sensitive resources. These advantages are most effective when paired with appropriate controls; centralization alone does not guarantee protection.

Common VDI Security Risks

  • Compromised accounts: Stolen or weak credentials can give attackers access to virtual desktops and connected systems.
  • Misconfigured infrastructure: Incorrect permissions, exposed management interfaces, or overly permissive network rules can create openings for attackers.
  • Unpatched systems: Virtual desktop images, hypervisors, gateways, brokers, and other components can contain vulnerabilities if updates are delayed.
  • Insecure endpoints: A virtual desktop may be centrally hosted, but users still connect from physical devices that can be infected, outdated, or shared.
  • Data leakage: Features such as clipboard sharing, printing, file transfer, and local drive mapping can allow information to move outside the controlled environment.
  • Service disruption: VDI depends on infrastructure, network connectivity, and identity services. Outages or denial-of-service attacks can prevent users from working.
  • Excessive privileges: Users and administrators with more access than they need can increase the impact of an account compromise or human error.

Best Practices for Securing VDI

Use Strong Identity and Access Controls

Require multifactor authentication, especially for remote access and privileged accounts. Apply role-based access controls so users can reach only the desktops, applications, and data required for their work. Review access regularly and promptly remove permissions when roles change or accounts are no longer needed.

Secure the Connection

Use secure, supported connection methods and protect traffic with appropriate encryption. Avoid exposing administrative interfaces directly to the public internet. Where possible, use a secure access gateway and limit connections based on identity, device health, location, or other risk signals.

Harden and Update the Environment

Maintain a clear inventory of VDI components, including desktop images, brokers, gateways, hypervisors, and management tools. Apply security updates promptly, remove unnecessary services, and use hardened baseline configurations. Test updates and image changes before broad deployment to reduce the risk of disruption.

Protect Endpoints and Manage Data Movement

Secure the devices users connect from with endpoint protection, current operating system updates, and device compliance checks. Configure clipboard access, printing, downloads, file transfers, and local drive redirection according to the sensitivity of the work. In some environments, these features may need to be restricted or disabled.

Segment Networks and Limit Privileges

Separate VDI components and user groups where practical, and restrict communication to what is necessary. Keep management networks isolated from ordinary user traffic. Use separate, tightly controlled administrative accounts, and avoid using privileged accounts for routine work.

Monitor and Test

Collect logs from identity systems, VDI platforms, endpoints, and network controls. Monitor for unusual sign-in patterns, unexpected privilege changes, suspicious data transfers, and repeated access failures. Test incident response procedures and maintain backups or recovery plans for critical systems and desktop images.

Balance Security with Usability

Security controls that are too restrictive can interfere with legitimate work, while controls that are too permissive can expose data. Organizations should assess the sensitivity of their information, the needs of their users, and the risks of each workflow. A contractor handling general business applications may require different access than an employee working with regulated or confidential information.

It is also important to distinguish between persistent and nonpersistent desktops. Nonpersistent desktops can be rebuilt from a standard image, which may simplify maintenance, but user data and configuration must be stored appropriately. Persistent desktops can preserve user-specific changes, but they require careful patching and lifecycle management. Neither model is inherently secure in every situation.

Building a Practical VDI Security Program

Start by mapping the VDI environment: identify its components, users, data flows, external connections, and dependencies. Then evaluate access controls, patching practices, endpoint requirements, data transfer settings, monitoring, and recovery plans. Prioritize improvements based on risk and verify that security measures work as intended through regular reviews and testing.

VDI can support a more controlled desktop environment, but it also concentrates important systems and access in shared infrastructure. Protecting it requires layered security across identities, servers, endpoints, networks, and data. With thoughtful configuration and ongoing oversight, organizations can make VDI a useful part of a broader cybersecurity program.


7 Key Cybersecurity Benefits of Virtual Desktop Infrastructure (VDI)

  1. Centralized security management
  2. Consistent desktop configurations
  3. Simplified patch deployment
  4. Reduced local data storage
  5. Stronger access control options
  6. Easier monitoring and auditing
  7. Faster desktop recovery


6 VDI Cybersecurity Risks and Drawbacks

  1. Centralized infrastructure can become a high-value target.
  2. Misconfigured access may expose desktops and data.
  3. Compromised credentials can grant broad access.
  4. Outages can disrupt many users at once.
  5. Endpoint devices can still introduce malware.
  6. Security tools and maintenance can be costly.

Centralized security management

Centralized security management is a key cybersecurity advantage of VDI. Because virtual desktops are managed from a central environment, IT teams can apply consistent security policies, deploy patches, update software, and adjust user permissions across many desktops more efficiently. This centralized oversight can reduce configuration differences and help teams respond faster when a vulnerability or security issue arises. Organizations should still monitor the underlying infrastructure and connected devices, since centralized management does not eliminate every security risk.

Consistent desktop configurations

Consistent desktop configurations are a key cybersecurity advantage of VDI. IT teams can create and maintain standardized desktop images with approved software, security settings, and access controls, then apply them across many users. This reduces configuration drift, limits opportunities for insecure settings or unapproved applications, and makes it easier to patch systems and verify compliance. When a desktop becomes compromised or misconfigured, it can often be restored from a trusted image, helping teams return it to a known, secure state.

Simplified patch deployment

Simplified patch deployment: VDI lets IT teams update centralized desktop images and systems instead of relying on users to patch each computer individually. This can make it easier to roll out security fixes consistently, reduce the time vulnerable software remains unpatched, and verify that virtual desktops are using approved versions. For persistent desktops and other individually managed components, updates may still require separate deployment and monitoring.

Reduced local data storage

Reduced local data storage can help lower the risk of sensitive information being exposed if a laptop or other endpoint is lost, stolen, or compromised. With VDI, files and applications can remain in a centrally managed environment rather than being stored directly on each user’s device. This gives IT teams more control over access, backups, and data protection policies. However, organizations should also secure the VDI platform and manage features such as downloads, printing, and clipboard sharing to prevent data from leaving the protected environment.

Stronger access control options

One key cybersecurity advantage of VDI is its stronger access control options. Because virtual desktops are managed centrally, IT teams can apply consistent rules for who can sign in, which applications and data they can access, and what actions they can perform. Multifactor authentication, role-based permissions, and restrictions based on device or location can add further layers of protection. These controls help limit unauthorized access and reduce the potential impact of a compromised account.

Easier monitoring and auditing

VDI can make security monitoring and auditing easier by centralizing desktops, applications, and activity logs in a managed environment. Instead of tracking activity across many individual computers, IT teams can review access, system changes, and security events from a smaller set of centralized tools. This can help organizations spot unusual behavior, investigate incidents, and demonstrate compliance with internal policies or regulatory requirements—provided logging is configured appropriately and records are retained securely.

Faster desktop recovery

Faster desktop recovery: VDI can help users get back to work quickly after a desktop issue or security incident. Because virtual desktops are centrally managed, IT teams can restore a user’s environment from a clean, standardized image instead of rebuilding a physical computer from scratch. This can reduce downtime and help limit the impact of malware or configuration problems, especially when recovery images and user data are backed up and tested regularly.

Centralized infrastructure can become a high-value target.

Centralized VDI infrastructure can become a high-value target because it may host many users’ desktops, applications, and access to sensitive data in one environment. If attackers compromise a virtual desktop management platform, connection broker, or administrator account, the impact could extend across many users and systems. Organizations can reduce this risk by limiting administrative access, requiring multifactor authentication, segmenting networks, applying security updates promptly, and monitoring for suspicious activity.

Misconfigured access may expose desktops and data.

Misconfigured access can expose virtual desktops and sensitive data to people who should not have them. For example, overly broad permissions, weak authentication requirements, or improperly secured remote connections may let an unauthorized user access company systems. Limiting access by role, requiring multifactor authentication, and regularly reviewing permissions can help reduce this risk.

Compromised credentials can grant broad access.

Compromised credentials pose a serious risk in a VDI environment because a single stolen account may give an attacker access to a virtual desktop, connected applications, and sensitive data. If the account has broad permissions or lacks multifactor authentication, the attacker may be able to move beyond the initial desktop and reach additional systems. Limit this risk with multifactor authentication, least-privilege access, strong monitoring, and prompt account lockout and recovery procedures.

Outages can disrupt many users at once.

A major drawback of VDI is that an outage can affect many users at the same time. Because virtual desktops depend on shared infrastructure, a failure in a server, network connection, or identity system may prevent entire teams from accessing their desktops and applications. This can interrupt daily operations and delay critical work, so organizations need reliable backup systems, redundancy, and tested recovery plans.

Endpoint devices can still introduce malware.

Although VDI centralizes desktops and data, endpoint devices can still introduce malware into the environment. A compromised laptop, thin client, or personal device may expose login credentials, capture sensitive information, or spread malicious activity through an active VDI session. Organizations should protect endpoints with up-to-date security software, regular patching, device health checks, and strong authentication, while limiting what users can copy, download, or transfer between the virtual desktop and local device.

Security tools and maintenance can be costly.

A potential drawback of VDI cybersecurity is the cost of security tools and ongoing maintenance. Organizations may need to invest in identity protection, endpoint monitoring, encryption, threat detection, and backup solutions, along with the infrastructure and skilled staff required to manage them. Regular updates, security assessments, and incident response planning add to the expense. For smaller organizations, these costs can make it challenging to maintain strong protection as the VDI environment grows.

cyber security operations

Cyber Security Operations: A Practical Guide to Protecting Your Organization

Cybersecurity Operations: A Practical Guide to Protecting Your Organization

Cybersecurity operations are the people, processes, and technologies an organization uses to monitor its systems, detect threats, and respond to security incidents. They help turn cybersecurity from a collection of tools into an ongoing practice: identifying risks, protecting important assets, and limiting damage when something goes wrong.

As businesses rely on cloud services, connected devices, remote work, and digital data, their potential attack surface continues to grow. Effective cybersecurity operations help organizations keep pace by providing visibility into their environments and a coordinated way to handle threats.

What Are Cybersecurity Operations?

Cybersecurity operations cover the day-to-day work of defending an organization’s networks, devices, applications, and information. This work may be performed by an internal security team, a managed security provider, or a combination of both.

A central part of many operations programs is a security operations center, or SOC. A SOC is a team or function responsible for monitoring security activity, investigating alerts, and coordinating responses. Not every organization needs a dedicated, 24-hour SOC, but every organization benefits from clear ownership of security monitoring and incident response.

Core Functions of a Security Operations Program

Continuous Monitoring

Teams collect and review security data from sources such as endpoints, servers, cloud platforms, identity systems, and network devices. Monitoring can reveal unusual behavior, suspicious logins, malware activity, or changes that may indicate an attack.

Threat Detection and Investigation

Security tools generate alerts when activity matches known indicators or appears unusual. Analysts assess those alerts, determine whether they represent a real threat, and gather context before deciding what to do. Good detection depends not only on technology but also on well-tuned rules and an understanding of normal business activity.

Incident Response

When a security incident is confirmed, the response team works to contain it, remove the threat, and restore affected systems. A documented incident response plan clarifies roles, decision-making authority, communication steps, and recovery priorities before an emergency occurs.

Vulnerability and Patch Management

Cybersecurity operations also include finding weaknesses in software, devices, and configurations. Teams prioritize vulnerabilities based on factors such as severity, exposure, and business impact, then coordinate testing and remediation. Timely updates can reduce the opportunities attackers have to exploit known flaws.

Threat Intelligence

Threat intelligence provides information about current attacker techniques, malicious infrastructure, and emerging risks. Used thoughtfully, it can help teams improve detection and focus their attention. Intelligence is most useful when it is relevant to the organization’s systems and connected to practical defensive actions.

People, Processes, and Technology

Strong cybersecurity operations require more than purchasing security software. The three essential elements are:

  • People: Skilled staff who can interpret alerts, make sound decisions, and communicate with technical teams and business leaders.
  • Processes: Clear procedures for monitoring, escalation, incident response, recovery, and continuous improvement.
  • Technology: Tools that provide visibility, help identify threats, and support investigation and response.

When one of these elements is missing, the entire program can suffer. For example, a security platform may generate more alerts than a small team can investigate. Well-designed processes help prioritize those alerts, while training and automation can help staff act efficiently.

Common Challenges

Organizations often face a high volume of security alerts, limited staffing, and complex technology environments. Data may be spread across on-premises systems, multiple cloud services, and employee devices. Inconsistent logging or unclear ownership can make investigations slower and less reliable.

Alert fatigue is another common concern. When teams receive too many low-priority or false-positive alerts, important warnings can be overlooked. Regularly reviewing detection rules, improving asset visibility, and prioritizing alerts by risk can help reduce this problem.

How to Improve Cybersecurity Operations

  1. Understand your environment. Maintain an inventory of important systems, devices, accounts, and data. You cannot reliably protect assets you do not know exist.
  2. Prioritize business risks. Identify the systems and information whose loss or disruption would have the greatest impact, then align monitoring and response plans with those priorities.
  3. Establish clear procedures. Document how incidents are reported, investigated, escalated, contained, and communicated.
  4. Improve visibility. Collect useful security logs from critical systems and protect those logs from unauthorized changes.
  5. Practice response. Tabletop exercises and technical drills help teams find gaps in their plans before a real incident occurs.
  6. Measure and refine. Review response times, recurring incident types, alert quality, and remediation progress. Use the results to improve the program.

The Role of Automation and AI

Automation can handle repetitive tasks, such as enriching an alert with related information or isolating a device under approved conditions. These capabilities can help teams respond faster, but they should be tested and governed carefully. High-impact actions should have appropriate safeguards, oversight, and a way to reverse mistakes.

Artificial intelligence can help analyze large volumes of activity and surface patterns for investigation. It does not replace security professionals or eliminate the need for sound processes. Organizations should evaluate how automated systems use data, validate their results, and ensure that people remain accountable for important security decisions.

Building a Resilient Security Program

Cybersecurity operations are an ongoing cycle of preparation, monitoring, detection, response, and improvement. No organization can prevent every attack, but a well-organized program can make threats easier to identify and incidents less disruptive.

By combining capable people, tested procedures, and appropriately selected technology, organizations can strengthen their defenses and recover more effectively when security events occur. The best starting point is a clear understanding of critical assets, realistic risks, and the actions the organization will take when those risks become real.


Top 5 Essential Cybersecurity Tips for Protecting Your Operations

  1. Enable multi-factor authentication on all accounts.
  2. Patch systems promptly to close known vulnerabilities.
  3. Monitor logs for unusual activity and failed logins.
  4. Back up critical data and test recovery regularly.
  5. Train staff to spot phishing and report incidents.

Enable multi-factor authentication on all accounts.

Enable multi-factor authentication (MFA) on every account that supports it, especially email, banking, administrator, and cloud service accounts. MFA requires an additional verification step—such as an authenticator app, security key, or passkey—along with a password, making it harder for attackers to gain access with stolen or reused credentials. For stronger protection, choose phishing-resistant options like passkeys or hardware security keys when available, and keep recovery methods secure and up to date.

Patch systems promptly to close known vulnerabilities.

Patch systems promptly to close known vulnerabilities before attackers can exploit them. Apply security updates to operating systems, applications, devices, and cloud services as soon as practical, prioritizing internet-facing and business-critical systems. Test patches where needed, schedule updates to limit disruption, and verify that installations succeed. For systems that cannot be patched right away, use temporary safeguards—such as restricting access or disabling affected features—and track the issue until it is resolved.

Monitor logs for unusual activity and failed logins.

Monitor system, application, and network logs for unusual activity, including repeated failed login attempts, logins from unfamiliar locations, and access at unexpected times. These patterns can signal a brute-force attack, compromised account, or other security issue. Centralize logs where possible, set alerts for suspicious behavior, and investigate promptly. Keep logs protected and retain them long enough to support incident investigations.

Back up critical data and test recovery regularly.

Back up critical data regularly and keep copies separate from the systems they protect, so an attack, hardware failure, or accidental deletion won’t destroy every version. Just as important, test your recovery process on a regular schedule: verify that backups are complete, can be restored, and meet your organization’s recovery needs. A backup is only useful if you can access it and restore operations when it matters.

Train staff to spot phishing and report incidents.

Train staff to recognize phishing emails, texts, and calls by watching for suspicious links, unexpected attachments, urgent demands, and requests for sensitive information. Encourage employees to report anything suspicious promptly through a clear, easy-to-use process—even if they are unsure or have already clicked a link. Regular training and realistic practice help people respond confidently, giving security teams a better chance to contain threats before they spread.

cybersecurity as a service

Cybersecurity as a Service: A Practical Guide for Businesses

Cybersecurity as a Service: A Practical Guide for Businesses

Cybersecurity is no longer a one-time project. Threats change constantly, software needs regular updates, and even well-prepared organizations can face new risks. For many businesses, keeping up requires more time and specialized expertise than an in-house team can provide. Cybersecurity as a Service (CSaaS) offers another approach: access to ongoing security tools and expertise through an external provider.

What Is Cybersecurity as a Service?

Cybersecurity as a Service is a model in which an organization relies on a third-party provider for some or all of its security operations. Services are typically delivered on an ongoing basis and may be tailored to the organization’s size, systems, risk profile, and regulatory requirements.

Depending on the provider and service plan, CSaaS may include security monitoring, threat detection, vulnerability assessments, incident response support, employee training, and help with security policies. Some providers focus on a specific area, while others offer a broader managed security program.

Common Cybersecurity as a Service Offerings

  • Security monitoring: Reviewing activity across networks, devices, cloud environments, and applications to identify suspicious behavior.
  • Managed detection and response: Investigating potential threats and helping contain or remediate them. The exact level of response varies by provider and contract.
  • Vulnerability management: Identifying weaknesses in systems and helping prioritize fixes based on risk.
  • Endpoint protection: Managing security for computers, mobile devices, and servers.
  • Cloud security: Helping protect cloud accounts, workloads, data, and configurations.
  • Identity and access management: Supporting controls such as multifactor authentication, role-based access, and account reviews.
  • Security awareness training: Teaching employees how to recognize phishing, handle sensitive information, and report concerns.
  • Incident response planning: Preparing procedures and providing support when a security event occurs.

Why Businesses Choose CSaaS

Access to specialized expertise: Security providers may bring experience across different technologies and threat scenarios. This can be valuable for organizations that do not have a dedicated security team.

Ongoing coverage: Security risks do not follow business hours. Some services provide continuous monitoring or on-call support, depending on the agreement.

Predictable costs: A subscription or managed-services arrangement can make security spending easier to plan than building every capability internally. Costs and included services vary, so it is important to review the full scope.

Room to scale: Services can often be adjusted as an organization adds employees, locations, applications, or cloud systems.

More focus on core work: By delegating selected security tasks, internal staff may have more time for other business priorities. Outsourcing does not remove the organization’s responsibility for managing risk, however.

What CSaaS Does Not Do

Cybersecurity as a Service is not a guarantee that an organization will never experience a breach. No provider can eliminate every risk, and technology alone cannot prevent every incident. Effective security still depends on clear policies, reliable backups, timely software updates, appropriate access controls, and informed employees.

Responsibility is also shared. The provider may operate specific tools or monitor defined systems, while the customer remains responsible for decisions such as approving access, protecting business data, and following applicable legal or regulatory requirements. Those boundaries should be documented before service begins.

How to Choose a Provider

Start by identifying the problems the service needs to solve. A business seeking help with after-hours monitoring may need a different arrangement from one preparing for a compliance review or improving cloud security.

  • Define the scope: Confirm which systems, locations, users, and data are covered—and which are not.
  • Understand response procedures: Ask who investigates alerts, who can take action, how quickly the provider responds, and when the business will be contacted.
  • Review service levels: Look for clear commitments about availability, response times, reporting, and escalation. Check how those commitments are measured.
  • Ask about data handling: Understand what information the provider collects, where it is stored, who can access it, and how it is protected.
  • Check experience and references: Look for experience with organizations of a similar size, industry, and technology environment.
  • Clarify responsibilities: Establish who manages software updates, account permissions, investigations, backups, and incident communications.
  • Plan for continuity: Ask how service handoffs, data access, and security operations will work if the contract ends.

Making the Most of the Service

Before onboarding, create an accurate inventory of devices, applications, cloud services, and important data. Share existing policies and known risks with the provider, and identify internal contacts who can make decisions during an incident. Regularly review reports and hold meetings to discuss unresolved issues, changing business needs, and recommended improvements.

It is also important to test the relationship before an emergency. Tabletop exercises and incident-response drills can reveal unclear responsibilities and communication gaps while there is still time to address them.

Conclusion

Cybersecurity as a Service can help businesses access security expertise and ongoing support without building every capability in-house. The value depends on choosing services that match actual risks, defining responsibilities clearly, and staying actively involved. With a well-scoped agreement and sound internal practices, CSaaS can become a practical part of a broader cybersecurity program.


Top 5 Advantages of Cybersecurity as a Service for Your Business

  1. Access to specialized security expertise
  2. Continuous threat monitoring
  3. Predictable subscription costs
  4. Scales with business needs
  5. Frees staff to focus on core work


7 Potential Drawbacks of Cybersecurity as a Service: Costs, Control, and More

  1. Ongoing subscription costs can add up.
  2. Less direct control over security operations.
  3. Service quality varies between providers.
  4. Sensitive data may be shared with a vendor.
  5. Response times may depend on the service agreement.
  6. Integrating tools can be complex.
  7. Outsourcing does not eliminate business risk.

Access to specialized security expertise

Cybersecurity as a Service gives businesses access to specialized security expertise without requiring them to hire and maintain a large in-house team. Providers bring experience with evolving threats, security tools, and industry practices, helping organizations identify risks, strengthen defenses, and respond to potential incidents. This expertise can be especially valuable for small and midsize businesses that need knowledgeable support but may not have the resources to build a dedicated security department.

Continuous threat monitoring

Continuous threat monitoring helps organizations spot suspicious activity as it happens, rather than discovering it after significant damage has occurred. A cybersecurity provider can monitor networks, devices, and cloud systems around the clock, investigate alerts, and notify the right people when action is needed. This ongoing visibility can help businesses respond to emerging threats more quickly, even when their internal team is unavailable.

Predictable subscription costs

Cybersecurity as a Service can make security spending more predictable through a regular subscription fee. Instead of making large upfront investments in tools, hiring, and ongoing maintenance, businesses can budget for an agreed set of services each month or year. Costs depend on the provider and scope, so reviewing what’s included—and what may incur extra charges—helps avoid surprises.

Scales with business needs

Cybersecurity as a Service can scale as your business changes. You can adjust coverage as you add employees, open new locations, adopt cloud tools, or face new security requirements—without having to build an entirely new in-house security team. This flexibility helps keep protection aligned with your needs and budget as your organization grows.

Frees staff to focus on core work

Cybersecurity as a Service can free employees from time-consuming security tasks, such as monitoring alerts, managing tools, and tracking routine updates. With a specialized provider handling agreed-upon responsibilities, your team can spend more time on the work that directly supports your business goals. Outsourcing security does not eliminate the need for internal oversight, but it can help staff focus their attention where it matters most.

Ongoing subscription costs can add up.

Ongoing subscription costs for cybersecurity as a service can add up over time, especially as a business grows or adds more users, devices, and security features. What starts as a manageable monthly expense may become a significant part of the IT budget, so it’s important to review pricing, renewal terms, and potential add-on fees regularly. Compare the total long-term cost with the value and coverage provided to make sure the service continues to fit your needs.

Less direct control over security operations.

One potential drawback of cybersecurity as a service is having less direct control over day-to-day security operations. When an outside provider manages monitoring, tools, or incident response, your team may have limited visibility into how decisions are made or how quickly actions are taken. This can create challenges if the provider’s procedures do not align with your business priorities. To reduce the risk, define responsibilities, approval requirements, reporting expectations, and escalation procedures clearly in the service agreement.

Service quality varies between providers.

Service quality can vary significantly between cybersecurity providers, making it difficult to know what level of protection you’ll receive. Providers may differ in their expertise, monitoring capabilities, response times, communication, and the tools they use. A service that sounds comprehensive may also have important limits in its contract. Before choosing a provider, review exactly what’s included, ask how incidents are handled, and check references to ensure the service meets your organization’s needs.

Sensitive data may be shared with a vendor.

One potential drawback of cybersecurity as a service is that protecting your systems may require sharing sensitive data with an outside vendor. Depending on the service, the provider could access security logs, user information, system configurations, or other confidential details. This creates additional privacy and data-protection risks, especially if the vendor’s controls or practices are inadequate. Before signing an agreement, review what data will be collected, how it will be stored and protected, who can access it, and whether it will be shared with subcontractors.

Response times may depend on the service agreement.

Response times for cybersecurity as a service can depend on the terms of the service agreement. A provider may prioritize incidents according to severity, offer different response levels for different plans, or limit support to certain hours. If those details are unclear, a business could wait longer than expected for help during a security incident. Before signing, confirm response-time commitments, after-hours coverage, escalation procedures, and what actions the provider is authorized to take.

Integrating tools can be complex.

Integrating cybersecurity tools can be complex, especially when a provider’s platforms need to work with existing networks, cloud services, and business applications. Compatibility issues, duplicated alerts, or gaps in data sharing can make it harder to get a clear view of security risks. Setup may also require changes to workflows and access controls, so businesses should clarify integration requirements, responsibilities, and ongoing support before adopting a service.

Outsourcing does not eliminate business risk.

Outsourcing cybersecurity can add valuable expertise and support, but it does not eliminate a business’s responsibility for managing risk. The provider can only protect the systems, data, and processes covered by the agreement, and gaps in scope, communication, or internal practices may leave the organization exposed. Businesses still need to make informed security decisions, maintain sound policies, train employees, and understand who is responsible for each task—especially during an incident.

cybersecurity service

Enhancing Your Security: Comprehensive Cybersecurity Services for Your Business

The Importance of Cybersecurity Services in Today’s Digital World

In today’s interconnected world, cybersecurity has become a critical aspect of any organization’s operations. With the increasing number of cyber threats and attacks, businesses need to prioritize their cybersecurity measures to protect sensitive data and maintain the trust of their customers.

What Are Cybersecurity Services?

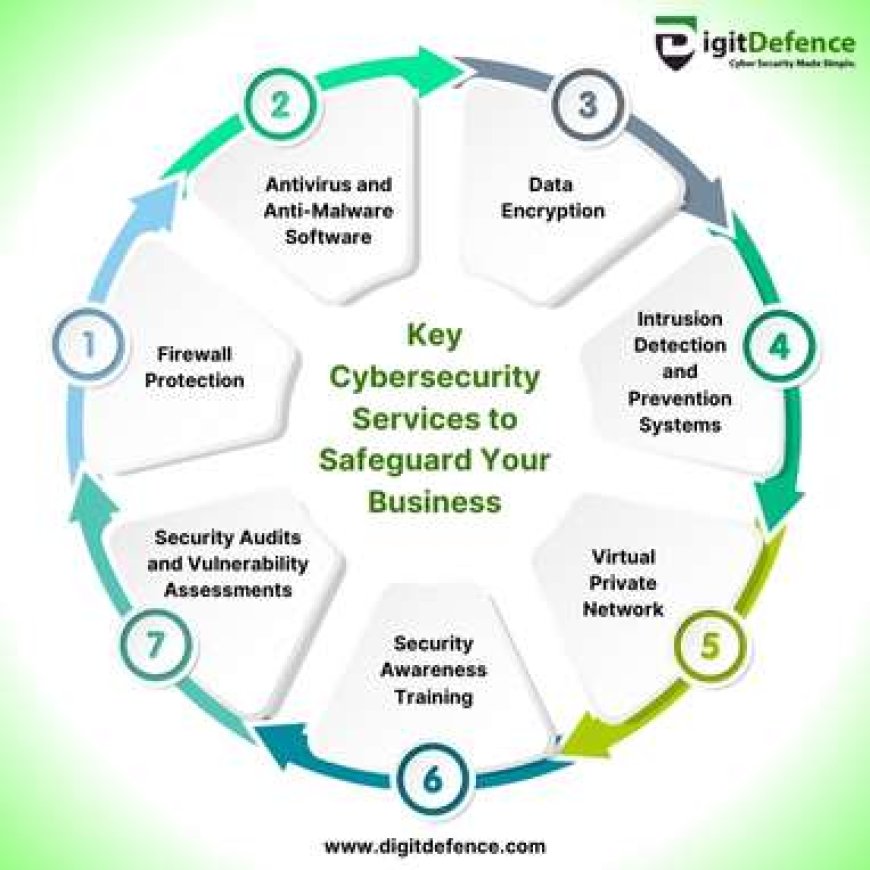
Cybersecurity services encompass a range of practices and technologies designed to protect networks, devices, programs, and data from unauthorized access or attacks. These services aim to ensure the confidentiality, integrity, and availability of information systems.

The Role of Cybersecurity Services

Effective cybersecurity services play a crucial role in safeguarding organizations against various cyber threats, including malware, phishing attacks, ransomware, and data breaches. By implementing robust cybersecurity measures, businesses can prevent unauthorized access to their systems and mitigate potential risks.

Benefits of Cybersecurity Services

Investing in cybersecurity services offers numerous benefits to organizations, such as:

  • Data Protection: Secure sensitive information from unauthorized access or theft.
  • Threat Detection: Identify and respond to potential security threats in real-time.
  • Compliance: Ensure compliance with industry regulations and standards related to data security.
  • Business Continuity: Minimize disruptions to operations caused by cyber incidents.
  • Customer Trust: Build trust with customers by demonstrating a commitment to protecting their data.

Cybersecurity Service Providers

Many organizations rely on specialized cybersecurity service providers to enhance their security posture. These providers offer a range of services, including:

  • Network Security: Implement firewalls, intrusion detection systems, and secure VPNs.
  • Endpoint Security: Protect individual devices from malware and other cyber threats.
  • Incident Response: Develop strategies for responding to security incidents effectively.
  • Vulnerability Management: Identify and address vulnerabilities in systems and applications.

In Conclusion

In conclusion, cybersecurity services are essential for safeguarding organizations against evolving cyber threats. By investing in robust cybersecurity measures and working with reputable service providers, businesses can protect their valuable assets and maintain a secure digital environment for their operations.

Contact us today to learn more about how our cybersecurity services can help secure your organization’s digital infrastructure.


9 Essential Benefits of Cybersecurity Services for Protecting Your Business

  1. Protect sensitive data from unauthorized access
  2. Prevent malware infections and cyber attacks
  3. Ensure compliance with industry regulations and standards
  4. Detect and respond to security threats in real-time
  5. Minimize disruptions to business operations caused by cyber incidents
  6. Enhance customer trust by demonstrating a commitment to data security
  7. Safeguard financial information and transactions
  8. Mitigate risks of data breaches and identity theft
  9. Provide peace of mind knowing that your digital assets are secure


Challenges of Cybersecurity Services: High Costs, Complexity, False Positives, and User Resistance

  1. Costly Investment
  2. Complexity
  3. False Positives
  4. User Resistance

Protect sensitive data from unauthorized access

One significant advantage of cybersecurity services is their ability to protect sensitive data from unauthorized access. By implementing robust security measures, organizations can safeguard confidential information, such as customer data, financial records, and intellectual property, from cyber threats. This proactive approach not only helps prevent data breaches and unauthorized disclosures but also ensures the integrity and confidentiality of critical assets, fostering trust with customers and stakeholders.

Prevent malware infections and cyber attacks

One of the key benefits of cybersecurity services is their ability to prevent malware infections and cyber attacks. By implementing robust security measures, organizations can proactively safeguard their networks, systems, and data from malicious software and cyber threats. This proactive approach not only helps prevent costly downtime and data breaches but also ensures the continuity of business operations without disruptions caused by malware infections or cyber attacks.

Ensure compliance with industry regulations and standards

Ensuring compliance with industry regulations and standards is a crucial benefit of cybersecurity services. By implementing robust security measures, organizations can meet the requirements set forth by regulatory bodies and industry standards. Compliance not only helps in avoiding potential legal repercussions but also demonstrates a commitment to data security and privacy, building trust with customers and stakeholders. Cybersecurity services play a vital role in guiding businesses towards adherence to relevant regulations, ensuring that sensitive information is handled in accordance with best practices and legal mandates.

Detect and respond to security threats in real-time

One significant advantage of cybersecurity services is the ability to detect and respond to security threats in real-time. By leveraging advanced monitoring tools and threat detection technologies, organizations can swiftly identify suspicious activities or potential breaches within their networks. This proactive approach allows for immediate action to be taken to mitigate the impact of security incidents, minimizing potential damage and ensuring the continuity of business operations. Real-time threat detection and response are crucial components of a comprehensive cybersecurity strategy that helps organizations stay one step ahead of cyber threats.

Minimize disruptions to business operations caused by cyber incidents

One significant advantage of cybersecurity services is their ability to minimize disruptions to business operations caused by cyber incidents. By implementing robust security measures and proactive monitoring, organizations can effectively identify and mitigate potential cyber threats before they escalate into major disruptions. This proactive approach not only helps maintain the continuity of business operations but also reduces the risk of financial losses and reputational damage associated with cyber incidents. Investing in cybersecurity services can provide businesses with the peace of mind that their operations are protected against unforeseen disruptions, allowing them to focus on their core activities without interruption.

Enhance customer trust by demonstrating a commitment to data security

By investing in cybersecurity services, organizations can enhance customer trust by demonstrating a strong commitment to data security. When customers know that their sensitive information is protected from cyber threats and unauthorized access, they are more likely to have confidence in the organization’s ability to safeguard their data. This commitment to data security not only helps build trust with existing customers but also attracts new customers who prioritize the protection of their personal information. Ultimately, prioritizing cybersecurity measures sends a clear message that the organization values the privacy and security of its customers’ data, fostering long-term relationships built on trust and reliability.

Safeguard financial information and transactions

Cybersecurity services play a crucial role in safeguarding financial information and transactions from unauthorized access and fraud. By implementing robust security measures, organizations can protect sensitive financial data, such as bank account details, credit card information, and transaction records. Encryption techniques, secure payment gateways, and multi-factor authentication help ensure the confidentiality and integrity of financial transactions, reducing the risk of cyber attacks and financial losses. With cybersecurity services in place, businesses can instill trust in their customers and partners by demonstrating a commitment to protecting their financial information.

Mitigate risks of data breaches and identity theft

Cybersecurity services play a crucial role in mitigating the risks of data breaches and identity theft. By implementing robust security measures, organizations can protect sensitive information from unauthorized access and prevent cybercriminals from stealing valuable data. Proactive cybersecurity strategies, such as encryption, multi-factor authentication, and regular security audits, help safeguard against potential threats and ensure that personal and confidential data remains secure. By investing in cybersecurity services, businesses can significantly reduce the likelihood of data breaches and identity theft, thereby safeguarding their reputation and maintaining the trust of their customers.

Provide peace of mind knowing that your digital assets are secure

Cybersecurity services offer a valuable benefit by providing peace of mind to individuals and organizations, knowing that their digital assets are secure. By implementing robust security measures and proactive monitoring, cybersecurity services help prevent unauthorized access, data breaches, and other cyber threats. This assurance allows businesses to focus on their core activities without constantly worrying about the safety of their sensitive information, ultimately enhancing trust with customers and stakeholders.

Costly Investment

Implementing comprehensive cybersecurity services can pose a significant financial challenge for many organizations, particularly small businesses operating with constrained budgets. The cost of acquiring and maintaining sophisticated security measures, along with the need for ongoing monitoring and updates, can strain financial resources and divert funds from other essential areas of operation. Balancing the necessity of robust cybersecurity with the financial constraints faced by some organizations remains a persistent conundrum in the realm of digital security.

Complexity

The complexity of managing cybersecurity services poses a significant challenge for organizations lacking dedicated IT security teams. Securing networks, identifying vulnerabilities, and responding to cyber threats demand specialized knowledge and expertise that may be beyond the capabilities of general IT staff. Without the necessary skills and resources in place, organizations risk leaving their systems vulnerable to attacks and data breaches. As cyber threats continue to evolve, navigating the intricate landscape of cybersecurity becomes increasingly daunting for businesses without access to dedicated security professionals.

False Positives

False positives are a significant con of cybersecurity services as they can create unnecessary challenges for organizations. Security tools used in cybersecurity services may occasionally produce alerts that mistakenly identify benign activities as potential threats. This can result in wasted time and resources as teams investigate false alarms, diverting their attention from genuine security issues. Moreover, false positives can cause disruptions to normal business operations, leading to productivity losses and increased frustration among employees. Addressing the issue of false positives is crucial for organizations to streamline their cybersecurity efforts and ensure that genuine threats are promptly identified and addressed.

User Resistance

User Resistance can pose a significant challenge to cybersecurity services within an organization. When employees resist security measures, such as complex password requirements or multi-factor authentication, it can weaken the overall security posture and leave the organization vulnerable to cyber threats. User resistance may stem from inconvenience, lack of awareness about the importance of cybersecurity, or simply a desire for convenience over security. Addressing user resistance requires effective communication, training, and engagement to ensure that employees understand the rationale behind security measures and are motivated to comply with them for the greater protection of the organization’s data and systems.