cfchris.com

Loading

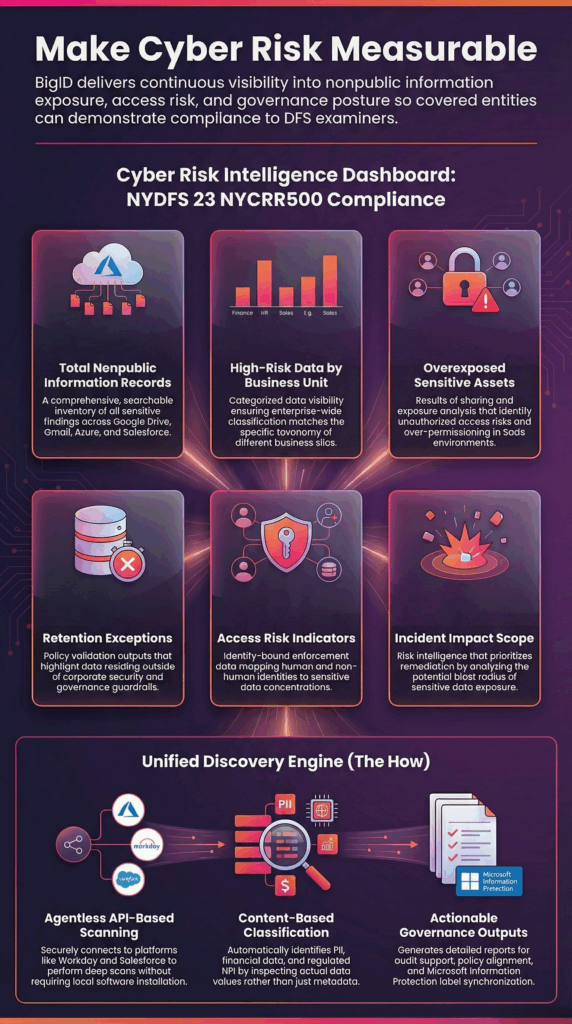
23 nycrr 500

Navigating Compliance: Understanding the Impact of 23 NYCRR 500

Article: 23 NYCRR 500

Understanding 23 NYCRR 500: New York’s Cybersecurity Regulation

23 NYCRR 500 is a cybersecurity regulation issued by the New York State Department of Financial Services (DFS). This regulation aims to protect sensitive data and information held by financial institutions operating in New York.

Key Requirements of 23 NYCRR 500

The regulation mandates financial institutions to:

  • Establish a cybersecurity program designed to protect nonpublic information.
  • Conduct regular risk assessments and implement cybersecurity measures based on identified risks.
  • Implement multi-factor authentication for accessing internal systems and sensitive data.
  • Maintain an incident response plan to address and recover from cybersecurity events promptly.
  • Provide cybersecurity awareness training to employees to enhance overall security posture.
  • Engage third-party service providers who comply with the regulation’s requirements.

Implications for Financial Institutions

Compliance with 23 NYCRR 500 is crucial for financial institutions as non-compliance can lead to severe penalties, including fines and reputational damage. By adhering to the regulation, organizations can strengthen their cybersecurity defenses, reduce the risk of data breaches, and safeguard customer information.

Conclusion

23 NYCRR 500 sets a high standard for cybersecurity practices within the financial sector in New York. Financial institutions subject to this regulation must prioritize data protection, implement robust security measures, and continually assess and enhance their cybersecurity posture to mitigate risks effectively.

© 2022 CFChris. All rights reserved.


Strengthening Cybersecurity: 8 Key Benefits of 23 NYCRR 500 for New York Financial Institutions

  1. Enhances cybersecurity measures for financial institutions in New York
  2. Protects sensitive data and nonpublic information from cyber threats
  3. Mandates regular risk assessments to identify and address vulnerabilities
  4. Requires the implementation of multi-factor authentication for enhanced security
  5. Promotes cybersecurity awareness training among employees
  6. Establishes incident response plans to mitigate the impact of cyber incidents
  7. Encourages collaboration with compliant third-party service providers
  8. Helps organizations strengthen their overall security posture and reduce data breach risks


Challenges of 23 NYCRR 500: Compliance Costs, Complexity, and Third-Party Provider Burdens

  1. Compliance costs
  2. Complexity
  3. Burden on third-party providers

Enhances cybersecurity measures for financial institutions in New York

The implementation of 23 NYCRR 500 significantly enhances cybersecurity measures for financial institutions operating in New York. By mandating the establishment of robust cybersecurity programs, conducting regular risk assessments, and implementing multi-factor authentication, the regulation strengthens the overall security posture of these institutions. This proactive approach not only helps in safeguarding sensitive data but also aids in preventing cyber threats and potential breaches, ultimately fostering a more secure environment for both the institutions and their clients.

Protects sensitive data and nonpublic information from cyber threats

One significant advantage of 23 NYCRR 500 is its ability to safeguard sensitive data and nonpublic information from cyber threats. By requiring financial institutions to establish robust cybersecurity programs and implement protective measures, the regulation helps prevent unauthorized access, data breaches, and other cyber incidents that could compromise the security and confidentiality of valuable information. This proactive approach not only enhances data protection but also instills trust among stakeholders, demonstrating a commitment to maintaining the integrity and privacy of sensitive data in today’s digital landscape.

Mandates regular risk assessments to identify and address vulnerabilities

One significant advantage of 23 NYCRR 500 is that it mandates regular risk assessments to identify and address vulnerabilities. By requiring financial institutions to conduct these assessments, the regulation promotes proactive measures to enhance cybersecurity defenses. Identifying potential risks allows organizations to implement targeted security measures, prioritize resource allocation, and mitigate vulnerabilities before they can be exploited. This proactive approach not only strengthens the overall security posture of financial institutions but also helps in safeguarding sensitive data and information from potential cyber threats.

Requires the implementation of multi-factor authentication for enhanced security

One significant advantage of 23 NYCRR 500 is its requirement for the implementation of multi-factor authentication to enhance security measures. By mandating the use of multi-factor authentication, the regulation adds an extra layer of protection to sensitive data and internal systems within financial institutions. This additional security measure helps prevent unauthorized access and significantly reduces the risk of data breaches or cyber attacks. Overall, the emphasis on multi-factor authentication under 23 NYCRR 500 plays a crucial role in bolstering cybersecurity defenses and safeguarding confidential information effectively.

Promotes cybersecurity awareness training among employees

One significant advantage of 23 NYCRR 500 is that it promotes cybersecurity awareness training among employees. By requiring financial institutions to provide training on cybersecurity best practices, potential threats, and how to respond to security incidents, the regulation helps enhance the overall security posture of organizations. This proactive approach not only equips employees with the knowledge and skills needed to identify and mitigate cyber risks but also fosters a culture of cybersecurity consciousness within the workplace. Ultimately, promoting cybersecurity awareness training among employees can contribute to a stronger defense against cyber threats and safeguard sensitive information effectively.

Establishes incident response plans to mitigate the impact of cyber incidents

One significant advantage of 23 NYCRR 500 is that it requires financial institutions to establish incident response plans to mitigate the impact of cyber incidents. By mandating the development of structured procedures for responding to cybersecurity breaches, this regulation helps organizations effectively manage and contain threats, minimize potential damages, and swiftly recover from security incidents. Implementing robust incident response plans ensures that financial institutions can respond promptly and decisively in the event of a cyber attack, enhancing their overall resilience against evolving cyber threats.

Encourages collaboration with compliant third-party service providers

One significant benefit of 23 NYCRR 500 is that it encourages collaboration with compliant third-party service providers. By engaging with service providers who adhere to the regulation’s cybersecurity requirements, financial institutions can enhance the overall security of their operations. This collaboration ensures that sensitive data shared with third parties is adequately protected, reducing the risk of data breaches and strengthening the cybersecurity ecosystem within the financial sector. The emphasis on partnering with compliant providers fosters a culture of shared responsibility for cybersecurity and promotes a more secure environment for all stakeholders involved.

Helps organizations strengthen their overall security posture and reduce data breach risks

One of the key benefits of 23 NYCRR 500 is that it helps organizations strengthen their overall security posture and reduce the risks of data breaches. By mandating the establishment of robust cybersecurity programs, regular risk assessments, and the implementation of security measures tailored to identified risks, this regulation ensures that financial institutions operating in New York prioritize data protection and enhance their resilience against cyber threats. Compliance with 23 NYCRR 500 not only safeguards sensitive information but also contributes to a more secure and trustworthy financial ecosystem.

Compliance costs

Implementing and maintaining a cybersecurity program in accordance with 23 NYCRR 500 can pose a significant financial burden on financial institutions. The costs associated with meeting the regulation’s requirements, such as conducting regular risk assessments, implementing security measures, providing employee training, and engaging compliant third-party service providers, can add up quickly. These compliance costs may strain the resources of smaller institutions and require substantial investments in cybersecurity infrastructure and personnel to ensure ongoing adherence to the regulation.

Complexity

The complexity of the regulatory requirements outlined in 23 NYCRR 500 presents a significant challenge, particularly for smaller organizations with constrained resources. Interpreting and implementing the intricate guidelines can be daunting, leading to potential compliance issues and increased operational burdens. Smaller entities may struggle to navigate the nuanced provisions effectively, highlighting the need for additional support and guidance in meeting the stringent cybersecurity standards set forth by the regulation.

Burden on third-party providers

One significant con of 23 NYCRR 500 is the burden it places on third-party providers. Financial institutions are required to verify that their external service providers adhere to the regulation, introducing an additional layer of oversight and management. Ensuring compliance among third parties can be complex and time-consuming, as institutions must monitor and assess the cybersecurity practices of each vendor to maintain regulatory alignment. This added responsibility increases the administrative workload for financial organizations and may lead to challenges in coordinating and enforcing cybersecurity standards across multiple external entities.
saas cyber security

Enhancing SaaS Cyber Security: Best Practices for Data Protection

The Importance of SaaS Cyber Security

The Importance of SaaS Cyber Security

Software as a Service (SaaS) has become increasingly popular among businesses for its convenience and scalability. However, with the rise of SaaS applications comes the need for robust cyber security measures to protect sensitive data and ensure business continuity.

Why SaaS Cyber Security Matters

Securing SaaS applications is crucial to safeguarding valuable information stored in the cloud. Cyber threats such as data breaches, ransomware attacks, and phishing scams pose significant risks to organizations that rely on SaaS solutions.

Key Aspects of SaaS Cyber Security

Effective SaaS cyber security involves implementing various measures to mitigate risks and prevent unauthorized access to data. Some key aspects include:

  • Data Encryption: Encrypting data both in transit and at rest helps protect information from being intercepted or compromised.
  • Multi-Factor Authentication: Implementing multi-factor authentication adds an extra layer of security by requiring users to provide multiple forms of verification.
  • Regular Security Audits: Conducting regular security audits helps identify vulnerabilities and ensure compliance with industry standards.
  • Employee Training: Educating employees about best practices for data security and how to recognize potential threats can help prevent cyber attacks.
  • Incident Response Plan: Having a well-defined incident response plan in place enables organizations to respond quickly and effectively in the event of a security breach.

The Future of SaaS Cyber Security

As technology continues to evolve, so do cyber threats. It is essential for organizations to stay vigilant and proactive in enhancing their SaaS cyber security posture. By investing in robust security measures and staying informed about emerging threats, businesses can better protect their data and maintain the trust of their customers.


7 Key Advantages of SaaS Cybersecurity: Boosting Protection and Efficiency

  1. Enhanced Data Security
  2. Scalability
  3. Cost-Effective
  4. Automatic Updates
  5. Accessibility
  6. Compliance Assurance
  7. Disaster Recovery


Top 7 Concerns About SaaS Cybersecurity: What You Need to Know

  1. Dependency on Service Provider
  2. Data Privacy Concerns
  3. Limited Control
  4. Internet Connectivity Dependency
  5. Shared Resources
  6. Vendor Lock-in
  7. Security Incidents Impact Multiple Users

Enhanced Data Security

Enhanced data security is a significant advantage of SaaS cyber security measures. By implementing robust security protocols, SaaS applications ensure that sensitive data is safeguarded against unauthorized access. This protection is crucial in today’s digital landscape, where data breaches and cyber attacks are prevalent threats. With SaaS cyber security in place, organizations can have peace of mind knowing that their valuable information is well-protected, maintaining the trust of their customers and stakeholders.

Scalability

Scalability is a significant advantage of SaaS cyber security, allowing businesses to adapt and expand their security measures seamlessly as they grow and evolve. With SaaS solutions, organizations can easily adjust their security protocols to accommodate increased data volumes, user access levels, and changing business needs. This flexibility ensures that businesses can maintain a strong and effective security posture throughout their growth journey without significant disruptions or delays.

Cost-Effective

Implementing SaaS cyber security is a cost-effective solution that offers significant savings compared to establishing and managing in-house security infrastructure. By leveraging SaaS services, businesses can benefit from advanced security measures without the hefty upfront costs associated with building and maintaining their own security systems. This cost-efficient approach allows organizations to allocate resources more efficiently, focusing on core business activities while ensuring robust protection against cyber threats.

Automatic Updates

SaaS providers offer a significant advantage in terms of cyber security through automatic updates. By consistently updating their security features to address new threats and vulnerabilities, SaaS providers ensure that their clients’ data remains protected against evolving cyber risks. This proactive approach to security maintenance not only saves businesses time and resources but also enhances their overall resilience to potential cyber attacks. Automatic updates play a crucial role in keeping SaaS applications secure and up-to-date, providing peace of mind to users knowing that they are always equipped with the latest defense mechanisms against emerging threats.

Accessibility

The accessibility aspect of SaaS cyber security offers users the convenience of accessing secure applications from any location with an internet connection. This flexibility allows users to work remotely, collaborate seamlessly, and stay productive without being tied to a specific physical location. By enabling users to access software and data securely from anywhere, SaaS enhances efficiency and agility within organizations while maintaining robust security measures to protect sensitive information.

Compliance Assurance

Compliance assurance is a significant advantage of SaaS cyber security as many SaaS providers diligently adhere to industry regulations and standards. By following established guidelines, SaaS providers help businesses ensure compliance with data protection laws and other regulatory requirements. This proactive approach not only helps organizations avoid costly penalties but also instills trust among customers and stakeholders, demonstrating a commitment to safeguarding sensitive information and maintaining high standards of security.

Disaster Recovery

SaaS solutions offer a valuable pro in the form of disaster recovery capabilities. These platforms typically come equipped with robust backup and recovery features that play a critical role in safeguarding data during emergencies or unforeseen events. By leveraging these built-in tools, businesses can ensure that their information remains secure and accessible even in the face of disasters, helping them maintain continuity and minimize potential disruptions to their operations.

Dependency on Service Provider

Organizations face a significant con of SaaS cyber security in the form of dependency on the service provider for security measures. This reliance introduces a potential risk, especially when the provider’s security practices are insufficient or inadequate. In such cases, organizations may find themselves vulnerable to cyber threats and data breaches that could have been prevented with more robust security protocols in place. The lack of control over the security practices of the SaaS provider underscores the importance for organizations to thoroughly vet and assess the security capabilities of their service providers to mitigate this inherent risk.

Data Privacy Concerns

Storing sensitive data in the cloud raises significant data privacy concerns for organizations utilizing SaaS solutions. The potential risk of unauthorized access to confidential information stored in the cloud poses a threat to data privacy and can lead to compliance issues with regulations such as GDPR and HIPAA. Ensuring that data is securely handled and protected from cyber threats is crucial to maintaining trust with customers and meeting regulatory requirements in an increasingly data-sensitive environment. Organizations must address these data privacy concerns proactively by implementing robust security measures and encryption protocols to safeguard sensitive information stored in the cloud.

Limited Control

Organizations utilizing Software as a Service (SaaS) solutions may encounter the con of limited control over the security protocols and infrastructure provided by the SaaS provider. This lack of control can pose challenges for organizations that have specific security requirements or compliance standards to meet. Without the ability to directly manage or customize security measures, businesses may feel vulnerable to potential risks and find it difficult to address security concerns that are not within their control. It is crucial for organizations to carefully assess and negotiate security agreements with SaaS providers to ensure that their data remains protected and compliant with industry regulations.

Internet Connectivity Dependency

Access to SaaS applications is crucial for modern businesses, but one significant con of SaaS cyber security is the dependency on internet connectivity. Organizations relying on SaaS solutions are vulnerable to disruptions caused by internet outages or connectivity issues. Any interruption in internet access can hinder productivity and impact business operations, highlighting the importance of having contingency plans in place to mitigate the risks associated with this dependency.

Shared Resources

In SaaS environments, one significant con of cyber security is the concept of shared resources due to multi-tenancy. When resources are shared among multiple users, there is a higher risk of data exposure. This shared infrastructure can create vulnerabilities that may be exploited by malicious actors, leading to potential breaches and unauthorized access to sensitive information. Organizations must carefully assess and manage the risks associated with shared resources in SaaS environments to ensure the protection of their data and maintain a secure operating environment.

Vendor Lock-in

Vendor lock-in is a significant con of SaaS cyber security, as it can restrict businesses from easily switching between providers. This limitation not only hinders flexibility but also poses potential security risks when considering a change in SaaS vendors. Organizations may find themselves locked into a specific provider’s ecosystem, making it challenging to migrate data and applications to a different platform without encountering compatibility issues or data security vulnerabilities. The lack of portability and interoperability in SaaS solutions due to vendor lock-in can impede businesses from adapting to evolving security needs and exploring alternative options for better cyber security measures.

Security Incidents Impact Multiple Users

A significant drawback of SaaS cyber security is that security incidents have the potential to impact multiple users at once. When a security breach occurs in a SaaS application, the repercussions can be widespread, affecting numerous users simultaneously. This amplifies the consequences for organizations, as the compromised data or system vulnerability may have far-reaching effects on business operations and data integrity. The interconnected nature of SaaS platforms means that a single breach can have a cascading impact, underscoring the importance of robust security measures to protect both individual users and the organization as a whole.