
cfchris.com

Loading

cyber services

Cyber Services: Protecting Your Business in a Connected World

Cyber Services: Protecting Your Business in a Connected World

Businesses rely on digital tools to communicate, serve customers, store information, and manage daily operations. That connectivity creates opportunity—but it also brings risks. Cyber services help organizations protect their systems, data, and people from online threats while preparing them to respond when problems occur.

What Are Cyber Services?

Cyber services are professional services designed to strengthen an organization’s cybersecurity. Depending on a business’s needs, they may include assessing security risks, monitoring networks, protecting accounts and devices, training employees, and responding to cyber incidents.

Cybersecurity is not a one-time project. Technology, business needs, and threats change over time, so effective protection requires ongoing attention and regular improvements.

Common Types of Cyber Services

Security Assessments

A security assessment reviews an organization’s systems, policies, and practices to identify weaknesses. The results can help prioritize improvements, such as updating software, tightening access controls, or creating stronger data-handling procedures.

Network and Endpoint Protection

Networks, computers, mobile devices, and servers can all be targets. Cyber services may help configure firewalls, endpoint protection, secure remote access, and other safeguards to reduce the chance that an attacker can enter or move through a system.

Identity and Access Management

Access controls help ensure that people can use only the information and systems required for their roles. Services in this area may include multi-factor authentication, account reviews, and policies for creating, changing, and removing user access.

Security Monitoring

Monitoring can help detect unusual activity, such as unexpected login attempts or suspicious changes to a system. Depending on the service, alerts may be reviewed around the clock or during specified business hours. Clear monitoring and escalation procedures help organizations respond more quickly to potential issues.

Employee Security Training

Employees play an important role in protecting an organization. Practical training can help them recognize phishing messages, use passwords safely, handle sensitive information, and report suspicious activity. Regular reminders and realistic examples can make security practices easier to apply in daily work.

Incident Response and Recovery

Even organizations with strong protections can experience a security incident. Incident response services help establish what to do, who should be involved, and how to contain and investigate an event. Recovery planning can also address backups, restoration procedures, and communication with affected parties.

Why Cyber Services Matter

A cyber incident can interrupt operations, expose private information, damage trust, and create unexpected costs. Cyber services can help reduce these risks by identifying vulnerabilities, improving defenses, and preparing teams to act. They can also support organizations that need to meet contractual, regulatory, or industry-specific security requirements.

No service can guarantee that an organization will never experience an attack. The goal is to make systems harder to compromise, detect problems sooner, and limit the impact if an incident occurs.

Choosing the Right Cyber Services

The right approach depends on an organization’s size, technology, data, budget, and risk tolerance. Before choosing a provider, consider:

  • Which systems and information need the most protection?
  • What security work is already handled internally?
  • How quickly will the provider respond to alerts or incidents?
  • What services are included, and what may cost extra?
  • How will progress and recommendations be reported?
  • Does the provider have experience with organizations of a similar size or type?

Ask for clear explanations of service scope, responsibilities, response times, and data handling. A useful provider should be able to explain risks and recommendations in plain language, not just provide technical reports.

Building a Stronger Security Program

Cyber services work best as part of a broader security program. Organizations can support that work by keeping software updated, using multi-factor authentication, limiting access to sensitive systems, maintaining reliable backups, and giving employees a clear way to report concerns. Regular reviews help ensure that protections keep pace with changes in the business.

With a thoughtful plan and the right expertise, cyber services can help an organization protect its operations, respond with confidence, and make informed decisions about technology and risk.


8 Essential Tips for Enhancing Your Cybersecurity Services

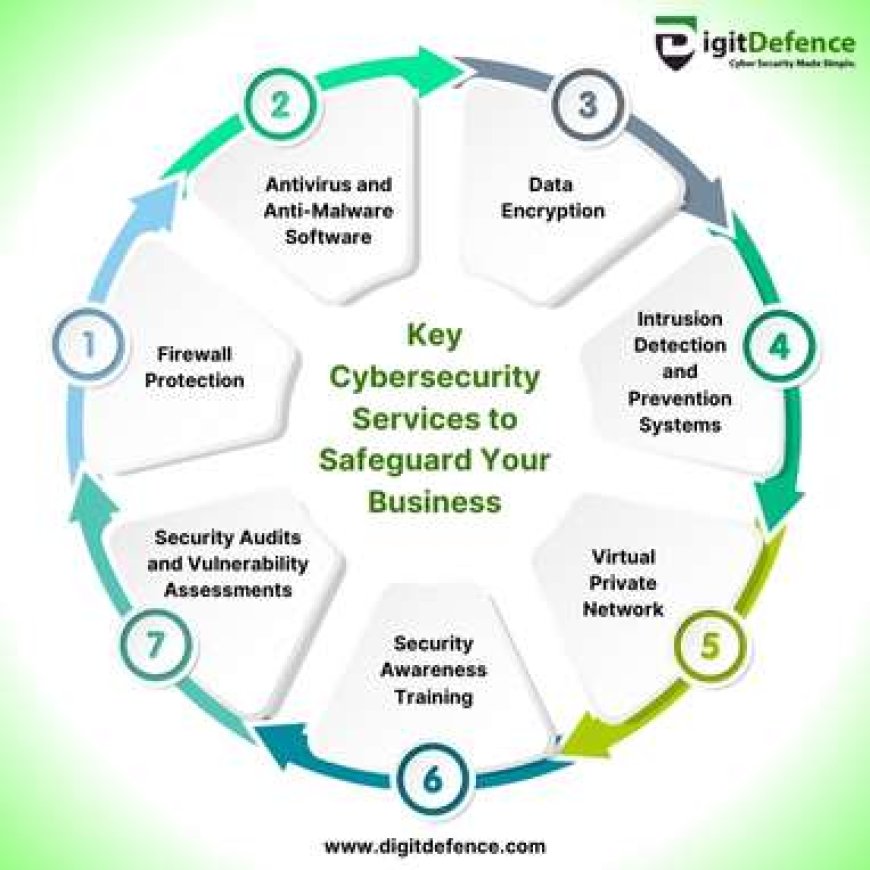
  1. Choose a trusted cybersecurity provider.
  2. Enable multifactor authentication.
  3. Keep software and services updated.
  4. Use strong, unique passwords.
  5. Back up important data regularly.
  6. Train staff to spot phishing.
  7. Review access permissions often.
  8. Check incident response plans regularly.

Choose a trusted cybersecurity provider.

Choosing a trusted cybersecurity provider is an important step in protecting your business. Look for a provider with relevant experience, clear service offerings, strong references, and a straightforward approach to explaining risks and recommendations. Before signing an agreement, ask about response times, data handling, and exactly what the services include. A reliable provider will take time to understand your needs and help you make informed security decisions.

Enable multifactor authentication.

Enable multifactor authentication (MFA) on your email, financial, cloud, and other important accounts. MFA requires a second form of verification—such as an authenticator app, security key, or one-time code—in addition to your password. This extra step can help prevent unauthorized access even if a password is stolen. For stronger protection, use an authenticator app or security key when available, and never share verification codes with anyone.

Keep software and services updated.

Keeping software and services updated is one of the simplest ways to strengthen cybersecurity. Updates often fix known security vulnerabilities that attackers could exploit, as well as improve reliability and performance. Turn on automatic updates when practical, and regularly check that operating systems, applications, plug-ins, and cloud services are current. For business-critical systems, plan updates carefully and verify that backups and recovery procedures are in place before making major changes.

Use strong, unique passwords.

Use strong, unique passwords for every account to make it harder for attackers to access your systems and sensitive information. A long passphrase made from several unrelated words can be easier to remember and tougher to guess than a short, complicated password. Avoid reusing passwords across work and personal accounts, and consider using a reputable password manager to create and store them securely. Enable multi-factor authentication whenever it’s available for an extra layer of protection.

Back up important data regularly.

Back up important data regularly to reduce the risk of losing files to hardware failure, accidental deletion, ransomware, or other disruptions. Use a reliable backup solution, keep copies separate from your main devices or network, and protect them with strong access controls. Test your backups periodically to make sure the data can be restored when you need it.

Train staff to spot phishing.

Train staff to spot phishing by teaching them to recognize common warning signs, such as unexpected attachments, urgent requests, unfamiliar sender addresses, and links that don’t match the message. Encourage employees to verify unusual requests through a separate trusted channel and report suspicious messages promptly. Regular, practical training helps make careful email habits part of everyday work and can reduce the risk of stolen credentials, malware, and data breaches.

Review access permissions often.

Review access permissions often to make sure employees and contractors can reach only the systems and information they need for their roles. Remove access promptly when someone changes jobs or leaves the organization, and disable unused accounts to reduce opportunities for unauthorized entry. Regular permission reviews can help catch outdated or excessive access before it becomes a security risk.

Check incident response plans regularly.

Check your incident response plans regularly to make sure they reflect your current systems, team members, and business needs. Review contact lists, roles, escalation steps, and recovery procedures, and update them whenever something changes. Practicing the plan with realistic scenarios can reveal gaps before an actual incident occurs, helping your team respond faster and reduce disruption.
Network Security Best Practices: Essential Steps to Protect Your Network

Network Security Best Practices

A secure network helps protect sensitive information, keep systems available, and reduce the risk of costly disruptions. Whether you manage a home network, a small business, or a large organization, network security works best as an ongoing process—not a one-time setup. The practices below can help you strengthen your defenses and respond more effectively to threats.

Keep Systems and Network Devices Updated

Install security updates for operating systems, applications, routers, firewalls, and other network equipment as soon as practical. Updates often fix vulnerabilities that attackers could otherwise exploit. Replace devices that no longer receive security support, and remove software or services that are no longer needed.

Where possible, enable automatic updates for routine security fixes. For business environments, test important updates before broad deployment and maintain a schedule for reviewing devices that may have been missed.

Use Strong Authentication

Change default usernames and passwords on routers, access points, and other equipment. Use long, unique passwords for every account, ideally stored in a reputable password manager. Avoid shared accounts when individual accounts are available, since personal accounts make it easier to track activity and revoke access when someone leaves.

Enable multifactor authentication (MFA) for administrative accounts, remote access, cloud services, and other important systems. MFA adds another verification step, making a stolen password less useful to an attacker.

Limit Access and Apply Least Privilege

Give users and devices only the access they need to do their work. Separate everyday user accounts from administrator accounts, and use elevated privileges only when necessary. Review permissions regularly, especially after job changes or departures.

Disable unused accounts, open ports, network services, and remote-access tools. Restrict administrative interfaces so they are reachable only from approved devices or trusted network locations.

Segment the Network

Network segmentation divides a network into smaller sections, limiting how far an intruder can move if one device or account is compromised. For example, organizations can separate employee computers, servers, guest Wi-Fi, and internet-connected devices such as cameras or printers.

Use firewall rules to control which sections can communicate and allow only the connections required for normal operations. Review these rules periodically to remove outdated or overly broad access.

Secure Wi-Fi and Remote Connections

Protect wireless networks with current encryption and a strong, unique passphrase. Change the access point’s default administrator credentials, keep its firmware updated, and use a separate guest network for visitors and personal devices. Avoid exposing the network’s administrative interface to the public internet.

For remote work, require secure connections through an approved VPN or other protected access method. Combine remote access with MFA, limit who can use it, and monitor for unusual sign-in activity. Do not rely on a VPN alone; remote devices should also be updated and protected.

Deploy Firewalls and Endpoint Protection

Firewalls help control traffic entering and leaving a network. Configure them to deny unnecessary connections by default, then allow only the traffic required for business or personal use. Check firewall logs and rules for unexpected changes or suspicious activity.

Install reputable endpoint protection on computers and servers, and keep it enabled and updated. Endpoint tools can help detect malicious files, suspicious behavior, and other threats that network controls may not catch.

Protect Data and Backups

Encrypt sensitive data when it is stored and when it travels across networks. Use secure protocols and avoid sending confidential information over untrusted connections without appropriate protection.

Maintain regular backups of important data and systems. Keep at least one backup isolated from the main network so malware or an intruder cannot easily alter or delete every copy. Test restores periodically; a backup is useful only if it can be recovered.

Monitor Activity and Prepare to Respond

Collect and review logs from firewalls, servers, endpoints, and important applications. Alerts can help identify unusual login attempts, unexpected data transfers, or changes to critical settings. Make sure logs are protected from unauthorized changes and retained long enough to support investigations.

Create an incident response plan that explains who to contact, how to isolate affected systems, how to preserve evidence, and how to restore operations. Practice the plan so that people know what to do under pressure.

Train Users and Review Security Regularly

People play an important role in network security. Teach users how to recognize phishing attempts, report suspicious messages, handle sensitive information, and use approved tools. Make reporting easy and respond constructively so potential problems are raised quickly.

Regularly review network diagrams, device inventories, access permissions, firewall rules, and security policies. Periodic vulnerability assessments can help identify weaknesses before they are exploited. Address findings according to their risk and verify that fixes have worked.

Make Security an Ongoing Practice

No single tool can protect every network from every threat. Strong security comes from combining updated systems, careful access controls, segmentation, monitoring, backups, and informed users. Start with the measures that address your most important risks, document your decisions, and revisit them as your network and needs change.


7 Essential Tips for Strengthening Your Network Security

  1. Use strong, unique passwords and enable multifactor authentication.
  2. Keep routers, firewalls, and devices updated.
  3. Use WPA3 or WPA2 encryption for Wi-Fi.
  4. Change default administrator usernames and passwords.
  5. Segment guest and smart-home devices from sensitive systems.
  6. Disable unused ports, services, and remote access.
  7. Monitor network logs and investigate unusual activity.

Use strong, unique passwords and enable multifactor authentication.

Use strong, unique passwords for every network account, especially administrator and remote-access accounts. Long passphrases are easier to remember and harder to guess, while a password manager can help you store them securely without reusing them. Enable multifactor authentication (MFA) wherever possible to add another layer of protection, so a stolen password alone is less likely to grant access.

Keep routers, firewalls, and devices updated.

Keep routers, firewalls, computers, and other connected devices updated with the latest security patches and firmware. Updates often fix vulnerabilities that attackers could exploit, so install them promptly and enable automatic updates when available. Replace devices that no longer receive security support, and remove outdated software or services you no longer use.

Use WPA3 or WPA2 encryption for Wi-Fi.

Use WPA3 encryption to protect your Wi-Fi network whenever your router and devices support it. If WPA3 isn’t available, choose WPA2-AES rather than outdated options such as WEP or WPA. Set a strong, unique Wi-Fi password, change the router’s default administrator credentials, and keep its firmware up to date to help prevent unauthorized access.

Change default administrator usernames and passwords.

Change the default administrator username and password on every router, access point, and network device you manage. Default credentials are often publicly documented, so attackers may try them to gain control of a device and alter its settings, intercept traffic, or access connected systems. Choose a unique, strong password for each device, change the administrator username if the device allows it, and store the credentials securely in a password manager.

Segment guest and smart-home devices from sensitive systems.

Place guest devices and smart-home equipment—such as TVs, cameras, and speakers—on a separate Wi-Fi network from computers, phones, and other systems that contain sensitive information. These devices may have weaker security or receive fewer updates, so separating them helps limit access if one is compromised. Use your router’s guest-network or network-segmentation feature, and allow only the connections each device needs.

Disable unused ports, services, and remote access.

Disable unused network ports, services, and remote-access tools to reduce the number of ways an attacker could reach your systems. Turn off features you don’t need, close unnecessary firewall ports, and limit administrative access to trusted devices or locations. Review these settings regularly, since old services and access rules can remain enabled long after they’re needed.

Monitor network logs and investigate unusual activity.

Monitor network logs regularly to spot unusual activity, such as repeated failed sign-in attempts, unexpected connections, or large transfers of data. Set alerts for suspicious patterns and investigate them promptly to determine whether they’re harmless or signs of a security issue. Keeping logs protected and retaining them long enough can also help identify what happened and support a faster response.

siem cyber

SIEM Cybersecurity: A Guide to Security Information and Event Management

SIEM in Cybersecurity: How Security Information and Event Management Works

Cyberattacks can leave clues across an organization’s computers, applications, networks, and cloud services. The challenge is finding those clues quickly and understanding whether they point to a real threat. Security information and event management (SIEM) helps by bringing security data together, analyzing it, and alerting teams to suspicious activity.

What Is SIEM?

SIEM, pronounced “sim,” is a cybersecurity technology that collects and analyzes security-related data from across an organization’s IT environment. It can gather logs and events from sources such as servers, endpoints, firewalls, identity systems, applications, and cloud platforms.

By reviewing this information in one place, security teams can spot patterns that might be difficult to see in separate systems. For example, an unusual login may look harmless on its own. When correlated with repeated failed attempts and unexpected access to sensitive files, it may signal a compromised account.

How Does SIEM Work?

Most SIEM solutions support several core activities:

  1. Data collection: The system receives logs and security events from connected sources.
  2. Normalization: It organizes data from different tools into a consistent format so events can be compared.
  3. Correlation and analysis: Rules, analytics, and sometimes machine learning identify relationships or unusual behavior across events.
  4. Alerting: When activity matches a detection rule or risk pattern, the SIEM creates an alert for investigation.
  5. Investigation and reporting: Analysts use search tools, dashboards, and timelines to examine activity and document findings.

SIEM systems can also retain event data for a set period, helping teams investigate incidents and meet applicable audit or compliance requirements. Retention capabilities and requirements vary by product and organization.

Why SIEM Matters for Cybersecurity

A SIEM can help security teams gain a broader view of activity across their environment. Its value often includes:

  • Centralized visibility: Security events from multiple systems can be reviewed in one place.
  • Threat detection: Correlation can reveal suspicious combinations of events that individual tools may not identify together.
  • Faster investigations: Searchable logs and event timelines can help analysts understand what happened and when.
  • Incident response support: Alerts and investigative context can help teams decide what actions to take.
  • Audit and compliance support: Reports and retained logs may help organizations demonstrate how security events are monitored and reviewed.

A SIEM is not a substitute for a complete security program. It works best alongside sound security practices, capable staff, clear response procedures, and effective controls such as multifactor authentication and endpoint protection.

Common SIEM Use Cases

Organizations use SIEM tools to monitor for a range of security concerns, including:

  • Repeated or unusual login attempts
  • Unexpected access to sensitive information
  • Suspicious changes to user accounts or permissions
  • Malware alerts and unusual endpoint behavior
  • Potential data exfiltration or unusual network traffic
  • Activity involving accounts, devices, or locations that differ from normal patterns

These detections depend on which data sources are connected and how the system is configured. A SIEM cannot reliably identify activity it cannot observe, and alerts require appropriate review.

SIEM Challenges to Consider

SIEM can strengthen security monitoring, but it also requires thoughtful implementation and ongoing maintenance. Common challenges include:

  • Alert fatigue: Too many low-value alerts can make it harder to prioritize genuine risks.
  • Incomplete data: Missing or poorly configured data sources can create gaps in visibility.
  • Complex setup: Detection rules and integrations often need to be tailored to an organization’s systems and risks.
  • Storage and cost: Collecting and retaining large volumes of logs can affect licensing, infrastructure, and operational costs.
  • Staffing and expertise: Analysts need time and training to investigate alerts and improve detection quality.

Organizations can address these challenges by prioritizing important data sources, tuning detection rules, setting clear alert-handling procedures, and regularly reviewing whether the SIEM is producing useful results.

SIEM and Related Security Technologies

SIEM is often used alongside other security tools. A security orchestration, automation, and response (SOAR) platform can help coordinate or automate parts of incident response. Extended detection and response (XDR) tools focus on detecting and responding to threats across connected security products. Some modern security platforms combine capabilities from several categories, but features and terminology differ among vendors.

How to Get Started with SIEM

Before choosing or deploying a SIEM, an organization should define what it needs to monitor and why. A practical starting point includes:

  1. Identify critical systems, sensitive data, and key security risks.
  2. Select the log sources that provide meaningful visibility into those risks.
  3. Establish detection priorities and define who will review alerts.
  4. Set retention, access, and privacy requirements for collected data.
  5. Test alerts and response procedures, then adjust rules based on real results.
  6. Measure performance using relevant indicators, such as investigation time and the proportion of actionable alerts.

The Role of SIEM in a Strong Security Program

SIEM helps organizations turn activity from many systems into information that security teams can investigate. Its effectiveness depends on the quality of the data it receives, the relevance of its detections, and the organization’s ability to respond.

With clear goals, reliable integrations, and ongoing tuning, SIEM can become an important part of cybersecurity monitoring. It gives teams a more connected view of potential threats—and a stronger foundation for investigating suspicious activity.


Understanding SIEM in Cybersecurity: Key FAQs Answered

  1. What is SIEM in cybersecurity?
  2. How does a SIEM system work?
  3. What are the main benefits of using SIEM?
  4. What types of security events can SIEM detect?
  5. What is the difference between SIEM, SOAR, and XDR?
  6. How much does SIEM cost, and what affects the price?

What is SIEM in cybersecurity?

SIEM, or security information and event management, is a cybersecurity technology that collects and analyzes log and event data from systems such as networks, servers, applications, and cloud services. By bringing this information together, SIEM helps security teams identify suspicious patterns, investigate potential threats, and respond to incidents. Its effectiveness depends on having useful data sources, well-tuned alerts, and a team or process to review and act on findings.

How does a SIEM system work?

A SIEM system works by collecting security logs and events from sources such as computers, applications, firewalls, and cloud services, then organizing and analyzing that data in one place. It looks for suspicious patterns by comparing events against detection rules and expected behavior. When it identifies activity that may indicate a threat, it generates an alert so security teams can investigate, respond, and review related events.

What are the main benefits of using SIEM?

The main benefits of using SIEM (security information and event management) include centralized visibility into security activity, faster detection of suspicious behavior, and more efficient incident investigations. By collecting and correlating data from systems such as networks, servers, endpoints, and cloud services, SIEM can help security teams identify patterns they might otherwise miss. It can also support incident response, provide searchable records for audits, and help organizations meet certain compliance requirements. Its effectiveness depends on collecting the right data, tuning alerts, and having people and processes in place to respond.

What types of security events can SIEM detect?

A SIEM can detect a wide range of security events by analyzing logs and activity from systems such as networks, endpoints, applications, identity platforms, and cloud services. Depending on the data sources and detection rules in place, it may flag repeated failed logins, unusual access to accounts or sensitive files, unexpected changes to permissions, malware alerts, suspicious network traffic, and signs of possible data exfiltration. SIEM can also connect events across different systems—for example, linking an unusual login to later access to critical data—to help security teams investigate potential threats. Detection coverage depends on how the SIEM is configured and the quality of the data it receives.

What is the difference between SIEM, SOAR, and XDR?

SIEM, SOAR, and XDR support cybersecurity in different ways. A SIEM collects and analyzes security data from across an organization to identify suspicious activity and generate alerts. SOAR helps teams coordinate and automate parts of their response, such as assigning incidents or running approved investigation steps. XDR detects and responds to threats across connected security layers, such as endpoints, email, and cloud services, often bringing related activity together for investigation. These tools can complement one another, but their capabilities vary by product.

How much does SIEM cost, and what affects the price?

SIEM costs vary widely, from a few hundred dollars per month for a small or managed service to much higher amounts for large, complex deployments. Pricing may be based on daily data volume, the number of monitored devices or users, data retention, and included features. Costs can also include setup, integrations, cloud storage, staff training, ongoing tuning, and analyst support. To compare options, estimate the log data you need to collect, identify essential capabilities, and ask vendors to clarify any usage limits or add-on fees.

cybersecurity as a service

Cybersecurity as a Service: A Practical Guide for Businesses

Cybersecurity as a Service: A Practical Guide for Businesses

Cybersecurity is no longer a one-time project. Threats change constantly, software needs regular updates, and even well-prepared organizations can face new risks. For many businesses, keeping up requires more time and specialized expertise than an in-house team can provide. Cybersecurity as a Service (CSaaS) offers another approach: access to ongoing security tools and expertise through an external provider.

What Is Cybersecurity as a Service?

Cybersecurity as a Service is a model in which an organization relies on a third-party provider for some or all of its security operations. Services are typically delivered on an ongoing basis and may be tailored to the organization’s size, systems, risk profile, and regulatory requirements.

Depending on the provider and service plan, CSaaS may include security monitoring, threat detection, vulnerability assessments, incident response support, employee training, and help with security policies. Some providers focus on a specific area, while others offer a broader managed security program.

Common Cybersecurity as a Service Offerings

  • Security monitoring: Reviewing activity across networks, devices, cloud environments, and applications to identify suspicious behavior.
  • Managed detection and response: Investigating potential threats and helping contain or remediate them. The exact level of response varies by provider and contract.
  • Vulnerability management: Identifying weaknesses in systems and helping prioritize fixes based on risk.
  • Endpoint protection: Managing security for computers, mobile devices, and servers.
  • Cloud security: Helping protect cloud accounts, workloads, data, and configurations.
  • Identity and access management: Supporting controls such as multifactor authentication, role-based access, and account reviews.
  • Security awareness training: Teaching employees how to recognize phishing, handle sensitive information, and report concerns.
  • Incident response planning: Preparing procedures and providing support when a security event occurs.

Why Businesses Choose CSaaS

Access to specialized expertise: Security providers may bring experience across different technologies and threat scenarios. This can be valuable for organizations that do not have a dedicated security team.

Ongoing coverage: Security risks do not follow business hours. Some services provide continuous monitoring or on-call support, depending on the agreement.

Predictable costs: A subscription or managed-services arrangement can make security spending easier to plan than building every capability internally. Costs and included services vary, so it is important to review the full scope.

Room to scale: Services can often be adjusted as an organization adds employees, locations, applications, or cloud systems.

More focus on core work: By delegating selected security tasks, internal staff may have more time for other business priorities. Outsourcing does not remove the organization’s responsibility for managing risk, however.

What CSaaS Does Not Do

Cybersecurity as a Service is not a guarantee that an organization will never experience a breach. No provider can eliminate every risk, and technology alone cannot prevent every incident. Effective security still depends on clear policies, reliable backups, timely software updates, appropriate access controls, and informed employees.

Responsibility is also shared. The provider may operate specific tools or monitor defined systems, while the customer remains responsible for decisions such as approving access, protecting business data, and following applicable legal or regulatory requirements. Those boundaries should be documented before service begins.

How to Choose a Provider

Start by identifying the problems the service needs to solve. A business seeking help with after-hours monitoring may need a different arrangement from one preparing for a compliance review or improving cloud security.

  • Define the scope: Confirm which systems, locations, users, and data are covered—and which are not.
  • Understand response procedures: Ask who investigates alerts, who can take action, how quickly the provider responds, and when the business will be contacted.
  • Review service levels: Look for clear commitments about availability, response times, reporting, and escalation. Check how those commitments are measured.
  • Ask about data handling: Understand what information the provider collects, where it is stored, who can access it, and how it is protected.
  • Check experience and references: Look for experience with organizations of a similar size, industry, and technology environment.
  • Clarify responsibilities: Establish who manages software updates, account permissions, investigations, backups, and incident communications.
  • Plan for continuity: Ask how service handoffs, data access, and security operations will work if the contract ends.

Making the Most of the Service

Before onboarding, create an accurate inventory of devices, applications, cloud services, and important data. Share existing policies and known risks with the provider, and identify internal contacts who can make decisions during an incident. Regularly review reports and hold meetings to discuss unresolved issues, changing business needs, and recommended improvements.

It is also important to test the relationship before an emergency. Tabletop exercises and incident-response drills can reveal unclear responsibilities and communication gaps while there is still time to address them.

Conclusion

Cybersecurity as a Service can help businesses access security expertise and ongoing support without building every capability in-house. The value depends on choosing services that match actual risks, defining responsibilities clearly, and staying actively involved. With a well-scoped agreement and sound internal practices, CSaaS can become a practical part of a broader cybersecurity program.


Top 5 Advantages of Cybersecurity as a Service for Your Business

  1. Access to specialized security expertise
  2. Continuous threat monitoring
  3. Predictable subscription costs
  4. Scales with business needs
  5. Frees staff to focus on core work


7 Potential Drawbacks of Cybersecurity as a Service: Costs, Control, and More

  1. Ongoing subscription costs can add up.
  2. Less direct control over security operations.
  3. Service quality varies between providers.
  4. Sensitive data may be shared with a vendor.
  5. Response times may depend on the service agreement.
  6. Integrating tools can be complex.
  7. Outsourcing does not eliminate business risk.

Access to specialized security expertise

Cybersecurity as a Service gives businesses access to specialized security expertise without requiring them to hire and maintain a large in-house team. Providers bring experience with evolving threats, security tools, and industry practices, helping organizations identify risks, strengthen defenses, and respond to potential incidents. This expertise can be especially valuable for small and midsize businesses that need knowledgeable support but may not have the resources to build a dedicated security department.

Continuous threat monitoring

Continuous threat monitoring helps organizations spot suspicious activity as it happens, rather than discovering it after significant damage has occurred. A cybersecurity provider can monitor networks, devices, and cloud systems around the clock, investigate alerts, and notify the right people when action is needed. This ongoing visibility can help businesses respond to emerging threats more quickly, even when their internal team is unavailable.

Predictable subscription costs

Cybersecurity as a Service can make security spending more predictable through a regular subscription fee. Instead of making large upfront investments in tools, hiring, and ongoing maintenance, businesses can budget for an agreed set of services each month or year. Costs depend on the provider and scope, so reviewing what’s included—and what may incur extra charges—helps avoid surprises.

Scales with business needs

Cybersecurity as a Service can scale as your business changes. You can adjust coverage as you add employees, open new locations, adopt cloud tools, or face new security requirements—without having to build an entirely new in-house security team. This flexibility helps keep protection aligned with your needs and budget as your organization grows.

Frees staff to focus on core work

Cybersecurity as a Service can free employees from time-consuming security tasks, such as monitoring alerts, managing tools, and tracking routine updates. With a specialized provider handling agreed-upon responsibilities, your team can spend more time on the work that directly supports your business goals. Outsourcing security does not eliminate the need for internal oversight, but it can help staff focus their attention where it matters most.

Ongoing subscription costs can add up.

Ongoing subscription costs for cybersecurity as a service can add up over time, especially as a business grows or adds more users, devices, and security features. What starts as a manageable monthly expense may become a significant part of the IT budget, so it’s important to review pricing, renewal terms, and potential add-on fees regularly. Compare the total long-term cost with the value and coverage provided to make sure the service continues to fit your needs.

Less direct control over security operations.

One potential drawback of cybersecurity as a service is having less direct control over day-to-day security operations. When an outside provider manages monitoring, tools, or incident response, your team may have limited visibility into how decisions are made or how quickly actions are taken. This can create challenges if the provider’s procedures do not align with your business priorities. To reduce the risk, define responsibilities, approval requirements, reporting expectations, and escalation procedures clearly in the service agreement.

Service quality varies between providers.

Service quality can vary significantly between cybersecurity providers, making it difficult to know what level of protection you’ll receive. Providers may differ in their expertise, monitoring capabilities, response times, communication, and the tools they use. A service that sounds comprehensive may also have important limits in its contract. Before choosing a provider, review exactly what’s included, ask how incidents are handled, and check references to ensure the service meets your organization’s needs.

Sensitive data may be shared with a vendor.

One potential drawback of cybersecurity as a service is that protecting your systems may require sharing sensitive data with an outside vendor. Depending on the service, the provider could access security logs, user information, system configurations, or other confidential details. This creates additional privacy and data-protection risks, especially if the vendor’s controls or practices are inadequate. Before signing an agreement, review what data will be collected, how it will be stored and protected, who can access it, and whether it will be shared with subcontractors.

Response times may depend on the service agreement.

Response times for cybersecurity as a service can depend on the terms of the service agreement. A provider may prioritize incidents according to severity, offer different response levels for different plans, or limit support to certain hours. If those details are unclear, a business could wait longer than expected for help during a security incident. Before signing, confirm response-time commitments, after-hours coverage, escalation procedures, and what actions the provider is authorized to take.

Integrating tools can be complex.

Integrating cybersecurity tools can be complex, especially when a provider’s platforms need to work with existing networks, cloud services, and business applications. Compatibility issues, duplicated alerts, or gaps in data sharing can make it harder to get a clear view of security risks. Setup may also require changes to workflows and access controls, so businesses should clarify integration requirements, responsibilities, and ongoing support before adopting a service.

Outsourcing does not eliminate business risk.

Outsourcing cybersecurity can add valuable expertise and support, but it does not eliminate a business’s responsibility for managing risk. The provider can only protect the systems, data, and processes covered by the agreement, and gaps in scope, communication, or internal practices may leave the organization exposed. Businesses still need to make informed security decisions, maintain sound policies, train employees, and understand who is responsible for each task—especially during an incident.