
cfchris.com

Loading

cyber security managed services

Cyber Security Managed Services: A Practical Guide for Businesses

Cybersecurity Managed Services: A Practical Guide for Businesses

Cybersecurity threats can affect organizations of every size. Phishing, ransomware, stolen credentials, and software vulnerabilities can disrupt operations, expose sensitive information, and damage customer trust. Keeping up with these risks takes time and specialized expertise—resources that many businesses do not have in-house. Cybersecurity managed services can help fill that gap.

What Are Cybersecurity Managed Services?

Cybersecurity managed services are ongoing security services provided by an external team. Depending on the provider and the organization’s needs, these services may include monitoring systems, identifying vulnerabilities, responding to incidents, managing security tools, and helping meet regulatory requirements.

Some providers offer a broad security program, while others focus on specific areas such as endpoint protection or cloud security. The goal is to strengthen an organization’s defenses and provide access to security expertise without requiring every capability to be built internally.

Common Services

A managed cybersecurity program may include a combination of the following:

  • 24/7 security monitoring: Reviewing alerts and system activity to help identify suspicious behavior.
  • Threat detection and response: Investigating potential incidents and coordinating actions to contain them.
  • Endpoint security: Protecting computers, servers, and mobile devices from malware and unauthorized access.
  • Vulnerability management: Finding and prioritizing weaknesses in software, systems, and configurations.
  • Security assessments: Evaluating existing controls, processes, and exposure to risk.
  • Identity and access management: Helping ensure users have appropriate access and that authentication controls are in place.
  • Cloud security: Reviewing cloud environments, permissions, and configurations for common security issues.
  • Security awareness training: Helping employees recognize phishing attempts and follow safer practices.
  • Incident response planning: Establishing roles, procedures, and communication plans before an incident occurs.

How Managed Services Can Help

Access to specialized expertise: Security providers can bring experience with current threats, technologies, and response practices. This can be valuable for organizations that do not have a large internal security team.

Consistent monitoring: Threats do not follow business hours. Depending on the service agreement, a provider may monitor systems around the clock and escalate significant alerts when they occur.

More predictable costs: Managed services often use recurring fees, which can make security spending easier to plan than building every capability from scratch. Costs and included services vary, so the contract should be reviewed carefully.

Support for internal teams: A provider can handle routine monitoring or specialized tasks, allowing in-house staff to focus on business priorities. Managed services work best when responsibilities are clearly divided rather than assumed.

Improved readiness: Regular assessments, documented procedures, and testing can help an organization prepare for security incidents and reduce confusion during a response.

Choosing a Managed Security Provider

Not every provider offers the same capabilities. Before selecting one, consider your organization’s systems, risk tolerance, compliance obligations, and internal expertise. Ask prospective providers questions such as:

  • Which services are included, and which cost extra?
  • Who monitors alerts, and what are the response hours?
  • How quickly will critical incidents be escalated?
  • What actions can the provider take without approval?
  • How will the provider protect access to your systems and data?
  • What reports, reviews, and service-level commitments are provided?
  • How does the provider support incident response and recovery?
  • Can the services scale as your organization changes?

Request clear documentation of responsibilities, escalation paths, data handling practices, and service levels. It is also useful to understand how the provider will work with your IT team, leadership, legal counsel, and other vendors during an incident.

Managed Services Do Not Transfer All Responsibility

Hiring a cybersecurity provider does not make an organization automatically secure or remove its responsibility for protecting information. Business leaders still need to set priorities, approve policies, manage user access, maintain backups, and ensure employees understand their role in security. The provider can supply tools and expertise, but effective security requires cooperation between the provider and the organization.

Organizations should also review the provider’s own security practices. A managed security provider may need access to sensitive systems, so its access controls, incident procedures, confidentiality commitments, and handling of customer data matter.

Making the Most of a Managed Security Partnership

Start by identifying critical systems and information, then define the outcomes the service should support. Set measurable expectations, such as reporting frequency, alert escalation procedures, and vulnerability remediation timelines. Review results regularly and update the scope when your technology, risks, or business needs change.

Cybersecurity managed services can help businesses strengthen monitoring, improve incident readiness, and access expertise that may be difficult to maintain internally. With a carefully selected provider, clear responsibilities, and active oversight, they can become a useful part of a broader security program—not a substitute for one.


5 Essential Tips for Choosing and Managing Cybersecurity Services

  1. Define clear security goals and service-level expectations.
  2. Verify the provider’s certifications and incident response plan.
  3. Require regular vulnerability scans and patch management.
  4. Keep access limited with multifactor authentication.
  5. Review reports and test recovery plans regularly.

Define clear security goals and service-level expectations.

Define clear security goals and service-level expectations before choosing a cybersecurity managed services provider. Identify the outcomes that matter most—such as 24/7 monitoring, faster incident response, vulnerability remediation, or compliance support—and agree on measurable targets, reporting schedules, and escalation procedures. Clear expectations help your provider prioritize the right risks, coordinate effectively with your team, and demonstrate whether the service is meeting your needs.

Verify the provider’s certifications and incident response plan.

Before choosing a cybersecurity managed services provider, verify that its certifications are current, relevant to your needs, and held by the people who will work on your account. Ask for details about its incident response plan, including how it detects and escalates threats, who will contact your team, what actions it can take, and how quickly it will respond. A clear, tested plan and qualified staff can help ensure the provider is prepared to support your organization when a security incident occurs.

Require regular vulnerability scans and patch management.

Require your cybersecurity managed services provider to run vulnerability scans on a regular schedule and promptly share findings, priorities, and remediation plans. Scans can uncover outdated software, misconfigurations, and other weaknesses before attackers exploit them. Pair scanning with a clear patch management process that prioritizes critical updates, tests patches when appropriate, and tracks completion across your systems. Regular reporting helps confirm that issues are being addressed and that your security posture keeps pace with emerging risks.

Keep access limited with multifactor authentication.

Limit access to sensitive systems and data by giving each user only the permissions needed for their role, and require multifactor authentication (MFA) wherever possible. MFA adds a verification step—such as an authenticator app prompt or security key—so a stolen password alone is less likely to grant access. A managed security provider can help configure MFA, review access regularly, and remove accounts or permissions that are no longer needed.

Review reports and test recovery plans regularly.

Review cybersecurity reports regularly to understand emerging threats, unresolved vulnerabilities, and whether your managed services are meeting agreed-upon goals. Reports are most useful when they lead to clear actions, owners, and deadlines. Also test recovery plans on a recurring basis—not just on paper—to confirm that backups can be restored, critical systems can be brought back online, and everyone knows their role during an incident. Regular reviews and realistic exercises can reveal gaps early and help your business recover more confidently when disruption occurs.
cybersecurity as a service

Cybersecurity as a Service: A Practical Guide for Businesses

Cybersecurity as a Service: A Practical Guide for Businesses

Cybersecurity is no longer a one-time project. Threats change constantly, software needs regular updates, and even well-prepared organizations can face new risks. For many businesses, keeping up requires more time and specialized expertise than an in-house team can provide. Cybersecurity as a Service (CSaaS) offers another approach: access to ongoing security tools and expertise through an external provider.

What Is Cybersecurity as a Service?

Cybersecurity as a Service is a model in which an organization relies on a third-party provider for some or all of its security operations. Services are typically delivered on an ongoing basis and may be tailored to the organization’s size, systems, risk profile, and regulatory requirements.

Depending on the provider and service plan, CSaaS may include security monitoring, threat detection, vulnerability assessments, incident response support, employee training, and help with security policies. Some providers focus on a specific area, while others offer a broader managed security program.

Common Cybersecurity as a Service Offerings

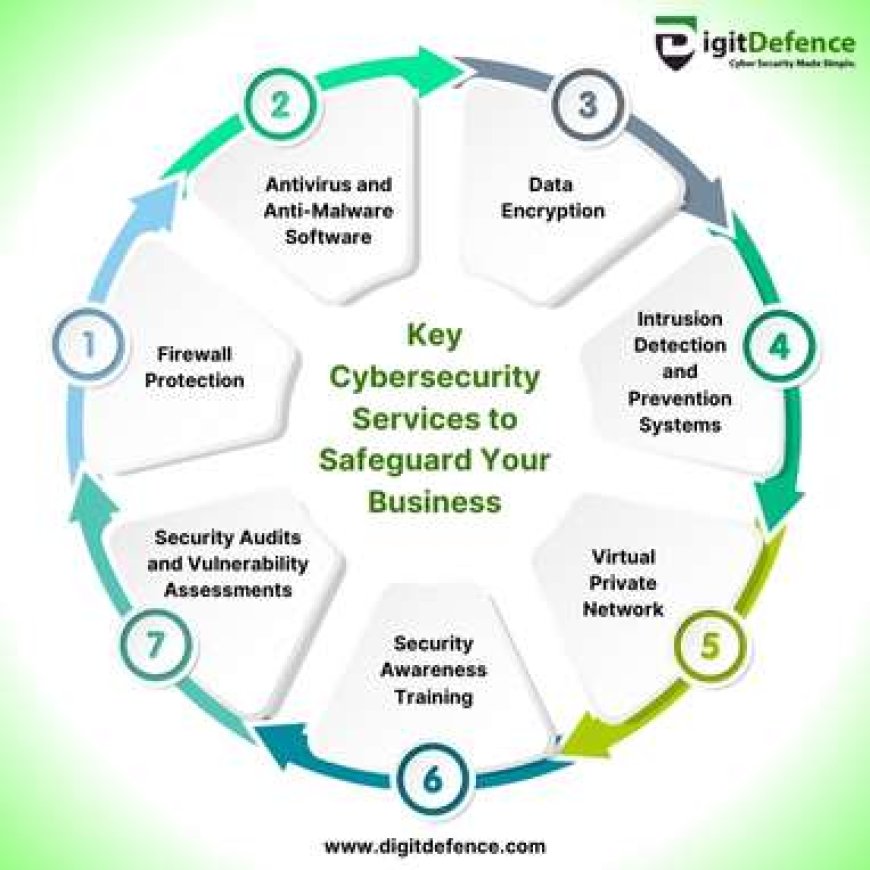
  • Security monitoring: Reviewing activity across networks, devices, cloud environments, and applications to identify suspicious behavior.
  • Managed detection and response: Investigating potential threats and helping contain or remediate them. The exact level of response varies by provider and contract.
  • Vulnerability management: Identifying weaknesses in systems and helping prioritize fixes based on risk.
  • Endpoint protection: Managing security for computers, mobile devices, and servers.
  • Cloud security: Helping protect cloud accounts, workloads, data, and configurations.
  • Identity and access management: Supporting controls such as multifactor authentication, role-based access, and account reviews.
  • Security awareness training: Teaching employees how to recognize phishing, handle sensitive information, and report concerns.
  • Incident response planning: Preparing procedures and providing support when a security event occurs.

Why Businesses Choose CSaaS

Access to specialized expertise: Security providers may bring experience across different technologies and threat scenarios. This can be valuable for organizations that do not have a dedicated security team.

Ongoing coverage: Security risks do not follow business hours. Some services provide continuous monitoring or on-call support, depending on the agreement.

Predictable costs: A subscription or managed-services arrangement can make security spending easier to plan than building every capability internally. Costs and included services vary, so it is important to review the full scope.

Room to scale: Services can often be adjusted as an organization adds employees, locations, applications, or cloud systems.

More focus on core work: By delegating selected security tasks, internal staff may have more time for other business priorities. Outsourcing does not remove the organization’s responsibility for managing risk, however.

What CSaaS Does Not Do

Cybersecurity as a Service is not a guarantee that an organization will never experience a breach. No provider can eliminate every risk, and technology alone cannot prevent every incident. Effective security still depends on clear policies, reliable backups, timely software updates, appropriate access controls, and informed employees.

Responsibility is also shared. The provider may operate specific tools or monitor defined systems, while the customer remains responsible for decisions such as approving access, protecting business data, and following applicable legal or regulatory requirements. Those boundaries should be documented before service begins.

How to Choose a Provider

Start by identifying the problems the service needs to solve. A business seeking help with after-hours monitoring may need a different arrangement from one preparing for a compliance review or improving cloud security.

  • Define the scope: Confirm which systems, locations, users, and data are covered—and which are not.
  • Understand response procedures: Ask who investigates alerts, who can take action, how quickly the provider responds, and when the business will be contacted.
  • Review service levels: Look for clear commitments about availability, response times, reporting, and escalation. Check how those commitments are measured.
  • Ask about data handling: Understand what information the provider collects, where it is stored, who can access it, and how it is protected.
  • Check experience and references: Look for experience with organizations of a similar size, industry, and technology environment.
  • Clarify responsibilities: Establish who manages software updates, account permissions, investigations, backups, and incident communications.
  • Plan for continuity: Ask how service handoffs, data access, and security operations will work if the contract ends.

Making the Most of the Service

Before onboarding, create an accurate inventory of devices, applications, cloud services, and important data. Share existing policies and known risks with the provider, and identify internal contacts who can make decisions during an incident. Regularly review reports and hold meetings to discuss unresolved issues, changing business needs, and recommended improvements.

It is also important to test the relationship before an emergency. Tabletop exercises and incident-response drills can reveal unclear responsibilities and communication gaps while there is still time to address them.

Conclusion

Cybersecurity as a Service can help businesses access security expertise and ongoing support without building every capability in-house. The value depends on choosing services that match actual risks, defining responsibilities clearly, and staying actively involved. With a well-scoped agreement and sound internal practices, CSaaS can become a practical part of a broader cybersecurity program.


Top 5 Advantages of Cybersecurity as a Service for Your Business

  1. Access to specialized security expertise
  2. Continuous threat monitoring
  3. Predictable subscription costs
  4. Scales with business needs
  5. Frees staff to focus on core work


7 Potential Drawbacks of Cybersecurity as a Service: Costs, Control, and More

  1. Ongoing subscription costs can add up.
  2. Less direct control over security operations.
  3. Service quality varies between providers.
  4. Sensitive data may be shared with a vendor.
  5. Response times may depend on the service agreement.
  6. Integrating tools can be complex.
  7. Outsourcing does not eliminate business risk.

Access to specialized security expertise

Cybersecurity as a Service gives businesses access to specialized security expertise without requiring them to hire and maintain a large in-house team. Providers bring experience with evolving threats, security tools, and industry practices, helping organizations identify risks, strengthen defenses, and respond to potential incidents. This expertise can be especially valuable for small and midsize businesses that need knowledgeable support but may not have the resources to build a dedicated security department.

Continuous threat monitoring

Continuous threat monitoring helps organizations spot suspicious activity as it happens, rather than discovering it after significant damage has occurred. A cybersecurity provider can monitor networks, devices, and cloud systems around the clock, investigate alerts, and notify the right people when action is needed. This ongoing visibility can help businesses respond to emerging threats more quickly, even when their internal team is unavailable.

Predictable subscription costs

Cybersecurity as a Service can make security spending more predictable through a regular subscription fee. Instead of making large upfront investments in tools, hiring, and ongoing maintenance, businesses can budget for an agreed set of services each month or year. Costs depend on the provider and scope, so reviewing what’s included—and what may incur extra charges—helps avoid surprises.

Scales with business needs

Cybersecurity as a Service can scale as your business changes. You can adjust coverage as you add employees, open new locations, adopt cloud tools, or face new security requirements—without having to build an entirely new in-house security team. This flexibility helps keep protection aligned with your needs and budget as your organization grows.

Frees staff to focus on core work

Cybersecurity as a Service can free employees from time-consuming security tasks, such as monitoring alerts, managing tools, and tracking routine updates. With a specialized provider handling agreed-upon responsibilities, your team can spend more time on the work that directly supports your business goals. Outsourcing security does not eliminate the need for internal oversight, but it can help staff focus their attention where it matters most.

Ongoing subscription costs can add up.

Ongoing subscription costs for cybersecurity as a service can add up over time, especially as a business grows or adds more users, devices, and security features. What starts as a manageable monthly expense may become a significant part of the IT budget, so it’s important to review pricing, renewal terms, and potential add-on fees regularly. Compare the total long-term cost with the value and coverage provided to make sure the service continues to fit your needs.

Less direct control over security operations.

One potential drawback of cybersecurity as a service is having less direct control over day-to-day security operations. When an outside provider manages monitoring, tools, or incident response, your team may have limited visibility into how decisions are made or how quickly actions are taken. This can create challenges if the provider’s procedures do not align with your business priorities. To reduce the risk, define responsibilities, approval requirements, reporting expectations, and escalation procedures clearly in the service agreement.

Service quality varies between providers.

Service quality can vary significantly between cybersecurity providers, making it difficult to know what level of protection you’ll receive. Providers may differ in their expertise, monitoring capabilities, response times, communication, and the tools they use. A service that sounds comprehensive may also have important limits in its contract. Before choosing a provider, review exactly what’s included, ask how incidents are handled, and check references to ensure the service meets your organization’s needs.

Sensitive data may be shared with a vendor.

One potential drawback of cybersecurity as a service is that protecting your systems may require sharing sensitive data with an outside vendor. Depending on the service, the provider could access security logs, user information, system configurations, or other confidential details. This creates additional privacy and data-protection risks, especially if the vendor’s controls or practices are inadequate. Before signing an agreement, review what data will be collected, how it will be stored and protected, who can access it, and whether it will be shared with subcontractors.

Response times may depend on the service agreement.

Response times for cybersecurity as a service can depend on the terms of the service agreement. A provider may prioritize incidents according to severity, offer different response levels for different plans, or limit support to certain hours. If those details are unclear, a business could wait longer than expected for help during a security incident. Before signing, confirm response-time commitments, after-hours coverage, escalation procedures, and what actions the provider is authorized to take.

Integrating tools can be complex.

Integrating cybersecurity tools can be complex, especially when a provider’s platforms need to work with existing networks, cloud services, and business applications. Compatibility issues, duplicated alerts, or gaps in data sharing can make it harder to get a clear view of security risks. Setup may also require changes to workflows and access controls, so businesses should clarify integration requirements, responsibilities, and ongoing support before adopting a service.

Outsourcing does not eliminate business risk.

Outsourcing cybersecurity can add valuable expertise and support, but it does not eliminate a business’s responsibility for managing risk. The provider can only protect the systems, data, and processes covered by the agreement, and gaps in scope, communication, or internal practices may leave the organization exposed. Businesses still need to make informed security decisions, maintain sound policies, train employees, and understand who is responsible for each task—especially during an incident.