cfchris.com

Loading

strategic it consulting services

Strategic IT Consulting Services: A Practical Guide to Business Growth

Strategic IT Consulting Services: Aligning Technology With Business Goals

Technology can help a business work faster, serve customers better, and adapt to change—but only when it supports the organization’s broader goals. Strategic IT consulting helps businesses make informed technology decisions, prioritize investments, and build a practical plan for the future.

What Are Strategic IT Consulting Services?

Strategic IT consulting services help organizations assess their technology environment and determine how it can better support business objectives. Rather than focusing only on individual tools or technical problems, a strategic consultant considers the full picture: operations, people, processes, risks, budgets, and long-term plans.

Depending on a company’s needs, this work may include evaluating existing systems, developing an IT roadmap, planning cloud adoption, improving cybersecurity, modernizing applications, or advising on technology budgets.

Why Strategic IT Planning Matters

Without a clear plan, technology decisions can become reactive. Businesses may invest in overlapping tools, rely on outdated systems, or struggle to manage security and maintenance. A well-defined IT strategy helps connect technology spending to measurable business priorities.

  • Better investment decisions: Prioritize projects based on business value, cost, and risk.
  • Greater operational efficiency: Identify manual tasks and outdated processes that technology could improve.
  • Reduced risk: Address cybersecurity, compliance, continuity, and vendor concerns more proactively.
  • Improved scalability: Prepare systems and processes to support growth or changing demands.
  • Clearer accountability: Establish priorities, timelines, ownership, and ways to measure progress.

Common Strategic IT Consulting Services

IT Assessments

An assessment reviews an organization’s current systems, infrastructure, applications, processes, and risks. The findings can reveal technical debt, security gaps, unnecessary costs, and opportunities to improve performance.

IT Roadmaps and Planning

An IT roadmap translates business goals into a sequence of technology initiatives. It can help leadership understand what to address now, what can wait, and how projects depend on one another.

Cloud and Infrastructure Strategy

Consultants can help evaluate whether public cloud, private cloud, on-premises infrastructure, or a hybrid approach is appropriate. Planning should consider cost, performance, security, resilience, and the skills required to manage the chosen environment.

Cybersecurity and Risk Management

Strategic security planning goes beyond installing individual tools. It considers policies, access controls, employee practices, incident response, data protection, and business continuity. The goal is to make security part of everyday operations and long-term planning.

Application and Data Strategy

Businesses often rely on a mix of software and data sources. Consulting can help assess applications, plan integrations, reduce duplication, and establish better practices for data quality, access, and governance.

Technology Budgeting and Vendor Guidance

Consultants can help organizations forecast technology costs, compare options, review vendor proposals, and understand the full cost of ownership. This makes it easier to balance immediate needs with longer-term investments.

What the Consulting Process Typically Looks Like

  1. Discovery: The consultant learns about business priorities, current challenges, users, and existing technology.
  2. Assessment: Systems, processes, risks, and costs are reviewed to establish a baseline.
  3. Recommendations: Findings are translated into practical options, with trade-offs and expected outcomes explained.
  4. Roadmap: Initiatives are prioritized and organized by timing, dependencies, budget, and business impact.
  5. Implementation support: Depending on the engagement, the consultant may help coordinate projects, guide vendors, or track progress.
  6. Review and refinement: Results are evaluated, and the plan is updated as business needs change.

How to Choose an IT Consulting Partner

A useful consulting engagement starts with a clear understanding of your business—not a one-size-fits-all technology recommendation. Look for a partner who asks thoughtful questions, communicates in plain language, and explains the reasoning behind proposed solutions.

Consider the consultant’s experience with organizations of a similar size or complexity, their approach to security and change management, and how they measure success. It is also important to clarify the scope of work, deliverables, timeline, fees, and whether implementation support is included.

Making Technology a Strategic Advantage

Strategic IT consulting can help organizations move from reactive technology decisions to a more deliberate, business-focused approach. With a clear understanding of current capabilities and future priorities, leaders can make better investments, manage risk, and build systems that support lasting growth.

The most effective IT strategy is not simply a list of tools to buy. It is a practical plan for using technology to help the organization achieve its goals.


Understanding Strategic IT Consulting: Roles, Services, and Key Differences

  1. What does an IT strategy consultant do?
  2. What services do strategy consultants offer?
  3. What is the difference between tech consulting and strategy consulting?
  4. What is the difference between IT services and IT consultant?

What does an IT strategy consultant do?

An IT strategy consultant helps a business align its technology with its goals. They assess existing systems, processes, budgets, and risks; identify opportunities for improvement; and recommend practical steps for areas such as cybersecurity, cloud services, software, and infrastructure. They may also create a technology roadmap, prioritize investments, and guide implementation so the organization can make informed decisions and adapt as its needs change.

What services do strategy consultants offer?

Strategy consultants help businesses make informed decisions about their goals, operations, and future direction. Their services may include evaluating current business and technology strategies, identifying opportunities and risks, developing strategic plans and roadmaps, advising on digital transformation and IT investments, improving processes, and supporting organizational change. They may also help define performance measures and guide implementation so recommendations translate into practical results. The exact services depend on the consultant’s expertise and the organization’s needs.

What is the difference between tech consulting and strategy consulting?

Technology consulting focuses on specific technology needs, such as selecting software, modernizing infrastructure, improving cybersecurity, or implementing new systems. Strategy consulting focuses more broadly on an organization’s business direction, opportunities, and challenges. Strategic IT consulting connects the two: it examines how technology can support business goals and helps prioritize investments, initiatives, and roadmaps accordingly. In practice, the areas can overlap, but the key distinction is whether the primary focus is solving a technology problem or shaping business strategy.

What is the difference between IT services and IT consultant?

IT services typically involve the ongoing delivery and management of technology, such as help desk support, network monitoring, cybersecurity, and cloud administration. An IT consultant focuses on assessing your organization’s needs and recommending how technology can better support its goals. Consultants may also help plan or guide specific projects, while IT service providers often handle day-to-day operations. Some companies offer both, so the key difference is whether the primary focus is strategic advice or ongoing technical support.
cyber services

Cyber Services: Protecting Your Business in a Connected World

Cyber Services: Protecting Your Business in a Connected World

Businesses rely on digital tools to communicate, serve customers, store information, and manage daily operations. That connectivity creates opportunity—but it also brings risks. Cyber services help organizations protect their systems, data, and people from online threats while preparing them to respond when problems occur.

What Are Cyber Services?

Cyber services are professional services designed to strengthen an organization’s cybersecurity. Depending on a business’s needs, they may include assessing security risks, monitoring networks, protecting accounts and devices, training employees, and responding to cyber incidents.

Cybersecurity is not a one-time project. Technology, business needs, and threats change over time, so effective protection requires ongoing attention and regular improvements.

Common Types of Cyber Services

Security Assessments

A security assessment reviews an organization’s systems, policies, and practices to identify weaknesses. The results can help prioritize improvements, such as updating software, tightening access controls, or creating stronger data-handling procedures.

Network and Endpoint Protection

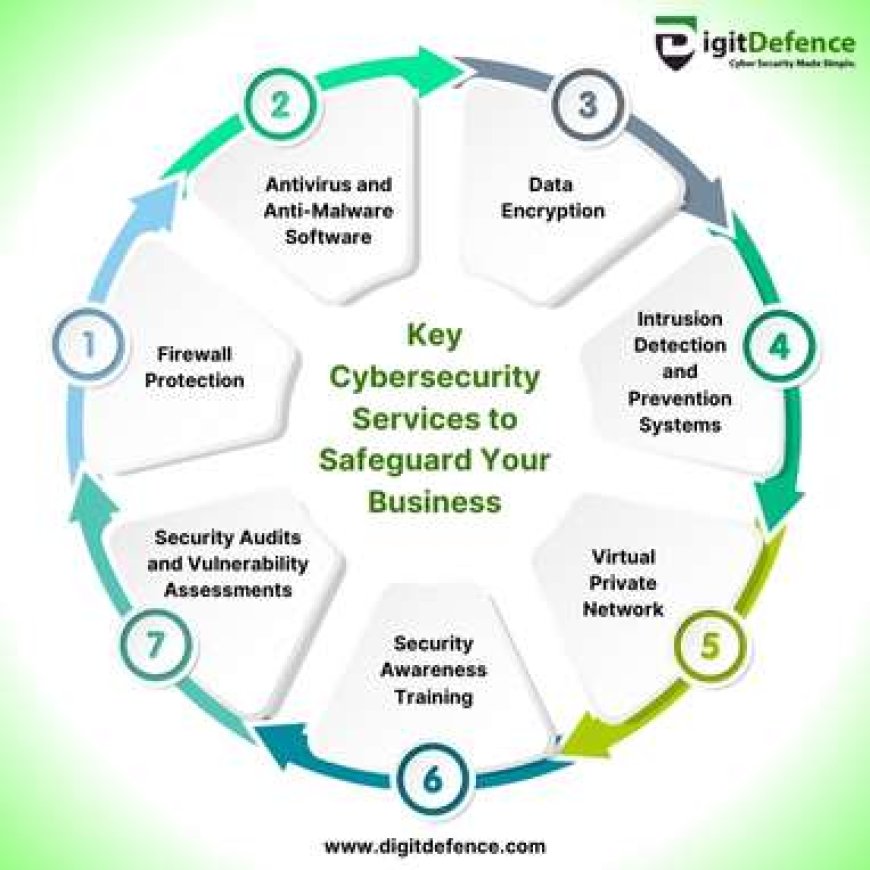
Networks, computers, mobile devices, and servers can all be targets. Cyber services may help configure firewalls, endpoint protection, secure remote access, and other safeguards to reduce the chance that an attacker can enter or move through a system.

Identity and Access Management

Access controls help ensure that people can use only the information and systems required for their roles. Services in this area may include multi-factor authentication, account reviews, and policies for creating, changing, and removing user access.

Security Monitoring

Monitoring can help detect unusual activity, such as unexpected login attempts or suspicious changes to a system. Depending on the service, alerts may be reviewed around the clock or during specified business hours. Clear monitoring and escalation procedures help organizations respond more quickly to potential issues.

Employee Security Training

Employees play an important role in protecting an organization. Practical training can help them recognize phishing messages, use passwords safely, handle sensitive information, and report suspicious activity. Regular reminders and realistic examples can make security practices easier to apply in daily work.

Incident Response and Recovery

Even organizations with strong protections can experience a security incident. Incident response services help establish what to do, who should be involved, and how to contain and investigate an event. Recovery planning can also address backups, restoration procedures, and communication with affected parties.

Why Cyber Services Matter

A cyber incident can interrupt operations, expose private information, damage trust, and create unexpected costs. Cyber services can help reduce these risks by identifying vulnerabilities, improving defenses, and preparing teams to act. They can also support organizations that need to meet contractual, regulatory, or industry-specific security requirements.

No service can guarantee that an organization will never experience an attack. The goal is to make systems harder to compromise, detect problems sooner, and limit the impact if an incident occurs.

Choosing the Right Cyber Services

The right approach depends on an organization’s size, technology, data, budget, and risk tolerance. Before choosing a provider, consider:

  • Which systems and information need the most protection?
  • What security work is already handled internally?
  • How quickly will the provider respond to alerts or incidents?
  • What services are included, and what may cost extra?
  • How will progress and recommendations be reported?
  • Does the provider have experience with organizations of a similar size or type?

Ask for clear explanations of service scope, responsibilities, response times, and data handling. A useful provider should be able to explain risks and recommendations in plain language, not just provide technical reports.

Building a Stronger Security Program

Cyber services work best as part of a broader security program. Organizations can support that work by keeping software updated, using multi-factor authentication, limiting access to sensitive systems, maintaining reliable backups, and giving employees a clear way to report concerns. Regular reviews help ensure that protections keep pace with changes in the business.

With a thoughtful plan and the right expertise, cyber services can help an organization protect its operations, respond with confidence, and make informed decisions about technology and risk.


8 Essential Tips for Enhancing Your Cybersecurity Services

  1. Choose a trusted cybersecurity provider.
  2. Enable multifactor authentication.
  3. Keep software and services updated.
  4. Use strong, unique passwords.
  5. Back up important data regularly.
  6. Train staff to spot phishing.
  7. Review access permissions often.
  8. Check incident response plans regularly.

Choose a trusted cybersecurity provider.

Choosing a trusted cybersecurity provider is an important step in protecting your business. Look for a provider with relevant experience, clear service offerings, strong references, and a straightforward approach to explaining risks and recommendations. Before signing an agreement, ask about response times, data handling, and exactly what the services include. A reliable provider will take time to understand your needs and help you make informed security decisions.

Enable multifactor authentication.

Enable multifactor authentication (MFA) on your email, financial, cloud, and other important accounts. MFA requires a second form of verification—such as an authenticator app, security key, or one-time code—in addition to your password. This extra step can help prevent unauthorized access even if a password is stolen. For stronger protection, use an authenticator app or security key when available, and never share verification codes with anyone.

Keep software and services updated.

Keeping software and services updated is one of the simplest ways to strengthen cybersecurity. Updates often fix known security vulnerabilities that attackers could exploit, as well as improve reliability and performance. Turn on automatic updates when practical, and regularly check that operating systems, applications, plug-ins, and cloud services are current. For business-critical systems, plan updates carefully and verify that backups and recovery procedures are in place before making major changes.

Use strong, unique passwords.

Use strong, unique passwords for every account to make it harder for attackers to access your systems and sensitive information. A long passphrase made from several unrelated words can be easier to remember and tougher to guess than a short, complicated password. Avoid reusing passwords across work and personal accounts, and consider using a reputable password manager to create and store them securely. Enable multi-factor authentication whenever it’s available for an extra layer of protection.

Back up important data regularly.

Back up important data regularly to reduce the risk of losing files to hardware failure, accidental deletion, ransomware, or other disruptions. Use a reliable backup solution, keep copies separate from your main devices or network, and protect them with strong access controls. Test your backups periodically to make sure the data can be restored when you need it.

Train staff to spot phishing.

Train staff to spot phishing by teaching them to recognize common warning signs, such as unexpected attachments, urgent requests, unfamiliar sender addresses, and links that don’t match the message. Encourage employees to verify unusual requests through a separate trusted channel and report suspicious messages promptly. Regular, practical training helps make careful email habits part of everyday work and can reduce the risk of stolen credentials, malware, and data breaches.

Review access permissions often.

Review access permissions often to make sure employees and contractors can reach only the systems and information they need for their roles. Remove access promptly when someone changes jobs or leaves the organization, and disable unused accounts to reduce opportunities for unauthorized entry. Regular permission reviews can help catch outdated or excessive access before it becomes a security risk.

Check incident response plans regularly.

Check your incident response plans regularly to make sure they reflect your current systems, team members, and business needs. Review contact lists, roles, escalation steps, and recovery procedures, and update them whenever something changes. Practicing the plan with realistic scenarios can reveal gaps before an actual incident occurs, helping your team respond faster and reduce disruption.

Network Security Best Practices: Essential Steps to Protect Your Network

Network Security Best Practices

A secure network helps protect sensitive information, keep systems available, and reduce the risk of costly disruptions. Whether you manage a home network, a small business, or a large organization, network security works best as an ongoing process—not a one-time setup. The practices below can help you strengthen your defenses and respond more effectively to threats.

Keep Systems and Network Devices Updated

Install security updates for operating systems, applications, routers, firewalls, and other network equipment as soon as practical. Updates often fix vulnerabilities that attackers could otherwise exploit. Replace devices that no longer receive security support, and remove software or services that are no longer needed.

Where possible, enable automatic updates for routine security fixes. For business environments, test important updates before broad deployment and maintain a schedule for reviewing devices that may have been missed.

Use Strong Authentication

Change default usernames and passwords on routers, access points, and other equipment. Use long, unique passwords for every account, ideally stored in a reputable password manager. Avoid shared accounts when individual accounts are available, since personal accounts make it easier to track activity and revoke access when someone leaves.

Enable multifactor authentication (MFA) for administrative accounts, remote access, cloud services, and other important systems. MFA adds another verification step, making a stolen password less useful to an attacker.

Limit Access and Apply Least Privilege

Give users and devices only the access they need to do their work. Separate everyday user accounts from administrator accounts, and use elevated privileges only when necessary. Review permissions regularly, especially after job changes or departures.

Disable unused accounts, open ports, network services, and remote-access tools. Restrict administrative interfaces so they are reachable only from approved devices or trusted network locations.

Segment the Network

Network segmentation divides a network into smaller sections, limiting how far an intruder can move if one device or account is compromised. For example, organizations can separate employee computers, servers, guest Wi-Fi, and internet-connected devices such as cameras or printers.

Use firewall rules to control which sections can communicate and allow only the connections required for normal operations. Review these rules periodically to remove outdated or overly broad access.

Secure Wi-Fi and Remote Connections

Protect wireless networks with current encryption and a strong, unique passphrase. Change the access point’s default administrator credentials, keep its firmware updated, and use a separate guest network for visitors and personal devices. Avoid exposing the network’s administrative interface to the public internet.

For remote work, require secure connections through an approved VPN or other protected access method. Combine remote access with MFA, limit who can use it, and monitor for unusual sign-in activity. Do not rely on a VPN alone; remote devices should also be updated and protected.

Deploy Firewalls and Endpoint Protection

Firewalls help control traffic entering and leaving a network. Configure them to deny unnecessary connections by default, then allow only the traffic required for business or personal use. Check firewall logs and rules for unexpected changes or suspicious activity.

Install reputable endpoint protection on computers and servers, and keep it enabled and updated. Endpoint tools can help detect malicious files, suspicious behavior, and other threats that network controls may not catch.

Protect Data and Backups

Encrypt sensitive data when it is stored and when it travels across networks. Use secure protocols and avoid sending confidential information over untrusted connections without appropriate protection.

Maintain regular backups of important data and systems. Keep at least one backup isolated from the main network so malware or an intruder cannot easily alter or delete every copy. Test restores periodically; a backup is useful only if it can be recovered.

Monitor Activity and Prepare to Respond

Collect and review logs from firewalls, servers, endpoints, and important applications. Alerts can help identify unusual login attempts, unexpected data transfers, or changes to critical settings. Make sure logs are protected from unauthorized changes and retained long enough to support investigations.

Create an incident response plan that explains who to contact, how to isolate affected systems, how to preserve evidence, and how to restore operations. Practice the plan so that people know what to do under pressure.

Train Users and Review Security Regularly

People play an important role in network security. Teach users how to recognize phishing attempts, report suspicious messages, handle sensitive information, and use approved tools. Make reporting easy and respond constructively so potential problems are raised quickly.

Regularly review network diagrams, device inventories, access permissions, firewall rules, and security policies. Periodic vulnerability assessments can help identify weaknesses before they are exploited. Address findings according to their risk and verify that fixes have worked.

Make Security an Ongoing Practice

No single tool can protect every network from every threat. Strong security comes from combining updated systems, careful access controls, segmentation, monitoring, backups, and informed users. Start with the measures that address your most important risks, document your decisions, and revisit them as your network and needs change.


7 Essential Tips for Strengthening Your Network Security

  1. Use strong, unique passwords and enable multifactor authentication.
  2. Keep routers, firewalls, and devices updated.
  3. Use WPA3 or WPA2 encryption for Wi-Fi.
  4. Change default administrator usernames and passwords.
  5. Segment guest and smart-home devices from sensitive systems.
  6. Disable unused ports, services, and remote access.
  7. Monitor network logs and investigate unusual activity.

Use strong, unique passwords and enable multifactor authentication.

Use strong, unique passwords for every network account, especially administrator and remote-access accounts. Long passphrases are easier to remember and harder to guess, while a password manager can help you store them securely without reusing them. Enable multifactor authentication (MFA) wherever possible to add another layer of protection, so a stolen password alone is less likely to grant access.

Keep routers, firewalls, and devices updated.

Keep routers, firewalls, computers, and other connected devices updated with the latest security patches and firmware. Updates often fix vulnerabilities that attackers could exploit, so install them promptly and enable automatic updates when available. Replace devices that no longer receive security support, and remove outdated software or services you no longer use.

Use WPA3 or WPA2 encryption for Wi-Fi.

Use WPA3 encryption to protect your Wi-Fi network whenever your router and devices support it. If WPA3 isn’t available, choose WPA2-AES rather than outdated options such as WEP or WPA. Set a strong, unique Wi-Fi password, change the router’s default administrator credentials, and keep its firmware up to date to help prevent unauthorized access.

Change default administrator usernames and passwords.

Change the default administrator username and password on every router, access point, and network device you manage. Default credentials are often publicly documented, so attackers may try them to gain control of a device and alter its settings, intercept traffic, or access connected systems. Choose a unique, strong password for each device, change the administrator username if the device allows it, and store the credentials securely in a password manager.

Segment guest and smart-home devices from sensitive systems.

Place guest devices and smart-home equipment—such as TVs, cameras, and speakers—on a separate Wi-Fi network from computers, phones, and other systems that contain sensitive information. These devices may have weaker security or receive fewer updates, so separating them helps limit access if one is compromised. Use your router’s guest-network or network-segmentation feature, and allow only the connections each device needs.

Disable unused ports, services, and remote access.

Disable unused network ports, services, and remote-access tools to reduce the number of ways an attacker could reach your systems. Turn off features you don’t need, close unnecessary firewall ports, and limit administrative access to trusted devices or locations. Review these settings regularly, since old services and access rules can remain enabled long after they’re needed.

Monitor network logs and investigate unusual activity.

Monitor network logs regularly to spot unusual activity, such as repeated failed sign-in attempts, unexpected connections, or large transfers of data. Set alerts for suspicious patterns and investigate them promptly to determine whether they’re harmless or signs of a security issue. Keeping logs protected and retaining them long enough can also help identify what happened and support a faster response.

cyber security management services

Cyber Security Management Services: Protecting Your Business from Digital Threats

Cybersecurity Management Services: Protecting Your Business in a Changing Threat Landscape

Cybersecurity is an ongoing business responsibility, not a one-time technology project. New threats, changing systems, and evolving work practices can create risks for organizations of every size. Cybersecurity management services help businesses assess those risks, strengthen their defenses, and respond effectively when security issues arise.

What Are Cybersecurity Management Services?

Cybersecurity management services provide ongoing support for the people, processes, and technologies used to protect an organization’s systems and information. Depending on a business’s needs, services may include security assessments, monitoring, policy development, employee training, incident response planning, and help with regulatory requirements.

Some organizations manage cybersecurity internally, while others work with an outside provider for specialized expertise or day-to-day support. A provider may work alongside an internal IT team or take responsibility for selected security functions.

Common Cybersecurity Management Services

Security Risk Assessments

A risk assessment identifies potential weaknesses in systems, accounts, applications, and business processes. It can help an organization understand which risks are most important and decide where to focus its security investments.

Security Monitoring and Threat Detection

Monitoring tools can help identify unusual activity, suspicious logins, malware, and other potential threats. When alerts are reviewed and handled promptly, businesses may be better positioned to investigate problems before they cause wider disruption.

Vulnerability and Patch Management

Software vulnerabilities can leave systems exposed if they are not addressed. Vulnerability management involves identifying known weaknesses, prioritizing them by risk, and coordinating updates or other safeguards.

Identity and Access Management

Managing who can access business systems is a core part of cybersecurity. Services may include multifactor authentication, access reviews, stronger account controls, and processes for promptly changing or removing access when someone changes roles or leaves the organization.

Employee Security Awareness

Employees can help protect an organization when they know how to recognize phishing attempts, handle sensitive information, and report suspicious activity. Training can reinforce practical security habits and make reporting concerns easier.

Incident Response Planning

Even well-prepared organizations can experience security incidents. An incident response plan outlines who should take action, how systems and information will be protected, and how the organization will communicate and recover. Planning ahead can reduce confusion during a high-pressure situation.

Backup and Recovery Planning

Reliable backups can help a business restore important data after an outage, accidental deletion, hardware failure, or ransomware incident. A recovery plan should identify what needs to be restored first and include regular tests to check that backups can be used.

Why Ongoing Cybersecurity Management Matters

Security needs change as organizations adopt new applications, hire employees, work with vendors, or move data to cloud services. Ongoing management can help businesses keep track of these changes and maintain appropriate protections over time.

  • Reduce avoidable risk: Regular reviews can reveal weaknesses before they become larger problems.
  • Improve response readiness: Clear plans and responsibilities help teams act more effectively during an incident.
  • Support business continuity: Security and recovery planning can help limit interruptions to essential operations.
  • Make security more consistent: Documented procedures help employees and teams follow the same expectations.
  • Use expertise effectively: Outside specialists can provide skills or coverage that may be difficult to maintain in-house.

Choosing a Cybersecurity Management Provider

Cybersecurity services should fit an organization’s systems, operations, and risk profile. Before selecting a provider, consider the following:

  • Which services are included, and which require additional fees?
  • How are alerts reviewed, prioritized, and escalated?
  • Who will be responsible for responding to an incident?
  • How will the provider coordinate with internal IT staff and leadership?
  • How are access to business systems and sensitive information controlled?
  • What reports, recommendations, or service reviews will be provided?
  • Can the provider support the organization’s legal, contractual, and regulatory obligations?

It is also helpful to ask how a provider will learn about the business, document its environment, and measure progress. A useful relationship should include clear communication and practical recommendations—not just software or alerts.

Build a Security Program That Can Adapt

Effective cybersecurity management is a continuing process. It starts with understanding the organization’s most important systems and risks, then combines suitable safeguards with monitoring, training, and response planning. Regular reviews help ensure those measures remain relevant as the business changes.

Cybersecurity management services can give organizations the structure and support to take a more proactive approach. With clear priorities and consistent oversight, businesses can better protect their information, support daily operations, and prepare for security challenges.


Top FAQs About Cybersecurity Management Services: Costs, Careers, and Key Players

  1. What are the top 3 cybersecurity companies?
  2. What is the average cost of cyber security services?
  3. Can I make $200,000 a year in cyber security?
  4. What are cyber security managed services?
  5. What is cybersecurity service management?
  6. What are the examples of managed security services?
  7. What is the role of cyber security management?
  8. How much do cybersecurity services cost?

What are the top 3 cybersecurity companies?

There isn’t a universally agreed-upon top three, since the best cybersecurity company depends on an organization’s size, needs, and budget. CrowdStrike, Palo Alto Networks, and Microsoft are widely recognized for their cybersecurity products and services, including threat detection, network security, and cloud protection. For managed cybersecurity services, compare providers based on their expertise, monitoring and response capabilities, industry experience, and fit with your existing systems.

What is the average cost of cyber security services?

There’s no single average cost for cybersecurity services because pricing depends on your organization’s size, risk level, systems, and the type of support needed. Small businesses may pay a few hundred to several thousand dollars per month for ongoing managed security, while assessments, compliance projects, and incident response are often priced separately. The best way to estimate your cost is to identify your priorities and request a detailed quote that explains what’s included, how support is provided, and whether there are additional fees.

Can I make $200,000 a year in cyber security?

Yes, earning $200,000 a year in cybersecurity is possible, especially in senior or specialized roles such as security architect, director of information security, or security consultant. Reaching that level often requires substantial experience, in-demand technical or leadership skills, and working in a higher-paying market; compensation may also include bonuses or stock rather than base salary alone. Pay varies widely by location, employer, and role, so $200,000 is achievable for some professionals but is not a typical starting salary or a guaranteed outcome.

What are cyber security managed services?

Cybersecurity managed services are ongoing security solutions provided by an outside specialist to help protect an organization’s systems, data, and users. Depending on the provider and service plan, they may include security monitoring, threat detection, vulnerability and patch management, access controls, employee training, and incident response support. These services can supplement an in-house IT team or provide security expertise a business does not have internally.

What is cybersecurity service management?

Cybersecurity service management is the process of planning, coordinating, and overseeing the security services an organization uses to protect its systems, data, and users. It may include managing security monitoring, access controls, vulnerability updates, incident response, employee training, and reporting. The goal is to make these services work together, align them with business needs, and continually adapt them as threats and technology change.

What are the examples of managed security services?

Examples of managed security services include 24/7 security monitoring and threat detection, managed firewalls, endpoint protection, vulnerability scanning and patch management, email security, identity and access management, security awareness training, data backup and recovery, and incident response support. A provider may deliver these services individually or combine them into a broader program tailored to an organization’s systems, risks, and needs.

What is the role of cyber security management?

Cybersecurity management helps an organization protect its systems, networks, and sensitive information by coordinating security policies, tools, and practices. It includes identifying and reducing risks, managing access, monitoring for suspicious activity, preparing for and responding to incidents, and helping employees follow safe security practices. By regularly reviewing and improving these measures, cybersecurity management supports business continuity and helps the organization adapt to changing threats.

How much do cybersecurity services cost?

The cost of cybersecurity services depends on your organization’s size, risk level, systems, and the type of support you need. A one-time security assessment typically costs less than ongoing services such as 24/7 monitoring, vulnerability management, incident response, or compliance support. Pricing may be based on a monthly subscription, the number of users or devices, or a custom scope of work. Requesting a detailed quote can help you compare what’s included and choose services that fit your budget and security priorities.

cybersecurity as a service

Cybersecurity as a Service: A Practical Guide for Businesses

Cybersecurity as a Service: A Practical Guide for Businesses

Cybersecurity is no longer a one-time project. Threats change constantly, software needs regular updates, and even well-prepared organizations can face new risks. For many businesses, keeping up requires more time and specialized expertise than an in-house team can provide. Cybersecurity as a Service (CSaaS) offers another approach: access to ongoing security tools and expertise through an external provider.

What Is Cybersecurity as a Service?

Cybersecurity as a Service is a model in which an organization relies on a third-party provider for some or all of its security operations. Services are typically delivered on an ongoing basis and may be tailored to the organization’s size, systems, risk profile, and regulatory requirements.

Depending on the provider and service plan, CSaaS may include security monitoring, threat detection, vulnerability assessments, incident response support, employee training, and help with security policies. Some providers focus on a specific area, while others offer a broader managed security program.

Common Cybersecurity as a Service Offerings

  • Security monitoring: Reviewing activity across networks, devices, cloud environments, and applications to identify suspicious behavior.
  • Managed detection and response: Investigating potential threats and helping contain or remediate them. The exact level of response varies by provider and contract.
  • Vulnerability management: Identifying weaknesses in systems and helping prioritize fixes based on risk.
  • Endpoint protection: Managing security for computers, mobile devices, and servers.
  • Cloud security: Helping protect cloud accounts, workloads, data, and configurations.
  • Identity and access management: Supporting controls such as multifactor authentication, role-based access, and account reviews.
  • Security awareness training: Teaching employees how to recognize phishing, handle sensitive information, and report concerns.
  • Incident response planning: Preparing procedures and providing support when a security event occurs.

Why Businesses Choose CSaaS

Access to specialized expertise: Security providers may bring experience across different technologies and threat scenarios. This can be valuable for organizations that do not have a dedicated security team.

Ongoing coverage: Security risks do not follow business hours. Some services provide continuous monitoring or on-call support, depending on the agreement.

Predictable costs: A subscription or managed-services arrangement can make security spending easier to plan than building every capability internally. Costs and included services vary, so it is important to review the full scope.

Room to scale: Services can often be adjusted as an organization adds employees, locations, applications, or cloud systems.

More focus on core work: By delegating selected security tasks, internal staff may have more time for other business priorities. Outsourcing does not remove the organization’s responsibility for managing risk, however.

What CSaaS Does Not Do

Cybersecurity as a Service is not a guarantee that an organization will never experience a breach. No provider can eliminate every risk, and technology alone cannot prevent every incident. Effective security still depends on clear policies, reliable backups, timely software updates, appropriate access controls, and informed employees.

Responsibility is also shared. The provider may operate specific tools or monitor defined systems, while the customer remains responsible for decisions such as approving access, protecting business data, and following applicable legal or regulatory requirements. Those boundaries should be documented before service begins.

How to Choose a Provider

Start by identifying the problems the service needs to solve. A business seeking help with after-hours monitoring may need a different arrangement from one preparing for a compliance review or improving cloud security.

  • Define the scope: Confirm which systems, locations, users, and data are covered—and which are not.
  • Understand response procedures: Ask who investigates alerts, who can take action, how quickly the provider responds, and when the business will be contacted.
  • Review service levels: Look for clear commitments about availability, response times, reporting, and escalation. Check how those commitments are measured.
  • Ask about data handling: Understand what information the provider collects, where it is stored, who can access it, and how it is protected.
  • Check experience and references: Look for experience with organizations of a similar size, industry, and technology environment.
  • Clarify responsibilities: Establish who manages software updates, account permissions, investigations, backups, and incident communications.
  • Plan for continuity: Ask how service handoffs, data access, and security operations will work if the contract ends.

Making the Most of the Service

Before onboarding, create an accurate inventory of devices, applications, cloud services, and important data. Share existing policies and known risks with the provider, and identify internal contacts who can make decisions during an incident. Regularly review reports and hold meetings to discuss unresolved issues, changing business needs, and recommended improvements.

It is also important to test the relationship before an emergency. Tabletop exercises and incident-response drills can reveal unclear responsibilities and communication gaps while there is still time to address them.

Conclusion

Cybersecurity as a Service can help businesses access security expertise and ongoing support without building every capability in-house. The value depends on choosing services that match actual risks, defining responsibilities clearly, and staying actively involved. With a well-scoped agreement and sound internal practices, CSaaS can become a practical part of a broader cybersecurity program.


Top 5 Advantages of Cybersecurity as a Service for Your Business

  1. Access to specialized security expertise
  2. Continuous threat monitoring
  3. Predictable subscription costs
  4. Scales with business needs
  5. Frees staff to focus on core work


7 Potential Drawbacks of Cybersecurity as a Service: Costs, Control, and More

  1. Ongoing subscription costs can add up.
  2. Less direct control over security operations.
  3. Service quality varies between providers.
  4. Sensitive data may be shared with a vendor.
  5. Response times may depend on the service agreement.
  6. Integrating tools can be complex.
  7. Outsourcing does not eliminate business risk.

Access to specialized security expertise

Cybersecurity as a Service gives businesses access to specialized security expertise without requiring them to hire and maintain a large in-house team. Providers bring experience with evolving threats, security tools, and industry practices, helping organizations identify risks, strengthen defenses, and respond to potential incidents. This expertise can be especially valuable for small and midsize businesses that need knowledgeable support but may not have the resources to build a dedicated security department.

Continuous threat monitoring

Continuous threat monitoring helps organizations spot suspicious activity as it happens, rather than discovering it after significant damage has occurred. A cybersecurity provider can monitor networks, devices, and cloud systems around the clock, investigate alerts, and notify the right people when action is needed. This ongoing visibility can help businesses respond to emerging threats more quickly, even when their internal team is unavailable.

Predictable subscription costs

Cybersecurity as a Service can make security spending more predictable through a regular subscription fee. Instead of making large upfront investments in tools, hiring, and ongoing maintenance, businesses can budget for an agreed set of services each month or year. Costs depend on the provider and scope, so reviewing what’s included—and what may incur extra charges—helps avoid surprises.

Scales with business needs

Cybersecurity as a Service can scale as your business changes. You can adjust coverage as you add employees, open new locations, adopt cloud tools, or face new security requirements—without having to build an entirely new in-house security team. This flexibility helps keep protection aligned with your needs and budget as your organization grows.

Frees staff to focus on core work

Cybersecurity as a Service can free employees from time-consuming security tasks, such as monitoring alerts, managing tools, and tracking routine updates. With a specialized provider handling agreed-upon responsibilities, your team can spend more time on the work that directly supports your business goals. Outsourcing security does not eliminate the need for internal oversight, but it can help staff focus their attention where it matters most.

Ongoing subscription costs can add up.

Ongoing subscription costs for cybersecurity as a service can add up over time, especially as a business grows or adds more users, devices, and security features. What starts as a manageable monthly expense may become a significant part of the IT budget, so it’s important to review pricing, renewal terms, and potential add-on fees regularly. Compare the total long-term cost with the value and coverage provided to make sure the service continues to fit your needs.

Less direct control over security operations.

One potential drawback of cybersecurity as a service is having less direct control over day-to-day security operations. When an outside provider manages monitoring, tools, or incident response, your team may have limited visibility into how decisions are made or how quickly actions are taken. This can create challenges if the provider’s procedures do not align with your business priorities. To reduce the risk, define responsibilities, approval requirements, reporting expectations, and escalation procedures clearly in the service agreement.

Service quality varies between providers.

Service quality can vary significantly between cybersecurity providers, making it difficult to know what level of protection you’ll receive. Providers may differ in their expertise, monitoring capabilities, response times, communication, and the tools they use. A service that sounds comprehensive may also have important limits in its contract. Before choosing a provider, review exactly what’s included, ask how incidents are handled, and check references to ensure the service meets your organization’s needs.

Sensitive data may be shared with a vendor.

One potential drawback of cybersecurity as a service is that protecting your systems may require sharing sensitive data with an outside vendor. Depending on the service, the provider could access security logs, user information, system configurations, or other confidential details. This creates additional privacy and data-protection risks, especially if the vendor’s controls or practices are inadequate. Before signing an agreement, review what data will be collected, how it will be stored and protected, who can access it, and whether it will be shared with subcontractors.

Response times may depend on the service agreement.

Response times for cybersecurity as a service can depend on the terms of the service agreement. A provider may prioritize incidents according to severity, offer different response levels for different plans, or limit support to certain hours. If those details are unclear, a business could wait longer than expected for help during a security incident. Before signing, confirm response-time commitments, after-hours coverage, escalation procedures, and what actions the provider is authorized to take.

Integrating tools can be complex.

Integrating cybersecurity tools can be complex, especially when a provider’s platforms need to work with existing networks, cloud services, and business applications. Compatibility issues, duplicated alerts, or gaps in data sharing can make it harder to get a clear view of security risks. Setup may also require changes to workflows and access controls, so businesses should clarify integration requirements, responsibilities, and ongoing support before adopting a service.

Outsourcing does not eliminate business risk.

Outsourcing cybersecurity can add valuable expertise and support, but it does not eliminate a business’s responsibility for managing risk. The provider can only protect the systems, data, and processes covered by the agreement, and gaps in scope, communication, or internal practices may leave the organization exposed. Businesses still need to make informed security decisions, maintain sound policies, train employees, and understand who is responsible for each task—especially during an incident.

it strategy and consulting

Maximizing Business Success Through Effective IT Strategy and Consulting

Article: IT Strategy and Consulting

The Importance of IT Strategy and Consulting in Today’s Business World

In the fast-paced and ever-evolving landscape of technology, having a robust IT strategy is crucial for the success of any business. An effective IT strategy not only aligns technology with business goals but also ensures that resources are utilized efficiently to drive growth and innovation.

Benefits of IT Strategy and Consulting

Alignment with Business Objectives: A well-defined IT strategy ensures that technology initiatives are in sync with the overall objectives of the organization, enabling seamless integration and collaboration across departments.

Cost Optimization: Through strategic planning and consulting, businesses can identify areas where technology investments can be optimized to reduce costs while maximizing returns on investment.

Risk Management: IT strategy helps businesses mitigate risks associated with cybersecurity threats, data breaches, compliance issues, and technological disruptions by implementing proactive security measures and disaster recovery plans.

Innovation and Competitive Advantage: By leveraging cutting-edge technologies and innovative solutions, businesses can gain a competitive edge in the market, drive product development, enhance customer experience, and stay ahead of industry trends.

The Role of IT Consultants

IT consultants play a vital role in helping businesses develop and implement effective IT strategies tailored to their specific needs. These professionals bring expertise in technology trends, industry best practices, and project management to guide organizations through complex technological challenges.

From conducting comprehensive assessments of existing IT infrastructure to recommending solutions for optimization and growth, IT consultants provide valuable insights that empower businesses to make informed decisions that drive success.

Conclusion

In conclusion, investing in IT strategy and consulting is essential for businesses looking to thrive in today’s digital age. By aligning technology with business objectives, optimizing costs, managing risks effectively, fostering innovation, and leveraging the expertise of IT consultants, organizations can position themselves for sustainable growth and competitive advantage in an increasingly tech-driven world.


Understanding IT Strategy and Consulting: Key Questions Answered

  1. What is strategy and consulting?
  2. What does an IT strategy consultant do?
  3. What is the difference between strategy and technology consulting?
  4. What is the highest IT consultant salary?
  5. What is the difference between Accenture technology and strategy and consulting?
  6. Who are the big 4 strategy consultants?

What is strategy and consulting?

Strategy and consulting in the realm of IT refer to the process of developing a comprehensive plan that aligns technology initiatives with the overarching goals and objectives of an organization. IT strategy involves analyzing current technological infrastructure, identifying areas for improvement, and outlining a roadmap for implementing solutions that drive efficiency, innovation, and growth. Consulting in this context entails seeking expert advice and guidance from professionals who specialize in IT to navigate complex technological challenges, optimize resources, mitigate risks, and leverage cutting-edge solutions to achieve strategic business outcomes. By combining strategic planning with expert consultation, businesses can enhance their competitive edge and adapt to the rapidly evolving digital landscape effectively.

What does an IT strategy consultant do?

An IT strategy consultant plays a crucial role in helping businesses navigate the complex world of technology by providing expert guidance on developing and implementing effective IT strategies. These professionals work closely with organizations to assess their current IT infrastructure, identify areas for improvement, and align technology initiatives with business goals. IT strategy consultants leverage their knowledge of industry best practices, emerging technologies, and project management to design customized solutions that drive innovation, optimize resources, mitigate risks, and enhance overall operational efficiency. By collaborating with IT strategy consultants, businesses can gain valuable insights and expertise to make informed decisions that propel them towards success in today’s competitive digital landscape.

What is the difference between strategy and technology consulting?

When it comes to IT strategy and consulting, understanding the difference between strategy and technology consulting is essential. Strategy consulting focuses on aligning technology initiatives with overall business objectives, identifying opportunities for growth, and optimizing resources to drive innovation. On the other hand, technology consulting delves into the technical aspects of implementing solutions, evaluating systems, and providing expertise on specific technologies to enhance operational efficiency. While strategy consulting guides the overarching direction of IT investments, technology consulting offers specialized knowledge and implementation support to ensure that technology solutions are effectively integrated into the business environment. Both types of consulting play complementary roles in helping organizations achieve their IT goals and maximize the value of their technological investments.

What is the highest IT consultant salary?

The highest IT consultant salary can vary depending on factors such as experience, expertise, industry demand, and geographic location. In general, top-tier IT consultants with extensive experience and specialized skills in areas like cybersecurity, cloud computing, or data analytics can command high salaries. Salaries for IT consultants at senior levels in major tech hubs or consulting firms can reach six figures or more, reflecting the value placed on their strategic guidance and technical proficiency by organizations seeking to optimize their IT infrastructure and drive digital transformation initiatives.

What is the difference between Accenture technology and strategy and consulting?

When comparing Accenture Technology and Strategy and Consulting services, it’s essential to understand their distinct focuses. Accenture Technology primarily centers on delivering innovative technological solutions and implementing digital transformations for businesses. On the other hand, Accenture Strategy and Consulting concentrate on providing strategic advice, management consulting, and helping organizations navigate complex business challenges by aligning their operations with overarching goals. While both divisions are integral parts of Accenture’s offerings, Technology emphasizes technology-driven solutions, whereas Strategy and Consulting focus on holistic business strategy and operational excellence.

Who are the big 4 strategy consultants?

The “Big 4” strategy consultants refer to the four largest and most renowned consulting firms globally, namely McKinsey & Company, The Boston Consulting Group (BCG), Bain & Company, and Deloitte. These firms are highly respected for their expertise in providing strategic advice and consulting services to a wide range of industries and organizations. Known for their innovative approaches, deep industry knowledge, and track record of delivering impactful solutions, the Big 4 strategy consultants are trusted partners for businesses seeking to enhance their competitive edge and navigate complex challenges in today’s dynamic business environment.

ai projects

Innovative AI Projects Shaping the Future of Technology

AI Projects: Transforming the Future

AI Projects: Transforming the Future

Artificial Intelligence (AI) has become a cornerstone of modern technology, revolutionizing industries and reshaping how we interact with the world. From healthcare to finance, AI projects are driving innovation and efficiency at an unprecedented pace. This article explores some of the most impactful AI projects and their potential to transform our future.

Healthcare Innovations

The healthcare industry is experiencing a paradigm shift thanks to AI projects focused on improving patient care and diagnosis accuracy. Machine learning algorithms analyze vast amounts of medical data to detect patterns that might be invisible to human eyes. For instance, AI-driven diagnostic tools can identify early signs of diseases like cancer or diabetes, enabling timely interventions.

Personalized Medicine

AI projects are also paving the way for personalized medicine. By analyzing genetic information and patient history, AI can tailor treatments to individual needs, increasing effectiveness and reducing side effects. This level of customization was unimaginable a decade ago but is now becoming a reality.

Financial Sector Advancements

The financial industry is leveraging AI projects for risk management, fraud detection, and customer service enhancement. Algorithms can process transactions in real-time to identify fraudulent activities, saving companies billions in potential losses.

Algorithmic Trading

One of the most notable applications is algorithmic trading. AI systems analyze market trends and execute trades at optimal times, maximizing profits while minimizing risks. These systems operate at speeds far beyond human capabilities, giving firms a competitive edge.

Sustainable Solutions

As environmental concerns grow, AI projects are being developed to promote sustainability. From optimizing energy consumption in smart grids to predicting climate change impacts through data analysis, AI plays a crucial role in creating a more sustainable future.

Agricultural Efficiency

Agriculture is another area where AI is making significant strides. Precision farming techniques use AI to analyze soil conditions and weather patterns, ensuring optimal crop yields while minimizing resource use.

The Road Ahead

The potential of AI projects is vast and largely untapped. As technology continues to evolve, so will the scope of what these projects can achieve. Collaboration between industries and governments will be essential in navigating ethical considerations and ensuring that AI serves humanity positively.

In conclusion, AI projects are not just technological advancements; they are transformative forces that have the power to redefine industries and improve lives globally. As we continue to explore their possibilities, one thing remains certain: the future with AI looks promising indeed.


9 Essential Tips for Successfully Managing AI Projects

  1. Clearly define the problem you want to solve with AI.
  2. Collect and prepare high-quality data for training your AI model.
  3. Choose the right algorithms and techniques based on your problem and data.
  4. Regularly evaluate and iterate on your AI model for improvements.
  5. Consider ethical implications in your AI project, such as bias and privacy concerns.
  6. Ensure transparency in how your AI model makes decisions or predictions.
  7. Plan for scalability to handle larger datasets or increased usage of your AI application.
  8. Keep up-to-date with advancements in AI research and technologies.
  9. Collaborate with experts from diverse fields to gain different perspectives on your AI project.

Clearly define the problem you want to solve with AI.

When embarking on an AI project, it’s crucial to clearly define the problem you aim to solve. This foundational step sets the direction for the entire project and ensures that resources are utilized effectively. By articulating a specific problem, teams can tailor their approach, select appropriate algorithms, and gather relevant data that directly addresses the issue at hand. A well-defined problem statement not only guides the development process but also helps in measuring success and evaluating outcomes. Without a clear understanding of the problem, AI projects risk becoming unfocused, leading to wasted efforts and suboptimal solutions.

Collect and prepare high-quality data for training your AI model.

Collecting and preparing high-quality data is a crucial step in training an effective AI model. The success of any AI project largely depends on the quality of the data fed into the system, as it directly influences the model’s ability to learn and make accurate predictions. High-quality data should be clean, relevant, and representative of the real-world scenarios the model will encounter. This involves removing any inaccuracies or inconsistencies, ensuring that the data is comprehensive and unbiased, and properly formatting it for analysis. By investing time in gathering and refining data, developers can significantly enhance the performance and reliability of their AI models, leading to more successful outcomes in their projects.

Choose the right algorithms and techniques based on your problem and data.

Choosing the right algorithms and techniques is crucial when embarking on an AI project, as it directly impacts the effectiveness and efficiency of the solution. The nature of your problem and the characteristics of your data should guide this selection process. For instance, if you’re dealing with a classification problem with labeled data, supervised learning algorithms like decision trees or support vector machines might be appropriate. On the other hand, if you have large amounts of unlabeled data, unsupervised learning techniques such as clustering or dimensionality reduction could be more suitable. Additionally, understanding the intricacies of your data—such as its volume, variety, and velocity—can help determine whether more complex models like deep learning are necessary. Ultimately, aligning your algorithm choice with your specific problem and data ensures that you build a robust and scalable AI solution.

Regularly evaluate and iterate on your AI model for improvements.

Regularly evaluating and iterating on your AI model is crucial for achieving continuous improvement and maintaining its effectiveness. As data evolves and new patterns emerge, the initial assumptions and parameters of an AI model may no longer be optimal. By routinely assessing the model’s performance using updated datasets, you can identify areas where it may be underperforming or encountering biases. Iterative refinement allows for adjustments that enhance accuracy, reliability, and adaptability to changing conditions. This process not only ensures that the AI system remains relevant but also maximizes its potential to deliver meaningful insights and results over time.

Consider ethical implications in your AI project, such as bias and privacy concerns.

When developing AI projects, it’s crucial to consider the ethical implications, particularly regarding bias and privacy concerns. AI systems can inadvertently perpetuate or even exacerbate biases present in the data they are trained on, leading to unfair outcomes. Therefore, it is essential to ensure that datasets are diverse and representative to mitigate these issues. Additionally, privacy is a significant concern as AI technologies often require vast amounts of personal data. Implementing robust data protection measures and being transparent about data usage can help build trust with users and stakeholders. Addressing these ethical considerations not only enhances the integrity of the project but also ensures that AI technologies contribute positively to society.

Ensure transparency in how your AI model makes decisions or predictions.

Ensuring transparency in AI models is crucial for building trust and accountability in their decision-making processes. When developing AI projects, it’s important to provide clear explanations of how models arrive at specific decisions or predictions. This involves documenting the data sources, algorithms, and methodologies used, as well as offering insights into the model’s reasoning pathways. Transparency helps stakeholders understand the basis of AI outputs, which is essential for validating accuracy and fairness. Moreover, it allows users to identify potential biases or errors, facilitating improvements and ethical compliance. By prioritizing transparency, developers can foster confidence among users and ensure that AI systems are both reliable and responsible.

Plan for scalability to handle larger datasets or increased usage of your AI application.

When developing AI projects, planning for scalability is crucial to ensure that your application can handle larger datasets and increased usage effectively. As the volume of data continues to grow exponentially, an AI system must be designed with the flexibility to expand its processing capabilities without compromising performance. This involves choosing scalable infrastructure solutions, such as cloud-based platforms, that allow for seamless integration of additional resources as needed. Additionally, implementing efficient algorithms and data management strategies will help maintain speed and accuracy even as demands increase. By prioritizing scalability from the outset, developers can future-proof their AI applications, ensuring they remain robust and reliable as user needs evolve.

Keep up-to-date with advancements in AI research and technologies.

Staying current with advancements in AI research and technologies is crucial for the success of any AI project. The field of artificial intelligence is rapidly evolving, with new algorithms, tools, and methodologies emerging regularly. By keeping up-to-date, project teams can leverage the latest innovations to enhance their solutions, improve efficiency, and maintain a competitive edge. Additionally, understanding current trends and breakthroughs allows teams to anticipate future challenges and opportunities, ensuring their projects remain relevant and effective. Engaging with academic publications, attending industry conferences, and participating in online forums are effective ways to stay informed about the ever-changing landscape of AI.

Collaborate with experts from diverse fields to gain different perspectives on your AI project.

Collaboration with experts from diverse fields is crucial for the success of AI projects, as it brings a wealth of perspectives and expertise that can drive innovation and problem-solving. By engaging professionals from various disciplines—such as data science, engineering, ethics, and domain-specific fields—you can ensure that your AI project benefits from a comprehensive understanding of both technical and contextual challenges. This multidisciplinary approach not only helps in identifying potential biases and ethical concerns but also fosters creative solutions that might not emerge within a single field. Ultimately, leveraging diverse expertise leads to more robust, effective, and socially responsible AI systems.

narrow ai

Unlocking the Potential of Narrow AI: Specialized Intelligence for Tomorrow

Understanding Narrow AI: The Specialized Intelligence of the Future

Artificial Intelligence (AI) has become a buzzword in today’s technological landscape, but not all AI is created equal. One of the most prevalent forms of AI currently in use is Narrow AI, also known as weak AI. Unlike general AI, which aims to replicate human intelligence across a wide range of tasks, narrow AI is designed to perform specific tasks with remarkable efficiency.

What is Narrow AI?

Narrow AI refers to systems that are highly proficient at performing a particular task or set of tasks. These systems are trained on large datasets and utilize algorithms to achieve high performance levels in their area of expertise. Examples include facial recognition software, recommendation algorithms, and voice assistants like Siri and Alexa.

Characteristics of Narrow AI

  • Task-Specific: Narrow AI excels at specific tasks but lacks the ability to perform outside its designated domain.
  • Data-Driven: These systems rely heavily on data for training and improving their performance over time.
  • Lack of Consciousness: Unlike general or strong AI, narrow AI does not possess consciousness or self-awareness.

The Impact of Narrow AI

Narrow AI has already made significant contributions across various industries:

  • Healthcare: In medical diagnostics, narrow AI can analyze medical images with high accuracy, assisting doctors in early detection and treatment planning.
  • Finance: Algorithms are used for fraud detection and risk management, ensuring secure transactions and investments.
  • E-commerce: Recommendation engines personalize shopping experiences by suggesting products based on user behavior and preferences.

The Limitations of Narrow AI

Despite its capabilities, narrow AI has limitations that must be acknowledged:

  • Lack of Flexibility: These systems cannot adapt to new tasks without significant reprogramming or retraining.
  • No Understanding: While they can process information efficiently, they do not understand it as humans do.
  • Poor Generalization: Their effectiveness diminishes when applied outside their trained domain or when faced with unfamiliar data patterns.

The Future of Narrow AI

The future holds immense potential for narrow AI as advancements continue to enhance its capabilities. By integrating more sophisticated machine learning techniques and expanding data inputs, narrow AI systems can become even more precise and efficient in their specialized roles. However, the development towards general or strong AI remains a separate challenge requiring further breakthroughs in understanding cognition and consciousness.

Conclusion

Narrow AI stands as a testament to how technology can transform industries by performing specific tasks with unparalleled precision. As we continue to innovate within this realm, it’s crucial to recognize both the strengths and limitations of these systems while exploring ethical considerations surrounding their deployment. By harnessing the power of narrow AI responsibly, society can benefit from its specialized intelligence without compromising broader human values.


7 Key Benefits of Narrow AI: Boosting Efficiency, Accuracy, and Personalization Across Industries

  1. Highly efficient at specific tasks
  2. Can process large amounts of data quickly and accurately
  3. Improves productivity by automating repetitive tasks
  4. Enhances decision-making with data-driven insights
  5. Increases precision and accuracy in various applications
  6. Facilitates personalized user experiences in e-commerce and entertainment
  7. Aids in medical diagnostics for early detection and treatment planning


Challenges of Narrow AI: Limited Adaptability, Lack of Understanding, and Domain-Specific Performance

  1. Limited Adaptability
  2. Lack of Understanding
  3. Diminished Performance Outside Trained Domain

Highly efficient at specific tasks

Narrow AI is renowned for its high efficiency in performing specific tasks, making it an invaluable tool across various industries. By focusing on a single domain, these systems can be meticulously trained to achieve exceptional levels of accuracy and speed. For instance, in the realm of data analysis, narrow AI can process vast amounts of information far more quickly and accurately than a human could, identifying patterns and insights that might otherwise go unnoticed. This efficiency not only saves time but also reduces errors, leading to better decision-making and streamlined operations. Whether it’s recognizing faces in images or optimizing supply chains, narrow AI’s ability to excel at specialized tasks allows businesses to enhance productivity and deliver superior results.

Can process large amounts of data quickly and accurately

Narrow AI excels in processing large amounts of data quickly and accurately, making it an invaluable tool in today’s data-driven world. Unlike humans, who can be overwhelmed by vast datasets, narrow AI systems can analyze and interpret complex information at incredible speeds. This capability allows businesses and organizations to gain insights and make data-driven decisions more efficiently than ever before. For instance, in industries like finance and healthcare, narrow AI can sift through massive volumes of transactions or medical records to identify patterns, detect anomalies, or predict outcomes with precision. This not only enhances operational efficiency but also leads to more informed strategies and improved outcomes across various sectors.

Improves productivity by automating repetitive tasks

Narrow AI significantly enhances productivity by automating repetitive tasks that would otherwise consume valuable time and resources. By taking over mundane and routine operations, such as data entry, scheduling, and basic customer service inquiries, narrow AI allows employees to focus on more complex and creative aspects of their work. This shift not only increases efficiency but also reduces the likelihood of human error in repetitive processes. As a result, businesses can achieve higher output levels with greater accuracy while freeing up human talent to drive innovation and strategic growth.

Enhances decision-making with data-driven insights

Narrow AI significantly enhances decision-making processes by providing data-driven insights that are both precise and actionable. By analyzing vast amounts of data quickly and accurately, narrow AI systems can identify patterns and trends that might be missed by human analysts. This capability allows businesses and organizations to make informed decisions based on empirical evidence rather than intuition alone. For example, in the financial sector, narrow AI can predict market trends and assess risks with high accuracy, enabling investors to optimize their portfolios. In healthcare, AI-driven insights can assist doctors in diagnosing diseases earlier and more accurately by detecting subtle indicators in medical imaging. Overall, the ability of narrow AI to process and interpret complex datasets empowers decision-makers across various industries to act with greater confidence and efficiency.

Increases precision and accuracy in various applications

Narrow AI significantly enhances precision and accuracy across a wide range of applications by leveraging advanced algorithms and large datasets. In fields such as healthcare, narrow AI systems can analyze medical images with exceptional detail, aiding in the early detection of diseases like cancer with greater accuracy than traditional methods. In manufacturing, AI-driven robots perform tasks with consistent precision, reducing errors and increasing efficiency on production lines. Financial institutions utilize narrow AI to detect fraudulent activities by identifying anomalies in transaction patterns with high accuracy. This increased precision not only improves outcomes but also saves time and resources, allowing professionals to focus on more complex decision-making tasks while relying on AI for meticulous data analysis.

Facilitates personalized user experiences in e-commerce and entertainment

Narrow AI significantly enhances personalized user experiences in e-commerce and entertainment by leveraging advanced algorithms to analyze individual preferences and behaviors. In e-commerce, narrow AI systems process vast amounts of data to recommend products tailored to a user’s past purchases, browsing history, and even real-time interactions. This level of personalization not only improves customer satisfaction but also increases conversion rates for businesses. Similarly, in the entertainment industry, streaming platforms use narrow AI to curate content recommendations based on a viewer’s watching habits, ensuring that users are consistently engaged with content that aligns with their tastes. By delivering highly customized experiences, narrow AI fosters a more engaging and efficient interaction between users and digital platforms.

Aids in medical diagnostics for early detection and treatment planning

Narrow AI plays a crucial role in the field of medical diagnostics by enhancing the accuracy and speed of early disease detection and treatment planning. By leveraging advanced algorithms and vast datasets, AI systems can analyze medical images, such as X-rays, MRIs, and CT scans, with remarkable precision. This capability allows healthcare professionals to identify abnormalities that might be missed by the human eye, leading to earlier diagnosis of conditions like cancer, cardiovascular diseases, and neurological disorders. As a result, patients benefit from timely interventions that can significantly improve outcomes and increase survival rates. Furthermore, narrow AI assists in developing personalized treatment plans by evaluating patient data against extensive medical databases to recommend the most effective therapies tailored to individual needs.

Limited Adaptability

Narrow AI, while highly effective at performing specific tasks, suffers from limited adaptability. This limitation means that these systems cannot easily transition to new tasks or environments without significant reprogramming or retraining. Unlike humans, who can apply general knowledge and reasoning to unfamiliar situations, narrow AI operates within a fixed framework defined by its initial programming and training data. As a result, any change in the task parameters or environment requires developers to invest considerable time and resources in updating the system. This inflexibility can hinder the deployment of narrow AI in dynamic settings where adaptability is crucial for success.

Lack of Understanding

Narrow AI systems, while highly efficient at processing vast amounts of data, fundamentally lack true understanding and contextual awareness. This limitation means that although they can analyze and generate outputs based on patterns and algorithms, they do not comprehend the deeper meaning behind the information they process. For instance, a language translation AI might convert text from one language to another with high accuracy, but it cannot grasp cultural nuances or the subtleties of human communication. This absence of genuine understanding can lead to errors or misinterpretations in situations where context is crucial. As a result, narrow AI often requires human oversight to ensure that its outputs align with real-world complexities and nuanced decision-making.

Diminished Performance Outside Trained Domain

Narrow AI systems are highly specialized, excelling in tasks they are specifically trained for, but their performance significantly diminishes when confronted with tasks or data patterns outside their training domain. This limitation arises because these systems rely heavily on large datasets and algorithms tailored to specific functions. When presented with unfamiliar scenarios, narrow AI lacks the flexibility and adaptability found in human intelligence, resulting in suboptimal or erroneous outputs. This constraint highlights the importance of carefully defining the scope and application of narrow AI systems to ensure they operate within environments where they can perform efficiently and accurately.

Exploring the Transformative Power of AI and ML in Today’s World

The Impact of AI and ML on Modern Technology

The Impact of AI and ML on Modern Technology

Artificial Intelligence (AI) and Machine Learning (ML) are two of the most transformative technologies in today’s digital landscape. They are driving innovation across various sectors, from healthcare to finance, and are reshaping how businesses operate and make decisions.

Understanding AI and ML

Artificial Intelligence refers to the simulation of human intelligence processes by machines, particularly computer systems. These processes include learning, reasoning, problem-solving, perception, and language understanding.

Machine Learning, a subset of AI, involves the use of algorithms that enable computers to learn from data and improve their performance over time without being explicitly programmed. ML is about making predictions or decisions based on data inputs.

Applications in Various Industries

The applications of AI and ML are vast and varied:

  • Healthcare: AI is being used to analyze complex medical data for diagnostics, personalize treatment plans, and even predict patient outcomes.
  • Finance: Financial institutions use ML algorithms for fraud detection, risk management, algorithmic trading, and personalized banking services.
  • Retail: Retailers leverage AI for inventory management, customer service through chatbots, personalized marketing strategies, and demand forecasting.
  • Automotive: Autonomous vehicles rely heavily on AI for navigation systems that can interpret sensor data to make driving decisions.

The Benefits of AI and ML

The integration of AI and ML into business operations offers several benefits:

  • Efficiency: Automation of routine tasks reduces human error and frees up resources for more strategic activities.
  • Insights: Advanced analytics provide deeper insights into customer behavior, market trends, and operational efficiencies.
  • Innovation: Companies can develop new products or services faster by leveraging predictive analytics to understand market needs better.

The Challenges Ahead

Despite their advantages, implementing AI and ML comes with challenges. These include concerns about data privacy, the need for large datasets to train models effectively, potential biases in algorithms leading to unfair outcomes, and the ethical implications of autonomous decision-making systems.

The Future Outlook

The future looks promising as advancements in computing power continue to drive innovation in AI and ML. As these technologies evolve further, they will become even more integral to our daily lives—enhancing productivity while opening up new possibilities across different fields.

A continued focus on ethical practices will be essential as society navigates this technological evolution. By addressing these concerns proactively while fostering innovation responsibly—AI’s potential can be harnessed fully for global benefit.


Exploring AI and ML: Key Differences, Applications, Ethics, Bias Mitigation, and Business Challenges

  1. What is the difference between Artificial Intelligence (AI) and Machine Learning (ML)?
  2. How are Artificial Intelligence and Machine Learning being used in healthcare?
  3. What are the ethical implications of using AI and ML in decision-making processes?
  4. Can AI algorithms be biased, and how can bias be mitigated in Machine Learning models?
  5. What are some common challenges faced when implementing AI and ML solutions in businesses?

What is the difference between Artificial Intelligence (AI) and Machine Learning (ML)?

Artificial Intelligence (AI) and Machine Learning (ML) are often used interchangeably, but they represent distinct concepts within the realm of computer science. AI is a broad field that encompasses the development of systems capable of performing tasks that typically require human intelligence, such as reasoning, problem-solving, and understanding language. It aims to create machines that can mimic cognitive functions like learning and adaptation. On the other hand, Machine Learning is a subset of AI focused on the idea that machines can learn from data. ML involves algorithms that allow computers to identify patterns and make decisions with minimal human intervention. Essentially, while all machine learning is AI, not all AI involves machine learning. ML is one approach to achieving AI by enabling systems to improve their performance over time through experience and data analysis.

How are Artificial Intelligence and Machine Learning being used in healthcare?

Artificial Intelligence (AI) and Machine Learning (ML) are revolutionizing healthcare by enhancing diagnostic accuracy, personalizing treatment, and improving patient outcomes. AI systems can analyze complex medical data, such as imaging scans and electronic health records, to assist doctors in diagnosing diseases more accurately and swiftly. Machine learning algorithms are being used to develop predictive models that identify patients at risk of certain conditions, enabling early intervention. Additionally, AI-driven tools help in drug discovery by analyzing vast datasets to identify potential new treatments. In personalized medicine, ML algorithms tailor treatment plans based on an individual’s genetic makeup and lifestyle factors, ensuring more effective care. These technologies are also streamlining administrative tasks within healthcare facilities, allowing professionals to focus more on patient care.

What are the ethical implications of using AI and ML in decision-making processes?

The ethical implications of using AI and ML in decision-making processes are significant and multifaceted. As these technologies become more integrated into various sectors, they raise concerns about bias, transparency, and accountability. AI systems can inadvertently perpetuate or even amplify existing biases present in the data they are trained on, leading to unfair or discriminatory outcomes. Transparency is another critical issue, as the decision-making processes of complex algorithms can be opaque, making it difficult for users to understand how decisions are reached. This lack of clarity can undermine trust and accountability, especially in high-stakes areas like criminal justice or hiring. Additionally, there are concerns about privacy and the extent to which personal data is used responsibly. Ensuring ethical use of AI and ML requires ongoing efforts to develop fair algorithms, implement robust oversight mechanisms, and engage in open dialogue about their societal impacts.

Can AI algorithms be biased, and how can bias be mitigated in Machine Learning models?

AI algorithms can indeed be biased, primarily because they learn from data that may contain existing biases. These biases can stem from unrepresentative datasets, historical prejudices, or flawed data collection methods. When AI models are trained on such data, they can inadvertently perpetuate or even amplify these biases in their predictions and decisions. To mitigate bias in Machine Learning models, it’s crucial to use diverse and representative datasets during the training phase. Additionally, implementing fairness-aware algorithms and regularly auditing models for biased outcomes are essential steps. Transparency in the development process and involving interdisciplinary teams to evaluate model outputs can further help identify and address potential biases, ensuring that AI systems operate more equitably across different user groups.

What are some common challenges faced when implementing AI and ML solutions in businesses?

Implementing AI and ML solutions in businesses often presents several challenges. One of the primary hurdles is data quality and availability; AI and ML models require large volumes of high-quality data to function effectively, yet many organizations struggle with data silos or incomplete datasets. Additionally, integrating these technologies into existing systems can be complex and resource-intensive, requiring significant investment in infrastructure and skilled personnel. There is also the challenge of algorithmic bias, where models may inadvertently perpetuate existing biases present in the training data, leading to unfair outcomes. Furthermore, ensuring data privacy and security is crucial, as AI systems often handle sensitive information. Lastly, businesses must navigate the cultural shift within the organization as employees adapt to new workflows and processes driven by AI technologies.

applied artificial intelligence

Unlocking Potential: The Power of Applied Artificial Intelligence

Applied Artificial Intelligence: Transforming Industries

Applied Artificial Intelligence: Transforming Industries

Artificial Intelligence (AI) has moved from the realm of science fiction into real-world applications that are transforming industries across the globe. Applied AI refers to the practical implementation of AI technologies to solve specific problems and enhance efficiency in various sectors.

What is Applied Artificial Intelligence?

Applied AI involves using machine learning algorithms, neural networks, and other AI techniques to create systems that can perform tasks traditionally requiring human intelligence. This includes visual perception, speech recognition, decision-making, and language translation.

Key Areas of Application

The impact of applied AI is vast and spans multiple industries:

  • Healthcare: In healthcare, AI is used for predictive analytics, personalized medicine, and robotic surgery. It helps in diagnosing diseases more accurately and developing treatment plans tailored to individual patients.
  • Finance: Financial institutions use AI for fraud detection, algorithmic trading, and risk management. These applications help in identifying suspicious activities and making informed investment decisions.
  • Manufacturing: In manufacturing, AI enhances production processes through predictive maintenance and quality control. It helps reduce downtime by predicting equipment failures before they occur.
  • Retail: Retailers leverage AI for inventory management, customer service chatbots, and personalized shopping experiences. This improves customer satisfaction and optimizes supply chain operations.
  • Agriculture: Farmers use AI-driven tools for precision agriculture, which involves analyzing data from drones or sensors to optimize crop yields while minimizing resource usage.

The Benefits of Applied AI

The application of AI provides numerous benefits:

  1. Increased Efficiency: Automation of repetitive tasks leads to faster processing times and reduces human error.
  2. Improved Decision-Making: Data-driven insights enable better decision-making processes across various sectors.
  3. Cost Reduction: By optimizing processes and reducing waste, businesses can achieve significant cost savings.
  4. Enhanced Customer Experience: Personalized services improve customer engagement and satisfaction levels.

The Future of Applied Artificial Intelligence

The future of applied AI holds immense potential as advancements continue at a rapid pace. As technology evolves, we can expect even more sophisticated applications that will further revolutionize industries worldwide. However, it is essential to address ethical considerations such as data privacy and bias in algorithms to ensure responsible deployment of these technologies.

The ongoing integration of applied artificial intelligence into everyday operations signifies a transformative shift towards more intelligent systems capable of augmenting human capabilities like never before. As we embrace this technological evolution responsibly, the possibilities are limitless for creating a smarter world driven by innovation.


6 Essential Tips for Successfully Applying Artificial Intelligence in Real-World Scenarios

  1. Understand the problem you are trying to solve before applying AI.
  2. Collect and prepare high-quality data for training AI models.
  3. Choose the right AI algorithm or model based on the nature of the problem.
  4. Regularly evaluate and fine-tune your AI models to improve performance.
  5. Consider ethical implications and biases when deploying AI in real-world applications.
  6. Stay updated with the latest advancements in AI technology and research.

Understand the problem you are trying to solve before applying AI.

Before diving into the implementation of artificial intelligence solutions, it’s crucial to have a clear understanding of the problem at hand. This preliminary step ensures that AI is applied effectively and efficiently, tailored to address specific challenges rather than being a one-size-fits-all solution. By thoroughly analyzing the problem, stakeholders can identify the most relevant data, determine appropriate AI models, and set realistic goals for what the technology should achieve. This approach not only maximizes the potential benefits of AI but also minimizes wasted resources and time by avoiding unnecessary complexity. In essence, a well-defined problem statement lays the groundwork for successful AI application, ensuring that technological efforts align closely with business objectives and deliver tangible results.

Collect and prepare high-quality data for training AI models.

In the realm of applied artificial intelligence, one of the most crucial steps is collecting and preparing high-quality data for training AI models. The performance and accuracy of an AI system are heavily dependent on the quality of the data it learns from. High-quality data ensures that the model can recognize patterns effectively and make accurate predictions or decisions. This involves not only gathering a large volume of relevant data but also ensuring that it is clean, well-labeled, and representative of real-world scenarios. Proper data preparation includes handling missing values, eliminating duplicates, and normalizing formats to ensure consistency. By investing time and resources in this foundational step, organizations can significantly enhance the effectiveness of their AI applications, leading to more reliable outcomes and insights.

Choose the right AI algorithm or model based on the nature of the problem.

When applying artificial intelligence, selecting the appropriate algorithm or model is crucial to effectively addressing the specific problem at hand. Different AI algorithms are designed to tackle various types of tasks, such as classification, regression, clustering, or natural language processing. For instance, if the goal is to categorize images into different groups, a convolutional neural network (CNN) might be suitable due to its strength in image recognition tasks. On the other hand, for predicting future sales based on historical data, a time series forecasting model could be more appropriate. Understanding the nature of the problem allows for choosing an AI approach that maximizes accuracy and efficiency while minimizing computational resources. This strategic selection not only enhances performance but also ensures that AI solutions are tailored to meet specific business needs and objectives.

Regularly evaluate and fine-tune your AI models to improve performance.

Regularly evaluating and fine-tuning AI models is crucial for maintaining and enhancing their performance. As data evolves and business environments change, AI models can become less effective if not periodically updated. By continuously assessing model accuracy and relevance, organizations can identify areas for improvement and make necessary adjustments. Fine-tuning involves recalibrating the model’s parameters or incorporating new data to ensure it adapts to current conditions. This proactive approach not only helps in achieving more accurate predictions but also enhances the overall efficiency of AI systems, ensuring they deliver optimal results aligned with organizational goals.

Consider ethical implications and biases when deploying AI in real-world applications.

When deploying AI in real-world applications, it is crucial to consider the ethical implications and potential biases that may arise. AI systems are often trained on large datasets, which can inadvertently contain biases reflecting historical or societal prejudices. If not addressed, these biases can lead to unfair outcomes or reinforce existing inequalities. Ethical considerations should be at the forefront of AI development, ensuring transparency, accountability, and fairness in decision-making processes. By actively identifying and mitigating biases, developers and organizations can build trust with users and create AI systems that promote equitable treatment across diverse populations. Balancing innovation with ethical responsibility is essential for harnessing the full potential of applied artificial intelligence while safeguarding human rights and values.

Stay updated with the latest advancements in AI technology and research.

Staying updated with the latest advancements in AI technology and research is crucial for anyone involved in the field, as it ensures that individuals and organizations remain competitive and innovative. By keeping abreast of new developments, one can leverage cutting-edge techniques and tools to improve existing systems or create groundbreaking applications. This continuous learning process allows for the identification of emerging trends, such as novel machine learning algorithms or breakthroughs in neural network architectures, which can be pivotal in solving complex problems more efficiently. Additionally, understanding the latest research helps in anticipating future challenges and opportunities, enabling proactive strategies that align with technological progress. Engaging with academic publications, attending conferences, and participating in professional networks are effective ways to stay informed and inspired by the rapidly evolving landscape of artificial intelligence.