cfchris.com

Loading

Enhancing Cyber Security: The Role of Trusted Providers

The Importance of Cyber Security Providers

The Importance of Cyber Security Providers

In today’s digital age, where businesses and individuals rely heavily on technology, the need for robust cyber security measures has never been greater. Cyber threats are constantly evolving, becoming more sophisticated and dangerous. This is where cyber security providers play a crucial role in safeguarding sensitive information and protecting against cyber attacks.

What Do Cyber Security Providers Offer?

Cyber security providers offer a range of services designed to protect organizations from cyber threats. These services may include:

  • Network security: Securing networks from unauthorized access and monitoring for suspicious activities.
  • Endpoint security: Protecting individual devices such as computers, laptops, and mobile devices from malware and other threats.
  • Incident response: Developing strategies to respond to and mitigate the impact of cyber attacks.
  • Security awareness training: Educating employees on best practices for maintaining cyber security.
  • Vulnerability assessments: Identifying weaknesses in systems that could be exploited by attackers.

Why Choose a Cyber Security Provider?

Partnering with a cyber security provider offers several benefits:

  • Expertise: Cyber security providers have specialized knowledge and experience in identifying and mitigating cyber threats.
  • 24/7 Monitoring: Many providers offer around-the-clock monitoring to detect and respond to threats in real-time.
  • Compliance: Providers can help ensure that organizations comply with relevant regulations and standards related to data protection.
  • Cutting-Edge Technology: Providers stay abreast of the latest trends in cyber security technology to provide the most effective protection.
  • Cost-Effectiveness: Outsourcing cyber security services can be more cost-effective than maintaining an in-house team.

Conclusion

In conclusion, cyber security providers play a vital role in defending against the ever-growing threat of cyber attacks. By partnering with a reputable provider, organizations can enhance their defenses, protect sensitive data, and maintain business continuity in the face of evolving cyber threats.


Top 7 FAQs About Choosing and Working with Cyber Security Providers

  1. What services do cyber security providers offer?
  2. How can a cyber security provider help protect my business from cyber threats?
  3. What factors should I consider when choosing a cyber security provider?
  4. Do cyber security providers offer 24/7 monitoring services?
  5. How do cyber security providers stay updated on the latest threats and technologies?
  6. Can a cyber security provider help my business comply with data protection regulations?
  7. What are the benefits of outsourcing cyber security services to a provider?

What services do cyber security providers offer?

Cyber security providers offer a wide range of services to help organizations protect themselves against cyber threats. These services typically include network security to secure systems from unauthorized access, endpoint security to protect individual devices from malware, incident response to mitigate the impact of cyber attacks, security awareness training for employees, and vulnerability assessments to identify weaknesses in systems. By offering these comprehensive services, cyber security providers empower businesses to enhance their defenses, safeguard sensitive information, and maintain a secure digital environment in the face of evolving cyber threats.

How can a cyber security provider help protect my business from cyber threats?

A cyber security provider can help protect your business from cyber threats by offering a comprehensive range of services tailored to your specific needs. They can conduct thorough assessments to identify vulnerabilities in your systems, implement robust security measures to safeguard your network and data, provide continuous monitoring for early threat detection, offer incident response services to mitigate the impact of attacks, and educate your employees on best practices for maintaining cyber security. By leveraging their expertise and cutting-edge technology, a cyber security provider can significantly enhance your defenses against cyber threats and ensure the resilience of your business in the face of evolving risks.

What factors should I consider when choosing a cyber security provider?

When choosing a cyber security provider, several factors should be carefully considered to ensure that you select the right partner for your organization’s needs. Firstly, evaluate the provider’s expertise and experience in the field of cyber security, including their track record in handling similar challenges. Assess the range of services they offer and determine if they align with your specific requirements. Additionally, consider the provider’s approach to compliance with industry regulations and standards to ensure that your data is adequately protected. It is also essential to assess their response capabilities in the event of a cyber incident and their commitment to staying updated on emerging threats and technologies. Lastly, factor in considerations such as cost-effectiveness, scalability of services, and the provider’s reputation within the industry when making your decision.

Do cyber security providers offer 24/7 monitoring services?

Yes, many cyber security providers offer 24/7 monitoring services as part of their comprehensive security solutions. This continuous monitoring allows for real-time detection and response to potential cyber threats, ensuring that any suspicious activities are identified and addressed promptly. By providing around-the-clock monitoring, cyber security providers can help organizations enhance their security posture and mitigate the risks associated with cyber attacks effectively.

How do cyber security providers stay updated on the latest threats and technologies?

Cyber security providers stay updated on the latest threats and technologies through a variety of proactive measures. They continuously monitor industry trends, research emerging cyber threats, and analyze data from previous incidents to stay ahead of potential risks. Additionally, many providers participate in information-sharing networks, collaborate with other security professionals, attend conferences, and undergo regular training to enhance their knowledge and skills. By investing in ongoing education and leveraging a network of resources, cyber security providers ensure they are well-equipped to protect their clients from evolving cyber threats.

Can a cyber security provider help my business comply with data protection regulations?

A cyber security provider can indeed help your business comply with data protection regulations. These providers have expertise in understanding and implementing the necessary security measures to ensure that your organization meets the requirements set forth by data protection regulations. They can assist in identifying potential vulnerabilities, implementing appropriate safeguards, and monitoring compliance to mitigate risks of data breaches. By partnering with a cyber security provider, businesses can benefit from specialized knowledge and guidance to navigate the complex landscape of data protection regulations effectively.

What are the benefits of outsourcing cyber security services to a provider?

Outsourcing cyber security services to a provider offers numerous benefits to organizations. By partnering with a specialized cyber security provider, businesses can access expert knowledge and experience in identifying and mitigating cyber threats. These providers often offer 24/7 monitoring, ensuring that threats are detected and responded to in real-time. Additionally, outsourcing can help organizations ensure compliance with data protection regulations and standards, leverage cutting-edge technology for enhanced protection, and potentially reduce costs compared to maintaining an in-house cyber security team. Overall, outsourcing cyber security services to a reputable provider can strengthen an organization’s defenses and safeguard sensitive data against evolving cyber threats.
aws cyber security

Enhancing Cloud Security: Leveraging AWS Cyber Security Solutions

AWS Cyber Security: Protecting Your Cloud Infrastructure

AWS Cyber Security: Protecting Your Cloud Infrastructure

As businesses increasingly rely on cloud services for their operations, ensuring the security of data and applications hosted on platforms like Amazon Web Services (AWS) is paramount. AWS offers robust security features to help protect your cloud infrastructure from cyber threats.

Key Aspects of AWS Cyber Security

Here are some key aspects of AWS cyber security that you should be aware of:

Shared Responsibility Model:

AWS follows a shared responsibility model, where they are responsible for the security of the cloud infrastructure, while customers are responsible for securing their data and applications within the cloud. Understanding this model is essential for implementing effective security measures.

Identity and Access Management (IAM):

AWS IAM allows you to manage user access to resources securely. By defining granular permissions and roles, you can control who can access which resources, helping prevent unauthorized access to sensitive data.

Network Security:

AWS provides tools such as Virtual Private Cloud (VPC) and Security Groups to secure your network infrastructure. You can create private networks, set up firewalls, and monitor network traffic to detect and prevent potential security breaches.

Data Encryption:

Encrypting data at rest and in transit is crucial for maintaining the confidentiality and integrity of your information. AWS offers services like AWS Key Management Service (KMS) for managing encryption keys and Amazon S3 server-side encryption for securing data stored in S3 buckets.

Best Practices for AWS Cyber Security

To enhance the security of your AWS environment, consider implementing the following best practices:

  • Regularly review and update IAM policies to ensure least privilege access.
  • Enable multi-factor authentication (MFA) for added account protection.
  • Monitor logs and set up alerts to detect suspicious activities.
  • Conduct regular vulnerability assessments and penetration testing.
  • Stay informed about AWS security updates and best practices.

Conclusion

In conclusion, AWS offers a wide range of security features to help safeguard your cloud infrastructure against cyber threats. By understanding these features and following best practices for AWS cyber security, you can create a more secure environment for your data and applications in the cloud.


8 Essential Tips for Strengthening AWS Cybersecurity

  1. Enable multi-factor authentication (MFA) for all user accounts
  2. Regularly rotate access keys and credentials
  3. Use AWS Identity and Access Management (IAM) to control access to AWS resources
  4. Encrypt data at rest and in transit using AWS Key Management Service (KMS)
  5. Monitor your AWS environment for security incidents using Amazon GuardDuty
  6. Implement network security best practices, such as configuring security groups and network ACLs
  7. Regularly update and patch your EC2 instances and other AWS services
  8. Enable logging and monitoring in AWS CloudTrail, CloudWatch, and Config

Enable multi-factor authentication (MFA) for all user accounts

Enabling multi-factor authentication (MFA) for all user accounts is a crucial step in enhancing the security of your AWS environment. By requiring an additional verification method beyond just a password, such as a unique code sent to a mobile device, MFA adds an extra layer of protection against unauthorized access. This simple yet effective measure significantly reduces the risk of account compromise and strengthens overall security posture, ensuring that only authorized users can access sensitive resources within your AWS infrastructure.

Regularly rotate access keys and credentials

Regularly rotating access keys and credentials is a crucial practice in AWS cyber security. By frequently updating these keys and credentials, you can reduce the risk of unauthorized access to your cloud resources. This proactive measure helps enhance the overall security posture of your AWS environment, ensuring that only authorized users have access to sensitive data and applications. Regular rotation of access keys and credentials is a simple yet effective way to mitigate potential security vulnerabilities and protect your cloud infrastructure from cyber threats.

Use AWS Identity and Access Management (IAM) to control access to AWS resources

Utilizing AWS Identity and Access Management (IAM) is a crucial tip for enhancing AWS cyber security. By leveraging IAM, businesses can effectively manage and control access to their AWS resources. IAM allows organizations to set granular permissions and roles, ensuring that only authorized users have access to specific resources within the cloud environment. This helps prevent unauthorized access, reduces the risk of data breaches, and enhances overall security posture on the AWS platform.

Encrypt data at rest and in transit using AWS Key Management Service (KMS)

To enhance the security of your data stored in Amazon Web Services (AWS), it is crucial to encrypt data both at rest and in transit using AWS Key Management Service (KMS). By utilizing KMS, you can manage encryption keys securely and ensure that your sensitive information remains protected from unauthorized access. Encrypting data at rest prevents unauthorized users from accessing data stored in databases or on disk, while encrypting data in transit adds an extra layer of security when data is being transferred between services or applications within your AWS environment. Implementing encryption with AWS KMS helps mitigate the risk of data breaches and strengthens the overall security posture of your cloud infrastructure.

Monitor your AWS environment for security incidents using Amazon GuardDuty

Monitoring your AWS environment for security incidents is crucial in maintaining a secure cloud infrastructure. Amazon GuardDuty is a powerful tool that can help you detect and respond to potential threats in real-time. By leveraging GuardDuty’s threat detection capabilities, you can proactively identify unauthorized access, malicious activities, and other suspicious behavior within your AWS environment. This proactive approach allows you to take immediate action to mitigate risks and strengthen the overall security posture of your cloud infrastructure.

Implement network security best practices, such as configuring security groups and network ACLs

Implementing network security best practices, such as configuring security groups and network Access Control Lists (ACLs), is crucial for enhancing the overall security of your AWS environment. By setting up proper security groups and ACLs, you can control inbound and outbound traffic to your instances, restrict access to specific ports, and prevent unauthorized network communication. These measures help reduce the attack surface and mitigate potential security risks, ensuring a more secure and resilient cloud infrastructure on Amazon Web Services.

Regularly update and patch your EC2 instances and other AWS services

Regularly updating and patching your EC2 instances and other AWS services is a critical aspect of maintaining strong cyber security in your cloud environment. By staying current with software updates and patches, you can address known vulnerabilities and reduce the risk of potential security breaches. This proactive approach helps to enhance the overall security posture of your AWS infrastructure, ensuring that your systems are better protected against emerging threats and attacks.

Enable logging and monitoring in AWS CloudTrail, CloudWatch, and Config

Enabling logging and monitoring in AWS services like CloudTrail, CloudWatch, and Config is a crucial tip for enhancing cyber security. By setting up comprehensive logging and monitoring mechanisms, businesses can gain valuable insights into their AWS environment, detect suspicious activities or unauthorized access in real-time, and ensure compliance with security policies. These tools provide visibility into user actions, resource changes, and system configurations, allowing organizations to proactively identify and respond to potential security threats effectively.

managed security services

Maximizing Security with Managed Security Services: Protecting Your Digital Assets

Article: Managed Security Services

The Importance of Managed Security Services

Managed Security Services (MSS) have become essential in today’s digital landscape where cyber threats are constantly evolving and becoming more sophisticated. Organizations, both large and small, are increasingly turning to MSS providers to protect their sensitive data and ensure the security of their IT infrastructure.

What are Managed Security Services?

Managed Security Services involve outsourcing the monitoring and management of security devices and systems to a third-party provider. These services typically include round-the-clock monitoring, threat detection, incident response, vulnerability assessments, and security updates.

The Benefits of Managed Security Services

Enhanced Security: MSS providers utilize advanced tools and technologies to detect and respond to security incidents in real-time, reducing the risk of data breaches.

Cost-Effectiveness: Outsourcing security operations to an MSS provider can be more cost-effective than maintaining an in-house security team, especially for small and medium-sized businesses.

Expertise: MSS providers employ cybersecurity experts who stay up-to-date with the latest threats and best practices in the industry, ensuring that your organization receives top-notch security services.

Choosing the Right MSS Provider

When selecting an MSS provider, consider factors such as their experience, reputation, range of services offered, compliance with industry standards, and scalability to accommodate your organization’s growth.

In Conclusion

Managed Security Services play a crucial role in safeguarding organizations against cyber threats and ensuring compliance with data protection regulations. By partnering with a reputable MSS provider, organizations can focus on their core business activities with the peace of mind that their digital assets are secure.


7 Benefits of Managed Security Services: Boosting Protection and Efficiency for Your Business

  1. Enhanced security through 24/7 monitoring
  2. Access to advanced cybersecurity tools and technologies
  3. Cost-effective compared to maintaining an in-house security team
  4. Expertise of cybersecurity professionals
  5. Quick incident response and threat detection
  6. Scalability to accommodate business growth
  7. Compliance with industry standards and regulations


7 Drawbacks of Managed Security Services: Cost, Dependency, and More

  1. Cost
  2. Dependency
  3. Integration Challenges
  4. Limited Customization
  5. Response Time
  6. Data Privacy Concerns
  7. Regulatory Compliance Risks

Enhanced security through 24/7 monitoring

Enhanced security through 24/7 monitoring is a key advantage of managed security services. With round-the-clock monitoring by dedicated cybersecurity experts, organizations can have peace of mind knowing that their IT infrastructure is continuously being monitored for any potential threats or vulnerabilities. This proactive approach allows for real-time threat detection and immediate response to security incidents, minimizing the risk of data breaches and ensuring that critical systems remain protected at all times.

Access to advanced cybersecurity tools and technologies

Access to advanced cybersecurity tools and technologies is a significant advantage of managed security services. By partnering with an MSS provider, organizations can leverage state-of-the-art security solutions that may be costly to acquire and maintain in-house. These advanced tools enable proactive threat detection, rapid incident response, and continuous monitoring of IT systems, enhancing overall cybersecurity posture and reducing the risk of data breaches. With access to cutting-edge technologies through managed security services, businesses can stay ahead of evolving cyber threats and better protect their sensitive information.

Cost-effective compared to maintaining an in-house security team

One significant advantage of opting for Managed Security Services is their cost-effectiveness when compared to the expenses involved in maintaining an in-house security team. By outsourcing security operations to a specialized provider, organizations can benefit from expert cybersecurity services without the overhead costs associated with hiring and training dedicated security personnel. This approach proves particularly advantageous for small and medium-sized businesses seeking robust security solutions within a budget-friendly framework.

Expertise of cybersecurity professionals

The expertise of cybersecurity professionals is a significant advantage of managed security services. These professionals are highly trained and experienced in identifying, mitigating, and responding to a wide range of cyber threats. By leveraging the knowledge and skills of these experts, organizations can enhance their security posture and stay ahead of evolving cyber risks. The specialized expertise of cybersecurity professionals within managed security services ensures that organizations receive proactive and effective protection against potential security breaches, ultimately safeguarding their sensitive data and IT infrastructure.

Quick incident response and threat detection

Quick incident response and threat detection are key benefits of managed security services. By outsourcing these functions to a specialized provider, organizations can leverage advanced tools and expertise to swiftly identify and address security incidents. This proactive approach helps minimize the impact of potential threats, reducing the risk of data breaches and downtime. With round-the-clock monitoring and real-time alerts, managed security services enable organizations to respond promptly to emerging threats, enhancing their overall cybersecurity posture.

Scalability to accommodate business growth

Managed Security Services offer the significant advantage of scalability to accommodate business growth. As organizations expand and evolve, their security needs also change. MSS providers can adjust their services and resources to meet the increasing demands of a growing business, ensuring that security measures remain effective and aligned with the organization’s evolving IT infrastructure. This flexibility allows businesses to scale up their security solutions seamlessly without compromising on protection or performance, providing peace of mind as they navigate through periods of expansion and transformation.

Compliance with industry standards and regulations

Ensuring compliance with industry standards and regulations is a significant advantage of managed security services. MSS providers have the expertise and resources to help organizations navigate the complex landscape of regulatory requirements, such as GDPR, HIPAA, or PCI DSS. By partnering with an MSS provider that is well-versed in these standards, businesses can mitigate the risk of non-compliance penalties, protect sensitive data, and maintain trust with their customers and stakeholders.

Cost

Managed security services can present a significant con in terms of cost, particularly for small businesses operating on limited budgets. The expense associated with outsourcing security operations to a managed service provider can sometimes be prohibitive for smaller organizations. This financial burden may pose a challenge for businesses looking to enhance their cybersecurity posture but facing constraints in allocating resources to manage security effectively. As a result, small businesses may need to carefully weigh the costs and benefits of engaging managed security services to ensure that their investment aligns with their overall security needs and financial capabilities.

Dependency

Relying on an external provider for security, as is the case with Managed Security Services, can introduce a significant con in the form of dependency. Organizations may feel a loss of control over their security measures and operations, as they are entrusting a third-party provider to safeguard their sensitive data and IT infrastructure. This dependency on an external entity can lead to concerns about responsiveness, customization, and decision-making autonomy in addressing security incidents and implementing tailored security solutions that align closely with the organization’s specific needs and risk profile.

Integration Challenges

Integrating managed security services with existing IT systems and processes can pose a significant challenge for organizations. The complexity and time-consuming nature of this integration process can disrupt operations and require careful planning and coordination. Ensuring seamless compatibility between the managed security services and the existing infrastructure is crucial to avoid potential conflicts or gaps in security coverage. Organizations must allocate resources and expertise to effectively navigate these integration challenges to fully leverage the benefits of managed security services while minimizing disruptions to their IT environment.

Limited Customization

Some MSS providers present a con in the form of limited customization, as they may provide standardized solutions that do not entirely align with the specific security requirements of an organization. This lack of customization can result in gaps in security coverage and leave certain aspects of an organization’s IT infrastructure vulnerable to potential threats. Organizations seeking tailored security measures may find themselves constrained by the off-the-shelf nature of some managed security services, necessitating a careful evaluation of provider capabilities to ensure comprehensive protection against evolving cyber risks.

Response Time

Delays in response time from Managed Security Services (MSS) providers can pose a significant challenge for organizations relying on swift incident response and threat mitigation. When incidents occur, every moment is crucial in containing the potential damage and minimizing risks. A delayed response can allow threats to escalate, leading to more severe consequences for the organization’s security posture. It is essential for organizations to carefully evaluate the responsiveness and service level agreements of MSS providers to ensure timely and effective incident management.

Data Privacy Concerns

Entrusting sensitive data to a third-party provider raises concerns about data privacy and confidentiality. Organizations may worry about the security measures implemented by the managed security services provider to safeguard their data from unauthorized access or breaches. The potential risk of data exposure or misuse can be a significant deterrent for businesses, especially those operating in highly regulated industries where compliance with strict data protection laws is paramount. Data privacy concerns highlight the importance of thorough vetting and due diligence when selecting a managed security services provider to ensure that data remains secure and protected at all times.

Regulatory Compliance Risks

One significant con of managed security services is the regulatory compliance risks associated with them. Organizations need to meticulously verify that their MSS provider adheres to all relevant regulations and standards to mitigate the potential compliance risks and penalties. Failure to ensure compliance with data protection laws and industry regulations could lead to severe consequences, including legal actions, fines, and reputational damage for the organization. It is crucial for businesses to thoroughly assess the regulatory compliance practices of their MSS provider before entrusting them with the security of sensitive data and IT infrastructure.

cyber security audit

Maximizing Security: The Essential Cyber Security Audit Process

The Importance of Cyber Security Audit

The Importance of Cyber Security Audit

In today’s digital age, where businesses rely heavily on technology to operate efficiently, the importance of cyber security cannot be overstated. Cyber attacks are becoming increasingly sophisticated, and organizations need to be proactive in safeguarding their data and systems.

A cyber security audit is a crucial step in assessing an organization’s security posture. It involves evaluating existing security measures, identifying vulnerabilities, and recommending improvements to enhance overall security.

Key Benefits of Cyber Security Audit:

  • Identifying Weaknesses: A cyber security audit helps uncover vulnerabilities in the organization’s network, systems, and processes that could be exploited by malicious actors.
  • Risk Assessment: By conducting an audit, organizations can assess the level of risk they face from potential cyber threats and prioritize mitigation efforts accordingly.
  • Compliance: Many industries have regulatory requirements for data protection. A cyber security audit ensures that the organization is compliant with relevant laws and standards.
  • Enhanced Protection: Implementing recommendations from a cyber security audit strengthens the organization’s defenses against cyber attacks and reduces the likelihood of a successful breach.
  • Awareness and Training: Audits can also highlight areas where employees may need additional training on best practices for maintaining a secure environment.

It is essential for organizations to conduct regular cyber security audits to stay ahead of emerging threats and protect sensitive information. By investing in proactive security measures, businesses can minimize the risk of data breaches and maintain trust with customers and stakeholders.

Remember, when it comes to cyber security, prevention is always better than cure. Stay vigilant, stay secure!


7 Essential Tips for a Comprehensive Cybersecurity Audit

  1. Regularly review and update security policies and procedures.
  2. Conduct vulnerability assessments to identify potential weaknesses.
  3. Implement strong access controls to protect sensitive data.
  4. Monitor network activity for any signs of unauthorized access.
  5. Train employees on cybersecurity best practices and awareness.
  6. Backup data regularly to prevent data loss in case of a breach.
  7. Engage with third-party experts for independent security audits.

Regularly review and update security policies and procedures.

It is crucial for organizations to regularly review and update their security policies and procedures as part of a comprehensive cyber security audit. By staying current with evolving threats and industry best practices, companies can ensure that their security measures remain effective and aligned with the latest standards. Updating policies and procedures allows businesses to address new vulnerabilities, strengthen defenses, and enhance overall resilience against cyber attacks. Consistent review and updates demonstrate a commitment to maintaining a robust security posture and safeguarding sensitive data from potential breaches.

Conduct vulnerability assessments to identify potential weaknesses.

To enhance the effectiveness of a cyber security audit, it is essential to conduct vulnerability assessments to identify potential weaknesses within an organization’s network, systems, and processes. By proactively seeking out vulnerabilities, businesses can prioritize remediation efforts and strengthen their overall security posture. Vulnerability assessments play a crucial role in mitigating risks and preventing potential cyber threats from exploiting weaknesses in the infrastructure.

Implement strong access controls to protect sensitive data.

To enhance the security of sensitive data during a cyber security audit, it is crucial to implement strong access controls. By restricting access to authorized personnel only, organizations can prevent unauthorized users from compromising sensitive information. Strong access controls include implementing multi-factor authentication, role-based access permissions, and regular monitoring of user activity to detect any suspicious behavior. These measures not only protect valuable data but also contribute to a robust security posture that safeguards against potential cyber threats.

Monitor network activity for any signs of unauthorized access.

Monitoring network activity for any signs of unauthorized access is a crucial tip in ensuring effective cyber security. By actively tracking and analyzing network traffic, organizations can quickly detect any unusual or suspicious behavior that may indicate a potential security breach. Identifying unauthorized access early allows for prompt response and mitigation measures to prevent data loss or system compromise. Continuous monitoring of network activity is essential in maintaining a secure environment and safeguarding sensitive information from cyber threats.

Train employees on cybersecurity best practices and awareness.

Training employees on cybersecurity best practices and raising awareness about potential cyber threats are essential components of a comprehensive cyber security audit. By educating staff members on how to identify phishing attempts, create strong passwords, and recognize suspicious activities, organizations can significantly reduce the risk of data breaches and cyber attacks. An informed workforce serves as an additional layer of defense against evolving threats in the digital landscape, ultimately contributing to a more secure and resilient business environment.

Backup data regularly to prevent data loss in case of a breach.

Regularly backing up your data is a crucial practice in cyber security to mitigate the risk of data loss in the event of a breach. By maintaining up-to-date backups of your important information, you can ensure that even if your systems are compromised, you have a secure copy of your data that can be restored. This proactive measure not only helps in recovery efforts but also provides peace of mind knowing that your valuable data is safeguarded against potential cyber threats.

Engage with third-party experts for independent security audits.

Engaging with third-party experts for independent security audits is a valuable tip in ensuring the thoroughness and objectivity of your cyber security assessment. By bringing in external specialists who possess a fresh perspective and specialized knowledge, organizations can uncover blind spots, identify vulnerabilities, and receive unbiased recommendations to enhance their overall security posture. Third-party experts can offer insights that internal teams may overlook, providing a comprehensive evaluation that strengthens defenses against potential cyber threats. Collaborating with independent auditors demonstrates a commitment to proactive risk management and underscores the importance of prioritizing cybersecurity in today’s digital landscape.

best cyber security consulting companies

Top Cyber Security Consulting Companies: Safeguarding Your Digital Assets

Top Cyber Security Consulting Companies

The Best Cyber Security Consulting Companies in the Industry

In today’s digital age, cyber security is more important than ever. With cyber threats on the rise, businesses and organizations need to ensure that their sensitive data and systems are protected. This is where cyber security consulting companies play a crucial role.

Accenture Security

Accenture Security is a global leader in cyber security consulting, offering a wide range of services to help businesses strengthen their security posture. With a team of experts and innovative solutions, Accenture Security is trusted by many top companies worldwide.

Deloitte Cyber Risk Services

Deloitte Cyber Risk Services provides comprehensive cyber security consulting services to help organizations identify and mitigate risks. Their team of professionals offers strategic guidance and practical solutions to enhance cyber resilience.

IBM Security Services

IBM Security Services is known for its cutting-edge technologies and deep expertise in cyber security. They offer a holistic approach to cyber defense, helping clients detect, respond to, and recover from cyber attacks effectively.

KPMG Cyber Security Services

KPMG Cyber Security Services delivers tailored solutions to address the unique security challenges faced by organizations. Their team of consultants combines industry knowledge with technical skills to provide top-notch cyber security services.

PwC Cybersecurity and Privacy

PwC’s Cybersecurity and Privacy practice offers a range of services to help clients protect their digital assets and data. With a focus on innovation and collaboration, PwC helps organizations build resilient cyber security strategies.

These are just a few of the best cyber security consulting companies that are leading the way in protecting businesses from evolving cyber threats. By partnering with these reputable firms, organizations can ensure that they have the expertise and resources needed to safeguard their digital assets.


Top FAQs About Choosing the Best Cyber Security Consulting Companies

  1. What services do cyber security consulting companies offer?
  2. How do I choose the best cyber security consulting company for my business?
  3. What are the key factors to consider when selecting a cyber security consulting firm?
  4. How can cyber security consulting companies help improve my organization’s security posture?
  5. Do cyber security consulting companies provide ongoing support and monitoring services?
  6. What sets top cyber security consulting companies apart from others in the industry?

What services do cyber security consulting companies offer?

Cyber security consulting companies offer a wide range of services to help businesses and organizations enhance their security posture and protect their sensitive data and systems. These services typically include risk assessments, vulnerability assessments, penetration testing, incident response planning, security architecture design, compliance management, security awareness training, and managed security services. By leveraging the expertise of cyber security consulting companies, clients can identify and mitigate potential risks, strengthen their defenses against cyber threats, and ensure regulatory compliance in an increasingly complex digital landscape.

How do I choose the best cyber security consulting company for my business?

When selecting the best cyber security consulting company for your business, it is crucial to consider several key factors. First and foremost, assess the company’s reputation and track record in the industry. Look for firms with a proven history of successful cyber security projects and satisfied clients. Additionally, evaluate the expertise and qualifications of their team members to ensure they have the necessary skills to address your specific needs. Consider the range of services offered by the consulting company and whether they align with your business requirements. Lastly, prioritize clear communication and transparency throughout the engagement process to establish a strong partnership built on trust and collaboration. By carefully evaluating these aspects, you can choose a cyber security consulting company that will effectively safeguard your business against potential threats.

What are the key factors to consider when selecting a cyber security consulting firm?

When selecting a cyber security consulting firm, several key factors should be considered to ensure that you choose the right partner to protect your organization’s digital assets. Firstly, expertise and experience play a crucial role – look for a firm with a proven track record in handling cyber security challenges effectively. Additionally, consider the range of services offered by the consulting firm and whether they align with your specific needs. Transparency, communication, and responsiveness are also essential factors to evaluate, as clear communication and prompt support are vital in addressing cyber threats swiftly. Lastly, assess the firm’s reputation, client testimonials, and industry certifications to gauge their reliability and credibility in the cyber security landscape. By carefully considering these factors, you can make an informed decision when selecting a cyber security consulting firm that best meets your organization’s requirements.

How can cyber security consulting companies help improve my organization’s security posture?

Cyber security consulting companies play a crucial role in enhancing an organization’s security posture by providing expert guidance, tailored solutions, and strategic advice. These companies conduct thorough assessments of the organization’s existing security measures, identify vulnerabilities and potential risks, and develop customized strategies to address them effectively. By leveraging their deep expertise and industry knowledge, cyber security consulting firms can help organizations implement robust security controls, enhance incident response capabilities, and stay ahead of emerging cyber threats. Through proactive monitoring, training programs, and continuous support, these companies empower organizations to strengthen their defenses and mitigate the impact of potential cyber attacks, ultimately safeguarding sensitive data and preserving business continuity.

Do cyber security consulting companies provide ongoing support and monitoring services?

When it comes to cyber security consulting companies, many of them offer ongoing support and monitoring services to ensure the continuous protection of their clients’ systems and data. These services often include real-time monitoring of network activities, threat detection, incident response, and regular security assessments to identify vulnerabilities. By providing ongoing support and monitoring, cyber security consulting companies help organizations stay ahead of potential threats and respond promptly to any security incidents that may arise. This proactive approach is essential in today’s dynamic cyber threat landscape to maintain a strong security posture and mitigate risks effectively.

What sets top cyber security consulting companies apart from others in the industry?

When it comes to distinguishing the top cyber security consulting companies from others in the industry, several key factors come into play. Firstly, top firms often boast a team of seasoned professionals with extensive experience and expertise in the field, allowing them to provide strategic insights and innovative solutions tailored to each client’s unique needs. Additionally, leading cyber security consulting companies stay ahead of emerging threats and trends by investing in cutting-edge technologies and continuous training for their staff. Their commitment to excellence, proactive approach to risk management, and ability to deliver measurable results set them apart as trusted partners in safeguarding organizations’ digital assets effectively.

owasp sdlc

Enhancing Software Security: A Guide to OWASP Secure Development Lifecycle (SDL)

Understanding OWASP Secure Development Lifecycle (SDL)

Understanding OWASP Secure Development Lifecycle (SDL)

The Open Web Application Security Project (OWASP) is a non-profit organization dedicated to improving the security of software. One of the key initiatives by OWASP is the Secure Development Lifecycle (SDL), which aims to integrate security practices into every phase of the software development process.

Key Principles of OWASP SDL:

  • Start Early: Security considerations should be addressed from the beginning of the development process.
  • Risk-Based Approach: Identify and prioritize security risks based on their potential impact.
  • Continuous Monitoring: Implement mechanisms to continuously monitor and assess security throughout the development lifecycle.
  • Educate and Train: Provide training to developers on secure coding practices and common vulnerabilities.

Phases of OWASP SDL:

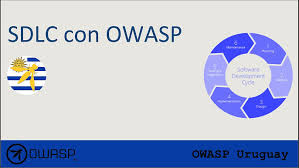
The OWASP SDL consists of several phases that guide developers in building secure software:

  1. Requirements: Define security requirements and constraints early in the project.
  2. Design: Incorporate security controls into the design phase to mitigate potential vulnerabilities.
  3. Implementation: Follow secure coding practices and conduct code reviews to identify and fix security issues.
  4. Testing: Perform thorough security testing, including penetration testing and vulnerability assessments, to identify weaknesses.
  5. Release/Deployment: Ensure that security controls are in place before deploying the application to production environments.
  6. Maintenance: Continuously monitor and update the application to address new security threats and vulnerabilities.

Benefits of OWASP SDL:

The implementation of OWASP SDL offers several benefits, including:

  • Better Security Posture: By integrating security from the start, developers can build more secure applications.
  • Cost Savings: Addressing security issues early in the development process can help prevent costly fixes later on.
  • Mitigation of Risks: Identifying and addressing vulnerabilities proactively reduces the risk of data breaches and cyber attacks.

In conclusion, adopting OWASP SDL principles can significantly enhance the security of software applications. By following a structured approach that incorporates security throughout the development lifecycle, organizations can build more resilient and secure systems that protect both their data and users.


Understanding OWASP Secure Development Lifecycle (SDL): Key FAQs and Insights

  1. What is OWASP Secure Development Lifecycle (SDL)?
  2. Why is OWASP SDL important in software development?
  3. What are the key principles of OWASP SDL?
  4. How does OWASP SDL help improve software security?
  5. What are the phases of OWASP SDL and their significance?
  6. How can developers integrate security practices into each phase of the SDLC?
  7. What are the benefits of implementing OWASP SDL in an organization?
  8. Are there any tools or resources available to support the implementation of OWASP SDL?

What is OWASP Secure Development Lifecycle (SDL)?

The OWASP Secure Development Lifecycle (SDL) is a structured approach designed by the Open Web Application Security Project (OWASP) to integrate security practices into every phase of the software development process. It aims to address security considerations from the early stages of development, prioritize and mitigate risks, continuously monitor security, and educate developers on secure coding practices. By following the OWASP SDL guidelines, organizations can build more secure software applications that are resilient against potential vulnerabilities and cyber threats.

Why is OWASP SDL important in software development?

The OWASP Secure Development Lifecycle (SDL) is crucial in software development because it integrates security practices at every stage of the development process. By prioritizing security from the beginning, OWASP SDL helps identify and mitigate potential vulnerabilities early on, reducing the risk of security breaches and data leaks. Incorporating security measures throughout the software development lifecycle not only enhances the overall security posture of applications but also saves time and resources by addressing issues proactively. OWASP SDL ensures that developers are well-equipped to build secure software that can withstand evolving cyber threats, ultimately safeguarding sensitive data and maintaining user trust.

What are the key principles of OWASP SDL?

One of the frequently asked questions about OWASP SDL revolves around its key principles. The key principles of OWASP Secure Development Lifecycle (SDL) emphasize starting early with security considerations, adopting a risk-based approach to prioritize vulnerabilities, implementing continuous monitoring mechanisms, and providing education and training to developers on secure coding practices and common vulnerabilities. By adhering to these principles, organizations can integrate security practices into every phase of the software development process, ultimately enhancing the security posture of their applications and mitigating potential risks effectively.

How does OWASP SDL help improve software security?

The OWASP Secure Development Lifecycle (SDL) plays a crucial role in enhancing software security by integrating security practices into every phase of the software development process. OWASP SDL helps improve software security by ensuring that security considerations are addressed from the early stages of development, identifying and prioritizing security risks based on their potential impact, implementing continuous monitoring mechanisms to assess security throughout the lifecycle, providing education and training on secure coding practices, and guiding developers through a structured approach that incorporates security controls into design, implementation, testing, release/deployment, and maintenance phases. By following OWASP SDL principles, organizations can build more secure applications, reduce vulnerabilities, mitigate risks of data breaches and cyber attacks, and ultimately enhance the overall security posture of their software products.

What are the phases of OWASP SDL and their significance?

The phases of OWASP Secure Development Lifecycle (SDL) play a crucial role in ensuring the security of software applications. Each phase, including requirements, design, implementation, testing, release/deployment, and maintenance, has its own significance in integrating security practices throughout the development process. By defining security requirements early on, incorporating security controls into the design phase, following secure coding practices during implementation, conducting thorough security testing, ensuring secure deployment, and maintaining ongoing security measures post-launch, organizations can build robust and resilient applications that are better protected against potential cyber threats. Embracing these phases helps developers identify and address security vulnerabilities proactively, ultimately leading to safer software products for users.

How can developers integrate security practices into each phase of the SDLC?

Developers can integrate security practices into each phase of the Software Development Lifecycle (SDLC) by following a structured approach outlined by OWASP SDL principles. Starting from the requirements phase, developers can define security requirements early on and incorporate security controls into the design phase to mitigate potential vulnerabilities. During implementation, following secure coding practices and conducting code reviews help identify and fix security issues. Thorough security testing, including penetration testing and vulnerability assessments, in the testing phase ensures that weaknesses are identified before deployment. By continuously monitoring and updating the application in the maintenance phase, developers can address new security threats and vulnerabilities effectively. This holistic approach ensures that security is ingrained in every aspect of the SDLC, leading to the development of more secure and resilient software applications.

What are the benefits of implementing OWASP SDL in an organization?

Implementing the OWASP Secure Development Lifecycle (SDL) in an organization offers a multitude of benefits. By integrating security practices from the early stages of software development, organizations can enhance their overall security posture. This proactive approach helps in identifying and addressing vulnerabilities before they become significant risks, ultimately leading to a reduction in potential data breaches and cyber attacks. Additionally, implementing OWASP SDL can result in cost savings by preventing expensive fixes that may be required if security issues are discovered later in the development process. Overall, embracing OWASP SDL principles can help organizations build more secure and resilient software applications that protect both their data and their reputation.

Are there any tools or resources available to support the implementation of OWASP SDL?

Many tools and resources are available to support the implementation of OWASP Secure Development Lifecycle (SDL). The OWASP community provides a variety of open-source tools, guidelines, and best practices that can help developers integrate security into their development processes. Tools such as OWASP ZAP (Zed Attack Proxy), Dependency-Check, and Code Dx offer functionalities for vulnerability scanning, dependency analysis, and code review to identify and address security issues early on. Additionally, OWASP provides comprehensive documentation, training materials, and reference guides to assist organizations in implementing SDL effectively. By leveraging these tools and resources, developers can enhance the security of their software applications and mitigate potential risks associated with vulnerabilities.