cfchris.com

Loading

software engineering practice

Software Engineering Practice: Principles for Building Better Software

Software Engineering Practice: Building Better Software, Together

Software engineering is more than writing code. It is the disciplined practice of understanding a problem, designing a solution, building and testing it, and improving it over time. Strong engineering practices help teams create software that is reliable, secure, maintainable, and useful to the people who depend on it.

Start with the Problem

Successful software begins with a clear understanding of what needs to be solved. Before choosing a framework or writing code, teams should identify users, requirements, constraints, and measures of success. Conversations with stakeholders and users can reveal important details that a brief feature request may leave out.

Requirements should be specific enough to guide implementation while remaining open to change as new information emerges. Breaking large goals into smaller, testable outcomes makes progress easier to plan and evaluate.

Design for Clarity and Change

Good design helps developers understand how a system works and where changes belong. Clear boundaries between components can limit unintended side effects and make the software easier to test. Designs should address real needs without adding unnecessary complexity.

Because requirements and technologies change, flexibility matters. A well-structured system makes reasonable changes straightforward, but it does not try to predict every possible future scenario. The best design is often the simplest one that meets current needs and leaves room for informed growth.

Write Readable, Maintainable Code

Code is read and revised far more often than it is initially written. Meaningful names, consistent formatting, focused functions, and concise documentation make a codebase easier to understand. These habits reduce the effort required to fix defects, add features, and bring new developers onto a project.

Maintainable code does not mean avoiding all complexity. Some problems are inherently complex. The goal is to make that complexity visible and manageable rather than hiding it behind unclear abstractions or overly clever implementations.

Test at Multiple Levels

Testing helps teams find problems before they reach users. Different kinds of tests serve different purposes:

  • Unit tests check small pieces of behavior, such as individual functions or components.
  • Integration tests verify that connected parts of a system work together.
  • End-to-end tests exercise important user workflows across the application.
  • Exploratory testing helps uncover issues that scripted tests may miss.

Tests are most useful when they are reliable, focused, and run regularly. A test suite should provide confidence, not create so much noise that teams learn to ignore failures.

Use Version Control and Code Review

Version control records how software changes over time and gives teams a safe way to collaborate. Small, focused changes are generally easier to review, test, and troubleshoot than large batches of unrelated work.

Code review adds another perspective before a change is merged. Reviewers can check correctness, readability, security, and consistency with the project’s design. Effective reviews are constructive and specific, with an emphasis on improving the code rather than criticizing the person who wrote it.

Automate Repetitive Work

Automation can make routine engineering tasks faster and more consistent. Continuous integration systems can build software and run tests whenever changes are submitted. Deployment automation can reduce manual steps and help teams release updates more safely.

Automation should be introduced thoughtfully. A process that is difficult to understand or maintain can become a source of delays. Teams should automate repeatable tasks while keeping the resulting workflows visible and understandable.

Build Security and Reliability In

Security is not a final checklist item; it is part of the entire development process. Teams should protect sensitive data, validate inputs, manage dependencies, use appropriate access controls, and keep software updated. Threat modeling and security reviews can help identify risks early, when they are often less expensive to address.

Reliability also requires preparation for failure. Monitoring, useful logs, backups, recovery plans, and clear incident procedures help teams detect problems and respond effectively. Designing for failure does not mean expecting every component to break. It means understanding what could go wrong and reducing the impact.

Communicate and Learn as a Team

Software development is collaborative work. Developers, designers, product managers, quality specialists, and operations teams benefit from shared goals and clear communication. Documentation, design discussions, and regular feedback help prevent misunderstandings from becoming expensive rework.

When a defect or incident occurs, a blameless review can help the team understand contributing factors and improve the system. The purpose is to learn and prevent recurrence, not to assign personal fault.

Improve Practices Over Time

No single process works equally well for every team or project. Effective engineering practices evolve through experience. Teams can review delivery bottlenecks, recurring defects, customer feedback, and maintenance costs to decide where to improve.

The aim is not to follow every trend or adopt the largest possible toolset. It is to create a sustainable way of working that helps people deliver valuable software with confidence. Clear requirements, thoughtful design, readable code, meaningful tests, responsible security, and open collaboration provide a strong foundation for that work.


8 Best Practices for Better Software Engineering

  1. Write small, focused functions.
  2. Use clear, consistent names.
  3. Review code before merging.
  4. Add tests for important behavior.
  5. Automate repetitive checks.
  6. Keep dependencies up to date.
  7. Document tricky decisions.
  8. Fix root causes, not symptoms.

Write small, focused functions.

Write small, focused functions, with each function responsible for one clear task. This makes code easier to read, test, debug, and reuse because the function’s purpose and behavior are easier to understand. When a function starts handling several unrelated responsibilities or grows difficult to follow, consider breaking it into smaller pieces with clear names. Keep functions focused without splitting them into so many tiny parts that the overall flow becomes harder to see.

Use clear, consistent names.

Use clear, consistent names to make code easier to read, understand, and maintain. Choose names that describe a variable’s purpose, a function’s behavior, or a class’s role, and follow the same naming conventions throughout the project. Avoid vague abbreviations and overly clever names that make readers guess what the code does. A few extra characters in a meaningful name can save teammates time and help prevent mistakes.

Review code before merging.

Review code before merging to catch bugs, improve clarity, and ensure changes fit the project’s standards. A thoughtful review also shares knowledge across the team and can reveal security or reliability concerns before they reach users. Keep changes small, give specific and respectful feedback, and focus on improving the code—not criticizing the person who wrote it.

Add tests for important behavior.

Add tests for important behavior to make sure your software continues to do what users and other parts of the system rely on. Focus first on critical workflows, business rules, edge cases, and areas where bugs could cause significant problems. Well-chosen tests catch regressions early, make changes safer, and document how the software is expected to work. Keep tests clear, reliable, and easy to run so they remain a practical part of everyday development.

Automate repetitive checks.

Automate repetitive checks to catch common problems early and give the team more time to focus on meaningful engineering work. For example, configure tools to run tests, check code formatting, scan for security issues, and validate builds whenever changes are submitted. Keep these checks fast, reliable, and easy to understand so developers can act on results without unnecessary delays. Automation supports consistent quality, but it works best alongside thoughtful code review and human judgment.

Keep dependencies up to date.

Keep dependencies up to date to benefit from security fixes, bug patches, and improvements from the maintainers. Regularly review your project’s libraries and tools, check release notes for breaking changes, and upgrade in small, manageable steps. Automated vulnerability alerts and dependency-update tools can help identify what needs attention, but every update should still be tested to confirm it works with your application.

Document tricky decisions.

Document tricky decisions by recording what was chosen, why it was chosen, and which alternatives were considered. A short note can preserve important context that might otherwise be lost as team members or project requirements change. This helps future developers understand the reasoning behind the design, avoid reopening settled debates, and make better decisions when the original constraints no longer apply.

Fix root causes, not symptoms.

Fixing root causes—not just symptoms—helps prevent the same problem from returning. When a bug or outage occurs, take time to investigate why it happened, using evidence such as logs, tests, and recent code changes. A quick patch may restore service, but addressing the underlying issue—such as unclear requirements, missing validation, or a fragile system design—leads to more reliable software and saves time in the long run.
best cybersecurity consulting firms

Best Cybersecurity Consulting Firms: How to Choose the Right Partner

Best Cybersecurity Consulting Firms: How to Choose the Right Partner

Cybersecurity consulting firms help organizations identify risks, strengthen defenses, respond to incidents, and meet regulatory requirements. The best firm for one company may not be the best fit for another: a global enterprise may need a large team with broad capabilities, while a growing business may prefer a specialist with focused expertise and flexible services.

This guide highlights established cybersecurity consulting firms and explains what to consider when comparing them. It is not a universal ranking; services, availability, and areas of expertise can change, so verify current offerings directly with each provider.

Cybersecurity Consulting Firms to Consider

Accenture Security

Accenture Security provides cybersecurity strategy, risk management, identity and access management, cloud security, and incident response services. Its global reach and broad technology consulting capabilities may suit large organizations managing complex environments or major security transformation projects.

Deloitte

Deloitte offers cybersecurity consulting across areas such as security strategy, cyber risk, privacy, identity management, cloud security, and incident readiness. Organizations that want cybersecurity services connected to broader risk, compliance, or business transformation work may consider Deloitte.

IBM Consulting

IBM Consulting works with organizations on security strategy, threat management, cloud security, identity, and incident response. Its experience with enterprise technology environments can be useful for companies seeking to coordinate cybersecurity improvements across a wide range of systems.

Mandiant, part of Google Cloud

Mandiant is known for threat intelligence, incident response, and investigations. It may be a strong option for organizations that need help responding to a significant security incident, understanding attacker activity, or improving defenses based on real-world threat information.

NCC Group

NCC Group provides services that include penetration testing, security assessments, incident response, and advisory work. Its specialist security focus may appeal to organizations looking for technical testing and independent insight into vulnerabilities and resilience.

Bishop Fox

Bishop Fox specializes in offensive security, including penetration testing, red teaming, and attack surface assessments. It may be a good fit for organizations that want to test how well their systems and security teams stand up to realistic attack techniques.

Kroll

Kroll offers cyber risk, incident response, digital forensics, and investigative services. Its combination of technical and investigative capabilities can be relevant when an organization needs to understand the scope, cause, and business impact of a cyber incident.

Coalfire

Coalfire focuses on cybersecurity and compliance services, including assessments, cloud security, penetration testing, and support for certain regulatory and industry frameworks. It may suit organizations that need to connect security improvements with compliance goals.

Optiv

Optiv provides cybersecurity consulting and related services, including strategy, risk management, implementation, and managed security offerings. Organizations looking for help evaluating and coordinating security technologies may find its broad, vendor-focused approach useful.

What Makes a Cybersecurity Consulting Firm “Best”?

A strong provider should match your organization’s specific needs, not simply offer the longest service list. Compare firms based on:

  • Relevant expertise: Look for experience with your industry, technology stack, organization size, and security challenges.
  • Scope of services: Decide whether you need strategy, technical testing, compliance support, incident response, implementation, or ongoing monitoring.
  • Incident response readiness: If response support is important, clarify availability, escalation procedures, and how quickly the firm can begin work.
  • Team qualifications: Ask who will do the work, what experience they bring, and whether specialized skills or certifications are relevant to your project.
  • Independence and conflicts: Understand whether the firm also sells or implements security products it may recommend.
  • Communication and reporting: Look for clear findings, prioritized recommendations, and practical guidance your team can act on.
  • Pricing and scope: Compare proposals carefully. Confirm deliverables, assumptions, timelines, and any fees for work outside the agreed scope.
  • References and results: Ask for relevant client references or examples of similar work, while respecting confidentiality requirements.

How to Choose the Right Firm

  1. Define the problem. Specify the outcome you need, such as a penetration test, incident response plan, cloud security review, or company-wide security strategy.
  2. Set priorities and constraints. Consider budget, deadlines, compliance obligations, locations, and the internal resources available to act on recommendations.
  3. Shortlist firms with relevant experience. Request proposals from providers that can demonstrate expertise in your particular area.
  4. Compare proposals consistently. Use the same requirements for each firm, and compare deliverables and methodology—not just price.
  5. Agree on measures of success. Establish how progress, findings, remediation, and knowledge transfer will be documented.

Questions to Ask Before Hiring a Cybersecurity Consultant

  • Have you handled projects similar to ours?
  • Who will perform the work, and who will be our main point of contact?
  • What information or access will you need?
  • How will you protect sensitive data during the engagement?
  • What will we receive at the end of the project?
  • Will you help prioritize or validate remediation work?
  • How do you handle urgent findings or an active incident?
  • What is not included in the proposed scope?

Frequently Asked Questions

How much do cybersecurity consulting services cost?

Costs vary based on the project’s scope, complexity, duration, and required expertise. A defined assessment may have a fixed fee, while broader advisory or incident response work may be priced differently. Request a detailed scope and confirm how additional work will be billed.

Should a small business hire a large consulting firm?

Not necessarily. A small business may benefit from a specialist or regional provider with experience supporting organizations of a similar size. The key is finding a firm that can deliver the needed expertise at an appropriate level of cost and complexity.

Is a cybersecurity consultant the same as a managed security provider?

No. A consultant typically provides defined advisory, assessment, testing, or response services. A managed security provider generally operates or monitors security services on an ongoing basis. Some firms offer both, so confirm exactly what is included.

Conclusion

The best cybersecurity consulting firm is the one that understands your risks, fits your environment, and provides clear recommendations your organization can implement. Compare providers on relevant experience, service scope, communication, independence, and measurable deliverables. A careful selection process can help turn cybersecurity spending into practical improvements in resilience.


Top Benefits of Hiring Leading Cybersecurity Consulting Firms

  1. Expert guidance to identify and reduce security risks
  2. Independent assessments of systems and defenses
  3. Specialized support for incident response
  4. Help meeting industry and regulatory requirements
  5. Practical recommendations tailored to business needs
  6. Access to experienced cybersecurity professionals


Considerations When Choosing Top Cybersecurity Consulting Firms: Balancing Cost, Expertise, Tools, and Operational Impact

  1. Services can be expensive.
  2. Expertise varies by firm.
  3. Recommendations may require costly tools.
  4. Remediation can disrupt operations.

Expert guidance to identify and reduce security risks

One of the biggest advantages of working with a top cybersecurity consulting firm is access to expert guidance for identifying and reducing security risks. Experienced consultants assess your systems, policies, and processes to uncover vulnerabilities that may be difficult to spot internally. They then help prioritize the most significant threats and recommend practical steps to strengthen defenses, protect sensitive data, and reduce the likelihood and impact of a cyberattack.

Independent assessments of systems and defenses

Independent assessments give organizations an objective view of how well their systems and defenses stand up to real-world threats. A cybersecurity consulting firm can identify vulnerabilities, gaps in security controls, and risks that internal teams may overlook, then explain which issues deserve attention first. Because the assessment comes from an outside perspective, it can also help leaders make informed decisions, prioritize improvements, and build greater confidence in their security program.

Specialized support for incident response

Specialized support for incident response: The best cybersecurity consulting firms can provide experienced specialists when a security incident occurs. They can help contain the threat, investigate how attackers gained access, assess which systems or data may be affected, and guide recovery efforts. Their expertise can help organizations make informed decisions under pressure, limit disruption, and strengthen defenses to reduce the risk of similar incidents in the future.

Help meeting industry and regulatory requirements

Experienced cybersecurity consulting firms can help organizations understand and meet the security requirements that apply to their industry and operations. They can assess current policies and controls, identify compliance gaps, and recommend practical steps to address standards and regulations such as HIPAA, PCI DSS, or applicable privacy laws. This support can make audits more manageable, strengthen the protection of sensitive information, and help organizations maintain compliance as requirements change. A consultant can guide the process, but responsibility for meeting regulatory obligations remains with the organization.

Practical recommendations tailored to business needs

One of the key advantages of the best cybersecurity consulting firms is their ability to provide practical recommendations tailored to a business’s needs. Rather than offering generic advice, experienced consultants consider an organization’s size, industry, technology, budget, and risk tolerance. They then prioritize realistic steps—such as improving access controls, addressing critical vulnerabilities, or strengthening incident response—that fit the company’s resources and goals. This helps businesses focus on meaningful security improvements without disrupting day-to-day operations or overspending on unnecessary tools.

Access to experienced cybersecurity professionals

One of the biggest advantages of working with a top cybersecurity consulting firm is access to experienced professionals with specialized skills. These experts bring knowledge of current threats, security tools, industry standards, and proven practices that may be difficult or costly to maintain in-house. Their experience can help an organization uncover weaknesses, prioritize risks, and develop practical steps to strengthen its defenses.

Services can be expensive.

One drawback of working with top cybersecurity consulting firms is that their services can be expensive. Fees may rise with the complexity of an assessment, the level of expertise required, or the need for urgent support. For small businesses and organizations with limited budgets, these costs can make it harder to get help or leave less funding for implementing the recommended security improvements. Compare proposals, clarify what each fee includes, and prioritize the services that address your most important risks.

Expertise varies by firm.

Expertise varies widely from one cybersecurity consulting firm to another. Some specialize in areas such as incident response, penetration testing, cloud security, or regulatory compliance, while others offer broader services with less depth in a particular field. A firm’s reputation alone doesn’t guarantee it has the right experience for your organization’s industry, technology, or specific risks, so review its relevant qualifications, past projects, and proposed team before making a decision.

Recommendations may require costly tools.

One potential drawback of working with a cybersecurity consulting firm is that its recommendations may involve costly tools, software, or ongoing services. Even when a proposed solution addresses a real security need, licensing, implementation, training, and maintenance can add up—especially for small businesses with limited budgets. Ask consultants to explain the expected costs, identify lower-cost alternatives, and prioritize recommendations so your organization can address the most important risks first.

Remediation can disrupt operations.

One potential drawback of working with a cybersecurity consulting firm is that remediation can disrupt day-to-day operations. Applying security fixes may require system updates, configuration changes, temporary service outages, or changes to employee workflows. Without careful planning and coordination, these steps can interrupt business processes or affect customer access. Before remediation begins, agree on a schedule, assess the impact of proposed changes, and plan testing and rollback procedures to minimize disruption.

cyber services

Cyber Services: Protecting Your Business in a Connected World

Cyber Services: Protecting Your Business in a Connected World

Businesses rely on digital tools to communicate, serve customers, store information, and manage daily operations. That connectivity creates opportunity—but it also brings risks. Cyber services help organizations protect their systems, data, and people from online threats while preparing them to respond when problems occur.

What Are Cyber Services?

Cyber services are professional services designed to strengthen an organization’s cybersecurity. Depending on a business’s needs, they may include assessing security risks, monitoring networks, protecting accounts and devices, training employees, and responding to cyber incidents.

Cybersecurity is not a one-time project. Technology, business needs, and threats change over time, so effective protection requires ongoing attention and regular improvements.

Common Types of Cyber Services

Security Assessments

A security assessment reviews an organization’s systems, policies, and practices to identify weaknesses. The results can help prioritize improvements, such as updating software, tightening access controls, or creating stronger data-handling procedures.

Network and Endpoint Protection

Networks, computers, mobile devices, and servers can all be targets. Cyber services may help configure firewalls, endpoint protection, secure remote access, and other safeguards to reduce the chance that an attacker can enter or move through a system.

Identity and Access Management

Access controls help ensure that people can use only the information and systems required for their roles. Services in this area may include multi-factor authentication, account reviews, and policies for creating, changing, and removing user access.

Security Monitoring

Monitoring can help detect unusual activity, such as unexpected login attempts or suspicious changes to a system. Depending on the service, alerts may be reviewed around the clock or during specified business hours. Clear monitoring and escalation procedures help organizations respond more quickly to potential issues.

Employee Security Training

Employees play an important role in protecting an organization. Practical training can help them recognize phishing messages, use passwords safely, handle sensitive information, and report suspicious activity. Regular reminders and realistic examples can make security practices easier to apply in daily work.

Incident Response and Recovery

Even organizations with strong protections can experience a security incident. Incident response services help establish what to do, who should be involved, and how to contain and investigate an event. Recovery planning can also address backups, restoration procedures, and communication with affected parties.

Why Cyber Services Matter

A cyber incident can interrupt operations, expose private information, damage trust, and create unexpected costs. Cyber services can help reduce these risks by identifying vulnerabilities, improving defenses, and preparing teams to act. They can also support organizations that need to meet contractual, regulatory, or industry-specific security requirements.

No service can guarantee that an organization will never experience an attack. The goal is to make systems harder to compromise, detect problems sooner, and limit the impact if an incident occurs.

Choosing the Right Cyber Services

The right approach depends on an organization’s size, technology, data, budget, and risk tolerance. Before choosing a provider, consider:

  • Which systems and information need the most protection?
  • What security work is already handled internally?
  • How quickly will the provider respond to alerts or incidents?
  • What services are included, and what may cost extra?
  • How will progress and recommendations be reported?
  • Does the provider have experience with organizations of a similar size or type?

Ask for clear explanations of service scope, responsibilities, response times, and data handling. A useful provider should be able to explain risks and recommendations in plain language, not just provide technical reports.

Building a Stronger Security Program

Cyber services work best as part of a broader security program. Organizations can support that work by keeping software updated, using multi-factor authentication, limiting access to sensitive systems, maintaining reliable backups, and giving employees a clear way to report concerns. Regular reviews help ensure that protections keep pace with changes in the business.

With a thoughtful plan and the right expertise, cyber services can help an organization protect its operations, respond with confidence, and make informed decisions about technology and risk.


8 Essential Tips for Enhancing Your Cybersecurity Services

  1. Choose a trusted cybersecurity provider.
  2. Enable multifactor authentication.
  3. Keep software and services updated.
  4. Use strong, unique passwords.
  5. Back up important data regularly.
  6. Train staff to spot phishing.
  7. Review access permissions often.
  8. Check incident response plans regularly.

Choose a trusted cybersecurity provider.

Choosing a trusted cybersecurity provider is an important step in protecting your business. Look for a provider with relevant experience, clear service offerings, strong references, and a straightforward approach to explaining risks and recommendations. Before signing an agreement, ask about response times, data handling, and exactly what the services include. A reliable provider will take time to understand your needs and help you make informed security decisions.

Enable multifactor authentication.

Enable multifactor authentication (MFA) on your email, financial, cloud, and other important accounts. MFA requires a second form of verification—such as an authenticator app, security key, or one-time code—in addition to your password. This extra step can help prevent unauthorized access even if a password is stolen. For stronger protection, use an authenticator app or security key when available, and never share verification codes with anyone.

Keep software and services updated.

Keeping software and services updated is one of the simplest ways to strengthen cybersecurity. Updates often fix known security vulnerabilities that attackers could exploit, as well as improve reliability and performance. Turn on automatic updates when practical, and regularly check that operating systems, applications, plug-ins, and cloud services are current. For business-critical systems, plan updates carefully and verify that backups and recovery procedures are in place before making major changes.

Use strong, unique passwords.

Use strong, unique passwords for every account to make it harder for attackers to access your systems and sensitive information. A long passphrase made from several unrelated words can be easier to remember and tougher to guess than a short, complicated password. Avoid reusing passwords across work and personal accounts, and consider using a reputable password manager to create and store them securely. Enable multi-factor authentication whenever it’s available for an extra layer of protection.

Back up important data regularly.

Back up important data regularly to reduce the risk of losing files to hardware failure, accidental deletion, ransomware, or other disruptions. Use a reliable backup solution, keep copies separate from your main devices or network, and protect them with strong access controls. Test your backups periodically to make sure the data can be restored when you need it.

Train staff to spot phishing.

Train staff to spot phishing by teaching them to recognize common warning signs, such as unexpected attachments, urgent requests, unfamiliar sender addresses, and links that don’t match the message. Encourage employees to verify unusual requests through a separate trusted channel and report suspicious messages promptly. Regular, practical training helps make careful email habits part of everyday work and can reduce the risk of stolen credentials, malware, and data breaches.

Review access permissions often.

Review access permissions often to make sure employees and contractors can reach only the systems and information they need for their roles. Remove access promptly when someone changes jobs or leaves the organization, and disable unused accounts to reduce opportunities for unauthorized entry. Regular permission reviews can help catch outdated or excessive access before it becomes a security risk.

Check incident response plans regularly.

Check your incident response plans regularly to make sure they reflect your current systems, team members, and business needs. Review contact lists, roles, escalation steps, and recovery procedures, and update them whenever something changes. Practicing the plan with realistic scenarios can reveal gaps before an actual incident occurs, helping your team respond faster and reduce disruption.

microsoft cloud security

Microsoft Cloud Security: Essential Strategies for Protecting Your Data and Workloads

Microsoft Cloud Security: A Practical Guide

Microsoft cloud services—including Azure, Microsoft 365, and services built on the Microsoft cloud—offer organizations flexible ways to run applications, collaborate, and manage data. Protecting those environments takes more than turning on a security feature. It requires clear ownership, strong identity controls, thoughtful configuration, and ongoing monitoring.

Understand the Shared Responsibility Model

Cloud security is a shared responsibility between Microsoft and its customers. Microsoft secures the underlying cloud infrastructure, while customers remain responsible for areas such as user accounts, access permissions, data, and many service configurations. The exact division of responsibility depends on the service being used. For example, a managed software service generally requires less infrastructure management by the customer than a virtual machine running in Azure.

Before deploying a workload, identify what Microsoft manages and what your organization must secure. This helps prevent gaps in areas such as patching, backups, access control, and data protection.

Make Identity Your First Line of Defense

Compromised accounts are a common path into cloud environments, so identity protection should be a priority. Microsoft Entra ID provides identity and access management capabilities for Microsoft cloud services and other applications.

  • Require multifactor authentication, especially for administrators and remote access.
  • Use conditional access policies to evaluate factors such as user, device, location, and risk.
  • Apply least privilege: give users and applications only the access they need.
  • Use privileged identity management practices to limit standing administrator access.
  • Review inactive accounts, service principals, and access permissions regularly.

Strong identity controls can reduce the impact of stolen passwords and help limit an attacker’s ability to move through an environment.

Protect Azure Workloads and Configurations

Misconfigured cloud resources can expose systems or data even when the underlying platform is secure. In Azure, organizations should establish secure configuration standards for subscriptions, networks, storage, virtual machines, and databases. Azure Policy can help enforce organizational requirements, while Microsoft Defender for Cloud can provide security recommendations and threat protection capabilities for supported resources.

Important practices include restricting public access where it is not required, using network segmentation, securing administrative connections, encrypting sensitive data, and keeping workloads patched. Backups should be protected from accidental deletion and ransomware, and recovery plans should be tested rather than assumed to work.

Secure Microsoft 365 and Collaboration

Microsoft 365 brings together email, file storage, meetings, and collaboration tools. Security settings should reflect how people actually work while limiting unnecessary exposure. Review sharing defaults in services such as SharePoint and OneDrive, manage external collaboration, and establish retention and access policies appropriate to the organization.

Microsoft Defender for Office 365 can help protect against threats such as phishing and malicious attachments, depending on the plan and configuration. Security awareness training and clear procedures for reporting suspicious messages remain important because technical controls cannot prevent every social-engineering attempt.

Protect and Govern Data

Cloud security also depends on knowing what data an organization stores and who can access it. Microsoft Purview includes data governance, information protection, and compliance capabilities, with features varying by product and license. Organizations can use classification and sensitivity labels to help identify and protect important information, and apply data loss prevention policies to reduce inappropriate sharing.

Start by identifying sensitive data, defining who should be able to access it, and deciding how long it should be retained. Policies should be tested with users and business teams to avoid disrupting legitimate work.

Monitor, Detect, and Respond

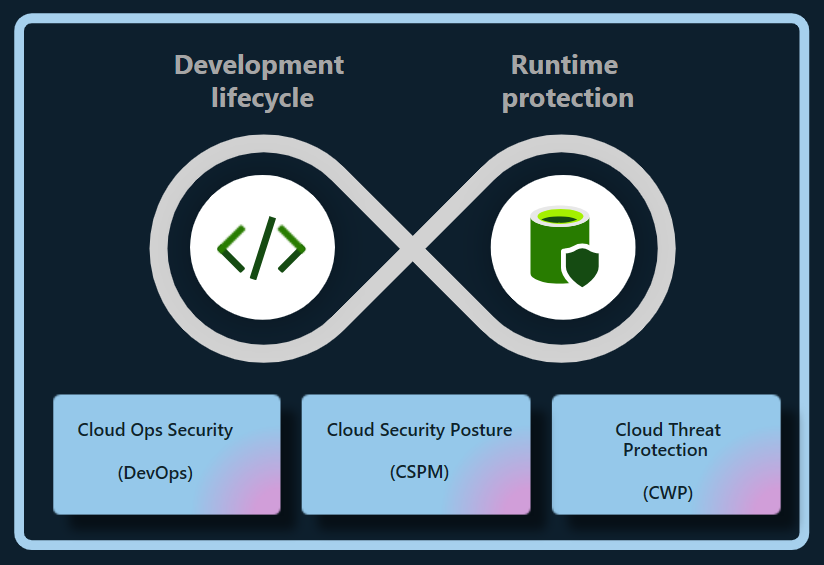
Security controls are most effective when organizations can detect suspicious activity and respond quickly. Microsoft Defender products provide security capabilities across various environments, while Microsoft Sentinel is a cloud-based security information and event management (SIEM) and security orchestration, automation, and response (SOAR) platform. The tools an organization needs depend on its environment, risk profile, and licensing.

Establish a process for reviewing alerts, investigating incidents, and escalating serious findings. Keep audit logging enabled where appropriate, define incident-response roles, and practice response scenarios such as account compromise, data exposure, and ransomware. Monitoring without a clear response process can leave important alerts unattended.

Build a Sustainable Security Program

Microsoft cloud security is not a one-time setup. Services change, employees join and leave, and business requirements evolve. A sustainable program includes regular access reviews, configuration assessments, vulnerability management, backup testing, and updates to policies and incident-response plans.

Begin with the basics: secure administrator accounts, enable strong authentication, reduce excessive permissions, protect sensitive data, and establish reliable monitoring. Then use Microsoft’s security guidance and the controls available in your specific services to improve protection over time. Because features and licensing can change, verify current capabilities and requirements in Microsoft’s official documentation before designing or purchasing a solution.


Top 9 Benefits of Microsoft Cloud Security for Your Business

  1. Scales with your business needs
  2. Offers strong identity controls
  3. Supports multifactor authentication
  4. Helps protect data with encryption
  5. Provides built-in threat detection
  6. Integrates with Microsoft 365
  7. Enables centralized security management
  8. Supports compliance and governance
  9. Offers tools for monitoring and response


5 Challenges of Microsoft Cloud Security: Complexity, Costs, and Dependence

  1. Can be complex to configure and manage.
  2. Advanced security features may require costly licenses.
  3. Misconfigurations can expose data and services.
  4. Dependence on Microsoft can limit flexibility.
  5. Requires ongoing expertise and monitoring.

Scales with your business needs

Microsoft cloud security can scale alongside your business, helping you adjust protection as your team, data, and workloads grow or change. You can add security capabilities, expand coverage across cloud services, and adapt access controls and policies as new needs arise—without having to build and maintain all the supporting infrastructure yourself. This flexibility can help keep security aligned with your business while making it easier to manage changing requirements.

Offers strong identity controls

Microsoft cloud security offers strong identity controls that help organizations protect accounts, apps, and data. With tools such as Microsoft Entra ID, teams can require multifactor authentication, apply access policies based on user and device risk, and limit permissions to only what each person needs. These safeguards make it harder for unauthorized users to gain access and help reduce the impact of compromised credentials.

Supports multifactor authentication

Microsoft cloud security supports multifactor authentication (MFA), adding an extra layer of protection beyond a password. Users may be asked to confirm their identity with an authenticator app, a security key, or another approved method. This makes it harder for someone to access an account with a stolen or guessed password and helps organizations better protect email, files, and cloud resources.

Helps protect data with encryption

Microsoft cloud security helps protect data with encryption, making information harder to read if it is accessed without authorization. Encryption can safeguard data while it is stored and while it moves between services or devices. With appropriate configuration and key-management practices, organizations can add an important layer of protection for sensitive information across their cloud environments.

Provides built-in threat detection

Microsoft cloud security includes built-in threat detection capabilities that help identify suspicious activity across supported services, users, devices, and workloads. These tools can analyze signals and surface alerts about potential risks—such as unusual sign-ins or malicious behavior—so security teams can investigate and respond more quickly. When configured to fit an organization’s environment, built-in detection can strengthen visibility without requiring every monitoring capability to be assembled from scratch.

Integrates with Microsoft 365

Microsoft cloud security integrates seamlessly with Microsoft 365, helping organizations protect email, files, meetings, and user accounts within the tools employees already use. This integration can bring security policies, identity controls, and threat protection together across services such as Outlook, Teams, SharePoint, and OneDrive. As a result, administrators can manage access more consistently, respond to potential threats with greater visibility, and help safeguard sensitive information without disrupting everyday collaboration.

Enables centralized security management

Microsoft cloud security enables centralized security management by bringing key security settings, policies, alerts, and monitoring tools together across cloud services. This gives IT and security teams a clearer view of their environment and helps them apply consistent protections, manage access, and respond to potential threats more efficiently. Centralized oversight can also make it easier to identify gaps and coordinate security practices across users, devices, and workloads.

Supports compliance and governance

Microsoft cloud security supports compliance and governance by providing tools to help organizations protect sensitive information, manage access, apply data-retention policies, and monitor activity. Services such as Microsoft Purview can help classify and govern data, while built-in security and compliance features can support an organization’s efforts to meet applicable regulatory and internal requirements. The right controls depend on the Microsoft services in use, the organization’s configuration, and its specific compliance obligations.

Offers tools for monitoring and response

Microsoft cloud security offers tools that help organizations monitor activity, detect potential threats, and respond to incidents. Services such as Microsoft Defender and Microsoft Sentinel can bring security signals together, surface suspicious behavior, and support investigation and response workflows. With appropriate configuration and ongoing oversight, these tools can help teams identify problems sooner and coordinate a more effective response.

Can be complex to configure and manage.

One drawback of Microsoft cloud security is that it can be complex to configure and manage. Services such as Azure, Microsoft 365, and Microsoft Entra ID offer many security settings, policies, and tools, and the right setup depends on an organization’s needs and licensing. Misconfigured controls or unclear responsibilities can leave gaps in protection, so teams may need specialized expertise, ongoing training, and regular reviews to manage the environment effectively.

Advanced security features may require costly licenses.

Advanced security features in Microsoft cloud services can come at a significant additional cost. Capabilities such as enhanced threat detection, identity protection, compliance tools, and advanced data protection may require higher-tier subscriptions or separate licenses. For organizations with tight budgets, these costs can make it difficult to deploy the full set of recommended safeguards, so it’s important to compare licensing options and prioritize features based on risk and business needs.

Misconfigurations can expose data and services.

One potential drawback of Microsoft cloud security is that misconfigurations can expose sensitive data and services to unauthorized access. A storage account with overly permissive access, an exposed network endpoint, or an incorrectly assigned user role can create security gaps—even when the underlying Microsoft platform is operating securely. Preventing these issues requires careful setup, regular configuration reviews, and ongoing monitoring.

Dependence on Microsoft can limit flexibility.

Relying heavily on Microsoft’s cloud security tools can limit an organization’s flexibility. Teams may find it difficult or costly to switch providers, integrate competing products, or adapt workflows built around Microsoft-specific services. This dependence can also make it harder to respond to changing business needs or negotiate terms, so organizations should consider portability and interoperability when designing their cloud security strategy.

Requires ongoing expertise and monitoring.

Microsoft cloud security requires ongoing expertise and monitoring to remain effective. Services, threats, and security settings change over time, so organizations need knowledgeable staff to review configurations, manage access, investigate alerts, and respond to incidents. Without consistent oversight, misconfigurations or suspicious activity may go unnoticed, leaving sensitive data and systems at risk.

Network Security Best Practices: Essential Steps to Protect Your Network

Network Security Best Practices

A secure network helps protect sensitive information, keep systems available, and reduce the risk of costly disruptions. Whether you manage a home network, a small business, or a large organization, network security works best as an ongoing process—not a one-time setup. The practices below can help you strengthen your defenses and respond more effectively to threats.

Keep Systems and Network Devices Updated

Install security updates for operating systems, applications, routers, firewalls, and other network equipment as soon as practical. Updates often fix vulnerabilities that attackers could otherwise exploit. Replace devices that no longer receive security support, and remove software or services that are no longer needed.

Where possible, enable automatic updates for routine security fixes. For business environments, test important updates before broad deployment and maintain a schedule for reviewing devices that may have been missed.

Use Strong Authentication

Change default usernames and passwords on routers, access points, and other equipment. Use long, unique passwords for every account, ideally stored in a reputable password manager. Avoid shared accounts when individual accounts are available, since personal accounts make it easier to track activity and revoke access when someone leaves.

Enable multifactor authentication (MFA) for administrative accounts, remote access, cloud services, and other important systems. MFA adds another verification step, making a stolen password less useful to an attacker.

Limit Access and Apply Least Privilege

Give users and devices only the access they need to do their work. Separate everyday user accounts from administrator accounts, and use elevated privileges only when necessary. Review permissions regularly, especially after job changes or departures.

Disable unused accounts, open ports, network services, and remote-access tools. Restrict administrative interfaces so they are reachable only from approved devices or trusted network locations.

Segment the Network

Network segmentation divides a network into smaller sections, limiting how far an intruder can move if one device or account is compromised. For example, organizations can separate employee computers, servers, guest Wi-Fi, and internet-connected devices such as cameras or printers.

Use firewall rules to control which sections can communicate and allow only the connections required for normal operations. Review these rules periodically to remove outdated or overly broad access.

Secure Wi-Fi and Remote Connections

Protect wireless networks with current encryption and a strong, unique passphrase. Change the access point’s default administrator credentials, keep its firmware updated, and use a separate guest network for visitors and personal devices. Avoid exposing the network’s administrative interface to the public internet.

For remote work, require secure connections through an approved VPN or other protected access method. Combine remote access with MFA, limit who can use it, and monitor for unusual sign-in activity. Do not rely on a VPN alone; remote devices should also be updated and protected.

Deploy Firewalls and Endpoint Protection

Firewalls help control traffic entering and leaving a network. Configure them to deny unnecessary connections by default, then allow only the traffic required for business or personal use. Check firewall logs and rules for unexpected changes or suspicious activity.

Install reputable endpoint protection on computers and servers, and keep it enabled and updated. Endpoint tools can help detect malicious files, suspicious behavior, and other threats that network controls may not catch.

Protect Data and Backups

Encrypt sensitive data when it is stored and when it travels across networks. Use secure protocols and avoid sending confidential information over untrusted connections without appropriate protection.

Maintain regular backups of important data and systems. Keep at least one backup isolated from the main network so malware or an intruder cannot easily alter or delete every copy. Test restores periodically; a backup is useful only if it can be recovered.

Monitor Activity and Prepare to Respond

Collect and review logs from firewalls, servers, endpoints, and important applications. Alerts can help identify unusual login attempts, unexpected data transfers, or changes to critical settings. Make sure logs are protected from unauthorized changes and retained long enough to support investigations.

Create an incident response plan that explains who to contact, how to isolate affected systems, how to preserve evidence, and how to restore operations. Practice the plan so that people know what to do under pressure.

Train Users and Review Security Regularly

People play an important role in network security. Teach users how to recognize phishing attempts, report suspicious messages, handle sensitive information, and use approved tools. Make reporting easy and respond constructively so potential problems are raised quickly.

Regularly review network diagrams, device inventories, access permissions, firewall rules, and security policies. Periodic vulnerability assessments can help identify weaknesses before they are exploited. Address findings according to their risk and verify that fixes have worked.

Make Security an Ongoing Practice

No single tool can protect every network from every threat. Strong security comes from combining updated systems, careful access controls, segmentation, monitoring, backups, and informed users. Start with the measures that address your most important risks, document your decisions, and revisit them as your network and needs change.


7 Essential Tips for Strengthening Your Network Security

  1. Use strong, unique passwords and enable multifactor authentication.
  2. Keep routers, firewalls, and devices updated.
  3. Use WPA3 or WPA2 encryption for Wi-Fi.
  4. Change default administrator usernames and passwords.
  5. Segment guest and smart-home devices from sensitive systems.
  6. Disable unused ports, services, and remote access.
  7. Monitor network logs and investigate unusual activity.

Use strong, unique passwords and enable multifactor authentication.

Use strong, unique passwords for every network account, especially administrator and remote-access accounts. Long passphrases are easier to remember and harder to guess, while a password manager can help you store them securely without reusing them. Enable multifactor authentication (MFA) wherever possible to add another layer of protection, so a stolen password alone is less likely to grant access.

Keep routers, firewalls, and devices updated.

Keep routers, firewalls, computers, and other connected devices updated with the latest security patches and firmware. Updates often fix vulnerabilities that attackers could exploit, so install them promptly and enable automatic updates when available. Replace devices that no longer receive security support, and remove outdated software or services you no longer use.

Use WPA3 or WPA2 encryption for Wi-Fi.

Use WPA3 encryption to protect your Wi-Fi network whenever your router and devices support it. If WPA3 isn’t available, choose WPA2-AES rather than outdated options such as WEP or WPA. Set a strong, unique Wi-Fi password, change the router’s default administrator credentials, and keep its firmware up to date to help prevent unauthorized access.

Change default administrator usernames and passwords.

Change the default administrator username and password on every router, access point, and network device you manage. Default credentials are often publicly documented, so attackers may try them to gain control of a device and alter its settings, intercept traffic, or access connected systems. Choose a unique, strong password for each device, change the administrator username if the device allows it, and store the credentials securely in a password manager.

Segment guest and smart-home devices from sensitive systems.

Place guest devices and smart-home equipment—such as TVs, cameras, and speakers—on a separate Wi-Fi network from computers, phones, and other systems that contain sensitive information. These devices may have weaker security or receive fewer updates, so separating them helps limit access if one is compromised. Use your router’s guest-network or network-segmentation feature, and allow only the connections each device needs.

Disable unused ports, services, and remote access.

Disable unused network ports, services, and remote-access tools to reduce the number of ways an attacker could reach your systems. Turn off features you don’t need, close unnecessary firewall ports, and limit administrative access to trusted devices or locations. Review these settings regularly, since old services and access rules can remain enabled long after they’re needed.

Monitor network logs and investigate unusual activity.

Monitor network logs regularly to spot unusual activity, such as repeated failed sign-in attempts, unexpected connections, or large transfers of data. Set alerts for suspicious patterns and investigate them promptly to determine whether they’re harmless or signs of a security issue. Keeping logs protected and retaining them long enough can also help identify what happened and support a faster response.

cyber security operations

Cyber Security Operations: A Practical Guide to Protecting Your Organization

Cybersecurity Operations: A Practical Guide to Protecting Your Organization

Cybersecurity operations are the people, processes, and technologies an organization uses to monitor its systems, detect threats, and respond to security incidents. They help turn cybersecurity from a collection of tools into an ongoing practice: identifying risks, protecting important assets, and limiting damage when something goes wrong.

As businesses rely on cloud services, connected devices, remote work, and digital data, their potential attack surface continues to grow. Effective cybersecurity operations help organizations keep pace by providing visibility into their environments and a coordinated way to handle threats.

What Are Cybersecurity Operations?

Cybersecurity operations cover the day-to-day work of defending an organization’s networks, devices, applications, and information. This work may be performed by an internal security team, a managed security provider, or a combination of both.

A central part of many operations programs is a security operations center, or SOC. A SOC is a team or function responsible for monitoring security activity, investigating alerts, and coordinating responses. Not every organization needs a dedicated, 24-hour SOC, but every organization benefits from clear ownership of security monitoring and incident response.

Core Functions of a Security Operations Program

Continuous Monitoring

Teams collect and review security data from sources such as endpoints, servers, cloud platforms, identity systems, and network devices. Monitoring can reveal unusual behavior, suspicious logins, malware activity, or changes that may indicate an attack.

Threat Detection and Investigation

Security tools generate alerts when activity matches known indicators or appears unusual. Analysts assess those alerts, determine whether they represent a real threat, and gather context before deciding what to do. Good detection depends not only on technology but also on well-tuned rules and an understanding of normal business activity.

Incident Response

When a security incident is confirmed, the response team works to contain it, remove the threat, and restore affected systems. A documented incident response plan clarifies roles, decision-making authority, communication steps, and recovery priorities before an emergency occurs.

Vulnerability and Patch Management

Cybersecurity operations also include finding weaknesses in software, devices, and configurations. Teams prioritize vulnerabilities based on factors such as severity, exposure, and business impact, then coordinate testing and remediation. Timely updates can reduce the opportunities attackers have to exploit known flaws.

Threat Intelligence

Threat intelligence provides information about current attacker techniques, malicious infrastructure, and emerging risks. Used thoughtfully, it can help teams improve detection and focus their attention. Intelligence is most useful when it is relevant to the organization’s systems and connected to practical defensive actions.

People, Processes, and Technology

Strong cybersecurity operations require more than purchasing security software. The three essential elements are:

  • People: Skilled staff who can interpret alerts, make sound decisions, and communicate with technical teams and business leaders.
  • Processes: Clear procedures for monitoring, escalation, incident response, recovery, and continuous improvement.
  • Technology: Tools that provide visibility, help identify threats, and support investigation and response.

When one of these elements is missing, the entire program can suffer. For example, a security platform may generate more alerts than a small team can investigate. Well-designed processes help prioritize those alerts, while training and automation can help staff act efficiently.

Common Challenges

Organizations often face a high volume of security alerts, limited staffing, and complex technology environments. Data may be spread across on-premises systems, multiple cloud services, and employee devices. Inconsistent logging or unclear ownership can make investigations slower and less reliable.

Alert fatigue is another common concern. When teams receive too many low-priority or false-positive alerts, important warnings can be overlooked. Regularly reviewing detection rules, improving asset visibility, and prioritizing alerts by risk can help reduce this problem.

How to Improve Cybersecurity Operations

  1. Understand your environment. Maintain an inventory of important systems, devices, accounts, and data. You cannot reliably protect assets you do not know exist.
  2. Prioritize business risks. Identify the systems and information whose loss or disruption would have the greatest impact, then align monitoring and response plans with those priorities.
  3. Establish clear procedures. Document how incidents are reported, investigated, escalated, contained, and communicated.
  4. Improve visibility. Collect useful security logs from critical systems and protect those logs from unauthorized changes.
  5. Practice response. Tabletop exercises and technical drills help teams find gaps in their plans before a real incident occurs.
  6. Measure and refine. Review response times, recurring incident types, alert quality, and remediation progress. Use the results to improve the program.

The Role of Automation and AI

Automation can handle repetitive tasks, such as enriching an alert with related information or isolating a device under approved conditions. These capabilities can help teams respond faster, but they should be tested and governed carefully. High-impact actions should have appropriate safeguards, oversight, and a way to reverse mistakes.

Artificial intelligence can help analyze large volumes of activity and surface patterns for investigation. It does not replace security professionals or eliminate the need for sound processes. Organizations should evaluate how automated systems use data, validate their results, and ensure that people remain accountable for important security decisions.

Building a Resilient Security Program

Cybersecurity operations are an ongoing cycle of preparation, monitoring, detection, response, and improvement. No organization can prevent every attack, but a well-organized program can make threats easier to identify and incidents less disruptive.

By combining capable people, tested procedures, and appropriately selected technology, organizations can strengthen their defenses and recover more effectively when security events occur. The best starting point is a clear understanding of critical assets, realistic risks, and the actions the organization will take when those risks become real.


Top 5 Essential Cybersecurity Tips for Protecting Your Operations

  1. Enable multi-factor authentication on all accounts.
  2. Patch systems promptly to close known vulnerabilities.
  3. Monitor logs for unusual activity and failed logins.
  4. Back up critical data and test recovery regularly.
  5. Train staff to spot phishing and report incidents.

Enable multi-factor authentication on all accounts.

Enable multi-factor authentication (MFA) on every account that supports it, especially email, banking, administrator, and cloud service accounts. MFA requires an additional verification step—such as an authenticator app, security key, or passkey—along with a password, making it harder for attackers to gain access with stolen or reused credentials. For stronger protection, choose phishing-resistant options like passkeys or hardware security keys when available, and keep recovery methods secure and up to date.

Patch systems promptly to close known vulnerabilities.

Patch systems promptly to close known vulnerabilities before attackers can exploit them. Apply security updates to operating systems, applications, devices, and cloud services as soon as practical, prioritizing internet-facing and business-critical systems. Test patches where needed, schedule updates to limit disruption, and verify that installations succeed. For systems that cannot be patched right away, use temporary safeguards—such as restricting access or disabling affected features—and track the issue until it is resolved.

Monitor logs for unusual activity and failed logins.

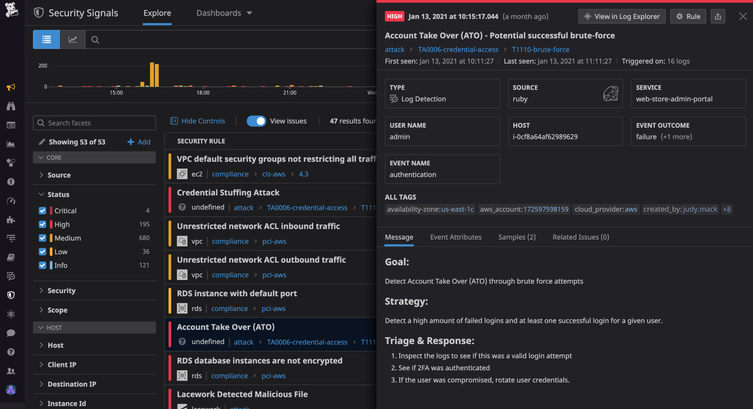
Monitor system, application, and network logs for unusual activity, including repeated failed login attempts, logins from unfamiliar locations, and access at unexpected times. These patterns can signal a brute-force attack, compromised account, or other security issue. Centralize logs where possible, set alerts for suspicious behavior, and investigate promptly. Keep logs protected and retain them long enough to support incident investigations.

Back up critical data and test recovery regularly.

Back up critical data regularly and keep copies separate from the systems they protect, so an attack, hardware failure, or accidental deletion won’t destroy every version. Just as important, test your recovery process on a regular schedule: verify that backups are complete, can be restored, and meet your organization’s recovery needs. A backup is only useful if you can access it and restore operations when it matters.

Train staff to spot phishing and report incidents.

Train staff to recognize phishing emails, texts, and calls by watching for suspicious links, unexpected attachments, urgent demands, and requests for sensitive information. Encourage employees to report anything suspicious promptly through a clear, easy-to-use process—even if they are unsure or have already clicked a link. Regular training and realistic practice help people respond confidently, giving security teams a better chance to contain threats before they spread.

cyber security monitoring

Cyber Security Monitoring: A Practical Guide to Detecting and Responding to Threats

Cybersecurity Monitoring: A Practical Guide for Organizations

Cybersecurity threats can emerge at any time, and even well-protected systems may have vulnerabilities. Cybersecurity monitoring helps organizations spot suspicious activity, investigate potential incidents, and respond before a problem causes serious damage. It is an ongoing process—not a one-time security check.

What Is Cybersecurity Monitoring?

Cybersecurity monitoring is the continuous review of activity across an organization’s computers, networks, applications, cloud services, and user accounts. Security teams look for signs of unauthorized access, malware, data theft, unusual behavior, and other possible threats.

Monitoring may rely on automated tools, human analysis, or a combination of both. For example, software might flag a login from an unfamiliar location, while an analyst determines whether it is a legitimate employee or a compromised account.

Why Is Monitoring Important?

Many attacks do not cause immediate, obvious disruption. An intruder may quietly explore a network, steal credentials, or access sensitive information over time. Continuous monitoring can help reduce the time between the start of an attack and its detection.

Effective monitoring can help organizations:

  • Identify suspicious activity earlier
  • Limit the impact of security incidents
  • Protect sensitive and customer data
  • Investigate events with useful system records
  • Meet security, privacy, or regulatory obligations
  • Understand recurring weaknesses and improve defenses

What Should Organizations Monitor?

A useful monitoring program considers the systems and information most important to the organization. Common sources of security data include:

  • Network traffic: Connections between devices, unusual data transfers, and attempts to reach suspicious destinations.
  • User accounts: Login patterns, failed sign-in attempts, changes to permissions, and activity involving privileged accounts.
  • Endpoints: Activity on laptops, desktops, servers, and mobile devices, including unexpected software or processes.
  • Applications and cloud services: Access to files, configuration changes, administrative actions, and unusual use of cloud resources.
  • Security tools: Alerts from firewalls, endpoint protection, email security, and identity systems.

How Cybersecurity Monitoring Works

Monitoring typically involves several connected activities:

  1. Collect data: Gather relevant logs and alerts from devices, services, and security tools.
  2. Analyze activity: Compare events with known threat indicators, established rules, and normal patterns of use.
  3. Prioritize alerts: Assess the likelihood and potential impact of each event to help teams focus on the most urgent risks.
  4. Investigate: Review related events and available evidence to determine whether an alert is a real incident.
  5. Respond: Take appropriate steps, such as disabling a compromised account, isolating a device, or blocking malicious traffic.
  6. Improve: Use lessons from incidents and near misses to refine security controls and response procedures.

Tools and Services

Organizations use a range of technologies to support monitoring. Security information and event management (SIEM) platforms collect and correlate data from multiple sources. Endpoint detection and response (EDR) tools help identify and investigate activity on individual devices. Network monitoring tools examine traffic, while identity and access management systems record account activity.

Some organizations operate an internal security operations center (SOC). Others use a managed security service provider to monitor systems and help investigate alerts. The right approach depends on an organization’s size, risk, budget, and available expertise. Tools can help process large volumes of data, but they still need thoughtful configuration and qualified people to interpret results.

Best Practices for an Effective Program

  • Start with important assets. Identify critical systems, sensitive data, and accounts that would cause significant harm if compromised.
  • Set clear priorities. Define which events require immediate attention and who is responsible for responding.
  • Protect and retain logs. Limit access to security records and keep them for a period that supports investigations and applicable requirements.
  • Reduce alert fatigue. Tune rules to minimize irrelevant alerts without overlooking meaningful warning signs.
  • Use multiple signals. A single unusual event may have an innocent explanation; related events can provide better context.
  • Prepare response procedures. Document how to report, investigate, contain, and recover from common incident types.
  • Test and review. Practice incident response and periodically check whether monitoring covers new systems, services, and risks.
  • Respect privacy. Establish appropriate policies for collecting and reviewing employee and customer data, and follow applicable laws.

Measuring Success

Counting alerts alone does not show whether a monitoring program is effective. Organizations can also assess how quickly they detect and respond to incidents, whether high-priority systems are covered, how often alerts are false positives, and whether investigations lead to practical improvements. These measures should support better decisions rather than encourage teams to chase a single target.

Conclusion

Cybersecurity monitoring gives organizations a clearer view of activity across their digital environments. When paired with sound security controls, trained responders, and a tested incident response plan, it can help detect threats sooner and reduce their impact. The strongest programs are continually reviewed and adapted as technology, business needs, and risks change.


6 Essential Tips for Effective Cybersecurity Monitoring

  1. Monitor network traffic for unusual patterns.
  2. Enable alerts for suspicious login attempts.
  3. Review security logs regularly.
  4. Use endpoint detection on all devices.
  5. Investigate alerts promptly.
  6. Test monitoring tools and response plans.

Monitor network traffic for unusual patterns.

Monitor network traffic for unusual patterns, such as unexpected data transfers, connections to unfamiliar destinations, or spikes in activity outside normal business hours. These changes may signal compromised accounts, malware, or unauthorized access. Set a baseline for typical network behavior, use monitoring tools to flag anomalies, and investigate alerts promptly to determine whether they’re legitimate or require a response.

Enable alerts for suspicious login attempts.

Enable alerts for suspicious login attempts so your team can quickly investigate potential account compromise. Configure notifications for patterns such as repeated failed sign-ins, logins from unusual locations or devices, and attempts to access privileged accounts. Pair alerts with a clear response process, such as verifying the activity with the user, requiring a password reset, or temporarily locking the account when appropriate. Tune alert settings regularly to reduce false alarms while ensuring genuinely risky activity receives prompt attention.

Review security logs regularly.

Review security logs regularly to spot unusual activity before it becomes a bigger problem. Check records from systems such as user accounts, servers, applications, and firewalls for unexpected logins, repeated failed sign-in attempts, unfamiliar devices, or unusual data transfers. Set a consistent review schedule, prioritize alerts involving sensitive systems, and investigate anything that doesn’t match normal activity. Regular reviews can help your team detect threats sooner and respond with better information.

Use endpoint detection on all devices.

Use endpoint detection and response (EDR) on every device that accesses your organization’s data, including laptops, desktops, and servers. EDR tools monitor device activity for signs of malware or other suspicious behavior and can help security teams investigate and contain threats quickly. Keep the software enabled and up to date, and make sure alerts are reviewed and acted on promptly.

Investigate alerts promptly.

Investigate security alerts promptly to determine whether they indicate a real threat and limit potential damage. Prioritize alerts based on their severity and the systems involved, then review relevant logs and activity for context. If an alert appears credible, follow your incident response plan—such as securing an account or isolating a device—and document what happened and how it was handled.

Test monitoring tools and response plans.

Regularly test your cybersecurity monitoring tools and response plans to make sure they work when an incident occurs. Run practice scenarios, such as a compromised account or suspicious data transfer, to confirm that alerts reach the right people and responders understand what to do. Use the results to fix gaps, update procedures, and ensure your tools are configured to detect the threats most relevant to your organization.

siem cyber

SIEM Cybersecurity: A Guide to Security Information and Event Management

SIEM in Cybersecurity: How Security Information and Event Management Works

Cyberattacks can leave clues across an organization’s computers, applications, networks, and cloud services. The challenge is finding those clues quickly and understanding whether they point to a real threat. Security information and event management (SIEM) helps by bringing security data together, analyzing it, and alerting teams to suspicious activity.

What Is SIEM?

SIEM, pronounced “sim,” is a cybersecurity technology that collects and analyzes security-related data from across an organization’s IT environment. It can gather logs and events from sources such as servers, endpoints, firewalls, identity systems, applications, and cloud platforms.

By reviewing this information in one place, security teams can spot patterns that might be difficult to see in separate systems. For example, an unusual login may look harmless on its own. When correlated with repeated failed attempts and unexpected access to sensitive files, it may signal a compromised account.

How Does SIEM Work?

Most SIEM solutions support several core activities:

  1. Data collection: The system receives logs and security events from connected sources.
  2. Normalization: It organizes data from different tools into a consistent format so events can be compared.
  3. Correlation and analysis: Rules, analytics, and sometimes machine learning identify relationships or unusual behavior across events.
  4. Alerting: When activity matches a detection rule or risk pattern, the SIEM creates an alert for investigation.
  5. Investigation and reporting: Analysts use search tools, dashboards, and timelines to examine activity and document findings.

SIEM systems can also retain event data for a set period, helping teams investigate incidents and meet applicable audit or compliance requirements. Retention capabilities and requirements vary by product and organization.

Why SIEM Matters for Cybersecurity

A SIEM can help security teams gain a broader view of activity across their environment. Its value often includes:

  • Centralized visibility: Security events from multiple systems can be reviewed in one place.
  • Threat detection: Correlation can reveal suspicious combinations of events that individual tools may not identify together.
  • Faster investigations: Searchable logs and event timelines can help analysts understand what happened and when.
  • Incident response support: Alerts and investigative context can help teams decide what actions to take.
  • Audit and compliance support: Reports and retained logs may help organizations demonstrate how security events are monitored and reviewed.

A SIEM is not a substitute for a complete security program. It works best alongside sound security practices, capable staff, clear response procedures, and effective controls such as multifactor authentication and endpoint protection.

Common SIEM Use Cases

Organizations use SIEM tools to monitor for a range of security concerns, including:

  • Repeated or unusual login attempts
  • Unexpected access to sensitive information
  • Suspicious changes to user accounts or permissions
  • Malware alerts and unusual endpoint behavior
  • Potential data exfiltration or unusual network traffic
  • Activity involving accounts, devices, or locations that differ from normal patterns

These detections depend on which data sources are connected and how the system is configured. A SIEM cannot reliably identify activity it cannot observe, and alerts require appropriate review.

SIEM Challenges to Consider

SIEM can strengthen security monitoring, but it also requires thoughtful implementation and ongoing maintenance. Common challenges include:

  • Alert fatigue: Too many low-value alerts can make it harder to prioritize genuine risks.
  • Incomplete data: Missing or poorly configured data sources can create gaps in visibility.
  • Complex setup: Detection rules and integrations often need to be tailored to an organization’s systems and risks.
  • Storage and cost: Collecting and retaining large volumes of logs can affect licensing, infrastructure, and operational costs.
  • Staffing and expertise: Analysts need time and training to investigate alerts and improve detection quality.

Organizations can address these challenges by prioritizing important data sources, tuning detection rules, setting clear alert-handling procedures, and regularly reviewing whether the SIEM is producing useful results.

SIEM and Related Security Technologies

SIEM is often used alongside other security tools. A security orchestration, automation, and response (SOAR) platform can help coordinate or automate parts of incident response. Extended detection and response (XDR) tools focus on detecting and responding to threats across connected security products. Some modern security platforms combine capabilities from several categories, but features and terminology differ among vendors.

How to Get Started with SIEM

Before choosing or deploying a SIEM, an organization should define what it needs to monitor and why. A practical starting point includes:

  1. Identify critical systems, sensitive data, and key security risks.
  2. Select the log sources that provide meaningful visibility into those risks.
  3. Establish detection priorities and define who will review alerts.
  4. Set retention, access, and privacy requirements for collected data.
  5. Test alerts and response procedures, then adjust rules based on real results.
  6. Measure performance using relevant indicators, such as investigation time and the proportion of actionable alerts.

The Role of SIEM in a Strong Security Program

SIEM helps organizations turn activity from many systems into information that security teams can investigate. Its effectiveness depends on the quality of the data it receives, the relevance of its detections, and the organization’s ability to respond.

With clear goals, reliable integrations, and ongoing tuning, SIEM can become an important part of cybersecurity monitoring. It gives teams a more connected view of potential threats—and a stronger foundation for investigating suspicious activity.


Understanding SIEM in Cybersecurity: Key FAQs Answered

  1. What is SIEM in cybersecurity?
  2. How does a SIEM system work?
  3. What are the main benefits of using SIEM?
  4. What types of security events can SIEM detect?
  5. What is the difference between SIEM, SOAR, and XDR?
  6. How much does SIEM cost, and what affects the price?

What is SIEM in cybersecurity?

SIEM, or security information and event management, is a cybersecurity technology that collects and analyzes log and event data from systems such as networks, servers, applications, and cloud services. By bringing this information together, SIEM helps security teams identify suspicious patterns, investigate potential threats, and respond to incidents. Its effectiveness depends on having useful data sources, well-tuned alerts, and a team or process to review and act on findings.

How does a SIEM system work?

A SIEM system works by collecting security logs and events from sources such as computers, applications, firewalls, and cloud services, then organizing and analyzing that data in one place. It looks for suspicious patterns by comparing events against detection rules and expected behavior. When it identifies activity that may indicate a threat, it generates an alert so security teams can investigate, respond, and review related events.

What are the main benefits of using SIEM?

The main benefits of using SIEM (security information and event management) include centralized visibility into security activity, faster detection of suspicious behavior, and more efficient incident investigations. By collecting and correlating data from systems such as networks, servers, endpoints, and cloud services, SIEM can help security teams identify patterns they might otherwise miss. It can also support incident response, provide searchable records for audits, and help organizations meet certain compliance requirements. Its effectiveness depends on collecting the right data, tuning alerts, and having people and processes in place to respond.

What types of security events can SIEM detect?

A SIEM can detect a wide range of security events by analyzing logs and activity from systems such as networks, endpoints, applications, identity platforms, and cloud services. Depending on the data sources and detection rules in place, it may flag repeated failed logins, unusual access to accounts or sensitive files, unexpected changes to permissions, malware alerts, suspicious network traffic, and signs of possible data exfiltration. SIEM can also connect events across different systems—for example, linking an unusual login to later access to critical data—to help security teams investigate potential threats. Detection coverage depends on how the SIEM is configured and the quality of the data it receives.

What is the difference between SIEM, SOAR, and XDR?

SIEM, SOAR, and XDR support cybersecurity in different ways. A SIEM collects and analyzes security data from across an organization to identify suspicious activity and generate alerts. SOAR helps teams coordinate and automate parts of their response, such as assigning incidents or running approved investigation steps. XDR detects and responds to threats across connected security layers, such as endpoints, email, and cloud services, often bringing related activity together for investigation. These tools can complement one another, but their capabilities vary by product.

How much does SIEM cost, and what affects the price?

SIEM costs vary widely, from a few hundred dollars per month for a small or managed service to much higher amounts for large, complex deployments. Pricing may be based on daily data volume, the number of monitored devices or users, data retention, and included features. Costs can also include setup, integrations, cloud storage, staff training, ongoing tuning, and analyst support. To compare options, estimate the log data you need to collect, identify essential capabilities, and ask vendors to clarify any usage limits or add-on fees.

Enhancing Cyber Security: The Role of Trusted Providers

The Importance of Cyber Security Providers

The Importance of Cyber Security Providers

In today’s digital age, where businesses and individuals rely heavily on technology, the need for robust cyber security measures has never been greater. Cyber threats are constantly evolving, becoming more sophisticated and dangerous. This is where cyber security providers play a crucial role in safeguarding sensitive information and protecting against cyber attacks.

What Do Cyber Security Providers Offer?

Cyber security providers offer a range of services designed to protect organizations from cyber threats. These services may include:

  • Network security: Securing networks from unauthorized access and monitoring for suspicious activities.
  • Endpoint security: Protecting individual devices such as computers, laptops, and mobile devices from malware and other threats.
  • Incident response: Developing strategies to respond to and mitigate the impact of cyber attacks.
  • Security awareness training: Educating employees on best practices for maintaining cyber security.
  • Vulnerability assessments: Identifying weaknesses in systems that could be exploited by attackers.

Why Choose a Cyber Security Provider?

Partnering with a cyber security provider offers several benefits:

  • Expertise: Cyber security providers have specialized knowledge and experience in identifying and mitigating cyber threats.
  • 24/7 Monitoring: Many providers offer around-the-clock monitoring to detect and respond to threats in real-time.
  • Compliance: Providers can help ensure that organizations comply with relevant regulations and standards related to data protection.
  • Cutting-Edge Technology: Providers stay abreast of the latest trends in cyber security technology to provide the most effective protection.
  • Cost-Effectiveness: Outsourcing cyber security services can be more cost-effective than maintaining an in-house team.

Conclusion

In conclusion, cyber security providers play a vital role in defending against the ever-growing threat of cyber attacks. By partnering with a reputable provider, organizations can enhance their defenses, protect sensitive data, and maintain business continuity in the face of evolving cyber threats.


Top 7 FAQs About Choosing and Working with Cyber Security Providers

  1. What services do cyber security providers offer?
  2. How can a cyber security provider help protect my business from cyber threats?
  3. What factors should I consider when choosing a cyber security provider?
  4. Do cyber security providers offer 24/7 monitoring services?
  5. How do cyber security providers stay updated on the latest threats and technologies?
  6. Can a cyber security provider help my business comply with data protection regulations?
  7. What are the benefits of outsourcing cyber security services to a provider?

What services do cyber security providers offer?

Cyber security providers offer a wide range of services to help organizations protect themselves against cyber threats. These services typically include network security to secure systems from unauthorized access, endpoint security to protect individual devices from malware, incident response to mitigate the impact of cyber attacks, security awareness training for employees, and vulnerability assessments to identify weaknesses in systems. By offering these comprehensive services, cyber security providers empower businesses to enhance their defenses, safeguard sensitive information, and maintain a secure digital environment in the face of evolving cyber threats.

How can a cyber security provider help protect my business from cyber threats?

A cyber security provider can help protect your business from cyber threats by offering a comprehensive range of services tailored to your specific needs. They can conduct thorough assessments to identify vulnerabilities in your systems, implement robust security measures to safeguard your network and data, provide continuous monitoring for early threat detection, offer incident response services to mitigate the impact of attacks, and educate your employees on best practices for maintaining cyber security. By leveraging their expertise and cutting-edge technology, a cyber security provider can significantly enhance your defenses against cyber threats and ensure the resilience of your business in the face of evolving risks.

What factors should I consider when choosing a cyber security provider?

When choosing a cyber security provider, several factors should be carefully considered to ensure that you select the right partner for your organization’s needs. Firstly, evaluate the provider’s expertise and experience in the field of cyber security, including their track record in handling similar challenges. Assess the range of services they offer and determine if they align with your specific requirements. Additionally, consider the provider’s approach to compliance with industry regulations and standards to ensure that your data is adequately protected. It is also essential to assess their response capabilities in the event of a cyber incident and their commitment to staying updated on emerging threats and technologies. Lastly, factor in considerations such as cost-effectiveness, scalability of services, and the provider’s reputation within the industry when making your decision.

Do cyber security providers offer 24/7 monitoring services?

Yes, many cyber security providers offer 24/7 monitoring services as part of their comprehensive security solutions. This continuous monitoring allows for real-time detection and response to potential cyber threats, ensuring that any suspicious activities are identified and addressed promptly. By providing around-the-clock monitoring, cyber security providers can help organizations enhance their security posture and mitigate the risks associated with cyber attacks effectively.

How do cyber security providers stay updated on the latest threats and technologies?

Cyber security providers stay updated on the latest threats and technologies through a variety of proactive measures. They continuously monitor industry trends, research emerging cyber threats, and analyze data from previous incidents to stay ahead of potential risks. Additionally, many providers participate in information-sharing networks, collaborate with other security professionals, attend conferences, and undergo regular training to enhance their knowledge and skills. By investing in ongoing education and leveraging a network of resources, cyber security providers ensure they are well-equipped to protect their clients from evolving cyber threats.

Can a cyber security provider help my business comply with data protection regulations?

A cyber security provider can indeed help your business comply with data protection regulations. These providers have expertise in understanding and implementing the necessary security measures to ensure that your organization meets the requirements set forth by data protection regulations. They can assist in identifying potential vulnerabilities, implementing appropriate safeguards, and monitoring compliance to mitigate risks of data breaches. By partnering with a cyber security provider, businesses can benefit from specialized knowledge and guidance to navigate the complex landscape of data protection regulations effectively.

What are the benefits of outsourcing cyber security services to a provider?

Outsourcing cyber security services to a provider offers numerous benefits to organizations. By partnering with a specialized cyber security provider, businesses can access expert knowledge and experience in identifying and mitigating cyber threats. These providers often offer 24/7 monitoring, ensuring that threats are detected and responded to in real-time. Additionally, outsourcing can help organizations ensure compliance with data protection regulations and standards, leverage cutting-edge technology for enhanced protection, and potentially reduce costs compared to maintaining an in-house cyber security team. Overall, outsourcing cyber security services to a reputable provider can strengthen an organization’s defenses and safeguard sensitive data against evolving cyber threats.

cybersecurity as a service

Cybersecurity as a Service: A Practical Guide for Businesses

Cybersecurity as a Service: A Practical Guide for Businesses

Cybersecurity is no longer a one-time project. Threats change constantly, software needs regular updates, and even well-prepared organizations can face new risks. For many businesses, keeping up requires more time and specialized expertise than an in-house team can provide. Cybersecurity as a Service (CSaaS) offers another approach: access to ongoing security tools and expertise through an external provider.

What Is Cybersecurity as a Service?

Cybersecurity as a Service is a model in which an organization relies on a third-party provider for some or all of its security operations. Services are typically delivered on an ongoing basis and may be tailored to the organization’s size, systems, risk profile, and regulatory requirements.

Depending on the provider and service plan, CSaaS may include security monitoring, threat detection, vulnerability assessments, incident response support, employee training, and help with security policies. Some providers focus on a specific area, while others offer a broader managed security program.

Common Cybersecurity as a Service Offerings

  • Security monitoring: Reviewing activity across networks, devices, cloud environments, and applications to identify suspicious behavior.
  • Managed detection and response: Investigating potential threats and helping contain or remediate them. The exact level of response varies by provider and contract.
  • Vulnerability management: Identifying weaknesses in systems and helping prioritize fixes based on risk.
  • Endpoint protection: Managing security for computers, mobile devices, and servers.
  • Cloud security: Helping protect cloud accounts, workloads, data, and configurations.
  • Identity and access management: Supporting controls such as multifactor authentication, role-based access, and account reviews.
  • Security awareness training: Teaching employees how to recognize phishing, handle sensitive information, and report concerns.
  • Incident response planning: Preparing procedures and providing support when a security event occurs.

Why Businesses Choose CSaaS

Access to specialized expertise: Security providers may bring experience across different technologies and threat scenarios. This can be valuable for organizations that do not have a dedicated security team.

Ongoing coverage: Security risks do not follow business hours. Some services provide continuous monitoring or on-call support, depending on the agreement.

Predictable costs: A subscription or managed-services arrangement can make security spending easier to plan than building every capability internally. Costs and included services vary, so it is important to review the full scope.

Room to scale: Services can often be adjusted as an organization adds employees, locations, applications, or cloud systems.

More focus on core work: By delegating selected security tasks, internal staff may have more time for other business priorities. Outsourcing does not remove the organization’s responsibility for managing risk, however.

What CSaaS Does Not Do

Cybersecurity as a Service is not a guarantee that an organization will never experience a breach. No provider can eliminate every risk, and technology alone cannot prevent every incident. Effective security still depends on clear policies, reliable backups, timely software updates, appropriate access controls, and informed employees.

Responsibility is also shared. The provider may operate specific tools or monitor defined systems, while the customer remains responsible for decisions such as approving access, protecting business data, and following applicable legal or regulatory requirements. Those boundaries should be documented before service begins.

How to Choose a Provider

Start by identifying the problems the service needs to solve. A business seeking help with after-hours monitoring may need a different arrangement from one preparing for a compliance review or improving cloud security.

  • Define the scope: Confirm which systems, locations, users, and data are covered—and which are not.
  • Understand response procedures: Ask who investigates alerts, who can take action, how quickly the provider responds, and when the business will be contacted.
  • Review service levels: Look for clear commitments about availability, response times, reporting, and escalation. Check how those commitments are measured.
  • Ask about data handling: Understand what information the provider collects, where it is stored, who can access it, and how it is protected.
  • Check experience and references: Look for experience with organizations of a similar size, industry, and technology environment.
  • Clarify responsibilities: Establish who manages software updates, account permissions, investigations, backups, and incident communications.
  • Plan for continuity: Ask how service handoffs, data access, and security operations will work if the contract ends.

Making the Most of the Service

Before onboarding, create an accurate inventory of devices, applications, cloud services, and important data. Share existing policies and known risks with the provider, and identify internal contacts who can make decisions during an incident. Regularly review reports and hold meetings to discuss unresolved issues, changing business needs, and recommended improvements.

It is also important to test the relationship before an emergency. Tabletop exercises and incident-response drills can reveal unclear responsibilities and communication gaps while there is still time to address them.

Conclusion

Cybersecurity as a Service can help businesses access security expertise and ongoing support without building every capability in-house. The value depends on choosing services that match actual risks, defining responsibilities clearly, and staying actively involved. With a well-scoped agreement and sound internal practices, CSaaS can become a practical part of a broader cybersecurity program.


Top 5 Advantages of Cybersecurity as a Service for Your Business

  1. Access to specialized security expertise
  2. Continuous threat monitoring
  3. Predictable subscription costs
  4. Scales with business needs
  5. Frees staff to focus on core work


7 Potential Drawbacks of Cybersecurity as a Service: Costs, Control, and More

  1. Ongoing subscription costs can add up.
  2. Less direct control over security operations.
  3. Service quality varies between providers.
  4. Sensitive data may be shared with a vendor.
  5. Response times may depend on the service agreement.
  6. Integrating tools can be complex.
  7. Outsourcing does not eliminate business risk.

Access to specialized security expertise

Cybersecurity as a Service gives businesses access to specialized security expertise without requiring them to hire and maintain a large in-house team. Providers bring experience with evolving threats, security tools, and industry practices, helping organizations identify risks, strengthen defenses, and respond to potential incidents. This expertise can be especially valuable for small and midsize businesses that need knowledgeable support but may not have the resources to build a dedicated security department.

Continuous threat monitoring

Continuous threat monitoring helps organizations spot suspicious activity as it happens, rather than discovering it after significant damage has occurred. A cybersecurity provider can monitor networks, devices, and cloud systems around the clock, investigate alerts, and notify the right people when action is needed. This ongoing visibility can help businesses respond to emerging threats more quickly, even when their internal team is unavailable.

Predictable subscription costs

Cybersecurity as a Service can make security spending more predictable through a regular subscription fee. Instead of making large upfront investments in tools, hiring, and ongoing maintenance, businesses can budget for an agreed set of services each month or year. Costs depend on the provider and scope, so reviewing what’s included—and what may incur extra charges—helps avoid surprises.

Scales with business needs

Cybersecurity as a Service can scale as your business changes. You can adjust coverage as you add employees, open new locations, adopt cloud tools, or face new security requirements—without having to build an entirely new in-house security team. This flexibility helps keep protection aligned with your needs and budget as your organization grows.

Frees staff to focus on core work

Cybersecurity as a Service can free employees from time-consuming security tasks, such as monitoring alerts, managing tools, and tracking routine updates. With a specialized provider handling agreed-upon responsibilities, your team can spend more time on the work that directly supports your business goals. Outsourcing security does not eliminate the need for internal oversight, but it can help staff focus their attention where it matters most.

Ongoing subscription costs can add up.

Ongoing subscription costs for cybersecurity as a service can add up over time, especially as a business grows or adds more users, devices, and security features. What starts as a manageable monthly expense may become a significant part of the IT budget, so it’s important to review pricing, renewal terms, and potential add-on fees regularly. Compare the total long-term cost with the value and coverage provided to make sure the service continues to fit your needs.

Less direct control over security operations.

One potential drawback of cybersecurity as a service is having less direct control over day-to-day security operations. When an outside provider manages monitoring, tools, or incident response, your team may have limited visibility into how decisions are made or how quickly actions are taken. This can create challenges if the provider’s procedures do not align with your business priorities. To reduce the risk, define responsibilities, approval requirements, reporting expectations, and escalation procedures clearly in the service agreement.

Service quality varies between providers.

Service quality can vary significantly between cybersecurity providers, making it difficult to know what level of protection you’ll receive. Providers may differ in their expertise, monitoring capabilities, response times, communication, and the tools they use. A service that sounds comprehensive may also have important limits in its contract. Before choosing a provider, review exactly what’s included, ask how incidents are handled, and check references to ensure the service meets your organization’s needs.

Sensitive data may be shared with a vendor.

One potential drawback of cybersecurity as a service is that protecting your systems may require sharing sensitive data with an outside vendor. Depending on the service, the provider could access security logs, user information, system configurations, or other confidential details. This creates additional privacy and data-protection risks, especially if the vendor’s controls or practices are inadequate. Before signing an agreement, review what data will be collected, how it will be stored and protected, who can access it, and whether it will be shared with subcontractors.

Response times may depend on the service agreement.

Response times for cybersecurity as a service can depend on the terms of the service agreement. A provider may prioritize incidents according to severity, offer different response levels for different plans, or limit support to certain hours. If those details are unclear, a business could wait longer than expected for help during a security incident. Before signing, confirm response-time commitments, after-hours coverage, escalation procedures, and what actions the provider is authorized to take.

Integrating tools can be complex.

Integrating cybersecurity tools can be complex, especially when a provider’s platforms need to work with existing networks, cloud services, and business applications. Compatibility issues, duplicated alerts, or gaps in data sharing can make it harder to get a clear view of security risks. Setup may also require changes to workflows and access controls, so businesses should clarify integration requirements, responsibilities, and ongoing support before adopting a service.

Outsourcing does not eliminate business risk.

Outsourcing cybersecurity can add valuable expertise and support, but it does not eliminate a business’s responsibility for managing risk. The provider can only protect the systems, data, and processes covered by the agreement, and gaps in scope, communication, or internal practices may leave the organization exposed. Businesses still need to make informed security decisions, maintain sound policies, train employees, and understand who is responsible for each task—especially during an incident.