cfchris.com

Loading

medical software engineer

Medical Software Engineer: Roles, Skills, and Career Outlook

What Does a Medical Software Engineer Do?

Medical software engineers design, build, and maintain software used in health care. Their work can support clinicians, patients, researchers, and health care organizations—from helping manage medical records to powering diagnostic tools and connected devices. Because these systems can affect patient care, the role calls for both strong engineering skills and a careful understanding of safety, privacy, and clinical needs.

What Medical Software Engineers Work On

The field covers a wide range of products and systems, including:

  • Electronic health record and patient management systems
  • Mobile apps for care teams and patients
  • Telehealth platforms and remote patient monitoring tools
  • Software that processes medical images or laboratory results
  • Applications that connect medical devices to clinical systems
  • Data platforms used for health research and operations

Some engineers focus on software for medical devices, while others build web services, mobile applications, or tools for hospitals and health technology companies. The exact responsibilities depend on the product and the setting.

Key Responsibilities

A medical software engineer may gather requirements from clinicians and product teams, translate them into technical designs, and write and review code. The job often includes testing software, investigating defects, documenting decisions, and supporting a product after it is released.

Engineers also need to think about how software behaves in real clinical environments. A feature that seems simple on a screen may affect a busy workflow, require information from several systems, or need to work reliably when connectivity is limited. Collaboration with clinicians, designers, quality specialists, security professionals, and regulatory teams is often essential.

Skills and Knowledge

Medical software engineers generally need a foundation in software development, such as experience with programming languages, databases, APIs, testing, and cloud or mobile technologies. They may also need to understand system architecture, accessibility, and secure development practices.

Health care adds important considerations. Engineers should be prepared to learn about clinical terminology, health data standards, privacy requirements, and the workflows of the people who use the software. Attention to detail, clear communication, curiosity, and a willingness to ask questions are especially valuable.

Safety, Privacy, and Reliability

Health care software may handle sensitive personal information or contribute to decisions about care. Protecting that information means designing for privacy and security from the start, limiting access appropriately, and responding responsibly to vulnerabilities.

Reliability matters, too. Teams use processes such as code review, automated and manual testing, risk analysis, and careful release management to reduce defects. Software intended for medical use may also be subject to regulatory requirements, depending on its purpose, features, and market. Engineers typically work with compliance and quality teams to understand which rules apply.

How to Become a Medical Software Engineer

Many people enter the field with a degree in computer science, software engineering, biomedical engineering, or a related discipline. A degree is not the only possible path: practical experience, a strong portfolio, and relevant technical training can also help candidates qualify for some roles.

Useful preparation includes building software projects, learning about secure coding and software testing, and developing an understanding of health care technology. Experience in internships, research labs, health technology companies, or projects involving clinical data can provide helpful context. Since the field is interdisciplinary, engineers should expect to keep learning throughout their careers.

Challenges and Rewards

Medical software projects can be complex. Teams may need to integrate with older systems, handle inconsistent data, meet demanding reliability expectations, and balance the needs of different users. Changes can require careful review because even a small update may affect established workflows.

At the same time, the work can be meaningful. Well-designed software can help reduce administrative burdens, improve access to information, support communication, and make health services easier to use. The greatest impact often comes from solving practical problems in close partnership with the people who provide and receive care.

The Future of Medical Software Engineering

Health care technology continues to evolve, with growing interest in connected devices, remote care, data interoperability, and artificial intelligence. These developments create opportunities as well as responsibilities. Engineers must evaluate new technologies carefully, communicate their limitations, protect patient information, and ensure that tools are tested in appropriate settings.

Medical software engineering brings technology and health care together. It is a strong fit for people who enjoy building reliable systems, solving complex problems, and working with others to create tools that serve real human needs.


Top 9 FAQs About Becoming a Medical Software Engineer

  1. What does a medical software engineer do?
  2. What skills does a medical software engineer need?
  3. What degree do you need to become a medical software engineer?
  4. How do you become a medical software engineer?
  5. What programming languages do medical software engineers use?
  6. Where do medical software engineers work?
  7. How much does a medical software engineer make?
  8. What regulations and standards apply to medical software engineering?
  9. What is the difference between a medical software engineer and a biomedical engineer?

What does a medical software engineer do?

A medical software engineer designs, develops, tests, and maintains software used in health care. This may include electronic health record systems, telehealth apps, medical device software, and tools that help clinicians analyze health data. The role often involves working with doctors, product teams, and quality specialists to ensure software is reliable, secure, easy to use, and suited to clinical workflows. Because these products may affect patient care, medical software engineers also pay close attention to privacy, safety, and applicable regulations.

What skills does a medical software engineer need?

A medical software engineer needs strong programming skills, a solid understanding of software design, databases, testing, and cybersecurity, plus the ability to build reliable, user-friendly systems. Knowledge of health care workflows, medical terminology, patient privacy, and relevant data standards is also valuable. Because these systems can affect care, attention to detail, clear communication, problem-solving, and collaboration with clinicians and other specialists are essential.

What degree do you need to become a medical software engineer?

There’s no single degree required to become a medical software engineer. Many professionals earn a bachelor’s degree in computer science, software engineering, biomedical engineering, or a related field, while others enter through practical experience, specialized training, or a strong portfolio of software projects. Coursework or experience in health care technology, data privacy, cybersecurity, and medical device regulations can also be helpful, depending on the role.

How do you become a medical software engineer?

To become a medical software engineer, build a strong foundation in software development through a degree in computer science, software engineering, biomedical engineering, or a related field—or through practical training and project experience. Learn programming, databases, APIs, testing, and secure software practices, then explore health care topics such as clinical workflows, health data privacy, and interoperability standards. Internships, personal projects, research, or entry-level roles in health technology can help you gain relevant experience. Because requirements vary by employer and product, keep learning and be ready to collaborate with clinicians, designers, and quality and regulatory teams.

What programming languages do medical software engineers use?

Medical software engineers use different programming languages depending on the product they build. Python is common in data analysis, automation, and machine learning; Java and C# are often used for enterprise health care systems; and JavaScript or TypeScript are widely used for web applications. Engineers developing medical devices or other embedded systems may use C or C++, while mobile app teams may use Swift for iOS or Kotlin for Android. SQL is also useful for working with databases. The best language for a role depends on the technology stack, safety requirements, and needs of the project.

Where do medical software engineers work?

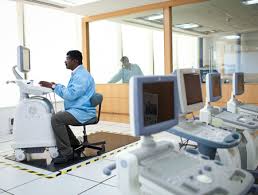
Medical software engineers work in a variety of settings, including health technology companies, hospitals and health systems, medical device manufacturers, pharmaceutical and biotechnology companies, research institutions, and government agencies. Some work for software firms that build electronic health records, telehealth platforms, or clinical data tools, while others develop software embedded in devices such as imaging equipment or patient monitors. Many roles are office-based or remote, with regular collaboration with clinicians, product teams, and quality or regulatory specialists.

How much does a medical software engineer make?

In the United States, a medical software engineer’s salary can vary widely based on experience, location, employer, and the type of software they develop. Many roles pay roughly $90,000 to $160,000 a year, while senior positions or jobs at large technology and medical-device companies may offer more, sometimes with bonuses or stock compensation. Salaries also depend on specialized skills, such as medical-device software, cybersecurity, or health data systems, so reviewing current job listings in your area is the best way to estimate pay.

What regulations and standards apply to medical software engineering?

The regulations and standards that apply depend on the software’s intended use, features, and role in a health care organization. In the U.S., software that meets the definition of a medical device may be subject to FDA requirements, including applicable device controls and the Quality Management System Regulation (QMSR), effective February 2, 2026, which incorporates ISO 13485:2016. Common engineering standards include IEC 62304 for medical-device software life-cycle processes, ISO 14971 for risk management, and IEC 62366-1 for usability engineering. HIPAA privacy and security requirements may apply when an organization handles protected health information, while FDA guidance and standards such as IEC 81001-5-1 can inform cybersecurity practices. Requirements vary by product and context, so teams should consult regulatory and quality specialists early; standards such as HL7 FHIR or DICOM may support interoperability but do not, by themselves, establish regulatory compliance.

What is the difference between a medical software engineer and a biomedical engineer?

A medical software engineer focuses on designing and developing software for health care, such as electronic health records, telehealth platforms, medical-device applications, and clinical data tools. A biomedical engineer applies engineering principles more broadly to health and medicine, often working on medical devices, prosthetics, imaging equipment, biomaterials, or other technologies that interact with the human body. The fields can overlap—for example, a biomedical engineer may help develop a device while a medical software engineer builds the software that controls it—but their typical training and day-to-day work differ.
microsoft cloud security

Microsoft Cloud Security: Essential Strategies for Protecting Your Data and Workloads

Microsoft Cloud Security: A Practical Guide

Microsoft cloud services—including Azure, Microsoft 365, and services built on the Microsoft cloud—offer organizations flexible ways to run applications, collaborate, and manage data. Protecting those environments takes more than turning on a security feature. It requires clear ownership, strong identity controls, thoughtful configuration, and ongoing monitoring.

Understand the Shared Responsibility Model

Cloud security is a shared responsibility between Microsoft and its customers. Microsoft secures the underlying cloud infrastructure, while customers remain responsible for areas such as user accounts, access permissions, data, and many service configurations. The exact division of responsibility depends on the service being used. For example, a managed software service generally requires less infrastructure management by the customer than a virtual machine running in Azure.

Before deploying a workload, identify what Microsoft manages and what your organization must secure. This helps prevent gaps in areas such as patching, backups, access control, and data protection.

Make Identity Your First Line of Defense

Compromised accounts are a common path into cloud environments, so identity protection should be a priority. Microsoft Entra ID provides identity and access management capabilities for Microsoft cloud services and other applications.

  • Require multifactor authentication, especially for administrators and remote access.
  • Use conditional access policies to evaluate factors such as user, device, location, and risk.
  • Apply least privilege: give users and applications only the access they need.
  • Use privileged identity management practices to limit standing administrator access.
  • Review inactive accounts, service principals, and access permissions regularly.

Strong identity controls can reduce the impact of stolen passwords and help limit an attacker’s ability to move through an environment.

Protect Azure Workloads and Configurations

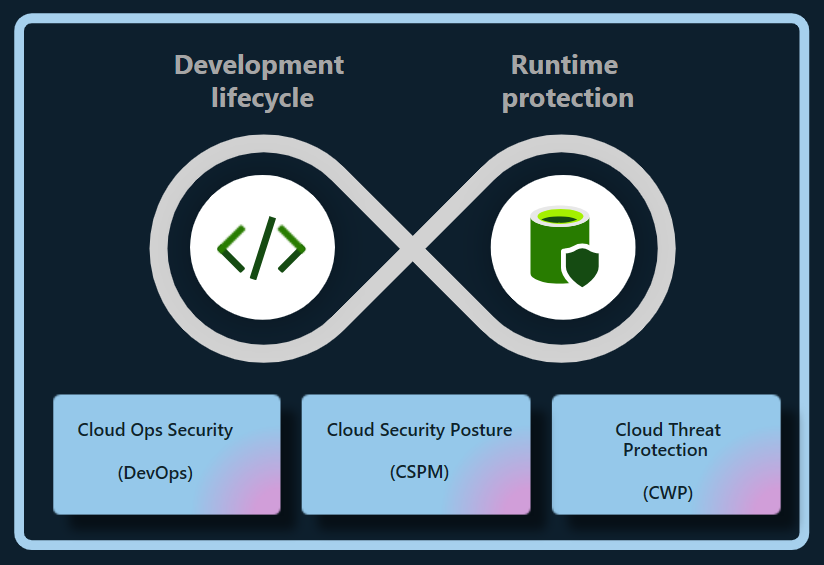
Misconfigured cloud resources can expose systems or data even when the underlying platform is secure. In Azure, organizations should establish secure configuration standards for subscriptions, networks, storage, virtual machines, and databases. Azure Policy can help enforce organizational requirements, while Microsoft Defender for Cloud can provide security recommendations and threat protection capabilities for supported resources.

Important practices include restricting public access where it is not required, using network segmentation, securing administrative connections, encrypting sensitive data, and keeping workloads patched. Backups should be protected from accidental deletion and ransomware, and recovery plans should be tested rather than assumed to work.

Secure Microsoft 365 and Collaboration

Microsoft 365 brings together email, file storage, meetings, and collaboration tools. Security settings should reflect how people actually work while limiting unnecessary exposure. Review sharing defaults in services such as SharePoint and OneDrive, manage external collaboration, and establish retention and access policies appropriate to the organization.

Microsoft Defender for Office 365 can help protect against threats such as phishing and malicious attachments, depending on the plan and configuration. Security awareness training and clear procedures for reporting suspicious messages remain important because technical controls cannot prevent every social-engineering attempt.

Protect and Govern Data

Cloud security also depends on knowing what data an organization stores and who can access it. Microsoft Purview includes data governance, information protection, and compliance capabilities, with features varying by product and license. Organizations can use classification and sensitivity labels to help identify and protect important information, and apply data loss prevention policies to reduce inappropriate sharing.

Start by identifying sensitive data, defining who should be able to access it, and deciding how long it should be retained. Policies should be tested with users and business teams to avoid disrupting legitimate work.

Monitor, Detect, and Respond

Security controls are most effective when organizations can detect suspicious activity and respond quickly. Microsoft Defender products provide security capabilities across various environments, while Microsoft Sentinel is a cloud-based security information and event management (SIEM) and security orchestration, automation, and response (SOAR) platform. The tools an organization needs depend on its environment, risk profile, and licensing.

Establish a process for reviewing alerts, investigating incidents, and escalating serious findings. Keep audit logging enabled where appropriate, define incident-response roles, and practice response scenarios such as account compromise, data exposure, and ransomware. Monitoring without a clear response process can leave important alerts unattended.

Build a Sustainable Security Program

Microsoft cloud security is not a one-time setup. Services change, employees join and leave, and business requirements evolve. A sustainable program includes regular access reviews, configuration assessments, vulnerability management, backup testing, and updates to policies and incident-response plans.

Begin with the basics: secure administrator accounts, enable strong authentication, reduce excessive permissions, protect sensitive data, and establish reliable monitoring. Then use Microsoft’s security guidance and the controls available in your specific services to improve protection over time. Because features and licensing can change, verify current capabilities and requirements in Microsoft’s official documentation before designing or purchasing a solution.


Top 9 Benefits of Microsoft Cloud Security for Your Business

  1. Scales with your business needs
  2. Offers strong identity controls
  3. Supports multifactor authentication
  4. Helps protect data with encryption
  5. Provides built-in threat detection
  6. Integrates with Microsoft 365
  7. Enables centralized security management
  8. Supports compliance and governance
  9. Offers tools for monitoring and response


5 Challenges of Microsoft Cloud Security: Complexity, Costs, and Dependence

  1. Can be complex to configure and manage.
  2. Advanced security features may require costly licenses.
  3. Misconfigurations can expose data and services.
  4. Dependence on Microsoft can limit flexibility.
  5. Requires ongoing expertise and monitoring.

Scales with your business needs

Microsoft cloud security can scale alongside your business, helping you adjust protection as your team, data, and workloads grow or change. You can add security capabilities, expand coverage across cloud services, and adapt access controls and policies as new needs arise—without having to build and maintain all the supporting infrastructure yourself. This flexibility can help keep security aligned with your business while making it easier to manage changing requirements.

Offers strong identity controls

Microsoft cloud security offers strong identity controls that help organizations protect accounts, apps, and data. With tools such as Microsoft Entra ID, teams can require multifactor authentication, apply access policies based on user and device risk, and limit permissions to only what each person needs. These safeguards make it harder for unauthorized users to gain access and help reduce the impact of compromised credentials.

Supports multifactor authentication

Microsoft cloud security supports multifactor authentication (MFA), adding an extra layer of protection beyond a password. Users may be asked to confirm their identity with an authenticator app, a security key, or another approved method. This makes it harder for someone to access an account with a stolen or guessed password and helps organizations better protect email, files, and cloud resources.

Helps protect data with encryption

Microsoft cloud security helps protect data with encryption, making information harder to read if it is accessed without authorization. Encryption can safeguard data while it is stored and while it moves between services or devices. With appropriate configuration and key-management practices, organizations can add an important layer of protection for sensitive information across their cloud environments.

Provides built-in threat detection

Microsoft cloud security includes built-in threat detection capabilities that help identify suspicious activity across supported services, users, devices, and workloads. These tools can analyze signals and surface alerts about potential risks—such as unusual sign-ins or malicious behavior—so security teams can investigate and respond more quickly. When configured to fit an organization’s environment, built-in detection can strengthen visibility without requiring every monitoring capability to be assembled from scratch.

Integrates with Microsoft 365

Microsoft cloud security integrates seamlessly with Microsoft 365, helping organizations protect email, files, meetings, and user accounts within the tools employees already use. This integration can bring security policies, identity controls, and threat protection together across services such as Outlook, Teams, SharePoint, and OneDrive. As a result, administrators can manage access more consistently, respond to potential threats with greater visibility, and help safeguard sensitive information without disrupting everyday collaboration.

Enables centralized security management

Microsoft cloud security enables centralized security management by bringing key security settings, policies, alerts, and monitoring tools together across cloud services. This gives IT and security teams a clearer view of their environment and helps them apply consistent protections, manage access, and respond to potential threats more efficiently. Centralized oversight can also make it easier to identify gaps and coordinate security practices across users, devices, and workloads.

Supports compliance and governance

Microsoft cloud security supports compliance and governance by providing tools to help organizations protect sensitive information, manage access, apply data-retention policies, and monitor activity. Services such as Microsoft Purview can help classify and govern data, while built-in security and compliance features can support an organization’s efforts to meet applicable regulatory and internal requirements. The right controls depend on the Microsoft services in use, the organization’s configuration, and its specific compliance obligations.

Offers tools for monitoring and response

Microsoft cloud security offers tools that help organizations monitor activity, detect potential threats, and respond to incidents. Services such as Microsoft Defender and Microsoft Sentinel can bring security signals together, surface suspicious behavior, and support investigation and response workflows. With appropriate configuration and ongoing oversight, these tools can help teams identify problems sooner and coordinate a more effective response.

Can be complex to configure and manage.

One drawback of Microsoft cloud security is that it can be complex to configure and manage. Services such as Azure, Microsoft 365, and Microsoft Entra ID offer many security settings, policies, and tools, and the right setup depends on an organization’s needs and licensing. Misconfigured controls or unclear responsibilities can leave gaps in protection, so teams may need specialized expertise, ongoing training, and regular reviews to manage the environment effectively.

Advanced security features may require costly licenses.

Advanced security features in Microsoft cloud services can come at a significant additional cost. Capabilities such as enhanced threat detection, identity protection, compliance tools, and advanced data protection may require higher-tier subscriptions or separate licenses. For organizations with tight budgets, these costs can make it difficult to deploy the full set of recommended safeguards, so it’s important to compare licensing options and prioritize features based on risk and business needs.

Misconfigurations can expose data and services.

One potential drawback of Microsoft cloud security is that misconfigurations can expose sensitive data and services to unauthorized access. A storage account with overly permissive access, an exposed network endpoint, or an incorrectly assigned user role can create security gaps—even when the underlying Microsoft platform is operating securely. Preventing these issues requires careful setup, regular configuration reviews, and ongoing monitoring.

Dependence on Microsoft can limit flexibility.

Relying heavily on Microsoft’s cloud security tools can limit an organization’s flexibility. Teams may find it difficult or costly to switch providers, integrate competing products, or adapt workflows built around Microsoft-specific services. This dependence can also make it harder to respond to changing business needs or negotiate terms, so organizations should consider portability and interoperability when designing their cloud security strategy.

Requires ongoing expertise and monitoring.

Microsoft cloud security requires ongoing expertise and monitoring to remain effective. Services, threats, and security settings change over time, so organizations need knowledgeable staff to review configurations, manage access, investigate alerts, and respond to incidents. Without consistent oversight, misconfigurations or suspicious activity may go unnoticed, leaving sensitive data and systems at risk.

cloud tech solutions

Cloud Tech Solutions: A Practical Guide for Modern Businesses

Cloud Tech Solutions: A Smarter Way to Work

Cloud technology has changed how businesses store information, run applications, and support their teams. Instead of relying only on equipment located in an office, organizations can use internet-based services to access computing resources when and where they need them. The result can be a more flexible, scalable approach to technology.

What Are Cloud Tech Solutions?

Cloud tech solutions are services and tools delivered over the internet. They may include data storage, software, servers, databases, networking, backup, and security tools. Businesses can use these services individually or combine them into a broader cloud environment.

Cloud services are commonly grouped into three categories:

  • Software as a Service (SaaS): Ready-to-use applications accessed online, such as email, collaboration tools, and customer management software.
  • Infrastructure as a Service (IaaS): On-demand computing resources, such as virtual servers, storage, and networking.
  • Platform as a Service (PaaS): Tools and environments developers use to build, test, and deploy applications.

Benefits of Cloud Technology

Scale as Needs Change

Cloud resources can often be increased or reduced as business demands shift. This flexibility can help organizations respond to seasonal changes, new projects, or growth without making every technology decision around a fixed set of in-house equipment.

Support Flexible Work

With the right setup, employees can securely access files and applications from different locations and devices. Cloud-based collaboration tools can also help teams share information and work together in real time.

Improve Business Continuity

Cloud backup and recovery services can help organizations restore important data and systems after an outage or other disruption. A well-designed continuity plan should define what needs protection, how often data is backed up, and how recovery will be tested.

Manage Costs More Effectively

Many cloud services use subscription or consumption-based pricing. This can reduce the need for large upfront hardware purchases, though costs should be monitored carefully. Unused resources, data transfers, and premium features can add up if they are not managed.

Security and Reliability Matter

Moving to the cloud does not automatically make systems secure. Providers typically protect their underlying infrastructure, while customers remain responsible for areas such as user access, data handling, application settings, and device security. Responsibilities vary by service, so it is important to understand the arrangement.

Good cloud security practices include using multifactor authentication, applying least-privilege access, encrypting sensitive data, keeping systems updated, and reviewing activity logs. Organizations should also consider compliance requirements and the location of their data before choosing services.

Choosing the Right Cloud Approach

There is no single cloud setup that works for every organization. Some businesses use a public cloud, where services are shared across customers. Others choose a private cloud for greater control, or a hybrid approach that combines cloud services with on-site systems.

Before selecting a solution, consider:

  • Which business problems the technology should address
  • How much storage, computing power, and availability are needed
  • Security, privacy, and compliance requirements
  • How the cloud service will connect with existing systems
  • Expected costs, including ongoing management and support
  • How data can be backed up, recovered, or moved in the future

Plan the Transition

A successful cloud transition starts with a clear plan. Begin by reviewing existing applications, data, and dependencies. Then prioritize workloads based on business value, risk, and complexity. Testing a small project first can reveal potential issues before a larger migration begins.

After migration, ongoing management is essential. Regularly review access permissions, performance, backup results, and spending. A cloud environment should evolve as the organization’s needs change.

Make Cloud Technology Work for Your Business

Cloud tech solutions can help organizations become more adaptable, support distributed teams, and access powerful tools without managing every part of the underlying infrastructure. The best results come from matching technology to real business needs and giving equal attention to planning, security, and ongoing oversight.


9 Essential Tips for Optimizing Your Cloud Technology Solutions

  1. Choose a cloud model that fits your needs.
  2. Set clear goals before migrating.
  3. Use multi-factor authentication.
  4. Encrypt data in transit and at rest.
  5. Automate backups and recovery tests.
  6. Monitor costs and set budget alerts.
  7. Scale resources to match demand.
  8. Review access permissions regularly.
  9. Plan for outages with redundancy.

Choose a cloud model that fits your needs.

Choose a cloud model that fits your needs by considering how much control, flexibility, and support your organization requires. A public cloud can be a cost-effective choice for scalable services, while a private cloud may suit businesses with strict security or compliance requirements. A hybrid cloud combines both, letting you keep sensitive workloads in a private environment while using public cloud resources for other tasks. Compare your options based on your budget, existing systems, security needs, and plans for growth.

Set clear goals before migrating.

Before moving to the cloud, define what you want the migration to achieve. Clear goals—such as improving application performance, supporting remote work, strengthening disaster recovery, or reducing infrastructure costs—help guide decisions about which services to choose and what to move first. Set measurable targets, identify potential risks, and agree on how success will be evaluated. With a well-defined plan, your team can keep the migration focused, manage costs, and confirm that the new cloud environment delivers real business value.

Use multi-factor authentication.

Use multi-factor authentication (MFA) to add an extra layer of protection to your cloud accounts. In addition to a password, MFA requires a second form of verification, such as an authenticator app, security key, or one-time code. This can help prevent unauthorized access even if a password is stolen or guessed. Enable MFA for all cloud services that support it, especially administrator and business accounts, and choose a secure verification method whenever possible.

Encrypt data in transit and at rest.

Encrypting data both in transit and at rest helps protect sensitive information from unauthorized access. Data in transit—such as information moving between a user’s device and a cloud service—should be protected with secure protocols like TLS. Data at rest, including files stored in cloud databases or backups, should also be encrypted. Use strong encryption settings, manage encryption keys carefully, and review your cloud provider’s security options to help keep information protected throughout its lifecycle.

Automate backups and recovery tests.

Automate backups and recovery tests to help protect important data and confirm it can be restored when needed. Set backups to run on a regular schedule, monitor them for failures, and test recovery procedures periodically. These checks can reveal missing files, outdated backup copies, or setup problems before an outage or cyberattack makes recovery urgent.

Monitor costs and set budget alerts.

Regularly monitoring cloud spending can help prevent small, unexpected charges from turning into a large bill. Review usage reports to spot idle resources, sudden increases, or services that are no longer needed, and set budget alerts to notify your team when spending approaches a chosen limit. Alerts won’t automatically stop charges, but they give you time to investigate and adjust before costs climb further.

Scale resources to match demand.

Scale cloud resources to match demand so your systems have the capacity they need without paying for more than necessary. During busy periods, you can add computing power or storage to maintain performance; when demand drops, scale back to reduce costs. Monitoring usage and setting clear scaling rules helps keep services responsive, efficient, and budget-friendly.

Review access permissions regularly.

Review access permissions regularly to make sure employees and vendors can access only the cloud resources they need. Remove accounts for people who have left the organization, update permissions when roles change, and check for inactive or overly privileged accounts. Routine reviews help reduce the risk of unauthorized access and keep sensitive data better protected.

Plan for outages with redundancy.

Plan for outages by building redundancy into your cloud environment. Use backups, failover systems, and resources in separate availability zones or regions so a single service disruption doesn’t bring critical operations to a halt. Test your recovery plan regularly, and make sure your team knows how to restore services and data quickly when an outage occurs.

nydfs cybersecurity

Enhancing Financial Security: The Role of NYDFS in Cybersecurity

The Role of NYDFS in Cybersecurity

The Role of NYDFS in Cybersecurity

As cyber threats continue to evolve and become more sophisticated, the New York Department of Financial Services (NYDFS) plays a crucial role in ensuring the cybersecurity of financial institutions operating within the state.

The NYDFS has implemented stringent regulations and guidelines to safeguard sensitive financial data and protect consumers from cyber attacks. These regulations require financial institutions to establish robust cybersecurity programs, conduct regular risk assessments, and report any cybersecurity incidents promptly.

One of the key initiatives introduced by the NYDFS is the Cybersecurity Regulation (23 NYCRR 500), which sets forth minimum standards for cybersecurity practices that financial institutions must adhere to. This regulation includes requirements such as multi-factor authentication, encryption of sensitive data, and regular cybersecurity training for employees.

In addition to setting regulatory standards, the NYDFS actively monitors compliance with these regulations through examinations and assessments. Financial institutions are required to submit annual certifications of their compliance with the Cybersecurity Regulation, demonstrating their commitment to maintaining strong cybersecurity measures.

Furthermore, the NYDFS collaborates with other regulatory agencies and law enforcement authorities to share information on emerging cyber threats and coordinate responses to cyber incidents. By fostering a culture of information sharing and cooperation, the NYDFS aims to enhance the overall resilience of the financial sector against cyber threats.

In conclusion, the NYDFS plays a vital role in promoting cybersecurity within the financial industry and protecting both institutions and consumers from cyber risks. Through its proactive approach to regulation and oversight, the NYDFS helps ensure that New York remains at the forefront of cybersecurity best practices.


6 Essential Tips for Strengthening Cybersecurity Compliance with NYDFS Regulations

  1. Regularly update software and systems to protect against vulnerabilities.
  2. Implement strong password policies and multi-factor authentication.
  3. Train employees on cybersecurity best practices and how to identify phishing attempts.
  4. Encrypt sensitive data both in transit and at rest.
  5. Conduct regular security assessments and audits to identify weaknesses.
  6. Establish a an incident response plan to quickly respond to and mitigate cybersecurity incidents.

Regularly update software and systems to protect against vulnerabilities.

Regularly updating software and systems is a critical tip in NYDFS cybersecurity practices to safeguard against vulnerabilities. By staying current with software patches and system updates, financial institutions can address known security weaknesses and reduce the risk of exploitation by cyber attackers. This proactive approach helps ensure that systems remain resilient to emerging threats and maintain the integrity of sensitive financial data. Compliance with this best practice not only enhances cybersecurity posture but also demonstrates a commitment to maintaining a secure environment for both the institution and its customers as mandated by NYDFS regulations.

Implement strong password policies and multi-factor authentication.

To enhance cybersecurity measures in compliance with NYDFS regulations, it is crucial for financial institutions to implement strong password policies and multi-factor authentication. By enforcing complex password requirements and requiring an additional layer of verification through multi-factor authentication, institutions can significantly reduce the risk of unauthorized access to sensitive data. These practices not only bolster security but also demonstrate a commitment to safeguarding confidential information and meeting the stringent cybersecurity standards set forth by the NYDFS.

Train employees on cybersecurity best practices and how to identify phishing attempts.

Training employees on cybersecurity best practices is essential in strengthening an organization’s defense against cyber threats. By educating staff members on how to identify phishing attempts, such as suspicious emails or messages, companies can empower their workforce to act as the first line of defense against potential security breaches. Equipping employees with the knowledge and skills to recognize and report phishing attempts not only helps protect sensitive data but also contributes to creating a culture of cybersecurity awareness within the organization.

Encrypt sensitive data both in transit and at rest.

It is crucial for financial institutions under NYDFS regulation to encrypt sensitive data both in transit and at rest. Encrypting data in transit ensures that information remains secure while being transferred between systems or devices, protecting it from interception by malicious actors. Similarly, encrypting data at rest safeguards stored information from unauthorized access, adding an extra layer of security to prevent data breaches. By implementing robust encryption practices, financial institutions can enhance the protection of sensitive data and comply with NYDFS cybersecurity requirements effectively.

Conduct regular security assessments and audits to identify weaknesses.

Regular security assessments and audits are essential components of a comprehensive cybersecurity strategy recommended by the NYDFS. By conducting these assessments on a regular basis, financial institutions can proactively identify vulnerabilities and weaknesses in their systems and processes. This proactive approach allows organizations to address potential security gaps before they are exploited by cyber attackers, helping to strengthen overall cybersecurity defenses and protect sensitive data from unauthorized access or breaches.

Establish a an incident response plan to quickly respond to and mitigate cybersecurity incidents.

Establishing an incident response plan is a critical component of NYDFS cybersecurity guidelines. By having a well-defined plan in place, financial institutions can swiftly respond to and mitigate cybersecurity incidents, minimizing potential damages and disruptions. This proactive approach not only helps in containing the impact of security breaches but also demonstrates a commitment to effective risk management and compliance with regulatory requirements. Having an incident response plan ensures that organizations are prepared to handle cyber threats promptly and efficiently, safeguarding both their own operations and the sensitive data of their customers.

tech solutions company

Empowering Businesses with Cutting-Edge Tech Solutions: The Role of a Leading Tech Solutions Company

Tech Solutions Company: Revolutionizing the IT Landscape

Tech Solutions Company: Revolutionizing the IT Landscape

In today’s fast-paced digital world, businesses are constantly seeking innovative tech solutions to stay ahead of the competition. This is where tech solutions companies play a crucial role in transforming the IT landscape and driving business success.

The Role of a Tech Solutions Company

A tech solutions company specializes in providing a wide range of services to address the diverse IT needs of businesses. From IT consultancy and network management to cybersecurity and software development, these companies offer comprehensive solutions tailored to meet specific requirements.

Driving Innovation and Efficiency

By leveraging cutting-edge technologies and industry best practices, tech solutions companies help organizations streamline their operations, enhance productivity, and achieve greater efficiency. Through custom software development, cloud solutions, and advanced analytics, these companies empower businesses to make informed decisions and adapt to evolving market trends.

Ensuring Data Security and Compliance

With the increasing threat of cyber attacks and data breaches, data security has become a top priority for businesses of all sizes. Tech solutions companies play a vital role in implementing robust cybersecurity measures to safeguard sensitive information and ensure regulatory compliance. By conducting regular security audits and providing training programs, these companies help mitigate risks and protect valuable assets.

Collaboration for Success

Collaboration is at the heart of every successful partnership between a business and a tech solutions company. By understanding the unique needs and goals of their clients, these companies work closely with organizations to develop tailored strategies that drive growth and innovation. Through open communication, continuous support, and proactive problem-solving, tech solutions companies build long-lasting relationships built on trust and mutual success.

In conclusion, tech solutions companies play a pivotal role in shaping the future of technology-driven businesses. With their expertise, experience, and commitment to excellence, these companies are revolutionizing the IT landscape and helping organizations thrive in an increasingly digital world.


7 Essential Tips for Thriving as a Tech Solutions Company

  1. Stay updated with the latest technology trends
  2. Focus on providing innovative and user-friendly solutions
  3. Develop a strong online presence through website and social media
  4. Offer excellent customer support to build trust and loyalty
  5. Collaborate with other tech companies for mutual growth opportunities
  6. Invest in research and development for continuous improvement
  7. Regularly assess and adapt your business strategies to stay competitive

Staying updated with the latest technology trends is essential for a tech solutions company to remain competitive and provide cutting-edge services to its clients. By keeping abreast of emerging technologies, such as artificial intelligence, blockchain, and Internet of Things, the company can offer innovative solutions that meet the evolving needs of businesses. Continuous learning and adaptation to new trends not only enhance the company’s expertise but also ensure that it stays ahead in a rapidly changing technological landscape.

Focus on providing innovative and user-friendly solutions

To stay competitive in the rapidly evolving tech industry, it is crucial for tech solutions companies to prioritize providing innovative and user-friendly solutions. By focusing on innovation, these companies can introduce cutting-edge technologies and creative approaches that address the ever-changing needs of their clients. Simultaneously, emphasizing user-friendliness ensures that the solutions are intuitive, easy to navigate, and tailored to enhance the overall user experience. This dual focus not only sets tech solutions companies apart from their competitors but also fosters long-term client satisfaction and loyalty.

Develop a strong online presence through website and social media

In today’s digital age, developing a strong online presence through a well-designed website and active social media channels is essential for any tech solutions company looking to reach a wider audience and showcase its expertise. A professional website serves as a virtual storefront, providing valuable information about the company’s services, portfolio, and contact details. Meanwhile, engaging with potential clients and industry peers on social media platforms not only increases brand visibility but also allows for direct communication and feedback. By leveraging the power of the internet, tech solutions companies can establish credibility, build relationships, and ultimately attract new business opportunities in a competitive market.

Offer excellent customer support to build trust and loyalty

Providing excellent customer support is a critical aspect of a tech solutions company’s success. By offering responsive and knowledgeable assistance to clients, businesses can build trust and loyalty. Effective customer support not only helps resolve issues promptly but also demonstrates a commitment to customer satisfaction. Building strong relationships with clients through exceptional support fosters long-term loyalty and enhances the reputation of the company in the competitive tech industry.

Collaborate with other tech companies for mutual growth opportunities

Collaborating with other tech companies can offer valuable growth opportunities for a tech solutions company. By forming strategic partnerships, sharing resources, and leveraging complementary expertise, tech companies can expand their reach, access new markets, and enhance their service offerings. Collaborations can lead to innovative solutions, increased efficiency, and a competitive edge in the ever-evolving tech industry. Through mutual support and collaboration, tech companies can achieve shared goals and drive collective success in the dynamic world of technology.

Invest in research and development for continuous improvement

Investing in research and development is a crucial strategy for tech solutions companies to achieve continuous improvement and stay ahead in the rapidly evolving IT industry. By dedicating resources to R&D, companies can innovate, explore new technologies, and enhance their service offerings. This proactive approach not only fosters creativity and problem-solving but also allows businesses to adapt to changing market demands, improve efficiency, and deliver cutting-edge solutions that meet the evolving needs of their clients.

Regularly assess and adapt your business strategies to stay competitive

In the rapidly evolving tech landscape, it is essential for tech solutions companies to regularly assess and adapt their business strategies to stay competitive. By continuously evaluating market trends, customer needs, and emerging technologies, these companies can proactively adjust their approaches to meet evolving demands and maintain a competitive edge. Embracing a culture of innovation and agility allows tech solutions companies to stay ahead of the curve, deliver cutting-edge solutions, and drive sustainable growth in a dynamic industry.

cybersecurity security solutions

Enhancing Data Protection: Cybersecurity Security Solutions for Today’s Threat Landscape

The Importance of Cybersecurity Security Solutions

The Importance of Cybersecurity Security Solutions

In today’s digital age, cybersecurity has become a critical concern for individuals and businesses alike. With the increasing frequency and sophistication of cyber threats, it is essential to implement robust security solutions to protect sensitive data and prevent unauthorized access.

Cybersecurity security solutions encompass a range of technologies, practices, and policies designed to safeguard networks, devices, and data from cyber attacks. These solutions help identify potential vulnerabilities, detect malicious activities, and respond effectively to security incidents.

Key Components of Cybersecurity Security Solutions

Effective cybersecurity security solutions typically include the following key components:

  • Firewalls: Firewalls act as a barrier between internal networks and external threats, monitoring and controlling incoming and outgoing network traffic.
  • Antivirus Software: Antivirus software helps detect and remove malware, viruses, and other malicious programs that can compromise system security.
  • Encryption: Encryption technologies protect data by converting it into a secure format that can only be accessed with the appropriate decryption key.
  • Intrusion Detection Systems (IDS) and Intrusion Prevention Systems (IPS): IDS and IPS monitor network traffic for suspicious activities and take action to prevent potential threats from compromising network security.
  • Security Awareness Training: Educating employees about cybersecurity best practices is crucial in preventing social engineering attacks and human errors that could lead to data breaches.

The Benefits of Implementing Cybersecurity Security Solutions

By investing in cybersecurity security solutions, organizations can enjoy several benefits, including:

  • Data Protection: Safeguarding sensitive information from unauthorized access or theft.
  • Risk Mitigation: Reducing the likelihood of costly data breaches or cyber attacks that could harm reputation and financial stability.
  • Compliance: Ensuring compliance with industry regulations and standards related to data privacy and security.
  • Business Continuity: Minimizing downtime due to cyber incidents by proactively identifying and addressing security vulnerabilities.

Conclusion

In conclusion, cybersecurity security solutions play a vital role in protecting organizations against evolving cyber threats. By implementing comprehensive security measures that address potential risks proactively, businesses can enhance their resilience in the face of cyber attacks and maintain trust with customers. Prioritizing cybersecurity is not just a necessity but a strategic investment in long-term success in today’s interconnected digital landscape.


8 Essential Tips for Strengthening Your Cybersecurity Defenses

  1. Keep your software and operating systems updated regularly.
  2. Use strong, unique passwords for each account and enable two-factor authentication when possible.
  3. Be cautious of suspicious emails or messages that may contain phishing attempts.
  4. Regularly back up your data to a secure location to prevent data loss in case of a cyber attack.
  5. Use reputable antivirus software and keep it updated to protect against malware.
  6. Secure your home network with a strong password and encryption.
  7. Limit the amount of personal information you share online to reduce the risk of identity theft.
  8. Educate yourself on common cybersecurity threats and best practices for staying safe online.

Keep your software and operating systems updated regularly.

Keeping your software and operating systems updated regularly is a crucial tip for maintaining strong cybersecurity security solutions. Software updates often include patches that address known vulnerabilities, reducing the risk of exploitation by cyber attackers. By staying current with updates, you ensure that your systems have the latest security features and enhancements, enhancing their resilience against potential threats. Regular updates also help to improve system performance and reliability, ensuring a smoother and more secure computing experience overall.

Use strong, unique passwords for each account and enable two-factor authentication when possible.

It is crucial to enhance your cybersecurity posture by following best practices such as using strong, unique passwords for each account and enabling two-factor authentication whenever possible. By creating complex passwords that are unique to each account, you can significantly reduce the risk of unauthorized access to your sensitive data. Additionally, implementing two-factor authentication adds an extra layer of security by requiring a secondary verification method, such as a code sent to your mobile device, further fortifying your accounts against potential cyber threats. Prioritizing these measures helps bolster your online security and safeguard your digital assets effectively.

Be cautious of suspicious emails or messages that may contain phishing attempts.

One crucial tip for enhancing cybersecurity security solutions is to remain vigilant and cautious of suspicious emails or messages that may contain phishing attempts. Cybercriminals often use deceptive tactics to trick individuals into divulging sensitive information or clicking on malicious links. By staying alert and verifying the authenticity of unexpected communications, individuals can significantly reduce the risk of falling victim to phishing attacks and protect their personal and organizational data from unauthorized access.

Regularly back up your data to a secure location to prevent data loss in case of a cyber attack.

Regularly backing up your data to a secure location is a crucial tip in cybersecurity security solutions. By creating consistent backups of your important files and storing them in a safe and separate location, you can mitigate the risk of data loss in the event of a cyber attack or system failure. This proactive measure ensures that even if your primary data is compromised, you can restore from backups and resume normal operations quickly, minimizing downtime and potential damage to your business or personal information.

Use reputable antivirus software and keep it updated to protect against malware.

To enhance your cybersecurity defenses, it is crucial to utilize trusted antivirus software and ensure it remains up to date. By employing reputable antivirus solutions and regularly updating them, you can effectively shield your systems from malware threats. These software programs play a pivotal role in detecting and removing malicious programs that could compromise the security of your devices and data. Stay vigilant by maintaining the latest virus definitions and security patches to fortify your digital environment against potential cyber attacks.

Secure your home network with a strong password and encryption.

Securing your home network with a strong password and encryption is a fundamental step in enhancing cybersecurity protection for your personal data and devices. By setting up a robust password that combines alphanumeric characters, symbols, and is not easily guessable, you can significantly reduce the risk of unauthorized access to your network. Additionally, enabling encryption protocols such as WPA2 or WPA3 ensures that the data transmitted over your network is encrypted, making it harder for cybercriminals to intercept and exploit sensitive information. Taking these proactive measures strengthens the overall security posture of your home network and helps safeguard against potential cyber threats.

Limit the amount of personal information you share online to reduce the risk of identity theft.

Limiting the amount of personal information you share online is a crucial tip in cybersecurity security solutions to mitigate the risk of identity theft. By being cautious about the details you disclose on the internet, such as your full name, address, birthdate, and financial information, you can minimize the chances of cybercriminals gaining access to sensitive data that could be used for fraudulent activities. Protecting your privacy online is an essential step in safeguarding your identity and maintaining control over your personal information in today’s digital age.

Educate yourself on common cybersecurity threats and best practices for staying safe online.

It is crucial to educate yourself on common cybersecurity threats and best practices for staying safe online. By understanding the potential risks and adopting proactive measures, you can enhance your digital security posture and protect your sensitive information from cyber threats. Stay informed about phishing scams, malware attacks, and other common tactics used by cybercriminals to target individuals and organizations. Implementing strong password practices, keeping software up to date, and being cautious with email attachments and links are essential steps in safeguarding your online presence. Remember, knowledge is power when it comes to cybersecurity, so invest time in learning how to navigate the digital landscape securely.

cloud security services in cloud computing

Enhancing Data Protection: The Role of Cloud Security Services in Cloud Computing

Cloud Security Services in Cloud Computing

The Importance of Cloud Security Services in Cloud Computing

Cloud computing has revolutionized the way businesses operate by offering scalable and flexible solutions for data storage, processing, and management. However, with the increasing reliance on cloud services comes the need for robust security measures to protect sensitive information from cyber threats.

What Are Cloud Security Services?

Cloud security services are specialized tools and protocols designed to safeguard data stored in cloud environments. These services aim to mitigate risks such as data breaches, unauthorized access, malware attacks, and other security vulnerabilities that can compromise the integrity and confidentiality of information.

The Benefits of Cloud Security Services

Implementing cloud security services offers several key benefits:

  • Data Protection: Encryption, access controls, and authentication mechanisms help prevent unauthorized access to sensitive data.
  • Compliance: Cloud security services assist businesses in meeting regulatory requirements and industry standards related to data protection.
  • Threat Detection: Advanced monitoring tools can detect and respond to potential security incidents in real-time.
  • Scalability: Cloud security services can scale up or down based on the evolving needs of a business without compromising security.

Common Cloud Security Services

Some of the most common cloud security services include:

  • Firewalls: Network firewalls help monitor and control incoming and outgoing traffic to prevent unauthorized access.
  • Intrusion Detection Systems (IDS): IDS tools analyze network traffic for suspicious activity that may indicate a cyber attack.
  • Data Loss Prevention (DLP): DLP solutions prevent sensitive data from being leaked or lost through monitoring and enforcement policies.
  • Vulnerability Assessment: Regular assessments identify potential weaknesses in a cloud environment that could be exploited by attackers.

In Conclusion

In today’s digital landscape, ensuring the security of cloud-based operations is paramount for businesses of all sizes. By investing in robust cloud security services, organizations can protect their valuable assets, maintain customer trust, and stay ahead of evolving cyber threats in the dynamic world of cloud computing.


Essential FAQs About Cloud Security Services in Cloud Computing

  1. What is cloud security and why is it important in cloud computing?
  2. How do cloud security services help protect data in the cloud?
  3. What are the common threats to cloud security?
  4. What are the key benefits of implementing cloud security services?
  5. How can businesses ensure compliance with regulations when using cloud services?
  6. What are some best practices for securing data stored in the cloud?
  7. Are there different types of cloud security services available for businesses?
  8. How does encryption play a role in ensuring data security in the cloud?
  9. What steps can organizations take to enhance their overall cybersecurity posture in a cloud environment?

What is cloud security and why is it important in cloud computing?

Cloud security in cloud computing refers to the measures and protocols implemented to protect data and resources stored in cloud environments from cyber threats and unauthorized access. It is essential in cloud computing because businesses entrust their sensitive information to third-party cloud service providers, making data security a top priority. Without robust cloud security measures in place, organizations are vulnerable to data breaches, cyber attacks, and potential loss of critical information. By ensuring strong cloud security practices, businesses can safeguard their assets, maintain compliance with regulations, and build trust with customers who rely on secure cloud services for their operations.

How do cloud security services help protect data in the cloud?

Cloud security services play a crucial role in safeguarding data in the cloud by implementing various protective measures. These services utilize encryption techniques to secure data both at rest and in transit, ensuring that sensitive information remains confidential and inaccessible to unauthorized users. Access controls and authentication mechanisms are also employed to verify the identity of users accessing the cloud environment, reducing the risk of data breaches. Additionally, continuous monitoring and threat detection capabilities enable cloud security services to identify and respond swiftly to potential security incidents, enhancing overall data protection in the cloud.

What are the common threats to cloud security?

Common threats to cloud security in cloud computing include data breaches, unauthorized access, malware infections, DDoS attacks, and misconfigured security settings. Data breaches can occur when sensitive information is accessed by unauthorized parties, leading to potential financial and reputational damage. Unauthorized access refers to individuals gaining entry to cloud resources without proper authorization, posing a risk of data theft or manipulation. Malware infections can compromise the integrity of data stored in the cloud, while DDoS attacks aim to disrupt services by overwhelming cloud servers with traffic. Misconfigured security settings leave vulnerabilities that attackers can exploit to gain access to confidential information. Implementing robust security measures and staying vigilant against these threats is crucial for safeguarding data in cloud environments.

What are the key benefits of implementing cloud security services?

Implementing cloud security services offers a multitude of key benefits for businesses operating in cloud computing environments. These services provide essential data protection through encryption, access controls, and authentication mechanisms, ensuring that sensitive information remains secure from unauthorized access. Additionally, cloud security services help organizations achieve compliance with regulatory requirements and industry standards related to data protection. They enable proactive threat detection with advanced monitoring tools, allowing real-time responses to potential security incidents. Moreover, the scalability of cloud security services ensures that businesses can adapt their security measures to meet evolving needs without compromising the integrity of their data.

How can businesses ensure compliance with regulations when using cloud services?

Ensuring compliance with regulations while utilizing cloud services is a critical aspect for businesses in today’s digital landscape. To achieve this, organizations can implement a comprehensive approach that includes thorough due diligence when selecting cloud service providers who adhere to relevant compliance standards. Businesses should also establish clear policies and procedures for data handling, access control, and encryption to meet regulatory requirements. Regular audits and assessments of the cloud environment can help identify any non-compliance issues and ensure continuous alignment with industry regulations. By proactively addressing compliance concerns and staying informed about evolving regulatory frameworks, businesses can confidently leverage cloud services while maintaining data security and regulatory adherence.

What are some best practices for securing data stored in the cloud?

When it comes to securing data stored in the cloud, following best practices is essential to safeguard sensitive information from potential cyber threats. Some key recommendations include implementing strong encryption protocols to protect data both at rest and in transit, enforcing strict access controls to limit who can view and modify data, regularly monitoring and auditing cloud environments for any suspicious activity, conducting regular security assessments and updates to address vulnerabilities promptly, and educating employees on cybersecurity best practices to mitigate human error risks. By adhering to these best practices, organizations can enhance the security of their cloud-stored data and maintain the integrity and confidentiality of their information assets.

Are there different types of cloud security services available for businesses?

When it comes to cloud security services in cloud computing, businesses have access to a variety of options tailored to their specific needs. Different types of cloud security services are available to address various aspects of data protection and threat mitigation. From encryption and access controls to intrusion detection systems and vulnerability assessments, businesses can choose from a range of solutions to enhance the security of their cloud environments. By leveraging these diverse offerings, organizations can implement a comprehensive security strategy that safeguards their data and infrastructure against cyber threats in the ever-evolving digital landscape.

How does encryption play a role in ensuring data security in the cloud?

Encryption plays a crucial role in ensuring data security in the cloud by transforming sensitive information into a coded format that can only be accessed by authorized parties with the decryption key. When data is encrypted before being stored or transmitted in the cloud, even if unauthorized individuals gain access to it, they cannot decipher the content without the encryption key. This adds an extra layer of protection to prevent data breaches and unauthorized access, making encryption an essential component of safeguarding data integrity and confidentiality in cloud computing environments.

What steps can organizations take to enhance their overall cybersecurity posture in a cloud environment?

To enhance their overall cybersecurity posture in a cloud environment, organizations can take several proactive steps. First and foremost, implementing strong access controls and encryption mechanisms is crucial to safeguarding sensitive data stored in the cloud. Regularly updating security patches and conducting vulnerability assessments help identify and mitigate potential weaknesses in the cloud infrastructure. Additionally, educating employees on best practices for data security and implementing multi-factor authentication can further bolster defenses against cyber threats. Collaborating with trusted cloud security service providers and staying informed about the latest trends in cloud security are also essential for maintaining a robust cybersecurity posture in a rapidly evolving digital landscape.

cyber security services for companies

Enhancing Business Resilience: Comprehensive Cyber Security Services for Companies

Cyber Security Services for Companies

The Importance of Cyber Security Services for Companies

In today’s digital age, cyber threats are becoming more sophisticated and prevalent than ever before. Companies of all sizes are at risk of cyber attacks that can result in data breaches, financial losses, and damage to their reputation. This is why investing in robust cyber security services is crucial for the protection of sensitive information and the continuity of business operations.

Key Benefits of Cyber Security Services for Companies:

  • Protection from Cyber Attacks: Cyber security services help companies defend against various cyber threats such as malware, ransomware, phishing attacks, and more.
  • Data Protection: By implementing encryption, access controls, and data backup solutions, companies can safeguard their valuable data from unauthorized access or loss.
  • Compliance with Regulations: Many industries have strict data protection regulations that companies must comply with. Cyber security services ensure that businesses meet these requirements to avoid legal repercussions.
  • Enhanced Business Continuity: In the event of a cyber attack or system failure, having robust cyber security measures in place can minimize downtime and ensure business continuity.
  • Reputation Management: A data breach or security incident can severely damage a company’s reputation. Cyber security services help prevent such incidents and maintain customer trust.

Types of Cyber Security Services Offered to Companies:

Companies can benefit from a range of cyber security services tailored to their specific needs, including:

  • Network Security: Protecting networks from unauthorized access and potential intrusions.
  • Endpoint Security: Securing endpoints such as laptops, desktops, and mobile devices from malware and other threats.
  • Incident Response: Developing response plans to quickly address and mitigate cyber security incidents.
  • Vulnerability Assessment: Identifying weaknesses in systems and applications to proactively address potential security risks.
  • Security Awareness Training: Educating employees on best practices for maintaining a secure work environment.

Cyber security is not a one-time investment but an ongoing process that requires continuous monitoring, updates, and adaptation to evolving threats. By partnering with reputable cyber security service providers, companies can stay ahead of cyber criminals and protect their assets effectively.


Essential Cybersecurity Tips for Companies: Strengthen Your Defense with These 6 Strategies

  1. Regularly update software and systems to patch security vulnerabilities.
  2. Implement strong password policies and enable multi-factor authentication.
  3. Train employees on cybersecurity best practices and how to recognize phishing attempts.
  4. Secure company devices with encryption and remote wipe capabilities in case of loss or theft.
  5. Back up important data regularly to prevent data loss from ransomware attacks or hardware failures.
  6. Monitor network traffic for suspicious activity and invest in intrusion detection/prevention systems.

Regularly update software and systems to patch security vulnerabilities.

Regularly updating software and systems is a crucial aspect of maintaining strong cyber security for companies. By applying patches and updates promptly, organizations can address known security vulnerabilities and reduce the risk of exploitation by cyber attackers. Keeping software and systems up to date ensures that they have the latest security features and fixes, enhancing overall protection against potential threats. Proactive maintenance through regular updates is a simple yet effective way to bolster the resilience of a company’s cyber defenses and safeguard sensitive data from potential breaches.

Implement strong password policies and enable multi-factor authentication.

To enhance cyber security measures, companies should implement strong password policies and enable multi-factor authentication. Strong password policies require employees to create complex passwords that are difficult to guess, thereby reducing the risk of unauthorized access to sensitive information. Multi-factor authentication adds an extra layer of security by requiring users to provide additional verification beyond just a password, such as a code sent to their mobile device. These measures significantly strengthen defenses against cyber threats and help safeguard company data from potential breaches.

Train employees on cybersecurity best practices and how to recognize phishing attempts.

Training employees on cybersecurity best practices and how to recognize phishing attempts is a crucial step in enhancing a company’s overall cyber security posture. By educating staff members on the importance of strong passwords, identifying suspicious emails, and being cautious of clicking on unknown links or attachments, organizations can significantly reduce the risk of falling victim to cyber attacks. Empowering employees with the knowledge and skills to detect and report potential security threats not only helps protect sensitive data but also strengthens the company’s defense against evolving cyber threats.

Secure company devices with encryption and remote wipe capabilities in case of loss or theft.

To enhance cyber security measures for companies, it is crucial to secure company devices with encryption and remote wipe capabilities in case of loss or theft. By encrypting sensitive data stored on devices, companies can protect information from unauthorized access even if the device falls into the wrong hands. Additionally, enabling remote wipe capabilities allows companies to remotely erase data on lost or stolen devices, minimizing the risk of data breaches and ensuring that confidential information remains secure. This proactive approach helps companies mitigate potential risks and safeguard their valuable assets effectively.

Back up important data regularly to prevent data loss from ransomware attacks or hardware failures.

Regularly backing up important data is a crucial practice for companies to prevent data loss from ransomware attacks or hardware failures. By maintaining up-to-date backups of critical information, businesses can ensure that they have copies of their data available in case of a cyber incident or system malfunction. This proactive approach not only safeguards against potential data breaches but also enables quick recovery and minimal disruption to operations in the event of an unforeseen event. Implementing a robust backup strategy is an essential component of a comprehensive cyber security plan for companies looking to protect their valuable assets and maintain business continuity.

Monitor network traffic for suspicious activity and invest in intrusion detection/prevention systems.

To enhance cyber security measures, companies should prioritize monitoring network traffic for any signs of suspicious activity. Investing in intrusion detection and prevention systems can help identify and mitigate potential threats before they escalate. By proactively monitoring network traffic and deploying robust security systems, companies can strengthen their defense against cyber attacks and safeguard their sensitive data from unauthorized access.

cisco cybersecurity

Enhancing Security with Cisco Cybersecurity Solutions

The Importance of Cisco Cybersecurity Solutions

The Importance of Cisco Cybersecurity Solutions

In today’s digital age, cybersecurity has become a critical concern for businesses of all sizes. With the increasing frequency and sophistication of cyber threats, organizations need robust solutions to protect their sensitive data and systems. This is where Cisco’s cybersecurity offerings come into play.

Comprehensive Protection

Cisco is a global leader in networking and cybersecurity solutions. Their cybersecurity products and services are designed to provide comprehensive protection against a wide range of cyber threats, including malware, ransomware, phishing attacks, and data breaches.

Advanced Threat Detection

Cisco’s cybersecurity solutions leverage advanced technologies such as artificial intelligence and machine learning to detect and respond to threats in real-time. By analyzing vast amounts of data and identifying patterns indicative of malicious activity, Cisco helps organizations stay one step ahead of cybercriminals.

Secure Access Control

With Cisco’s secure access control solutions, organizations can ensure that only authorized users have access to their networks and resources. By implementing robust authentication mechanisms and granular access controls, Cisco helps prevent unauthorized access and data exfiltration.

Continuous Monitoring and Compliance

Cisco offers tools for continuous monitoring of network traffic, system logs, and user activities to detect any anomalies that may indicate a security breach. Additionally, Cisco’s cybersecurity solutions help organizations achieve compliance with industry regulations and standards by providing detailed reporting and auditing capabilities.

Conclusion

In conclusion, Cisco cybersecurity solutions play a vital role in helping organizations protect their digital assets from evolving cyber threats. By investing in Cisco’s comprehensive security offerings, businesses can enhance their resilience against cyber attacks and safeguard their reputation and bottom line.


Top 9 FAQs About Cisco Cybersecurity: Solutions, Benefits, and Integration

  1. What is Cisco cybersecurity?
  2. Why is cybersecurity important for businesses?
  3. What are the key features of Cisco cybersecurity solutions?
  4. How does Cisco protect against cyber threats?
  5. What industries can benefit from Cisco cybersecurity solutions?
  6. Are Cisco cybersecurity products scalable for small to large enterprises?
  7. Does Cisco offer training and support for implementing their cybersecurity solutions?
  8. How does Cisco stay ahead of emerging cyber threats?
  9. Can Cisco cybersecurity solutions integrate with existing IT infrastructure?

What is Cisco cybersecurity?

Cisco cybersecurity refers to the range of products and services offered by Cisco Systems to help organizations protect their digital assets from cyber threats. Cisco’s cybersecurity solutions encompass a comprehensive set of tools and technologies designed to detect, prevent, and respond to various types of cyber attacks, including malware, ransomware, phishing attempts, and data breaches. By leveraging advanced technologies like artificial intelligence and machine learning, Cisco helps organizations strengthen their security posture and mitigate risks associated with the ever-evolving threat landscape. With a focus on continuous monitoring, secure access control, and compliance management, Cisco cybersecurity aims to provide robust protection for businesses of all sizes against cyber threats in today’s interconnected world.

Why is cybersecurity important for businesses?

Cybersecurity is crucial for businesses due to the increasing frequency and sophistication of cyber threats in today’s digital landscape. Protecting sensitive data, intellectual property, and customer information is paramount for maintaining trust and credibility with stakeholders. A successful cyber attack can have devastating consequences, including financial losses, reputational damage, legal implications, and operational disruptions. By investing in robust cybersecurity measures, businesses can mitigate risks, safeguard their assets, comply with regulations, and demonstrate a commitment to safeguarding their customers’ privacy and security. Ultimately, cybersecurity is essential for ensuring business continuity and resilience in the face of evolving cyber threats.

What are the key features of Cisco cybersecurity solutions?

Cisco cybersecurity solutions offer a comprehensive suite of key features that empower organizations to enhance their security posture. Some of the key features include advanced threat detection using cutting-edge technologies like artificial intelligence and machine learning, secure access control mechanisms to prevent unauthorized access, continuous monitoring for detecting anomalies and potential security breaches in real-time, robust data encryption to protect sensitive information, and compliance management tools to ensure adherence to industry regulations and standards. By leveraging these features, Cisco cybersecurity solutions provide organizations with the necessary tools to defend against a wide range of cyber threats and safeguard their critical assets effectively.

How does Cisco protect against cyber threats?

Cisco employs a multi-layered approach to protect against cyber threats. Through a combination of advanced technologies such as artificial intelligence, machine learning, and behavioral analytics, Cisco can detect and respond to threats in real-time. Cisco’s security solutions encompass network security, endpoint security, cloud security, and more, providing comprehensive protection across the entire IT infrastructure. By continuously monitoring network traffic and user activities, Cisco can identify and mitigate potential threats before they cause harm. Additionally, Cisco offers secure access control mechanisms to ensure that only authorized users can access sensitive data and resources, enhancing overall cybersecurity posture for organizations of all sizes.

What industries can benefit from Cisco cybersecurity solutions?

Various industries can benefit significantly from implementing Cisco cybersecurity solutions. Industries such as finance, healthcare, government, education, and retail rely heavily on secure and reliable networks to protect sensitive data and maintain regulatory compliance. Cisco’s robust cybersecurity offerings cater to the specific needs of each industry, providing advanced threat detection, secure access controls, continuous monitoring, and compliance reporting. By leveraging Cisco’s expertise in cybersecurity, organizations across diverse sectors can enhance their security posture, mitigate risks, and safeguard their critical assets from cyber threats.

Are Cisco cybersecurity products scalable for small to large enterprises?

When considering the scalability of Cisco cybersecurity products for small to large enterprises, it’s important to note that Cisco offers a range of solutions tailored to meet the diverse needs of businesses of varying sizes. Whether you are a small startup or a large corporation, Cisco provides cybersecurity products that can scale effectively to accommodate your organization’s growth and evolving security requirements. With flexible deployment options and customizable features, Cisco’s cybersecurity offerings are designed to adapt to the changing threat landscape and the expanding digital footprint of enterprises, making them suitable for both small businesses looking to establish a strong security foundation and large enterprises seeking robust protection at scale.

Does Cisco offer training and support for implementing their cybersecurity solutions?

Many individuals and organizations frequently inquire about whether Cisco provides training and support for implementing their cybersecurity solutions. The answer is a resounding yes. Cisco offers a wide range of training programs, certifications, and support services specifically tailored to help users effectively deploy and manage their cybersecurity solutions. Whether it’s through online courses, instructor-led training, or on-site workshops, Cisco ensures that users have access to the knowledge and resources needed to successfully implement and optimize their cybersecurity infrastructure. Additionally, Cisco’s dedicated support teams are available to provide guidance, troubleshooting assistance, and best practices to ensure a smooth and secure deployment of their cybersecurity solutions.

How does Cisco stay ahead of emerging cyber threats?

Cisco stays ahead of emerging cyber threats by continuously investing in research and development to innovate new cybersecurity technologies and solutions. By leveraging cutting-edge tools such as artificial intelligence, machine learning, and behavioral analytics, Cisco can proactively identify and mitigate potential threats before they can cause harm. Additionally, Cisco collaborates with industry experts, partners, and customers to gather insights on emerging cyber threats and trends, allowing them to adapt their security strategies accordingly. This proactive approach enables Cisco to stay one step ahead of cybercriminals and provide robust cybersecurity solutions that effectively protect organizations against evolving threats in today’s dynamic threat landscape.

Can Cisco cybersecurity solutions integrate with existing IT infrastructure?

When considering Cisco cybersecurity solutions, a commonly asked question is whether they can seamlessly integrate with existing IT infrastructure. The answer is yes. Cisco offers a range of cybersecurity products and services that are designed to be interoperable with various systems and technologies already in place within an organization. Whether it’s network devices, cloud services, or endpoint security solutions, Cisco provides integration capabilities to ensure a smooth transition and effective collaboration with existing IT infrastructure. This interoperability not only simplifies the implementation process but also enhances the overall security posture by leveraging the strengths of both Cisco’s cybersecurity solutions and the organization’s current technology environment.

cyber security audit

Maximizing Security: The Essential Cyber Security Audit Process

The Importance of Cyber Security Audit

The Importance of Cyber Security Audit

In today’s digital age, where businesses rely heavily on technology to operate efficiently, the importance of cyber security cannot be overstated. Cyber attacks are becoming increasingly sophisticated, and organizations need to be proactive in safeguarding their data and systems.

A cyber security audit is a crucial step in assessing an organization’s security posture. It involves evaluating existing security measures, identifying vulnerabilities, and recommending improvements to enhance overall security.

Key Benefits of Cyber Security Audit:

  • Identifying Weaknesses: A cyber security audit helps uncover vulnerabilities in the organization’s network, systems, and processes that could be exploited by malicious actors.
  • Risk Assessment: By conducting an audit, organizations can assess the level of risk they face from potential cyber threats and prioritize mitigation efforts accordingly.
  • Compliance: Many industries have regulatory requirements for data protection. A cyber security audit ensures that the organization is compliant with relevant laws and standards.
  • Enhanced Protection: Implementing recommendations from a cyber security audit strengthens the organization’s defenses against cyber attacks and reduces the likelihood of a successful breach.
  • Awareness and Training: Audits can also highlight areas where employees may need additional training on best practices for maintaining a secure environment.

It is essential for organizations to conduct regular cyber security audits to stay ahead of emerging threats and protect sensitive information. By investing in proactive security measures, businesses can minimize the risk of data breaches and maintain trust with customers and stakeholders.

Remember, when it comes to cyber security, prevention is always better than cure. Stay vigilant, stay secure!


7 Essential Tips for a Comprehensive Cybersecurity Audit

  1. Regularly review and update security policies and procedures.
  2. Conduct vulnerability assessments to identify potential weaknesses.
  3. Implement strong access controls to protect sensitive data.
  4. Monitor network activity for any signs of unauthorized access.
  5. Train employees on cybersecurity best practices and awareness.
  6. Backup data regularly to prevent data loss in case of a breach.
  7. Engage with third-party experts for independent security audits.

Regularly review and update security policies and procedures.

It is crucial for organizations to regularly review and update their security policies and procedures as part of a comprehensive cyber security audit. By staying current with evolving threats and industry best practices, companies can ensure that their security measures remain effective and aligned with the latest standards. Updating policies and procedures allows businesses to address new vulnerabilities, strengthen defenses, and enhance overall resilience against cyber attacks. Consistent review and updates demonstrate a commitment to maintaining a robust security posture and safeguarding sensitive data from potential breaches.

Conduct vulnerability assessments to identify potential weaknesses.

To enhance the effectiveness of a cyber security audit, it is essential to conduct vulnerability assessments to identify potential weaknesses within an organization’s network, systems, and processes. By proactively seeking out vulnerabilities, businesses can prioritize remediation efforts and strengthen their overall security posture. Vulnerability assessments play a crucial role in mitigating risks and preventing potential cyber threats from exploiting weaknesses in the infrastructure.

Implement strong access controls to protect sensitive data.

To enhance the security of sensitive data during a cyber security audit, it is crucial to implement strong access controls. By restricting access to authorized personnel only, organizations can prevent unauthorized users from compromising sensitive information. Strong access controls include implementing multi-factor authentication, role-based access permissions, and regular monitoring of user activity to detect any suspicious behavior. These measures not only protect valuable data but also contribute to a robust security posture that safeguards against potential cyber threats.

Monitor network activity for any signs of unauthorized access.

Monitoring network activity for any signs of unauthorized access is a crucial tip in ensuring effective cyber security. By actively tracking and analyzing network traffic, organizations can quickly detect any unusual or suspicious behavior that may indicate a potential security breach. Identifying unauthorized access early allows for prompt response and mitigation measures to prevent data loss or system compromise. Continuous monitoring of network activity is essential in maintaining a secure environment and safeguarding sensitive information from cyber threats.

Train employees on cybersecurity best practices and awareness.

Training employees on cybersecurity best practices and raising awareness about potential cyber threats are essential components of a comprehensive cyber security audit. By educating staff members on how to identify phishing attempts, create strong passwords, and recognize suspicious activities, organizations can significantly reduce the risk of data breaches and cyber attacks. An informed workforce serves as an additional layer of defense against evolving threats in the digital landscape, ultimately contributing to a more secure and resilient business environment.

Backup data regularly to prevent data loss in case of a breach.

Regularly backing up your data is a crucial practice in cyber security to mitigate the risk of data loss in the event of a breach. By maintaining up-to-date backups of your important information, you can ensure that even if your systems are compromised, you have a secure copy of your data that can be restored. This proactive measure not only helps in recovery efforts but also provides peace of mind knowing that your valuable data is safeguarded against potential cyber threats.

Engage with third-party experts for independent security audits.

Engaging with third-party experts for independent security audits is a valuable tip in ensuring the thoroughness and objectivity of your cyber security assessment. By bringing in external specialists who possess a fresh perspective and specialized knowledge, organizations can uncover blind spots, identify vulnerabilities, and receive unbiased recommendations to enhance their overall security posture. Third-party experts can offer insights that internal teams may overlook, providing a comprehensive evaluation that strengthens defenses against potential cyber threats. Collaborating with independent auditors demonstrates a commitment to proactive risk management and underscores the importance of prioritizing cybersecurity in today’s digital landscape.